Your new post is loading...

|
Scooped by
Gust MEES
May 7, 2012 12:31 PM
|
With the latest Lion security update, Mac OS X 10.7.3, Apple has accidentally turned on a debug log file outside of the encrypted area hat stores the user’s password in clear text! ===> Anyone who used FileVault encryption on their Mac prior to Lion, upgraded to Lion, but kept the folders encrypted using the legacy version of FileVault is vulnerable. FileVault 2 (whole disk encryption) is unaffected. <=== Read more...
|
|
Scooped by
Gust MEES
May 6, 2012 5:17 AM
|
Apple has exposed the encryption passwords of FileVault users in the most recent update to OS X Lion. ===> Users are advised to use full disk encryption and change passwords that may have been recorded ... <=== Read more...
|
|
Scooped by
Gust MEES
May 5, 2012 3:57 PM
|
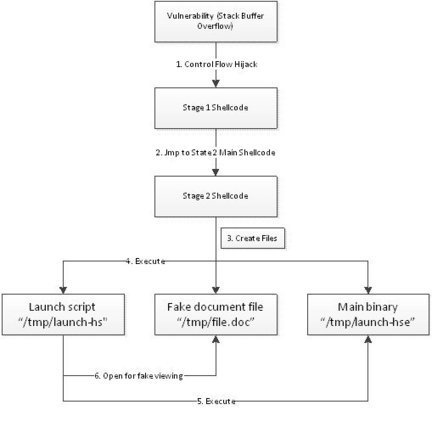
Microsoft explique avoir analysé le comportement d'un malware ciblant une faille au sein de Microsoft Office pour Mac. ===> « Aucun système d'exploitation sortant des laboratoires est immunisé contre les malwares », conclut ainsi Microsoft même si la vulnérabilité en question se trouve tout de même au sein d'une suite de logiciels développés par ses propres soins. <=== Quoi qu'il en soit, l'éditeur conseille aux utilisateurs de Microsoft Office pour Mac 2004/2008 d'activer les mises à jour. Notons que Mac OS X Lion n'est pas concerné par ce malware. La suite sur Clubic.com : Sécurité : Microsoft met en garde les utilisateurs de Mac OS X http://www.clubic.com/antivirus-securite-informatique/actualite-489960-microsoft-office-malware-mac-os.html#ixzz1u1jjCqV3
Informatique et high tech
|
|
Scooped by
Gust MEES
May 3, 2012 7:41 AM
|
Depuis les aventures du malware Flashback sur Mac OS X, la sécurité des Mac est redevenue un sujet à sensations. Les éditeurs de solutions de sécurité s’en sont donnés à cœur joie, l’occasion leur étant fournie de mettre en pratique des ... Lire plus...
|
|
Scooped by
Gust MEES
May 2, 2012 12:49 PM
|
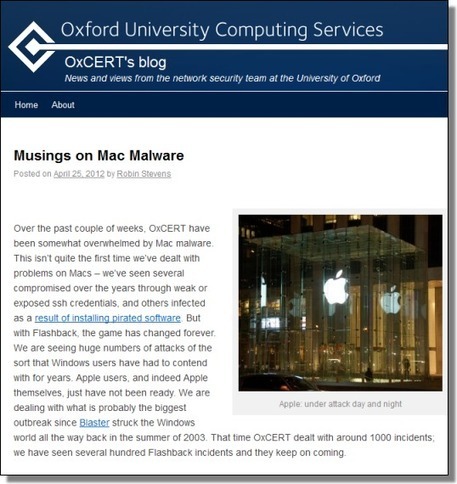
Oxford Muses on Mac Flashback: Worst Outbreak Since Blaster So how bad was last month's Mac Flashback outbreak and who suffered the most? Our guess: it was bad, and university IT help desks. And it looks like our guess might not be far off the mark. ===> Oxford University Computing Services' network security team (aka OxCERT) has written that they dealt "with what is probably the biggest outbreak since Blaster struck the Windows world all the way back in the summer of 2003." <=== OxCERT dealt with around 1000 incidents for Blaster. They've seen several hundred Flashback incidents… "and they keep on coming." Read more...
|
|
Scooped by
Gust MEES
May 2, 2012 8:51 AM
|
Vous croyez toujours que votre Mac est sécurisé, car les PC Microsoft tombent sous les virus et les vers, mais pas les Macs ? Réveillez-vous ! Cette année a connu la première compromission majeure de Macs à travers le monde (*). Qu'en est-il du vôtre ? Ainsi, utilisateurs de Mac, sachez que, d'une part mettre à jour en temps opportun, et d'autre part utiliser un logiciel anti-virus sont également bons pour votre Mac (et vos nerfs). Gardez votre système d'exploitation à jour en utilisant le mécanisme de "Mise à jour de logiciels..." qui est accessible dans le menu "Apple". Utilisez les droits "administrateur" uniquement lorsque c'est nécessaire, sinon, conservez les droits "utilisateur" restreints. Mais notez aussi qu'Apple peut encore s'améliorer: il leur a fallu des mois pour publier le correctif approprié - ce qui est long comparé au cycle mensuel de mise à jour de Microsoft.
|
|
Scooped by
Gust MEES
May 2, 2012 8:38 AM
|
Über Flashback dürften sich nicht nur die Besitzer befallener Rechner ärgern, sondern auch Google. Jeden Tag sollen dem Suchgiganten wegen des Trojaners bis zu 10'000 US-Dollar entgehen.
|
|
Scooped by
Gust MEES
May 1, 2012 5:15 PM
|
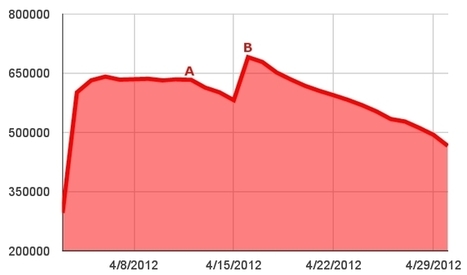
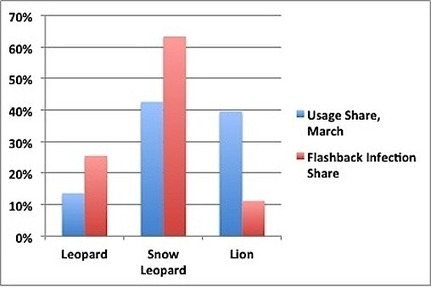
Dr. Web's count of Macs actively infected with Flashback over time. The "A" marks Apple's release of its Flashback removal tool, and the "B" marks Dr. Web's discovery of another variant of Flashback that led to an increase in its infection count. ===> Flashback has been used for click fraud, as detailed by Symantec’s researchers. The malware redirected traffic from Google search ads to its own pay-per-click ads, generating as much as $10,000 a day. <=== Even with its command and control servers disabled, the infected machines continue to engage in that traffic-hijacking. And with nearly half a million users still infected, Flashback’s authors are still likely profiting from their scheme. Read more...
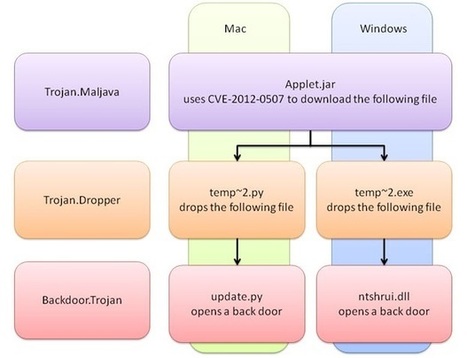
The same Java vulnerability used in the infamous Flashback malware is now being used as an attack vector for a single piece of malware that can infect both Windows and Mac OS X computers. Security vendors have discovered a new piece of malware that attacks both PCs and Macs. It uses the same Java security vulnerability exploited by the Flashback malware that infected hundreds of thousands of Macs. While the attack vector is the same as in Flashback, this Java Applet checks which OS it is running on and downloads suitable malware for it. Gust MEES: use my free courses to know how to stay secure, follow links below... - http://gustmeesen.wordpress.com/2012/03/16/beginners-it-security-guide/
|
|
Scooped by
Gust MEES
April 29, 2012 12:16 PM
|
A pair of high-profile malware attacks have given Apple a crash course in security response. ===> A MUST READ for Apple users!!! <===
|
|
Scooped by
Gust MEES
April 28, 2012 2:59 PM
|
New details about the extent of the Mac-specific Flashback malware epidemic emerged today.
|
|
Scooped by
Gust MEES
April 27, 2012 12:34 PM
|
Cyber criminals using same exploit to infect Windows and Mac OS machines with new malware...
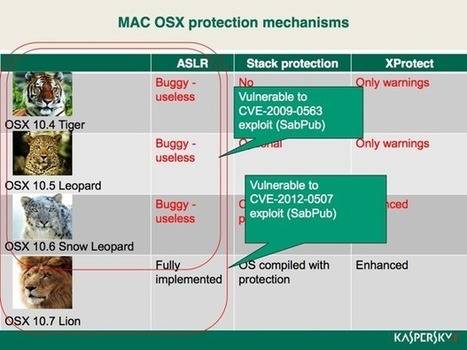
Apple a des leçons à prendre chez Microsoft en matière de sécurité, c'est le contast dressé par Eugene Kaspersky, le PDG de l'éditeur de logiciels spécialisés qui porte son nom. ===> Utilisateurs Mac, apprenez la sécurité informatique dès à présent ! <=== Lire plus...
|
In der aktuellen Version von MacOS 10.7 (Lion) hat sich ein Fehler eingeschlichen, durch den Passwörter im Klartext abgespeichert werden. Unbedingt weiter lesen...
|
|
Scooped by
Gust MEES
May 5, 2012 4:37 PM
|
A l’occasion de l’analyse d’un programme malveillant sur Mac OS X, exploitant une ancienne faille d’Office, Microsoft glisse une conclusion sur la sécurité du système d’Apple. Une analyse qui se croise avec les critiques de Kaspersky sur la sécurité d’Apple, mise en doute suite à la diffusion du cheval de Troie Flashback. Sur le Malware Protection Center, Microsoft est revenu le 30 avril sur un programme malveillant actif sur l’environnement d’Apple et qui exploite une faille d’Office pour Mac vieille de trois ans. A noter que cette faille n’est exploitable que sur les versions Snow Leopard et précédentes de l’OS, Lion n’étant donc pas concerné. Restez sur vos gardes, cela promet... rien de bon...
|
|
Scooped by
Gust MEES
May 3, 2012 8:51 AM
|
Jahrelang hat Apple Java für sein Mac OS selbst bereit gestellt und im Grunde versucht es loszuwerden. Doch jetzt hat man sich mit Oracle geeinigt, dass der Java-Hersteller diese Aufgabe übernehmen soll. Mac-Benutzer sollen in Bezug auf Java also Windows- und Linux-Nutzern gleichgestellt und somit früher als bislang mit Sicherheits-Updates versorgt werden. Read more...
|
|
Scooped by
Gust MEES
May 2, 2012 6:25 PM
|
Apple may have appeared to have pulled off a coup in persuading Oracle to maintain Java for Mac but can Oracle be trusted to get it right? The emergence of the Flashback Trojan - which exploited a vulnerability in Mac OS X's version of Java - earlier this year led to a lot of flak for both Oracle and Apple. The vulnerability was known about and fixed in the Windows and Linux versions of Java, but remained exposed in OS X for several more weeks. ===> The fact that Apple is ultimately responsible for maintaining Java on OS X saw Apple's ability to protect its users questioned. <=== Read more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
|
|
Scooped by
Gust MEES
May 2, 2012 8:54 AM
|
Selon Symantec, les auteurs du malware Flashback ont pu gagner jusqu'à 10 000 $ par jour au plus fort de l'infection, qui a touché environ 1 % des Mac en circulation. ===> Un business lucratif qui explique pourquoi, sa popularité aidant, le Mac est lui aussi devenu une proie pour les hackers. <===
|
|
Scooped by
Gust MEES
May 2, 2012 8:47 AM
|
Microsoft has detected a new piece of malware targeting Apple OS X computers that exploits a vulnerability in the Office productivity suite patched nearly three years ago. Microsoft advised those who use Microsoft Office 2004 or 2008 for Mac or the Open XML File Format Converter for Mac to ensure those products have applied the patch. ===> "In conclusion, we can see that Mac OS X is not safe from malware," Oh wrote. "Statistically speaking, as this operating system gains in consumer usage, attacks on the platform will increase." <=== Read more...
|
|
Scooped by
Gust MEES
May 1, 2012 5:53 PM
|
Flashback Malware Robs Google of $10,000/Day in Ad Revenue The authors of MacOS malware 'Flashback' are reaping an estimated $10,000 a day by through an additional component, Symantec reports. Read more...
|
|
Scooped by
Gust MEES
May 1, 2012 5:03 PM
|
Antivirus firm Symantec has published a new blog post examining how the Flashback malware affecting hundreds of thousand of Macs has been generating... Flashback Malware's Ad-Click Hijacking Detailed, Could Reap $10,000/Day Read more...
|
|
Scooped by
Gust MEES
April 29, 2012 3:18 PM
|
With the recent glut of high profile Mac-based malware like MacDefender and Flashback, it’s easy to forget that Macintosh computers (and Mac malware) have been kicking around for more than thirty years – longer, even, than Windows malware. In fact, the first documented Mac virus actually predated some of the first PC viruses by a good four years. While conventional wisdom has always assumed that Macs are inherently safer than PCs, wider adoption of Macs in recent years has given rise to new and more sophisticated threats, with many suggesting that Apple’s honeymoon with malware authors may be over. As this slideshow of Mac Malware through the years shows, however, Apple machines are no strangers to malicious software. Read more and don't forget "Nobody is perfect ;)"...
|
|
Scooped by
Gust MEES
April 28, 2012 3:49 PM
|
A trojan that hijacks how your computer accesses the Internet could cut off thousands of machines this summer. There’s a trojan out there that tricks computers — both PCs and Macs — into redirecting all their Internet traffic through malicious servers. Even though the trojan’s creators have been stopped and arrested, millions of PCs could still be infected. ===> For those machines, the Internet will cease to exist on July 9. <=== Read more...
|
|
Scooped by
Gust MEES
April 27, 2012 12:55 PM
|
A new malware attack is targeting Mac computers with a Python-based backdoor Trojan.
And Windows computers aren't getting away scott free either.
|
|
Scooped by
Gust MEES
April 27, 2012 12:13 PM
|
Mac computers are not immune to viruses... SECURITY VENDOR Sophos' senior technology consultant Graham Cluley warns that it's time for Apple users to take notice of the threats facing Mac OS X operating systems by securing their computers with antivirus software.
Source: The Inquirer (http://s.tt/1abnN)
Read more and watch the video...
|