



Java update is no protection against new SabPub Mac Trojan!
SabPub Mac Trojan is spreading via Word documents, using an ancient vulnerability...
Read more...

 Your new post is loading...
 Scoop.it! Java update is no protection against new SabPub Mac Trojan!
SabPub Mac Trojan is spreading via Word documents, using an ancient vulnerability...
Read more... 
No comment yet.
Sign up to comment
Scoop.it!
Repéré par des chercheurs de chez Kasperky, le malware SabPub exploite une fois encore une faille de sécurité Java dans Mac OS X via des documents Word piégés.
Scoop.it!

Découvert par Kaspersky, ce nouveau malware qui cible les Mac exploite une faille de sécurité Java.
Le répit aura été de courte durée. À peine Apple avait-il publié une mise à jour de Java contenant un logiciel de suppression du malware Flashback qu’un nouveau fléau était découvert. Baptisé SabPub, il a été découvert par l’éditeur Kaspersky qui en a repéré deux variantes.
Comme Flashback, SabPub passe par une faille de sécurité de Java au moyen d’un document Word piégé. Le Mac infecté va ensuite se connecter à un site web depuis lequel sont envoyées des commandes. Un pirate peut notamment obtenir des captures d’écran du Mac de la victime.
Cependant, le mode de diffusion de ce malware via des documents Word piégés rend sa propagation moins puissante que celle de Flashback qui a touché 600 000 machines de par le monde.
Scoop.it!

The Flashback malware is still on the decline, but the security firm says its latest estimate of infected machines is higher than expected.
In a blog post today, software maker and security firm Symantec lowered its estimate of machines that still have the malware to 140,000, which is down considerably from estimates of more than 600,000 less than two weeks ago. Even so, the firm said it was expecting a lower tally.
Read more...
Scoop.it!
April 17, 2012 — Network World — It was always thought that as Apple products increased in popularity, so would the target on its back placed by cybercriminals. Always looking to take down the king of the hill, cybercriminals finally got to Apple's Macs last week with a botnet that attacked more than 600,000 machines.
With such an accomplishment, the question is who is really safe from these attacks? The quick answer is no one. Anonymous has proven that.
One expert said recently, "it's the malware lurking in the background from these attacks that is truly scary. "Right now advanced persistent malware is very expensive to do right and is not being produced by very many organizations, but it is getting cheaper, it's going to get modularized and mass produced."
Read more...
Scoop.it!
Because Mac laptops' market share has grown so much, it appears Macs are being targeted more.
I hope the very legitimate sense of security Mac users have long had isn’t turning into a false sense of security.
“For years, Mac users have been able to believe that they are safer than the average computer user and turned their noses up at antivirus software. But as Apple’s market share has grown, so has the threat to Mac users’ security,” the Washington Post reports. Specifically, the Post was referring to a virus called “Flashback” that may have infected “up to 600,000 Macs … mostly in the United States and Canada” which seem now to be part of growing bonnet.” A botnet is a network of “bots” (also called “zombie networks”) that are basically compromised computers – infected computers that are obviously no longer controlled entirely by their owners.
Flashback “should be a wake-up call to those who still think that their Mac is invulnerable to attacks like this,” the Posts added.
The security advice offered in the article sounds a whole lot like what PC owners have been told for very a long time:
Read more...
Scoop.it!
A week after the Flashback Trojan began running rampant on Macintosh computers, the malware appears to be in remission.
Scoop.it!
A second variant of the Mac OS X Trojan referred to as Backdoor.OSX.SabPub.a or SX/Sabpab-A is exploiting a Microsoft Word security hole, not the usua...
Scoop.it!
A new OSX Trojan has been discovered – called Backdoor.OSX.SabPub.a – which uses a Java exploit which bypasses malware detection programs. It comes after the discovery of the Flashback Trojan this month.
According to Kaspersky Lab, the Trojan connects to a command and control server and ===> uses a Java exploit with an obfuscator to bypass malware detection programmes. <===
It’s the latest Mac Trojan discovered this month. Earlier, the Flashback Trojan was discovered and infected 600,000 Macs worldwide. Apple has since released software to detect and combat the Flashback Trojan.
Read more...
Scoop.it!
A new version of the Mac OS X Sabpab Trojan horse has come to light, and rather than relying upon a Java vulnerability - it appears to be exploiting malformed Word documents instead.
Scoop.it!
Many Mac users still refuse to understand what the successful Flashback attack really means.
No one, Apple included, ever said that OS X was immune
===> Mac users are still resisting the idea that their platform has become a popular attack target and that those attacks are succeeding. <===
Read more to have a realistic vue ;) and stop dreaming!
Scoop.it!
Sabpab exploits same Java vulnerability as Flashback...
Mac users should make sure they have applied Apple's latest Java update and installed anti-virus software after a new Trojan targeting OS X was spotted in the wild.
Ironically discovered on Friday 13th, the new Trojan - Sabpab - uses the same vulnerability in the OS X's Java plug-in to infect Macs, warns security firm Sophos.
===> It also doesn't require any user interaction to infect a system either - just like Flashback - all that needs to happen is for you to visit an infected webpage. <===
"The newly discovered Sabpab malware is in many ways a basic backdoor Trojan horse. It connects to a control server using HTTP, receiving commands from remote hackers as to what it should do.
The criminals behind the attack can grab screenshots from infected Macs, upload and download files, and execute commands remotely," said Graham Cluley, senior technology consultant at Sophos.
Scoop.it!
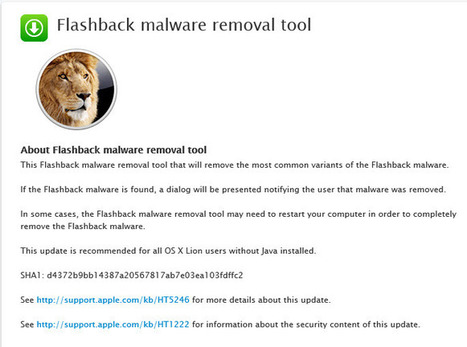
In its ongoing battle against the widespread Flashback malware attack, Apple has released a standalone removal tool.
===> The downloadable utility is available exclusively for Mac owners running OS X Lion. It will not run on Mac OS X 10.6 (Snow Leopard) or earlier versions. <===
Apple has not officially acknowledged the discontinuation of support for users of pre-Snow Leopard versions of OS X. Under the “Additional information” heading in its bulletin describing the Flashback malware, the company says: “For Macs running Mac OS X v10.5 or earlier, you can better protect yourself from this malware by disabling Java in your web browser(s) preferences.”
Several security companies have reported the discovery of a different malware variant that appears to attack the same Java vulnerability.
===> Like Flashback, this new Trojan requires no user interaction to infect your Apple Mac. Kaspersky refers to it as “Backdoor.OSX.SabPub.a” while Sophos calls it at “SX/Sabpab-A.” <===
Read more...
|
Scoop.it!
D'autres chevaux de Troie, moins graves que Flashback, ont visé Mac OS X - Malware - Après avoir découvert le Cheval de Troie Flashback sur Mac, les...
Scoop.it!

Given the attention that the Flashback Mac malware has received since the discovery of the 600K strong botnet of computers infected with it and the number of tools that various security firms and Apple issued for its removal, it's somewhat disheartening to hear that===> the botnet still counts around 140,000 zombies. <===
Read more...
Scoop.it!
Alors qu'Apple et plusieurs éditeurs en sécurité viennent de publier des correctifs pour venir à bout du cheval de Troie Flashback, un nouveau malware s'invite actuellement sur Mac OS X. Son nom : Backdoor.OSX.SabPub.a.
Scoop.it!

"SabPub" proves Macs are now targets of Advanced Persistant Threats (APTs), a persistent type of cyber attack operated by cyber criminals, Kaspersky Lab confirmed.
In an update to the ongoing SabPub saga, Kaspersky's researchers reported some unusual activity once the SabPub payload was dropped in its machine bait over the weekend.
===> The attackers were actively analyzing the computer's contents, clearly searching for something: <===
Read more...
Scoop.it!

Flaming Retort is back, this time trying to Coole and Explayne the flames we've had from some Mac users in the past few days.
My point here is not to prove that it is somebody's fault, but simply to remind us that perennially finding someone else to blame for our computer security woes is a bad idea. ...
===> Security is the responsibility of all of us: technologists, coders, mobile phone users, writers, video watchers, bloggers, Wikipedia readers, bank clerks, bicycle couriers, politicians, policemen and gardeners. <===
===> It's not your fault. It's your responsibility. <===
Scoop.it!
Die Sicherheitsexperten von Kaspersky Lab haben einen neuen Mac-Trojaner entdeckt. Die Schadsoftware heisst SabPub und verbreitet sich über Word-Dokumente.
Scoop.it!
This new minimum-threat malware development for OS X copies Flashback and suggests criminals jump on opportunistic bubbles.
Recently the Flashback malware attacks on OS X gained headlines, not because of the presence of the Trojan, which had been around for some months prior to the increase in attention, but rather because it gained the possibility of installation in a drive-by-download attack that did not require any interaction from the user in order to install.
Read more...
Scoop.it!
Attackers behind the Flashback and SabPub malware likely reverse-engineered a Java vulnerability patched for Windows almost two
Apple, which normally refuses to comment on any vulnerabilities in its products until after it's released a fix, broke with tradition by last week confirming that it was coding an OS X upgrade to nuke Flashback.
===> According to various security firms, approximately 600,000 Macs had been infected by Flashback, which makes it the largest malware infection to ever hit OS X users. <===
In addition, Kaspersky managed to tie the botnet to six malicious Microsoft Word documents that it's seen in the wild, two of which drop the SabPub vulnerability, and four of which drop the MaControl bot, which appears to be an earlier effort by the same virus writers. One key difference, however, is that MaControl didn't target the Java vulnerability exploited by Flashback and SabPub.
===> Another is that SabPub managed to remain active for about six weeks before anyone detected it. <===
Read more...
Scoop.it!

Die Sicherheitsexperten von Kaspersky warnen vor einem neuen Mac-Trojaner, der nach dem Flashback-Schädling erneut auf Apple-Anwender abzielt.
Der Flashback-Trojaner schaffte es vor wenigen Tagen binnen kürzester Zeit über 700.000 Macs zu infizieren und zu einem Teil eines Botnetzes zu machen. Der Schädling demonstrierte damit, dass Mac-Nutzer keineswegs sicher vor Online-Kriminellen sind.
Der von Kaspersky Lab neu entdeckte Schädling wurde auf den Namen SabPub getauft und verbreitet sich über Word-Dokumente.
Dabei wird dieses Mal die bereits bekannte Java-Schwachstelle CVE-2009-0563 ausgenutzt. Die Online-Kriminelle nutzen SabPub zum Aufbau eines Botnetzes, das unter anderem für Datenspionage genutzt wird.
Kaspersky warnt:"Das Schadprogramm wird via Spear Phishing – einer sehr zielgerichteten Phishing-Attacke – verbreitet.
Als Social-Engineering-Trick wird das Thema Tibet/Dalai Lama ausgenutzt, wie dies auch im so genannten „Lucky Cat“-Fall geschehen ist."
Read more...
Scoop.it!
Apple's decision to push out a Flashback malware removal tool for OS X Lion bundled with a new Java security update has proven to be rather fortunate, as a new Mac OS X threat has been discovered taking advantage of the vulnerability (CVE-2012-0507) exploited by the latest Flashback variants.
The security update in question configures the Java web plug-in to disable the automatic execution of Java applets in browsers, a move that should prevent users from inadvertently falling victim to similar drive-by malware attacks in the future.
In the meantime, those who haven't installed the update are at risk of getting their machines compromised by a newly detected backdoor Trojan that Kaspersky Lab researchers dubbed SabPub.
Scoop.it!

The folks at Kaspersky Lab report that there's new Mac malware in the wild, called Backdoor.OSX.SabPub.a.
There are at least two variants being spread through Java exploits. Read this blog post by Don Reisinger on Security & Privacy.
Read more...
Scoop.it!

In the aftermath of Flashback—one of the highest profile malware attacks on the Mac—Ars takes a look back at other security threats that didn't quite make such a big blip on the radar.
===> As Apple continues to increase its share of the PC market, Macs are becoming a viable target for malware authors, sprouting a handful or two of trojans in the last decade. <===
Here are five in particular that were considered (by some) to be harbingers of a great malware infestation for OS X that instead proved to be more bark than bite.
|




