Your new post is loading...

|
Rescooped by
Gust MEES
from ICT Security-Sécurité PC et Internet
September 5, 2012 5:38 AM
|
Der Vorwurf des Hacker-Kollektivs Antisec gegen das FBI wiegt schwer: Auf einem FBI-Laptop habe man eine Datei mit Millionen Seriennummern von iOS-Geräten gefunden. Die Ermittlungsbehörde dementiert. Mehr erfahren: http://www.tageblatt.lu/nachrichten/story/13507432
|
|
Scooped by
Gust MEES
September 4, 2012 6:45 AM
|
La firme de Cupertino n'est visiblement pas au repos ces derniers temps, c’est une liste d’identifiants d’iPhone qui vient d’être mise en ligne par un groupe de hackers. Ces pirates informatiques, dont le groupe semble dériver de la bande de LulzSec qui a été démantelée il y a peu par le FBI, dit avoir obtenu ces données en piratant l’ordinateur d’un agent du FBI. Ce méfait leur a permis de disposer d’une liste de près de 12 millions d’identifiants d’iPhone. Dabs le fichier original obtenu par les pirates, on retrouverait aussi les noms, les numéros de téléphones, les adresses postales et autres données personnelles d’utilisateurs d’iPhone. En savoir plus : http://www.logiciel.net/piratage-des-millions-didentifiants-iphone-devoiles-24063.htm?utm_source=Logiciel.net
|
|
Rescooped by
Gust MEES
from ICT Security-Sécurité PC et Internet
September 1, 2012 7:55 AM
|
(Phys.org)—Spyware sold legally can infect BlackBerrys, iPhones, and other mobile devices, according to a study from two security researchers at the University of Toronto Munk School of Global Affairs' Citizen Lab. Gust MEES: NOBODY IS PERFECT! Read more: http://phys.org/news/2012-09-toronto-mobile-spyware-shadow.html
|
|
Scooped by
Gust MEES
August 29, 2012 11:56 AM
|
|
|
Scooped by
Gust MEES
August 27, 2012 5:07 AM
|
S’il est illusoire de penser qu’il existe une protection optimale contre le vol de données, il est au moins possible d’améliorer l’ordinaire. Dropbox a ainsi mis en place un système d’authentification en deux étapes, plutôt que le simple combo identifiant/mot de passe trop facile à craquer. En savoir plus : http://www.macplus.net/depeche-68044-dropbox-renforce-la-securite
|
|
Scooped by
Gust MEES
August 21, 2012 3:06 PM
|
The malware - dubbed Crisis or Morcut - was not spotted in the wild, but received by the security researcher from VirusTotal in the form of a JAR file, the analysis of which revealed that it contained a .class file named WebEnhancer, and two installers - one for Windows and the other for OS X. Symantec's researchers have continued analyzing the file, and have recently discovered that the Windows version of the threat uses three methods to spread itself: to a removable disk drive, to a VMware virtual machine, and to a Windows Mobile device. Read more: http://www.net-security.org/malware_news.php?id=2235&utm_source=dlvr.it&utm_medium=twitter
|
|
Scooped by
Gust MEES
August 17, 2012 3:28 PM
|
Summary: A well-known security researcher urges iPhone users to distrust the legitimacy of text messages at first sight. A security research who goes by the handle "pod2g" has found a serious security vulnerability in the way iOS devices handle SMS messages, warning that this could be exploited by online criminals. The flaw, which the researcher describes as "severe," exists since the beginning of the implementation of SMS in the iPhone, and is still there in iOS 6 beta 4. According to a post on pod2g's blog, an attacker can exploit this flaw to send an SMS that seems to come from the receiver's bank asking for sensitive information or luring them to a maliciously rigged web site. In another scenario, an attacker could send a spoofed text message to an iPhone user to use as false evidence; or send spoofed messages to manipulate iPhone users into thinking they are receving legitimate SMS messages. A MUST read: http://www.zdnet.com/researcher-finds-serious-sms-spoofing-flaw-on-ios-7000002821/
|
|
Scooped by
Gust MEES
August 10, 2012 9:50 AM
|
|
|
Scooped by
Gust MEES
August 8, 2012 8:33 AM
|
One-quarter of the 30,156 websites tested in the second quarter by Zscaler’s Zulu service, which tests the security of websites, were malicious, according to Zscaler’s second quarter 2012 State of the Web report. The State of the Web report found that users are slow to update browser plug-ins and attackers know it, as witnessed by the Flashback Trojan, which infected over 650,000 Macs leveraging a Java vulnerability. However, the situation is improving. In the second quarter, 35% of installed Adobe Shockwave plug-ins were outdated, down from 52% in the fourth quarter of 2011. Adobe Acrobat was the worst in terms of updating, with close to 62% of plug-ins being outdated in the second quarter, followed by Adobe Shockwave with 38%, Microsoft Outlook with 5.7%, and Adobe Flash with 4.3%. ===> “Outdated plug-ins are vulnerable to exploitation, and the bad guys know that”, Geide observed. <=== Read more: http://www.infosecurity-magazine.com/view/27471/onequarter-of-websites-examined-by-testing-service-were-malicious/?utm_source=twitterfeed&utm_medium=twitter
|
|
Scooped by
Gust MEES
August 7, 2012 2:59 PM
|
Apple (NASDAQ: AAPL) reportedly allowed a hacker to take over a journalist's iCloud account by deceiving the company's tech support team. What affect will this have on the future of Apple's success? This situation could cause irreparable harm to Apple, which touts iCloud as an “automatic and effortless” offer that integrates into users’ apps. The iPhone maker heavily promotes the fact that iCloud allows users to backup and restore their data. Read more: http://www.forbes.com/sites/benzingainsights/2012/08/07/icloud-hacking-could-tarnish-apples-image/
|
|
Scooped by
Gust MEES
August 7, 2012 5:18 AM
|
|
|
Scooped by
Gust MEES
August 6, 2012 10:46 AM
|
|
|
Scooped by
Gust MEES
July 31, 2012 3:50 PM
|
Crisis malware lets attackers install without an administrator password and intercept email, IM, and other communications. Mac users, beware new malware targeting Apple OS X systems that's disguised as an Adobe Flash Player installer.
That warning comes via antivirus software vendor Kaspersky Lab, which said it first spotted the Crisis malware--also known as Morcut--last week. While not widespread, the malware's ability to intercept email and IM, among other features, demonstrates that malicious applications written to target Macs can be just as powerful as malware that comes gunning for PCs. Read more, a MUST...: http://www.informationweek.com/news/security/attacks/240004583?cid=RSSfeed_IWK_security
|
|
|
Scooped by
Gust MEES
September 4, 2012 6:03 PM
|
|
|
Scooped by
Gust MEES
September 4, 2012 6:37 AM
|
AntiSec hacker group has in its possession over 12,000,000 Apple iOS device IDs. To prove it, it has released 1,000,001 IDs to the public. Though they haven’t released them, hackers also claim the real names, addresses and cell phones in some cases accompany the UDIDs on the list, making this leak an even bigger privacy concern. Developing… “During the second week of March 2012, a Dell Vostro notebook, used by Supervisor Special Agent Christopher K. Stangl from FBI Regional Cyber Action Team and New York FBI Office Evidence Response Team was breached using the AtomicReferenceArray vulnerability on Java, during the shell session some files were downloaded from his Desktop folder one of them with the name of “NCFTA_iOS_devices_intel.csv” turned to be a list of 12,367,232 Apple iOS devices including Unique Device Identifiers (UDID), user names, name of device, type of device, Apple Push Notification Service tokens, zipcodes, cellphone numbers, addresses, etc,” claims Antisec. Read more: http://mashable.com/2012/09/04/hackers-apple-device-id/?utm_source=feedburner&utm_medium=feed&utm_campaign=Feed%3A+Mashable+%28Mashable%29
|
|
Scooped by
Gust MEES
August 30, 2012 1:22 AM
|
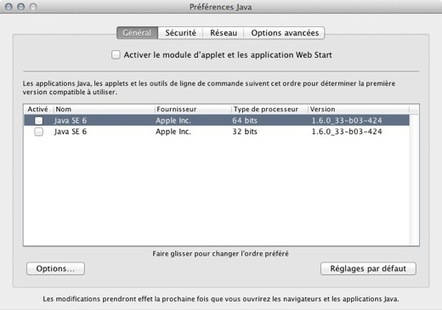
Actualité Apple : OS X : désactiver JAVA en attente d'un correctif de sécurité... JAVA ne se traine pas une formidable réputation en matière de sécurité, surtout sur nos Mac où Apple a souvent fait preuve d'une formidable lenteur pour mettre à jour la machine virtuelle JAVA. Désormais c'est Oracle qui préside aux destinées de la brique logicielle sur nos machines pommées. En attendant, si vous n'en avez pas un besoin immédiat et absolu, vous pouvez simplement désactiver JAVA pour régler la question. Pour cela, direction le dossier Utilitaires de votre dossier Applications. Lancez Préférences JAVA et, dans l'onglet gGénéral, désactivez Java SE 7 (oui, l'image montre un système avec JAVA 6). Et voilà. Pour réactiver, procédure inverse.
|
|
Scooped by
Gust MEES
August 24, 2012 6:06 PM
|
|
|
Scooped by
Gust MEES
August 20, 2012 11:28 AM
|
Eine Schwachstelle im Apple-Betriebssystem iOS könnte dazu führen, dass Kurznachrichten an die falsche Nummer geschickt werden. Der Blogger Pod2g will Hinweise für eine Sicherheitslücke in iOS ausgemacht haben, die den Versand von SMS-Nachrichten auf dem iPhone betrifft. So wäre es möglich, Kurznachrichten im PDU-Format zu verfassen, deren Zieladresse sich über einen editierbaren Abschnitt namens PDU (Protocol Description Unit) ändern ließe. Antwortet der Nutzer auf eine solche SMS, dann könnte die Antwort nicht an den ehemaligen Absender, sondern an ein fremdes Smartphone geschickt werden. Mehr lesen: http://www.pcwelt.de/news/Apple-Sicherheitsluecke-in-iOS-SMS-System-aufgedeckt-6477693.html?r=661529125805606&lid=191580
|
|
Scooped by
Gust MEES
August 10, 2012 10:02 AM
|
|
|
Scooped by
Gust MEES
August 9, 2012 10:15 AM
|
|
|
Scooped by
Gust MEES
August 8, 2012 8:22 AM
|
According to Wired, Amazon no longer allows people to call Amazon and change account settings such as email addresses and credit cards, and Apple has temporarily suspended the option of asking for an AppleID password reset over the phone. Read more: http://www.net-security.org/secworld.php?id=13392
|
|
Scooped by
Gust MEES
August 7, 2012 2:51 PM
|
Daten gelöscht aus der Ferne, Twitter- und Gmail-Account gekapert – ein amerikanischer Journalist gibt Apple die Schuld an einem besonders heftigen Hacker-Angriff. ===> Mittlerweile habe er wieder die Kontrolle über seine Accounts und Geräte. Apple arbeite an einer Wiederherstellung seiner Daten, die insofern erleichtert wird, weil dem Macbook der Strom ausging, bevor alle Daten gelöscht werden konnten. <=== Gust MEES: das muss man unbedingt lesen und schmunzeln ist garantiert, LOL ;) http://www.pcwelt.de/news/Apple-soll-schuld-haben-an-Hacker-Angriff-6182702.html?r=761528923305658&amp;amp;lid=189335
|
|
Scooped by
Gust MEES
August 6, 2012 9:02 AM
|
Summary: Gizmodo's Twitter account was recently hacked, after a former employee's iCloud account was breached, and all his Apple devices (iPhone, iPad, MacBook Air) were remotely wiped. Read more (nobody is perfect)...: http://knolinfos.visibli.com/share/yETAZs
|