

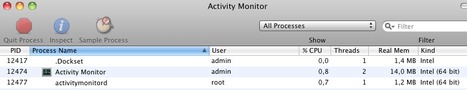

A sample of a new Mac spyware called OSX/Dockster.A was found today on Virus Total. This trojan is currently considered low risk as it is not known to have infected users. It has backdoor functiona...

 Your new post is loading...
 Scoop.it! A sample of a new Mac spyware called OSX/Dockster.A was found today on Virus Total. This trojan is currently considered low risk as it is not known to have infected users. It has backdoor functiona... 
No comment yet.
Sign up to comment
Scoop.it!
The malware threat on Macs is real, and should not be underestimated.
SophosLabs, is a new variant of the OSX/Imuler Trojan horse. In the past, earlier variants of the OSX/Imuler malware has been spread via topless photos of a Russian supermodel or embedded deep inside boobytrapped PDF files.
If your Mac was successfully infected by malware like this, you have effectively given remote control of your computer and your data to an invisible and unknown party.
===> They could steal files from your Mac, spy on your emails, and plant further malware onto your systems. <===
Read more, a MUST: http://nakedsecurity.sophos.com/2012/11/13/new-mac-trojan/
Scoop.it!
Opera recently released version 12.10 of its flagship browser, patching six security vulnerabilities on Mac OS X systems.
Read more and update: http://www.zdnet.com/opera-for-mac-os-x-patches-six-security-vulnerabilities-7000007174/
Scoop.it!
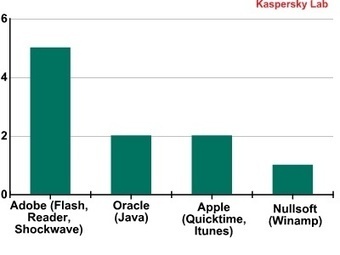
L'éditeur de logiciel de sécurité Kaspersky a publié quelques statistiques sur les failles de sécurité découvertes dans le monde au troisième trimestre. Pour délivrer ces chiffres, Kaspersky s'appuie sur la base d'utilisateurs de ses produits.
On trouve ensuite des logiciels d'Adobe (Flash, Adobe Reader et Shockwave) qui est le plus représenté dans ce top 10 avec cinq mentions. Apple est également présent avec des failles concernant QuickTime (14 % des utilisateurs concernés) et iTunes (12 %). Nullsoft avec Winamp ferme la marche.
En savoir plus :
http://www.macg.co/news/voir/257709/vulnerabilites-kaspersky-pointe-adobe-oracle-et-apple
Scoop.it!
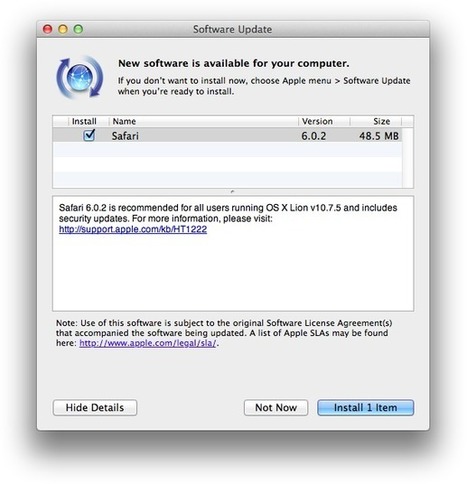
Two security vulnerabilities in Safari are being addressed in an update of the browser software released by Apple earlier today. This update coincides with Apple’s iOS 6.0.1 software update, which addressed multiple security problems. The 48.5 MB update to Safari 6.0.2 is available for OS X Lion and OS X Mountain Lion, and is recommended as it fixes security flaws in the software.
===> UPDATE asap!!! <===
Read more, a MUST: http://www.intego.com/mac-security-blog/safari-update-fixes-security-flaws/
Scoop.it!
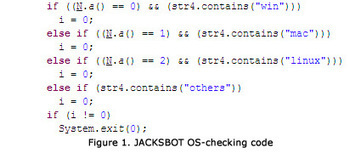
Two weeks ago, Mac security software company Intego discovered malware which it classified as "a new Java backdoor trojan called Java/Jacksbot.A.” New threats are discovered all the time, but Intego later concluded that even though Jacksbot is a variant of the Java remote access tool (RAT) created by the jailbreaking group Redpois0n, it can target multiple platforms.
The malware writers behind JACKSBOT may just be testing the waters for a successful multiplatform malware; however for now they appear to be unwilling to invest the time and resources to develop the code more completely.
===> It’s likely that the authors will continue to improve the code to fully support infection for OS X and Linux. <===
Read more, a MUST:
Scoop.it!
Despite the Mac reputation as being more secure because of Apple’s tight control over its vertically integrated ecosystem, Mac-specific malware and advanced persistent attacks (APTs) against human rights groups is on the rise, cautions Citizen Lab...
Read more, a MUST:
Scoop.it!

Intego has discovered a new version of the Imuler Trojan horse, which was first discovered in September 2011. Right now the risk is considered to be low – a sample of this malware was found on the VirusTotal website in a ZIP archive named “your dirty pics.zip.” Inside the ZIP file is an application with an icon making it look like an image.
If the file is run, ===> it installs a backdoor without the need for an admin password. <===
Read more: http://www.intego.com/mac-security-blog/new-imuler-variant-found-steer-clear-of-your-dirty-pics/
Scoop.it!
Apple has released Mac OS X 10.8.2 with security updates for Snow Leopard, Lion, Mountain Lion, iOS and iTunes – along with a single sign-on feature for Facebook and a Java patch.
Apple recommends that users upgrade using System Update, which can determine what fixes are already installed on the system, thus lightening the heft of the download.
As for the Facebook angle, users can now opt to have Facebook contact information integrated with the Mac’s native Contacts and Game Center applications. Users gain a single sign-on and the ability to be alerted to Facebook activity via Mac OS X's Notification Center.
===> UPDATE!!! <===
Read more:
Scoop.it!
As the popularity of Mac OS has increased, so has its attractiveness to online criminals. This cartoon busts some of the myths that still prevail when it com...
Scoop.it!
BlueToad, a Florida-based digital edition publishing company, has announced that the recent massive Apple UDID leak originated from their own servers, and not an FBI laptop.
Read more: http://www.net-security.org/secworld.php?id=13560
Scoop.it!
Cybercriminals are working on more complex schemes to wage attacks on PCs, laptops, and smartphones.
A new report shows that: ===> every single device that connects to the Internet is in danger. <===
Read this blog post by Dara Kerr on Security & Privacy:
Scoop.it!

Summary: Both the FBI and now Apple have come forward to state that they had no involvement the ongoing 'UDID-gate,' which led to more than 1 million iOS device codes leaking to the Web.
Read more: http://www.zdnet.com/apple-we-didnt-pass-iphone-ipad-device-ids-to-fbi-7000003786/?s_cid=e550
|
Scoop.it!
McAfee publie son rapport trimestriel sur les menaces informatiques, qui analyse notamment les techniques du cybercrime et l’évolution mondiale des cyberattaques. Le rapport dévoile de nouveaux détails sur l’opération « High Roller », ainsi que des chiffres en matière de logiciels malveillants visant les mobiles, qui ont quasiment doublé par rapport au trimestre précédent, et la hausse sans précédent des violations des bases de données.
McAfee Labs a également constaté une hausse importante de certaines catégories de logiciels malveillants, dont les logiciels de demande de rançons ou ransomware et les fichiers binaires signés.
===> Les rootkits et les logiciels malveillants ciblant les Mac continuent eux aussi d’augmenter, à l’instar des chevaux de Troie voleurs de mots de passe et des logiciels malveillants autoexécutables, qui ont enregistré une hausse considérable. <===
En savoir plus :
http://www.globalsecuritymag.fr/Rapport-trimestriel-McAfee,20121114,33708.html
Scoop.it!
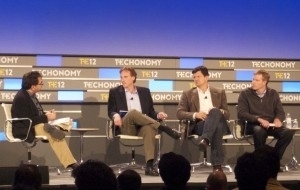
Who is the best among the "fantastic four" Internet companies: Apple, Facebook, Google and Amazon?
===> But which company is the most vulnerable in today’s quickly changing market? None other than Apple, according to one panelist speaking at the Techonomy conference. <===
Despite Apple’s massive market cap and blockbuster products, it’s the most vulnerable because it has to constantly maintain its innovation advantage in hardware to keep consumers coming back, said Alec Ellison, chairman of investment banking at Jefferies.
Read more:
Scoop.it!

New QuickTime fixes a number of security vulnerabilities!
===> UPDATE asap! <===
Scoop.it!
Apple released its first security updates to iOS 6. Version 6.0.1 includes patches for critical vulnerabilities in the operating system kernel, Passcode Lock and WebKit.
Read more: http://threatpost.com/en_us/blogs/apple-patches-kernel-passcode-lock-and-webkit-flaws-ios-601-110212
Scoop.it!
Company bolsters anti-hacker defences...
Apple has released an update for its Safari web browser designed to fix a number of security flaws.
Read more, a MUST:
Scoop.it!

Apple was eager to promote the many new features in iOS6, but avoided mention of one: IFA - or identifier for advertisers - the company's newest device tracking technology.
Read more, a MUST: http://knolinfos.visibli.com/share/DBFsX6
Scoop.it!
|

|
Scooped by
Gust MEES
September 20, 2012 5:22 PM
|
Scoop.it!
Two Dutch researchers successfully hacked a patched iPhone 4S, exploit a vulnerability also likely present in the new iPhone 5 due to be released tomorrow.
Joost Pol and Daan Keuper won the mobile Pwn2Own contest yesterday at EUSecWest event in Amsterdam by compromising a fully patched iPhone 4S device and stealing contacts, browsing history, photos and videos from the phone.
The pair was able to build an exploit for a vulnerability in WebKit to beat Apple's code-signing features and the MobileSafari sandbox. The same bug is present in the iOS6 Golden Master development code base, meaning iPhone 5 is vulnerable to the same exploit. Apple iPads and iPod Touch devices are also vulnerable, Pol and Keuper said, adding that it took them three weeks find the flaw and write an exploit.
Read more, a MUST:
|
|
Rescooped by
Gust MEES
from 21st Century Learning and Teaching
September 12, 2012 8:35 AM
|
Scoop.it!

Early last week the personal diary app Path became the fulcrum of a massive discussion about how cavalier mobile apps are getting with harvesting your, presumably, personal information. ...
Apps that do send data, with no warning
Foursquare stands alone here as an app that was, until an update issued on February 14th, sending personal data with no warning. This is similar to the previous behavior of Path that got it in so much hot water. Since the update, Foursqare now warns users before uploading data. Foursquare says that, while it was uploading the data, it was not storing it.
Foursquare (Email, Phone Numbers no warning)
Read more, a MUST:
|
|
Rescooped by
Gust MEES
from ICT Security-Sécurité PC et Internet
September 11, 2012 7:53 AM
|
Scoop.it!
La société américaine BlueToad explique s'être fait voler ces données il y a deux semaines. Le vol présumé à un agent du FBI perd en crédibilité.
La fuite de plus d'un million d'identifiants de terminaux Apple (iPhone et iPad) de la semaine dernière trouve une explication. Dans un entretien à NBC News, le PDG de l'éditeur d'applications BlueToad, Paul DeHart, déclare que les données publiées par un membre d'Anonymous ont été dérobées à sa société il y a deux semaines. Les serveurs les contenant n'étaient, semble-t-il, pas assez protégés.
En savoir plus :
|
|
Scooped by
Gust MEES
September 7, 2012 6:53 AM
|
Scoop.it!
By turning off Java by default, Apple is making customers choose whether to take the risk in using the troubled browser software...
Apple's patches automatically deactivated the Java plug-ins in browsers, leaving it up to Mac users to turn them back on. Until a few months ago, Apple had handled the release of all Java updates. Now, customers can download and install fixes directly from Oracle.
Read more:
|
|
Scooped by
Gust MEES
September 6, 2012 7:36 AM
|
Scoop.it!
Apple patcht vier gravierende Sicherheitslücken in Java 6 für Mac OS X
Betroffen sind Mac OS X 10.6, 10.7 und 10.8. Die Lücken lassen sich mit manipulierten Java-Applets ausnutzen. Sie sind seit dem durch den von Oracle in der vergangenen Woche bereitgestellten Patch öffentlich bekannt.
Da Apple für die Aktualisierung von Java 6 verantwortlich ist, mussten Nutzer von OS X warten, bis das Unternehmen aus Cupertino ein Update herausgibt. Ab Java 7 ist Oracle für die Mac-OS-Updates zuständig. Ein entsprechendes Update wurde letzte Woche bereitgestellt. Allerdings liegt Java 7 unter Mac OS nur als 64-Bit-Version vor, sodass 32-Bit-Browser wie Google Chrome noch auf die ältere Version zurückgreifen.
Zudem wurde auch in diesem Patch eine Sicherheitslücke entdeckt, die Angreifer missbrauchen können, um Schadcode einzuschleusen udn auszuführen. Das polnische Sicherheitsunternehmen Security Explorations hatte den Fehler nur wenige Stunden nachdem das Update bereitgestellt worden war entdeckt.
Mehr erfahren:





