Apple, Mac, MacOS, iOS4, iPad, iPhone and (in)security...
18.2K views | +9 today
Apple, Mac, MacOS, iOS4, iPad, iPhone and (in)security...
Everything related to the (in)security of Apple products
Curated by Gust MEES
Your new post is loading...
Scooped by Gust MEES
July 24, 2019 6:45 AM
Scoop.it!

Apple’s July patchfest fixes bugs in multiple products | #CyberSecurity #NobodyIsPerfect

Apple’s July patchfest fixes bugs in multiple products | #CyberSecurity #NobodyIsPerfect | Apple, Mac, MacOS, iOS4, iPad, iPhone and (in)security... | Scoop.it

Apple released fixes for various products this week, including several nasty arbitrary code execution (ACE) flaws, and a bug that has been public with proof-of-concept code for two months.

CVE-2019-8656, discovered by cybersecurity researcher Filippo Cavallarin, enabled an attacker to bypass Apple’s Gatekeeper functionality with a suitably formed Zip file. Gatekeeper is the Mac function that asks you if you want to run untrusted content downloaded from the web. Apple was supposed to have fixed this by mid-May following a 90-day responsible disclosure period, but didn’t, so Cavallarin published proof of concept code.

The fix was part of a patchfest addressing 48 separate entries in the CVE database. The patches spanned these Apple products:

iOS 12.4
tvOS 12.4 (the Apple TV operating system)
Safari browser 12.1.2
iTunes 12.9.6 for Windows
iCloud for Windows 10.6 and 7.13
watchOS 5.3
macOS Mojave 10.14.6, High Sierra, and Sierra


Many of the fixes addressed single bugs that affected multiple Apple products, showing how tightly integrated Apple’s code base is. One of the most notable was for the company’s WebKit browser engine, which it mandates for other browser vendors (Chrome is forced to use WebKit on Apple operating systems rather than its own Blink engine, for example).


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


Gust MEES's insight:

Apple released fixes for various products this week, including several nasty arbitrary code execution (ACE) flaws, and a bug that has been public with proof-of-concept code for two months.

CVE-2019-8656, discovered by cybersecurity researcher Filippo Cavallarin, enabled an attacker to bypass Apple’s Gatekeeper functionality with a suitably formed Zip file. Gatekeeper is the Mac function that asks you if you want to run untrusted content downloaded from the web. Apple was supposed to have fixed this by mid-May following a 90-day responsible disclosure period, but didn’t, so Cavallarin published proof of concept code.

The fix was part of a patchfest addressing 48 separate entries in the CVE database. The patches spanned these Apple products:

iOS 12.4
tvOS 12.4 (the Apple TV operating system)
Safari browser 12.1.2
iTunes 12.9.6 for Windows
iCloud for Windows 10.6 and 7.13
watchOS 5.3
macOS Mojave 10.14.6, High Sierra, and Sierra


Many of the fixes addressed single bugs that affected multiple Apple products, showing how tightly integrated Apple’s code base is. One of the most notable was for the company’s WebKit browser engine, which it mandates for other browser vendors (Chrome is forced to use WebKit on Apple operating systems rather than its own Blink engine, for example).


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


No comment yet.
Scooped by Gust MEES
July 9, 2019 6:25 AM
Scoop.it!

Le client macOS de Zoom peut activer la webcam de votre Mac sans votre accord

Le client macOS de Zoom peut activer la webcam de votre Mac sans votre accord | Apple, Mac, MacOS, iOS4, iPad, iPhone and (in)security... | Scoop.it

Zoom est l’une des solutions de visioconférence les plus populaires, surtout dans le monde de l’entreprise. Comme Skype ou Hangout, cette app permet de créer des réunions virtuelles que les participants peuvent rejoindre avec leur ordinateur et une webcam. Le chercheur en sécurité Jonathan Leitschuh a découvert plusieurs failles de sécurité dans l’app macOS du service, dont la plus importante permet à un site web d’activer la webcam d’un Mac sans aucune interaction de la part de l’utilisateur.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


https://www.scoop.it/topic/apple-mac-ios4-ipad-iphone-and-in-security/?&tag=Zoom


Gust MEES's insight:

Zoom est l’une des solutions de visioconférence les plus populaires, surtout dans le monde de l’entreprise. Comme Skype ou Hangout, cette app permet de créer des réunions virtuelles que les participants peuvent rejoindre avec leur ordinateur et une webcam. Le chercheur en sécurité Jonathan Leitschuh a découvert plusieurs failles de sécurité dans l’app macOS du service, dont la plus importante permet à un site web d’activer la webcam d’un Mac sans aucune interaction de la part de l’utilisateur.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


https://www.scoop.it/topic/apple-mac-ios4-ipad-iphone-and-in-security/?&tag=Zoom


No comment yet.
Scooped by Gust MEES
June 28, 2019 12:58 PM
Scoop.it!

OSX/CrescentCore: Mac malware designed to evade antivirus #CyberSecurity 

OSX/CrescentCore: Mac malware designed to evade antivirus #CyberSecurity  | Apple, Mac, MacOS, iOS4, iPad, iPhone and (in)security... | Scoop.it
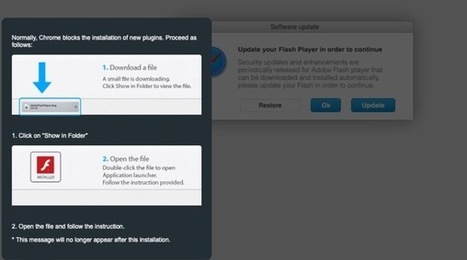
Meet OSX/CrescentCore, the next generation of fake Flash Player malware—now redesigned to evade antivirus detection.

Hot on the heels of Intego's discovery of OSX/Linker and being the first to detect OSX/NewTab, the Intego team has discovered in the wild another previously unknown bit of malware that installs other unwanted software—but only if you're not running third-party endpoint protection software, and only if your operating system isn't running inside a virtual machine.

Intego has observed this malware in multiple places across the Web, from sketchy copyright-infringing download sites to rogue, high-ranking, non-sponsored Google search results links.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


Gust MEES's insight:

Meet OSX/CrescentCore, the next generation of fake Flash Player malware—now redesigned to evade antivirus detection.

Hot on the heels of Intego's discovery of OSX/Linker and being the first to detect OSX/NewTab, the Intego team has discovered in the wild another previously unknown bit of malware that installs other unwanted software—but only if you're not running third-party endpoint protection software, and only if your operating system isn't running inside a virtual machine.

Intego has observed this malware in multiple places across the Web, from sketchy copyright-infringing download sites to rogue, high-ranking, non-sponsored Google search results links.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


No comment yet.
Scooped by Gust MEES
June 21, 2019 6:21 PM
Scoop.it!

Firefox Zero-Day Used to Install Mac Malware | #CyberSecurity #Apple #NobodyIsPerfect #Browsers

Firefox Zero-Day Used to Install Mac Malware | #CyberSecurity #Apple #NobodyIsPerfect #Browsers | Apple, Mac, MacOS, iOS4, iPad, iPhone and (in)security... | Scoop.it

Before either of those patches rolled out, Mozilla became aware of an attack leveraging both vulnerabilities. At the time, we only knew the attacks had something to do with Coinbase as the initial bug report came from a researcher who works on both Google’s Project Zero and the Coinbase security team. Now, Coinbase’s head of security Philip Martin says the attack was aimed at Coinbase employees and not users. Martin also notes that other exchanges were targeted in the attacks, although none have stepped forward.

Meanwhile, Apple security expert Patrick Wardle published an analysis of malware that appears to have installed itself on a fully updated Mac. The hash provided by Wardle matches one from Martin, and the victim of the attack was involved with a cryptocurrency exchange until very recently. Unfortunately, the malware is novel and avoided Apple’s protection mechanisms, but Wardle believes that Apple will have a patch to change the way macOS scans files downloaded by applications rather than the user.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


https://www.scoop.it/topic/apple-mac-ios4-ipad-iphone-and-in-security/?&tag=Browsers


Gust MEES's insight:

Before either of those patches rolled out, Mozilla became aware of an attack leveraging both vulnerabilities. At the time, we only knew the attacks had something to do with Coinbase as the initial bug report came from a researcher who works on both Google’s Project Zero and the Coinbase security team. Now, Coinbase’s head of security Philip Martin says the attack was aimed at Coinbase employees and not users. Martin also notes that other exchanges were targeted in the attacks, although none have stepped forward.

Meanwhile, Apple security expert Patrick Wardle published an analysis of malware that appears to have installed itself on a fully updated Mac. The hash provided by Wardle matches one from Martin, and the victim of the attack was involved with a cryptocurrency exchange until very recently. Unfortunately, the malware is novel and avoided Apple’s protection mechanisms, but Wardle believes that Apple will have a patch to change the way macOS scans files downloaded by applications rather than the user.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


https://www.scoop.it/topic/apple-mac-ios4-ipad-iphone-and-in-security/?&tag=Browsers


No comment yet.
Scooped by Gust MEES
May 27, 2019 9:42 AM
Scoop.it!

Unpatched Apple macOS Vulnerability Lets Malicious Apps Run | #CyberSecurity #Apps #Gatekeeper #NobodyIsPerfect

Unpatched Apple macOS Vulnerability Lets Malicious Apps Run | #CyberSecurity #Apps #Gatekeeper #NobodyIsPerfect | Apple, Mac, MacOS, iOS4, iPad, iPhone and (in)security... | Scoop.it

AppleInsider reports that a vulnerability first disclosed to Apple three months ago remains unpatched and now the security researcher who found it has gone public. Filippo Cavallarin has published details of how the vulnerability enables a user to be tricked into running malicious applications, bypassing the Gatekeeper function in the process.

Gatekeeper is the Apple mechanism that has, since 2012, been enforcing the code signing and verification of application downloads. If a user were to download an app outside of the Mac App Store then Gatekeeper would kick in and prevent it from running without the express consent of the user. In theory anyway.

Cavallarin says that, on macOS X version 10.14.5 (Mojave) and below, it is possible to "easily bypass Gatekeeper in order to execute untrusted code without any warning or user's explicit permission." According to Cavallarin, he contacted Apple February 22 and the vendor is aware of the issue. It was, he says, "supposed to be addressed, according to the vendor, on May 15, but Apple started dropping my emails." As a 90 day disclosure deadline, which he says Apple is aware of, has now passed, Cavallarin has made details of the vulnerability public.


Learn more / En savoir plus / Mehr erfahren:


http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


https://www.scoop.it/topic/apple-mac-ios4-ipad-iphone-and-in-security/?&tag=Gatekeeper


Gust MEES's insight:

AppleInsider reports that a vulnerability first disclosed to Apple three months ago remains unpatched and now the security researcher who found it has gone public. Filippo Cavallarin has published details of how the vulnerability enables a user to be tricked into running malicious applications, bypassing the Gatekeeper function in the process.

Gatekeeper is the Apple mechanism that has, since 2012, been enforcing the code signing and verification of application downloads. If a user were to download an app outside of the Mac App Store then Gatekeeper would kick in and prevent it from running without the express consent of the user. In theory anyway.

Cavallarin says that, on macOS X version 10.14.5 (Mojave) and below, it is possible to "easily bypass Gatekeeper in order to execute untrusted code without any warning or user's explicit permission." According to Cavallarin, he contacted Apple February 22 and the vendor is aware of the issue. It was, he says, "supposed to be addressed, according to the vendor, on May 15, but Apple started dropping my emails." As a 90 day disclosure deadline, which he says Apple is aware of, has now passed, Cavallarin has made details of the vulnerability public.


Learn more / En savoir plus / Mehr erfahren:


http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


https://www.scoop.it/topic/apple-mac-ios4-ipad-iphone-and-in-security/?&tag=Gatekeeper


No comment yet.
Scooped by Gust MEES
March 4, 2019 11:14 AM
Scoop.it!

'High severity' kernel security flaw found in macOS file system | #Apple #CyberSecurity 

'High severity' kernel security flaw found in macOS file system | #Apple #CyberSecurity  | Apple, Mac, MacOS, iOS4, iPad, iPhone and (in)security... | Scoop.it
Google's Project Zero has revealed a "high severity" flaw in the macOS kernel, one which could allow an attacker to make changes to a file without macOS being informed, an issue that could lead to infected files being opened and allowing more malicious activities to become available to abuse.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/topic/apple-mac-ios4-ipad-iphone-and-in-security


Gust MEES's insight:

Google's Project Zero has revealed a "high severity" flaw in the macOS kernel, one which could allow an attacker to make changes to a file without macOS being informed, an issue that could lead to infected files being opened and allowing more malicious activities to become available to abuse.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/topic/apple-mac-ios4-ipad-iphone-and-in-security


No comment yet.
Scooped by Gust MEES
March 4, 2019 10:21 AM
Scoop.it!

Thunderclap : une faille du Thunderbolt affecte tous les Mac produits depuis 2011 | #Apple #CyberSecurity

Thunderclap : une faille du Thunderbolt affecte tous les Mac produits depuis 2011 | #Apple #CyberSecurity | Apple, Mac, MacOS, iOS4, iPad, iPhone and (in)security... | Scoop.it

Des chercheurs en sécurité ont mis en évidence une faille de sécurité permettant de subtiliser des données en passant par un périphérique Thunderbolt. 


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/topic/apple-mac-ios4-ipad-iphone-and-in-security


https://www.scoop.it/topic/apple-mac-ios4-ipad-iphone-and-in-security/?&tag=Thunderclap


Gust MEES's insight:

Des chercheurs en sécurité ont mis en évidence une faille de sécurité permettant de subtiliser des données en passant par un périphérique Thunderbolt. 


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/topic/apple-mac-ios4-ipad-iphone-and-in-security


https://www.scoop.it/topic/apple-mac-ios4-ipad-iphone-and-in-security/?&tag=Thunderclap


No comment yet.
Scooped by Gust MEES
February 15, 2019 3:23 AM
Scoop.it!

Unpatched Apple macOS Hole Exposes Safari Browsing History | #CyberSecurity #Browsers

Unpatched Apple macOS Hole Exposes Safari Browsing History | #CyberSecurity #Browsers | Apple, Mac, MacOS, iOS4, iPad, iPhone and (in)security... | Scoop.it

There are no permission dialogues for apps in certain folders for macOS Mojave, which allows a malicious app to spy on browsing histories..

A design flaw in Apple’s macOS could allow a malicious application to steal victims’ Safari web browsing history.

The security hole exists in every version of the Mac’s Mojave operating system, including macOS Mojave 10.14.3 Supplemental Update recently released on Feb. 7. That’s according to Mac and iOS developer Jeff Johnson, who disclosed the bug over the weekend.

The issue specifically exists in the fact that there are no permission dialogues for apps in certain folders. While enforcing permissions would mean that these folders could only be accessed by certain apps, the alternative (no permissions required) in the case of ~/Library/Safari means that apps are allowed to look inside it.

And inside the folder is a user’s entire web browsing history (as well as reading list archives, remote notifications, template icons and more).


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/


Gust MEES's insight:

There are no permission dialogues for apps in certain folders for macOS Mojave, which allows a malicious app to spy on browsing histories..

A design flaw in Apple’s macOS could allow a malicious application to steal victims’ Safari web browsing history.

The security hole exists in every version of the Mac’s Mojave operating system, including macOS Mojave 10.14.3 Supplemental Update recently released on Feb. 7. That’s according to Mac and iOS developer Jeff Johnson, who disclosed the bug over the weekend.

The issue specifically exists in the fact that there are no permission dialogues for apps in certain folders. While enforcing permissions would mean that these folders could only be accessed by certain apps, the alternative (no permissions required) in the case of ~/Library/Safari means that apps are allowed to look inside it.

And inside the folder is a user’s entire web browsing history (as well as reading list archives, remote notifications, template icons and more).


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/


No comment yet.
Scooped by Gust MEES
February 7, 2019 1:42 PM
Scoop.it!

Apple releases iOS 12.1.4, fixes iPhone FaceTime spying bug | #CyberSecurity #Updates 

Apple releases iOS 12.1.4, fixes iPhone FaceTime spying bug | #CyberSecurity #Updates  | Apple, Mac, MacOS, iOS4, iPad, iPhone and (in)security... | Scoop.it

Apple has released iOS 12.1.4. It's a patch that fixes a bug that allowed users to spy on others by activating a group FaceTime call without the user's consent. What made this bug so serious was how trivial it was to leverage, and it forced Apple to pull the plug on the feature at the server end while it developed a fix.

Following the rollout of iOS 12.1.4, Apple will switch group FaceTime calls back on, but only for those who have applied the update. Group FaceTime will remain disabled for all iOS users running iOS 12.1.3 or earlier. So, if you like group FaceTime calls, this update is a must-have for you (and those you called).

This bug, likely the most serious to hit iPhone and iPad users, has already resulted in at least one lawsuit. 


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/


Gust MEES's insight:

Apple has released iOS 12.1.4. It's a patch that fixes a bug that allowed users to spy on others by activating a group FaceTime call without the user's consent. What made this bug so serious was how trivial it was to leverage, and it forced Apple to pull the plug on the feature at the server end while it developed a fix.

Following the rollout of iOS 12.1.4, Apple will switch group FaceTime calls back on, but only for those who have applied the update. Group FaceTime will remain disabled for all iOS users running iOS 12.1.3 or earlier. So, if you like group FaceTime calls, this update is a must-have for you (and those you called).

This bug, likely the most serious to hit iPhone and iPad users, has already resulted in at least one lawsuit. 


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/


No comment yet.
Scooped by Gust MEES
February 7, 2019 11:49 AM
Scoop.it!

Analyse ohne Einverständnis: Populäre iPhone-Apps machen heimlich Screenshots | #CyberSecurity #Privacy #Tracking #Apple 

Analyse ohne Einverständnis: Populäre iPhone-Apps machen heimlich Screenshots | #CyberSecurity #Privacy #Tracking #Apple  | Apple, Mac, MacOS, iOS4, iPad, iPhone and (in)security... | Scoop.it

Einige weltweit oft genutzte iPhone-Apps zeichnen alle Eingaben des Nutzers auf. Dies geschieht zwar mit einem bisher legalen Analyse-Tool, aber oft heimlich und ohne ausreichende Absicherung. Auch Kreditkartendaten sind in Gefahr.

Es ist verständlich, dass App-Entwickler gerne das Nutzerverhalten analysieren, um ihre Anwendungen zu optimieren. Wenn dies offen, sicher und mit Einverständnis des Nutzers geschieht, ist dagegen auch nichts einzuwenden. "Techcrunch" hat allerdings ein Tool ausfindig gemacht, dass in weltweit populären Apps Eingaben detailliert aufzeichnet, wobei Nutzer gar nicht oder nur völlig unzureichend informiert werden. Die Sicherheitsmaßnahmen sind außerdem gelegentlich so schlampig, dass Angreifer leichtes Spiel haben, sensible Daten zu erbeuten.


In Echtzeit sehen, was der Nutzer tut
Der Überwachungsdienst heißt Glassbox. Unter anderem kommt das Tool in den Apps von Santander, Citibank, Singapore Airlines oder Expedia zum Einsatz, wie der Website des britischen Unternehmens zu entnehmen ist. Es erlaubt den Entwicklern unter anderem, kontinuierliche Screenshots aufzunehmen, wenn die App genutzt wird. In einem Tweet umschreibt Glassbox das so: "Stell dir vor, deine Website oder App könnte in Echtzeit genau sehen, was deine Nutzer gerade tun und warum sie es tun. Das ist keine hypothetische Frage mehr, sondern eine echte Möglichkeit. Das ist Glassbox. Erlebe es selbst."


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/


Gust MEES's insight:

Einige weltweit oft genutzte iPhone-Apps zeichnen alle Eingaben des Nutzers auf. Dies geschieht zwar mit einem bisher legalen Analyse-Tool, aber oft heimlich und ohne ausreichende Absicherung. Auch Kreditkartendaten sind in Gefahr.

Es ist verständlich, dass App-Entwickler gerne das Nutzerverhalten analysieren, um ihre Anwendungen zu optimieren. Wenn dies offen, sicher und mit Einverständnis des Nutzers geschieht, ist dagegen auch nichts einzuwenden. "Techcrunch" hat allerdings ein Tool ausfindig gemacht, dass in weltweit populären Apps Eingaben detailliert aufzeichnet, wobei Nutzer gar nicht oder nur völlig unzureichend informiert werden. Die Sicherheitsmaßnahmen sind außerdem gelegentlich so schlampig, dass Angreifer leichtes Spiel haben, sensible Daten zu erbeuten.


In Echtzeit sehen, was der Nutzer tut
Der Überwachungsdienst heißt Glassbox. Unter anderem kommt das Tool in den Apps von Santander, Citibank, Singapore Airlines oder Expedia zum Einsatz, wie der Website des britischen Unternehmens zu entnehmen ist. Es erlaubt den Entwicklern unter anderem, kontinuierliche Screenshots aufzunehmen, wenn die App genutzt wird. In einem Tweet umschreibt Glassbox das so: "Stell dir vor, deine Website oder App könnte in Echtzeit genau sehen, was deine Nutzer gerade tun und warum sie es tun. Das ist keine hypothetische Frage mehr, sondern eine echte Möglichkeit. Das ist Glassbox. Erlebe es selbst."


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/


No comment yet.
Scooped by Gust MEES
January 26, 2019 5:38 AM
Scoop.it!

VeryMal : un malware cible macOS grâce à la stéganographie | #Apple #CyberSecurity #Steganography

VeryMal : un malware cible macOS grâce à la stéganographie | #Apple #CyberSecurity #Steganography | Apple, Mac, MacOS, iOS4, iPad, iPhone and (in)security... | Scoop.it

Des chercheurs en sécurité ont débusqué un malware ciblant récemment macOS, en se cachant dans une fausse mise à jour de Flash Player d'Adobe.

Une tentative d'infection de macOS par « VeryMal » a été détectée et analysée par Confiant et Malwarebytes, entre le 11 et le 13 janvier 2019. Le cheval de Troie « Shlayer » s'installait lorsque l'utilisateur acceptait de mettre à jour un programme se faisant passer pour Flash Player. Sur seulement trois jours, plus de 5 millions de Mac auraient été visés.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/?&tag=Steganography


https://www.scoop.it/t/securite-pc-et-internet/?&tag=Steganography


Gust MEES's insight:

Des chercheurs en sécurité ont débusqué un malware ciblant récemment macOS, en se cachant dans une fausse mise à jour de Flash Player d'Adobe.

Une tentative d'infection de macOS par « VeryMal » a été détectée et analysée par Confiant et Malwarebytes, entre le 11 et le 13 janvier 2019. Le cheval de Troie « Shlayer » s'installait lorsque l'utilisateur acceptait de mettre à jour un programme se faisant passer pour Flash Player. Sur seulement trois jours, plus de 5 millions de Mac auraient été visés.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/?&tag=Steganography


https://www.scoop.it/t/securite-pc-et-internet/?&tag=Steganography


No comment yet.
Scooped by Gust MEES
December 27, 2018 11:02 AM
Scoop.it!

FBI solves mystery surrounding 15-year-old Fruitfly Mac malware

FBI solves mystery surrounding 15-year-old Fruitfly Mac malware | Apple, Mac, MacOS, iOS4, iPad, iPhone and (in)security... | Scoop.it

The FBI has solved the final mystery surrounding a strain of Mac malware that was used by an Ohio man to spy on people for 14 years.

The man, 28-year-old Phillip Durachinsky, was arrested in January 2017, and charged a year later, in January 2018.

US authorities say he created the Fruitfly Mac malware (Quimitchin by some AV vendors) back in 2003 and used it until 2017 to infect victims and take control off their Mac computers to steal files, keyboard strokes, watch victims via the webcam, and listen in on conversations via the microphone.

Court documents reveal Durachinsky wasn't particularly interested in financial crime but was primarily focused on watching victims, having collected millions of images on his computer, including many of underage children.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/?&tag=Fruitfly


Gust MEES's insight:

The FBI has solved the final mystery surrounding a strain of Mac malware that was used by an Ohio man to spy on people for 14 years.

The man, 28-year-old Phillip Durachinsky, was arrested in January 2017, and charged a year later, in January 2018.

US authorities say he created the Fruitfly Mac malware (Quimitchin by some AV vendors) back in 2003 and used it until 2017 to infect victims and take control off their Mac computers to steal files, keyboard strokes, watch victims via the webcam, and listen in on conversations via the microphone.

Court documents reveal Durachinsky wasn't particularly interested in financial crime but was primarily focused on watching victims, having collected millions of images on his computer, including many of underage children.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/?&tag=Fruitfly


No comment yet.
Scooped by Gust MEES
December 7, 2018 2:06 PM
Scoop.it!

Mac malware combines EmPyre backdoor and XMRig miner | #Apple #CyberSecurity #NobodyIsPerfect

Mac malware combines EmPyre backdoor and XMRig miner | #Apple #CyberSecurity #NobodyIsPerfect | Apple, Mac, MacOS, iOS4, iPad, iPhone and (in)security... | Scoop.it

Earlier this week, we discovered a new piece of Mac malware that is combining two different open-source tools—the EmPyre backdoor and the XMRig cryptominer—for the purpose of evil.

The malware was being distributed through an application named Adobe Zii. Adobe Zii is software that is designed to aid in the piracy of a variety of Adobe applications. In this case, however, the app was called Adobe Zii, but it was definitely not the real thing.

As can be seen from the above screenshots, the actual Adobe Zii software, on the left, uses the Adobe Creative Cloud logo. (After all, if you’re going to write software to help people steal Adobe software, why not steal the logo, too?) The malware installer, however, uses a generic Automator applet icon.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


Gust MEES's insight:

Earlier this week, we discovered a new piece of Mac malware that is combining two different open-source tools—the EmPyre backdoor and the XMRig cryptominer—for the purpose of evil.

The malware was being distributed through an application named Adobe Zii. Adobe Zii is software that is designed to aid in the piracy of a variety of Adobe applications. In this case, however, the app was called Adobe Zii, but it was definitely not the real thing.

As can be seen from the above screenshots, the actual Adobe Zii software, on the left, uses the Adobe Creative Cloud logo. (After all, if you’re going to write software to help people steal Adobe software, why not steal the logo, too?) The malware installer, however, uses a generic Automator applet icon.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


No comment yet.
Scooped by Gust MEES
July 10, 2019 2:55 PM
Scoop.it!

#Update : Zoom corrige en urgence la faille de sécurité sur les webcams des Mac | #CyberSecurity #Apple 

#Update : Zoom corrige en urgence la faille de sécurité sur les webcams des Mac | #CyberSecurity #Apple  | Apple, Mac, MacOS, iOS4, iPad, iPhone and (in)security... | Scoop.it

Zoom, l’éditeur de l’application de visioconférence pour macOS, a déployé en urgence un correctif après qu’un chercheur en sécurité ait dévoilé l’existence d’une faille de sécurité pouvant permettre à des sites Web de lancer un chat vidéo Zoom depuis un Mac sans la permission de son propriétaire. Dans le cadre de son correctif, Zoom supprimera complètement le serveur web local créé sur les Mac.

Jonathan Leitschuh, le chercheur à l’origine de cette découverte, a indiqué qu’il avait également pu activer des webcams Mac sans autorisation.

L’éditeur ajoutera une option à la barre de menu de son application qui permet aux utilisateurs de désinstaller manuellement le client Zoom, y compris le serveur Web installé localement. Une fois le correctif déployé, les utilisateurs verront une option « Désinstaller Zoom », qui supprimera complètement logiciel et les paramètres enregistrés.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


https://www.scoop.it/topic/apple-mac-ios4-ipad-iphone-and-in-security/?&tag=Zoom


Gust MEES's insight:

Zoom, l’éditeur de l’application de visioconférence pour macOS, a déployé en urgence un correctif après qu’un chercheur en sécurité ait dévoilé l’existence d’une faille de sécurité pouvant permettre à des sites Web de lancer un chat vidéo Zoom depuis un Mac sans la permission de son propriétaire. Dans le cadre de son correctif, Zoom supprimera complètement le serveur web local créé sur les Mac.

Jonathan Leitschuh, le chercheur à l’origine de cette découverte, a indiqué qu’il avait également pu activer des webcams Mac sans autorisation.

L’éditeur ajoutera une option à la barre de menu de son application qui permet aux utilisateurs de désinstaller manuellement le client Zoom, y compris le serveur Web installé localement. Une fois le correctif déployé, les utilisateurs verront une option « Désinstaller Zoom », qui supprimera complètement logiciel et les paramètres enregistrés.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


https://www.scoop.it/topic/apple-mac-ios4-ipad-iphone-and-in-security/?&tag=Zoom


No comment yet.
Scooped by Gust MEES
June 29, 2019 9:04 AM
Scoop.it!

New Mac malware abuses recently disclosed Gatekeeper zero-day | #Apple #CyberSecurity #NobodyIsperfect 

New Mac malware abuses recently disclosed Gatekeeper zero-day | #Apple #CyberSecurity #NobodyIsperfect  | Apple, Mac, MacOS, iOS4, iPad, iPhone and (in)security... | Scoop.it

Mac malware developers have jumped on a recently disclosed macOS Gatekeeper vulnerability and are actively developing malware that abuses it.

The new malware has been named OSX/Linker and has been tied to the same group that operates the OSX/Surfbuyer adware, according to an investigation carried out by Joshua Long, Chief Security Analyst for Mac security software maker Intego.


Learn more / En savoir plus / Mehr erfahren:


http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


https://www.scoop.it/topic/apple-mac-ios4-ipad-iphone-and-in-security/?&tag=Gatekeeper


Gust MEES's insight:

Mac malware developers have jumped on a recently disclosed macOS Gatekeeper vulnerability and are actively developing malware that abuses it.

The new malware has been named OSX/Linker and has been tied to the same group that operates the OSX/Surfbuyer adware, according to an investigation carried out by Joshua Long, Chief Security Analyst for Mac security software maker Intego.


Learn more / En savoir plus / Mehr erfahren:


http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


https://www.scoop.it/topic/apple-mac-ios4-ipad-iphone-and-in-security/?&tag=Gatekeeper


No comment yet.
Scooped by Gust MEES
June 22, 2019 6:54 AM
Scoop.it!

Sur Mac, deux failles dans Firefox exploitées contre des plateformes de cryptomonnaies

Sur Mac, deux failles dans Firefox exploitées contre des plateformes de cryptomonnaies | Apple, Mac, MacOS, iOS4, iPad, iPhone and (in)security... | Scoop.it

Des hackers ont exploité deux failles dans Firefox pour installer un porte dérobée sur des Mac. Mozilla a comblé les vulnérabilités avec la version 67.0.4 de Firefox sortie hier. La mise à jour est donc chaudement recommandée à tous les utilisateurs (elle s’applique normalement automatiquement lors d’un redémarrage).

Les hackers ont visé des employés de Coinbase, une plateforme populaire d’achat et de vente de cryptomonnaies. D’après le responsable de la sécurité de Coinbase, l’attaque a été bloquée et aucun utilisateur de la plateforme n’aurait été visé directement. Il ajoute que d’autres plateformes cryptomonnaies ont été la cible d’une attaque identique.

Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


https://www.scoop.it/topic/apple-mac-ios4-ipad-iphone-and-in-security/?&tag=Browsers


Gust MEES's insight:

Des hackers ont exploité deux failles dans Firefox pour installer un porte dérobée sur des Mac. Mozilla a comblé les vulnérabilités avec la version 67.0.4 de Firefox sortie hier. La mise à jour est donc chaudement recommandée à tous les utilisateurs (elle s’applique normalement automatiquement lors d’un redémarrage).

Les hackers ont visé des employés de Coinbase, une plateforme populaire d’achat et de vente de cryptomonnaies. D’après le responsable de la sécurité de Coinbase, l’attaque a été bloquée et aucun utilisateur de la plateforme n’aurait été visé directement. Il ajoute que d’autres plateformes cryptomonnaies ont été la cible d’une attaque identique.

Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


https://www.scoop.it/topic/apple-mac-ios4-ipad-iphone-and-in-security/?&tag=Browsers


No comment yet.
Scooped by Gust MEES
May 28, 2019 5:33 PM
Scoop.it!

#Apple: Gatekeeper Bug in MacOS Mojave Allows Malware to Execute | CyberSecurity #NobodyIsPerfect 

#Apple: Gatekeeper Bug in MacOS Mojave Allows Malware to Execute | CyberSecurity #NobodyIsPerfect  | Apple, Mac, MacOS, iOS4, iPad, iPhone and (in)security... | Scoop.it

Researcher discloses vulnerability in macOS Gatekeeper security feature that allows the execution of malicious code on current version of the OS.

Researcher Filippo Cavallarin disclosed a bug in the macOS security feature Gatekeeper that allows malicious code execution on systems running the most recent version of Mojave (10.14.0).

MacOS Gatekeeper is an Apple security feature that enforces code signing and verifies downloads and apps before users run them. The goal is to eliminate the possibility of malicious files being executed on systems. Gatekeeper requires the user’s consent before opening a file.

“On MacOS X version <= 10.14.5 (at time of writing) it is possible to easily bypass Gatekeeper in order to execute untrusted code without any warning or user’s explicit permission,” wrote Cavallarin, the CEO of Segment, an Italian security firm.


Learn more / En savoir plus / Mehr erfahren:


http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


https://www.scoop.it/topic/apple-mac-ios4-ipad-iphone-and-in-security/?&tag=Gatekeeper


Gust MEES's insight:

Researcher discloses vulnerability in macOS Gatekeeper security feature that allows the execution of malicious code on current version of the OS.

Researcher Filippo Cavallarin disclosed a bug in the macOS security feature Gatekeeper that allows malicious code execution on systems running the most recent version of Mojave (10.14.0).

MacOS Gatekeeper is an Apple security feature that enforces code signing and verifies downloads and apps before users run them. The goal is to eliminate the possibility of malicious files being executed on systems. Gatekeeper requires the user’s consent before opening a file.

“On MacOS X version <= 10.14.5 (at time of writing) it is possible to easily bypass Gatekeeper in order to execute untrusted code without any warning or user’s explicit permission,” wrote Cavallarin, the CEO of Segment, an Italian security firm.


Learn more / En savoir plus / Mehr erfahren:


http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


https://www.scoop.it/topic/apple-mac-ios4-ipad-iphone-and-in-security/?&tag=Gatekeeper


la amour's curator insight, December 3, 2022 7:53 AM

https://achetersaxendaenligne.com/Produit/acheter-belviq-en-ligne/

https://acheteractiskenan.com/
https://acheteractiskenan.com/produit/
https://acheteractiskenan.com/produit/achete-klonopin/
https://acheteractiskenan.com/produit/acheter-4-aco-dmt/
https://acheteractiskenan.com/product/acheter-5-meo-dmt-usa/
https://acheteractiskenan.com/product/acheter-dmt/
https://acheteractiskenan.com/product/acheter-adderall-en-ligne/
https://acheteractiskenan.com/product/acheter-adipex/
https://acheteractiskenan.com/product/acheter-toseina-2-ml-solucion/
https://acheteractiskenan.com/product/acheter-oxycodone-mallinckrodt/
https://acheteractiskenan.com/product/acheter-de-loxycodone/
https://acheteractiskenan.com/product/acheter-ativan-en-ligne/
https://acheteractiskenan.com/product/acheter-percocet/
https://acheteractiskenan.com/product/acheter-tramadol/
https://acheteractiskenan.com/product/morphine/
https://acheteractiskenan.com/product/acheter-codeine-en-ligne/
https://acheteractiskenan.com/product/injection-de-morphine/
https://acheteractiskenan.com/product/acheter-phentermine-en-ligne/
https://acheteractiskenan.com/product/acheter-tren-a-en-ligne/
https://acheteractiskenan.com/product/achetez-trenbolone-enanthate/
https://acheteractiskenan.com/product/acheter-trenarapid-en-ligne/
https://acheteractiskenan.com/product/acheter-de-la-cocaine/
https://acheteractiskenan.com/product/acheter-demerol/
https://acheteractiskenan.com/product/acheter-desoxyn/
https://acheteractiskenan.com/product/buy-dexedrine-online/
https://acheteractiskenan.com/product/acheter-dilaudid-en-ligne/
https://acheteractiskenan.com/product/acheter-du-fentanyl/
https://acheteractiskenan.com/product/acheter-du-suboxone/
https://acheteractiskenan.com/product/acheter-du-xanax-vert/
https://acheteractiskenan.com/product/acheter-norvas-10mg/
https://acheteractiskenan.com/product/acheter-oramorph/
https://acheteractiskenan.com/product/acheter-rubifen/
https://acheteractiskenan.com/product/acheter-subutex/
https://acheteractiskenan.com/product/acheter-vicodin/
https://acheteractiskenan.com/product/achetez-vyvanse/
https://acheteractiskenan.com/product/acheter-de-la-cocaine/
https://acheteractiskenan.com/product/acheter-de-lheroine/
https://acheteractiskenan.com/product/acheter-methadone-en-ligne/
https://acheteractiskenan.com/product/acheter-ms-contin/
https://acheteractiskenan.com/product/acheter-oxazepam-en-ligne/
https://acheteractiskenan.com/product/acheter-oxynorm-en-ligne/
https://acheteractiskenan.com/product/acheter-phentermine-en-ligne/
https://acheteractiskenan.com/product/acheter-plegine-en-ligne/
https://acheteractiskenan.com/product/acheter-rubifen/
https://acheteractiskenan.com/product/acheter-stilpane-sirop-100ml/
https://acheteractiskenan.com/product/acheter-toseina-2-ml-solucion/
https://acheteractiskenan.com/product/acheter-histaverin-2-mg-ml/
https://acheteractiskenan.com/product/acheter-lheroine-black-goudron/
https://acheteractiskenan.com/product/acheter-la-cocaine-colombienne/
https://acheteractiskenan.com/product/acheter-ultram-en-ligne/
https://acheteractiskenan.com/product/acheter-oxecta-oxycodone-hcl-...

acheter percocet
acheter tramadol
acheter morphine
acheter codeine en lign
injection de morphine
acheter phentermine en ligne
achetez trenbolone enanthate
acheter trenarapid

kopen nembutal liquid
kopen oxycodon hcl
https://kopenoxycodone.com/
https://kopenoxycodone.com/producten/
https://kopenoxycodone.com/product/ambien-online-kopen/
https://kopenoxycodone.com/product/buprenorfine-kopen/
https://kopenoxycodone.com/product/carisoprodol-nederland-kopen/
https://kopenoxycodone.com/product/fentanyl-citrate-kopen/
https://kopenoxycodone.com/product/fentanyl-poeder-kopen/
https://kopenoxycodone.com/product/fentanyl-pleister-kopen/
https://kopenoxycodone.com/product/gouden-leraar-paddenstoelen/
https://kopenoxycodone.com/product/hydromorphone-kopen/
https://kopenoxycodone.com/product/ketamine-poeder-kopen/
https://kopenoxycodone.com/product/koop-5-meo-dmt/
https://kopenoxycodone.com/product/koop-adderall-online/
https://kopenoxycodone.com/product/koop-desoxyn-online/
https://kopenoxycodone.com/product/koop-dexedrine/
https://kopenoxycodone.com/product/koop-dmt-netherland/
https://kopenoxycodone.com/product/koop-flakka-a-pvp/
https://kopenoxycodone.com/product/koop-mdma-crystal/
https://kopenoxycodone.com/product/koop-morphine/
https://kopenoxycodone.com/product/koop-natriumcyanide/
https://kopenoxycodone.com/product/koop-nembutal-pentobarbital/
https://kopenoxycodone.com/product/koop-nembutal-poeder/
https://kopenoxycodone.com/product/koop-oxycodon/
https://kopenoxycodone.com/product/koop-oxycontin-online/
https://kopenoxycodone.com/product/koop-percocet-online/
https://kopenoxycodone.com/product/koop-phentermine-adipex/
https://kopenoxycodone.com/product/koop-suboxone-strips/
https://kopenoxycodone.com/product/koop-subutex-nederlands/
https://kopenoxycodone.com/product/koop-vicodin-online/
https://kopenoxycodone.com/product/koop-vyvanse-online/
https://kopenoxycodone.com/product/kopen-ultram-online/
https://kopenoxycodone.com/product/lsd-sheet/
https://kopenoxycodone.com/product/nembutal-pillen-kopen/
https://kopenoxycodone.com/product/koop-nembutal-liquid/
https://kopenoxycodone.com/product/oxycodon-hcl-kopen/
comprar-ultram
comprar xanax verde
buy xanax
comprar vyvanse en linea
comprar vicodin en linea
golden teacher
comprar psilocybe
comprar polvo-
comprar micro mushrooms
comprar metanfetaminas
comprar flakka
comprar fentanilo en linea
comprar extasis en linea
comprar-etizolam
comprar-5-meo-dmt
buy-seconal-sodium
buy-nembutal-pills
buy-nembutal-liquid
Oxycodone
comprar Oxycodone
https://comprarmorfina.com/
https://comprarmorfina.com/productos-comprar-dilaudid/
https://comprarmorfina.com/product/comprar-adderall-en-linea/
https://comprarmorfina.com/product/comprar-adipex-en-linea/
https://comprarmorfina.com/product/comprar-ambien-en-linea/
https://comprarmorfina.com/product/comprar-buprenorfine-en-linea/
https://comprarmorfina.com/product/comprar-dexedrina/
https://comprarmorfina.com/product/comprar-desoxyn-en-linea/
https://comprarmorfina.com/product/comprar-dilaudid/
https://comprarmorfina.com/product/comprar-dmt-en-linea/
https://comprarmorfina.com/product/comprar-heroina-en-linea/
https://comprarmorfina.com/product/comprar-ketamina/
https://comprarmorfina.com/product/comprar-klonopin/
https://comprarmorfina.com/product/comprar-morfina/
https://comprarmorfina.com/product/comprar-oxicodona-en-linea/
https://comprarmorfina.com/product/comprar-oxycontin-en-linea/
https://comprarmorfina.com/product/comprar-percocet-en-linea/
https://comprarmorfina.com/product/comprar-rubifen-espana/
https://comprarmorfina.com/product/comprar-soma-en-linea/
https://comprarmorfina.com/product/comprar-suboxone-en-linea/
https://comprarmorfina.com/product/comprar-subutex-en-linea/
https://comprarmorfina.com/product/comprar-ultram-en-linea/
https://comprarmorfina.com/product/comprar-xanax-verde/
https://comprarmorfina.com/product/buy-xanax/
https://comprarmorfina.com/product/comprar-vyvanse-en-linea/
https://comprarmorfina.com/product/comprar-vicodin-en-linea/
https://comprarmorfina.com/product/golden-teacher-crecer-rapidamente/https://onlinevapesshop.com/
https://onlinevapesshop.com/product/
https://onlinevapesshop.com/product/buy-phentermine-online/
https://onlinevapesshop.com/product/buy-adipex-online/
https://onlinevapesshop.com/product/buy-oxynorm-online/
https://onlinevapesshop.com/product/buy-oxycontin-online/
https://onlinevapesshop.com/product/buy-adderall-online-3/
https://onlinevapesshop.com/product/buy-adderall-online-2/
https://onlinevapesshop.com/product/buy-celexa-online/
https://onlinevapesshop.com/product/buy-concerta-online/
https://onlinevapesshop.com/product/buy-desoxyn-5mg-online/
https://onlinevapesshop.com/product/buy-dexedrine-online/
https://onlinevapesshop.com/product/buy-klonopin-online/
https://onlinevapesshop.com/product/buy-mescaline-online/
https://onlinevapesshop.com/product/buy-valium-online/
https://onlinevapesshop.com/product/buy-xanax-online/
https://onlinevapesshop.com/product/buy-yellow-xanax-bars-online/
https://onlinevapesshop.com/product/buy-zopiclone-online/
https://onlinevapesshop.com/product/buy-botox-online/
https://onlinevapesshop.com/product/buy-cbd-oil-online/
https://onlinevapesshop.com/product/buy-diclazepam-online/
https://onlinevapesshop.com/product/buy-liquid-red-mercury-online/
https://onlinevapesshop.com/product/buy-mdma-crystal-online/
https://onlinevapesshop.com/product/buy-phenylacetone-oil-online/
https://onlinevapesshop.com/product/buy-nembutal-pentobarbital-liqu...
https://onlinevapesshop.com/product/buy-piperonyl-methyl-ketone/
https://onlinevapesshop.com/product/buy-anavar-oxandrolone-online/
https://onlinevapesshop.com/product/buy-ssd-chemical-solution/
https://onlinevapesshop.com/product/buy-ayurvedic-urea-online/
https://onlinevapesshop.com/product/buy-dxn-code-strike-online/
https://onlinevapesshop.com/product/buy-deca-durabolin-online/
https://onlinevapesshop.com/product/buy-viagra-online/
https://onlinevapesshop.com/product/buy-genius-test-online/
https://onlinevapesshop.com/product/buy-viagra-online/
https://onlinevapesshop.com/product-category/growth-hormones/
https://onlinevapesshop.com/product/buy-viagra-online/
https://onlinevapesshop.com/product/buy-ketamine-liquid-online/
https://onlinevapesshop.com/product/buy-ketamine-powder-online/
https://onlinevapesshop.com/product/buy-methoxetamine-online/
https://onlinevapesshop.com/product/buy-methylone-crystals-online/
https://onlinevapesshop.com/product/buy-morphine-online-2/
https://onlinevapesshop.com/product/buy-oramorph-online/
https://onlinevapesshop.com/product/buy-percocet-online/
https://onlinevapesshop.com/product/buy-roxicodone-online/
https://onlinevapesshop.com/product/buy-soma-online/
https://onlinevapesshop.com/product/buy-tramadol-online/
https://onlinevapesshop.com/product/buy-vicodin-online/
Buy oxycodone online
Buy phentermine online
Buy adipex online
Buy oxynorm online
Buy oxycontin online
Buy adderall USA online
Buy adderall online
Buy oxycodone online
Buy 4-aco-dmt online
Buy 5-meo-dmt online
Buy adipex online
Buy ambien online
Buy oxycodone
buy oxycontin
buy percocet
buy oramorph
Buy oxycodone online
buy-nembutal liquid
https://dolorendo.com/
https://dolorendo.com/product/
https://dolorendo.com/product/comprar-oxicodona-en-linea/
https://dolorendo.com/product/comprar-oxicodon/
https://dolorendo.com/product/comprar-oxynorm-en-linea/
https://dolorendo.com/product/comprar-oxycontin-en-linea/
https://dolorendo.com/product/comprar-percocet-en-linea/
https://dolorendo.com/product/comprar-oramorph-sr/
https://dolorendo.com/productos-comprar-dilaudid/
https://dolorendo.com/product/comprar-vyvanse-en-linea/
https://dolorendo.com/product/comprar-suboxone-en-linea/
https://dolorendo.com/product/comprar-subutex-en-linea/
https://dolorendo.com/product/comprar-pastillas-nembutal/
https://dolorendo.com/productos-comprar-dilaudid/
https://dolorendo.com/product/comprar-acetaminofen-codeina/
https://dolorendo.com/product/comprar-adderall-en-linea/
https://dolorendo.com/product/comprar-desoxyn-en-linea/
https://dolorendo.com/product/comprar-dexedrina/
https://dolorendo.com/product/comprar-dmt-en-linea/
https://dolorendo.com/product/comprar-ketamina/
https://dolorendo.com/product/comprar-klonopin/
https://dolorendo.com/product/comprar-5-meo-dmt/
https://dolorendo.com/product/comprar-adipex-en-linea/
https://dolorendo.com/product/comprar-alphabol-cr/
https://buypsychedelicsnow.com/shop/buy-morphine-canada/
https://buypsychedelicsnow.com/shop/buy-5-meo-dmt-usa/
https://buypsychedelicsnow.com/shop/buy-codeine-online/
https://buypsychedelicsnow.com/shop/buy-4-aco-dmt-online/
https://buypsychedelicsnow.com/shop/buy-ayahuasca-online-usa/
https://buypsychedelicsnow.com/shop/black-tar-heroin/
https://buypsychedelicsnow.com/shop/buy-bolivian-cocaine/
https://buypsychedelicsnow.com/shop/buy-brown-heroin-usa/
https://buypsychedelicsnow.com/shop/buy-changa-online/
https://buypsychedelicsnow.com/shop/buy-white-heroin-online/
https://buypsychedelicsnow.com/shop/buy-dmt-online-canada/
https://buypsychedelicsnow.com/shop/buy-flakka-online/
https://buypsychedelicsnow.com/shop/buy-psilocybe-cubensis-online/
https://buypsychedelicsnow.com/shop/buy-ibogaine-online-canada/
https://buypsychedelicsnow.com/shop/ketamine-powder-for-sale/
https://buypsychedelicsnow.com/shop/buy-kratom-online-canada/
https://buypsychedelicsnow.com/shop/buy-lsd-online-canada/
https://buypsychedelicsnow.com/shop/mdma-for-sale-canada/
https://buypsychedelicsnow.com/shop/buy-mescaline-online-canada/
https://buypsychedelicsnow.com/shop/buy-mushroom-online-canada/
https://buypsychedelicsnow.com/shop/buy-psilocybin-online-canada/

https://achetersaxendaenligne.com/

https://achetersaxendaenligne.com/Produit/acheter-saxenda-en-ligne/

https://achetersaxendaenligne.com/

https://achetersaxendaenligne.com/Produit/acheter-saxenda-en-ligne/

https://achetersaxendaenligne.com/Produit/acheter-adipex-en-ligne/

https://achetersaxendaenligne.com/Produit/acheter-belviq-en-ligne/

https://achetersaxendaenligne.com/Produit/acheter-dexedrine/

https://achetersaxendaenligne.com/Produit/acheter-du-ritalin/https://achetersaxendaenligne.com/Produit/ozempic-sans-ordonnance/

https://achetersaxendaenligne.com/Produit/acheter-victoza-en-ligne/https://achetersaxendaenligne.com/Produit/acheter-vyvanse/

https://achetersaxendaenligne.com/Produit/achetez-qsymia-en-ligne/

Scooped by Gust MEES
March 23, 2019 9:00 AM
Scoop.it!

Pwn2Own 2019 : deux grosses failles de sécurité dans Safari | #Apple #CyberSecurity 

Pwn2Own 2019 : deux grosses failles de sécurité dans Safari | #Apple #CyberSecurity  | Apple, Mac, MacOS, iOS4, iPad, iPhone and (in)security... | Scoop.it

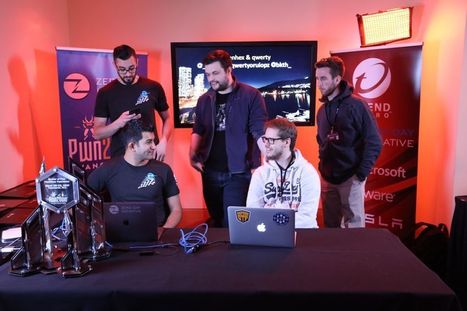
Le concours Pwn2Own 2019 a débuté à Vancouver (Canada), et dès le premier jour deux failles ont été dévoilées touchant Safari. La première, réalisée par l’équipe Fluorocetate, permet d’échapper au « bac à sable » du navigateur au moyen de la force brute. Amat Cama et Richard Zhu, les deux petits génies de l’équipe, ont remporté une récompense de 55 000 $ pour la démonstration de cette vulnérabilité.

Phoenhex et les bidouilleurs de l’équipe qwerty.
L’autre faiblesse de Safari mise en lumière durant la compétition est le fruit du travail de phoenhex et de l’équipe qwerty. Cette fois, il s’agit d’une élévation de privilèges depuis Safari, ouvrant aux hackers une porte vers le système… et donc, d’en prendre le contrôle. Apple connaissant déjà un des bugs permettant d’exploiter cette faille, les découvreurs devront se contenter de partager 45 000 $ (un joli cadeau de consolation).


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/topic/apple-mac-ios4-ipad-iphone-and-in-security


Gust MEES's insight:

Le concours Pwn2Own 2019 a débuté à Vancouver (Canada), et dès le premier jour deux failles ont été dévoilées touchant Safari. La première, réalisée par l’équipe Fluorocetate, permet d’échapper au « bac à sable » du navigateur au moyen de la force brute. Amat Cama et Richard Zhu, les deux petits génies de l’équipe, ont remporté une récompense de 55 000 $ pour la démonstration de cette vulnérabilité.


Phoenhex et les bidouilleurs de l’équipe qwerty.
L’autre faiblesse de Safari mise en lumière durant la compétition est le fruit du travail de phoenhex et de l’équipe qwerty. Cette fois, il s’agit d’une élévation de privilèges depuis Safari, ouvrant aux hackers une porte vers le système… et donc, d’en prendre le contrôle. Apple connaissant déjà un des bugs permettant d’exploiter cette faille, les découvreurs devront se contenter de partager 45 000 $ (un joli cadeau de consolation).


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/topic/apple-mac-ios4-ipad-iphone-and-in-security


No comment yet.
Scooped by Gust MEES
March 4, 2019 10:30 AM
Scoop.it!

Thunderclap : des vulnérabilités sur tous les Mac et PC Thunderbolt

Thunderclap : des vulnérabilités sur tous les Mac et PC Thunderbolt | Apple, Mac, MacOS, iOS4, iPad, iPhone and (in)security... | Scoop.it

Six chercheurs en sécurité ont publié leur découverte d'une faille de sécurité impliquant des périphériques Thunderbolt 3 et des cartes PCI Express. Alertés depuis 2016, Apple, Microsoft, ou encore Intel ont déployé des correctifs mais l'ensemble des problèmes n'a pas encore été réglé.

Cet ensemble de vulnérabilités est baptisé "Thunderclap". L'équipe a remarqué des lacunes dans les systèmes d'exploitation au niveau du contrôle d'accès à la mémoire de ces cartes PCIe et périphériques Thunderbolt.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/topic/apple-mac-ios4-ipad-iphone-and-in-security


https://www.scoop.it/topic/apple-mac-ios4-ipad-iphone-and-in-security/?&tag=Thunderclap


Gust MEES's insight:

Six chercheurs en sécurité ont publié leur découverte d'une faille de sécurité impliquant des périphériques Thunderbolt 3 et des cartes PCI Express. Alertés depuis 2016, Apple, Microsoft, ou encore Intel ont déployé des correctifs mais l'ensemble des problèmes n'a pas encore été réglé.

Cet ensemble de vulnérabilités est baptisé "Thunderclap". L'équipe a remarqué des lacunes dans les systèmes d'exploitation au niveau du contrôle d'accès à la mémoire de ces cartes PCIe et périphériques Thunderbolt.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/topic/apple-mac-ios4-ipad-iphone-and-in-security


https://www.scoop.it/topic/apple-mac-ios4-ipad-iphone-and-in-security/?&tag=Thunderclap


No comment yet.
Scooped by Gust MEES
February 15, 2019 4:48 PM
Scoop.it!

macOS Mojave : une faille permet de jeter un œil indiscret dans l’historique de Safari | #Apple #CyberSecurity #Tracking #Privacy #Browsers

macOS Mojave : une faille permet de jeter un œil indiscret dans l’historique de Safari | #Apple #CyberSecurity #Tracking #Privacy #Browsers | Apple, Mac, MacOS, iOS4, iPad, iPhone and (in)security... | Scoop.it

Depuis la première version de macOS Mojave, le dossier Safari (~/Library/Safari) n’est plus accessible qu’à une poignée d’applications (il était auparavant ouvert à tous les vents). Le Terminal ne peut même pas en afficher le contenu… Le système d’exploitation fournit l’accès à ce dossier à une poignée d’apps (et au Finder).

Jeff Johnson a néanmoins trouvé une faille qui permet à n’importe quel logiciel de regarder de plus près le contenu de ce dossier normalement protégé des regards indiscrets. Le tout, sans avoir besoin des sésames du système ou de l’utilisateur. La vulnérabilité se passe même de boîtes de dialogue d’autorisation. En exploitant ce bug, un malware peut obtenir l’historique de navigation et donc, potentiellement, des informations à caractère privé.

Mieux, ou pire encore, une application ayant reçu l’estampille du notaire de Mojave (une mesure de sécurité inaugurée avec macOS 10.14) pourrait tout de même être en mesure de piocher sans autorisation dans l’historique de Safari. En revanche, une application sandboxée, c’est à dire distribuée sur le Mac App Store, est incapable de tirer partie de cette faille.

Le découvreur a dûment informé Apple de sa découverte, avec tous les détails de la faille. Jeff Johnson a déjà été crédité par le constructeur pour ses trouvailles, et il est probable qu’une future mise à jour de sécurité vienne combler ce bug.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/


Gust MEES's insight:

Depuis la première version de macOS Mojave, le dossier Safari (~/Library/Safari) n’est plus accessible qu’à une poignée d’applications (il était auparavant ouvert à tous les vents). Le Terminal ne peut même pas en afficher le contenu… Le système d’exploitation fournit l’accès à ce dossier à une poignée d’apps (et au Finder).

Jeff Johnson a néanmoins trouvé une faille qui permet à n’importe quel logiciel de regarder de plus près le contenu de ce dossier normalement protégé des regards indiscrets. Le tout, sans avoir besoin des sésames du système ou de l’utilisateur. La vulnérabilité se passe même de boîtes de dialogue d’autorisation. En exploitant ce bug, un malware peut obtenir l’historique de navigation et donc, potentiellement, des informations à caractère privé.

Mieux, ou pire encore, une application ayant reçu l’estampille du notaire de Mojave (une mesure de sécurité inaugurée avec macOS 10.14) pourrait tout de même être en mesure de piocher sans autorisation dans l’historique de Safari. En revanche, une application sandboxée, c’est à dire distribuée sur le Mac App Store, est incapable de tirer partie de cette faille.

Le découvreur a dûment informé Apple de sa découverte, avec tous les détails de la faille. Jeff Johnson a déjà été crédité par le constructeur pour ses trouvailles, et il est probable qu’une future mise à jour de sécurité vienne combler ce bug.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/


No comment yet.
Scooped by Gust MEES
February 12, 2019 6:47 PM
Scoop.it!

Wenn die EXE-Datei den Mac angreift | #Apple #CyberSecurity #NobodyIsPerfect

Wenn die EXE-Datei den Mac angreift | #Apple #CyberSecurity #NobodyIsPerfect | Apple, Mac, MacOS, iOS4, iPad, iPhone and (in)security... | Scoop.it

Sicherheitsforscher haben eine schädliche EXE-Datei entdeckt, die es speziell auf Nutzer von Apples macOS-System abgesehen hat. Über einen Trick hebelt die Schadsoftware sogar die  Gatekeeper-Schutzfunktion aus.


Da die meiste Schadsoftware für Windows-Systeme programmiert wird, haben Nutzer von macOS und Linux meist nicht viele Gefahren im Netz zu fürchten. Allzu unbedacht sollten sich Anwender aber auch auf diesen Systemen nicht verhalten, wie ein aktueller Virenfund von Trend Micro belegt: Die Sicherheitsexperten haben eine EXE-Schadsoftware entdeckt, die für den Angriff von Macs vorgesehen ist und sogar die Gatekeeper-Funktion umgeht.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/


Gust MEES's insight:

Sicherheitsforscher haben eine schädliche EXE-Datei entdeckt, die es speziell auf Nutzer von Apples macOS-System abgesehen hat. Über einen Trick hebelt die Schadsoftware sogar die  Gatekeeper-Schutzfunktion aus.


Da die meiste Schadsoftware für Windows-Systeme programmiert wird, haben Nutzer von macOS und Linux meist nicht viele Gefahren im Netz zu fürchten. Allzu unbedacht sollten sich Anwender aber auch auf diesen Systemen nicht verhalten, wie ein aktueller Virenfund von Trend Micro belegt: Die Sicherheitsexperten haben eine EXE-Schadsoftware entdeckt, die für den Angriff von Macs vorgesehen ist und sogar die Gatekeeper-Funktion umgeht.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/


la amour's curator insight, December 3, 2022 7:53 AM

https://achetersaxendaenligne.com/Produit/acheter-belviq-en-ligne/

https://acheteractiskenan.com/
https://acheteractiskenan.com/produit/
https://acheteractiskenan.com/produit/achete-klonopin/
https://acheteractiskenan.com/produit/acheter-4-aco-dmt/
https://acheteractiskenan.com/product/acheter-5-meo-dmt-usa/
https://acheteractiskenan.com/product/acheter-dmt/
https://acheteractiskenan.com/product/acheter-adderall-en-ligne/
https://acheteractiskenan.com/product/acheter-adipex/
https://acheteractiskenan.com/product/acheter-toseina-2-ml-solucion/
https://acheteractiskenan.com/product/acheter-oxycodone-mallinckrodt/
https://acheteractiskenan.com/product/acheter-de-loxycodone/
https://acheteractiskenan.com/product/acheter-ativan-en-ligne/
https://acheteractiskenan.com/product/acheter-percocet/
https://acheteractiskenan.com/product/acheter-tramadol/
https://acheteractiskenan.com/product/morphine/
https://acheteractiskenan.com/product/acheter-codeine-en-ligne/
https://acheteractiskenan.com/product/injection-de-morphine/
https://acheteractiskenan.com/product/acheter-phentermine-en-ligne/
https://acheteractiskenan.com/product/acheter-tren-a-en-ligne/
https://acheteractiskenan.com/product/achetez-trenbolone-enanthate/
https://acheteractiskenan.com/product/acheter-trenarapid-en-ligne/
https://acheteractiskenan.com/product/acheter-de-la-cocaine/
https://acheteractiskenan.com/product/acheter-demerol/
https://acheteractiskenan.com/product/acheter-desoxyn/
https://acheteractiskenan.com/product/buy-dexedrine-online/
https://acheteractiskenan.com/product/acheter-dilaudid-en-ligne/
https://acheteractiskenan.com/product/acheter-du-fentanyl/
https://acheteractiskenan.com/product/acheter-du-suboxone/
https://acheteractiskenan.com/product/acheter-du-xanax-vert/
https://acheteractiskenan.com/product/acheter-norvas-10mg/
https://acheteractiskenan.com/product/acheter-oramorph/
https://acheteractiskenan.com/product/acheter-rubifen/
https://acheteractiskenan.com/product/acheter-subutex/
https://acheteractiskenan.com/product/acheter-vicodin/
https://acheteractiskenan.com/product/achetez-vyvanse/
https://acheteractiskenan.com/product/acheter-de-la-cocaine/
https://acheteractiskenan.com/product/acheter-de-lheroine/
https://acheteractiskenan.com/product/acheter-methadone-en-ligne/
https://acheteractiskenan.com/product/acheter-ms-contin/
https://acheteractiskenan.com/product/acheter-oxazepam-en-ligne/
https://acheteractiskenan.com/product/acheter-oxynorm-en-ligne/
https://acheteractiskenan.com/product/acheter-phentermine-en-ligne/
https://acheteractiskenan.com/product/acheter-plegine-en-ligne/
https://acheteractiskenan.com/product/acheter-rubifen/
https://acheteractiskenan.com/product/acheter-stilpane-sirop-100ml/
https://acheteractiskenan.com/product/acheter-toseina-2-ml-solucion/
https://acheteractiskenan.com/product/acheter-histaverin-2-mg-ml/
https://acheteractiskenan.com/product/acheter-lheroine-black-goudron/
https://acheteractiskenan.com/product/acheter-la-cocaine-colombienne/
https://acheteractiskenan.com/product/acheter-ultram-en-ligne/
https://acheteractiskenan.com/product/acheter-oxecta-oxycodone-hcl-...

acheter percocet
acheter tramadol
acheter morphine
acheter codeine en lign
injection de morphine
acheter phentermine en ligne
achetez trenbolone enanthate
acheter trenarapid

kopen nembutal liquid
kopen oxycodon hcl
https://kopenoxycodone.com/
https://kopenoxycodone.com/producten/
https://kopenoxycodone.com/product/ambien-online-kopen/
https://kopenoxycodone.com/product/buprenorfine-kopen/
https://kopenoxycodone.com/product/carisoprodol-nederland-kopen/
https://kopenoxycodone.com/product/fentanyl-citrate-kopen/
https://kopenoxycodone.com/product/fentanyl-poeder-kopen/
https://kopenoxycodone.com/product/fentanyl-pleister-kopen/
https://kopenoxycodone.com/product/gouden-leraar-paddenstoelen/
https://kopenoxycodone.com/product/hydromorphone-kopen/
https://kopenoxycodone.com/product/ketamine-poeder-kopen/
https://kopenoxycodone.com/product/koop-5-meo-dmt/
https://kopenoxycodone.com/product/koop-adderall-online/
https://kopenoxycodone.com/product/koop-desoxyn-online/
https://kopenoxycodone.com/product/koop-dexedrine/
https://kopenoxycodone.com/product/koop-dmt-netherland/
https://kopenoxycodone.com/product/koop-flakka-a-pvp/
https://kopenoxycodone.com/product/koop-mdma-crystal/
https://kopenoxycodone.com/product/koop-morphine/
https://kopenoxycodone.com/product/koop-natriumcyanide/
https://kopenoxycodone.com/product/koop-nembutal-pentobarbital/
https://kopenoxycodone.com/product/koop-nembutal-poeder/
https://kopenoxycodone.com/product/koop-oxycodon/
https://kopenoxycodone.com/product/koop-oxycontin-online/
https://kopenoxycodone.com/product/koop-percocet-online/
https://kopenoxycodone.com/product/koop-phentermine-adipex/
https://kopenoxycodone.com/product/koop-suboxone-strips/
https://kopenoxycodone.com/product/koop-subutex-nederlands/
https://kopenoxycodone.com/product/koop-vicodin-online/
https://kopenoxycodone.com/product/koop-vyvanse-online/
https://kopenoxycodone.com/product/kopen-ultram-online/
https://kopenoxycodone.com/product/lsd-sheet/
https://kopenoxycodone.com/product/nembutal-pillen-kopen/
https://kopenoxycodone.com/product/koop-nembutal-liquid/
https://kopenoxycodone.com/product/oxycodon-hcl-kopen/
comprar-ultram
comprar xanax verde
buy xanax
comprar vyvanse en linea
comprar vicodin en linea
golden teacher
comprar psilocybe
comprar polvo-
comprar micro mushrooms
comprar metanfetaminas
comprar flakka
comprar fentanilo en linea
comprar extasis en linea
comprar-etizolam
comprar-5-meo-dmt
buy-seconal-sodium
buy-nembutal-pills
buy-nembutal-liquid
Oxycodone
comprar Oxycodone
https://comprarmorfina.com/
https://comprarmorfina.com/productos-comprar-dilaudid/
https://comprarmorfina.com/product/comprar-adderall-en-linea/
https://comprarmorfina.com/product/comprar-adipex-en-linea/
https://comprarmorfina.com/product/comprar-ambien-en-linea/
https://comprarmorfina.com/product/comprar-buprenorfine-en-linea/
https://comprarmorfina.com/product/comprar-dexedrina/
https://comprarmorfina.com/product/comprar-desoxyn-en-linea/
https://comprarmorfina.com/product/comprar-dilaudid/
https://comprarmorfina.com/product/comprar-dmt-en-linea/
https://comprarmorfina.com/product/comprar-heroina-en-linea/
https://comprarmorfina.com/product/comprar-ketamina/
https://comprarmorfina.com/product/comprar-klonopin/
https://comprarmorfina.com/product/comprar-morfina/
https://comprarmorfina.com/product/comprar-oxicodona-en-linea/
https://comprarmorfina.com/product/comprar-oxycontin-en-linea/
https://comprarmorfina.com/product/comprar-percocet-en-linea/
https://comprarmorfina.com/product/comprar-rubifen-espana/
https://comprarmorfina.com/product/comprar-soma-en-linea/
https://comprarmorfina.com/product/comprar-suboxone-en-linea/
https://comprarmorfina.com/product/comprar-subutex-en-linea/
https://comprarmorfina.com/product/comprar-ultram-en-linea/
https://comprarmorfina.com/product/comprar-xanax-verde/
https://comprarmorfina.com/product/buy-xanax/
https://comprarmorfina.com/product/comprar-vyvanse-en-linea/
https://comprarmorfina.com/product/comprar-vicodin-en-linea/
https://comprarmorfina.com/product/golden-teacher-crecer-rapidamente/https://onlinevapesshop.com/
https://onlinevapesshop.com/product/
https://onlinevapesshop.com/product/buy-phentermine-online/
https://onlinevapesshop.com/product/buy-adipex-online/
https://onlinevapesshop.com/product/buy-oxynorm-online/
https://onlinevapesshop.com/product/buy-oxycontin-online/
https://onlinevapesshop.com/product/buy-adderall-online-3/
https://onlinevapesshop.com/product/buy-adderall-online-2/
https://onlinevapesshop.com/product/buy-celexa-online/
https://onlinevapesshop.com/product/buy-concerta-online/
https://onlinevapesshop.com/product/buy-desoxyn-5mg-online/
https://onlinevapesshop.com/product/buy-dexedrine-online/
https://onlinevapesshop.com/product/buy-klonopin-online/
https://onlinevapesshop.com/product/buy-mescaline-online/
https://onlinevapesshop.com/product/buy-valium-online/
https://onlinevapesshop.com/product/buy-xanax-online/
https://onlinevapesshop.com/product/buy-yellow-xanax-bars-online/
https://onlinevapesshop.com/product/buy-zopiclone-online/
https://onlinevapesshop.com/product/buy-botox-online/
https://onlinevapesshop.com/product/buy-cbd-oil-online/
https://onlinevapesshop.com/product/buy-diclazepam-online/
https://onlinevapesshop.com/product/buy-liquid-red-mercury-online/
https://onlinevapesshop.com/product/buy-mdma-crystal-online/
https://onlinevapesshop.com/product/buy-phenylacetone-oil-online/
https://onlinevapesshop.com/product/buy-nembutal-pentobarbital-liqu...
https://onlinevapesshop.com/product/buy-piperonyl-methyl-ketone/
https://onlinevapesshop.com/product/buy-anavar-oxandrolone-online/
https://onlinevapesshop.com/product/buy-ssd-chemical-solution/
https://onlinevapesshop.com/product/buy-ayurvedic-urea-online/
https://onlinevapesshop.com/product/buy-dxn-code-strike-online/
https://onlinevapesshop.com/product/buy-deca-durabolin-online/
https://onlinevapesshop.com/product/buy-viagra-online/
https://onlinevapesshop.com/product/buy-genius-test-online/
https://onlinevapesshop.com/product/buy-viagra-online/
https://onlinevapesshop.com/product-category/growth-hormones/
https://onlinevapesshop.com/product/buy-viagra-online/
https://onlinevapesshop.com/product/buy-ketamine-liquid-online/
https://onlinevapesshop.com/product/buy-ketamine-powder-online/
https://onlinevapesshop.com/product/buy-methoxetamine-online/
https://onlinevapesshop.com/product/buy-methylone-crystals-online/
https://onlinevapesshop.com/product/buy-morphine-online-2/
https://onlinevapesshop.com/product/buy-oramorph-online/
https://onlinevapesshop.com/product/buy-percocet-online/
https://onlinevapesshop.com/product/buy-roxicodone-online/
https://onlinevapesshop.com/product/buy-soma-online/
https://onlinevapesshop.com/product/buy-tramadol-online/
https://onlinevapesshop.com/product/buy-vicodin-online/
Buy oxycodone online
Buy phentermine online
Buy adipex online
Buy oxynorm online
Buy oxycontin online
Buy adderall USA online
Buy adderall online
Buy oxycodone online
Buy 4-aco-dmt online
Buy 5-meo-dmt online
Buy adipex online
Buy ambien online
Buy oxycodone
buy oxycontin
buy percocet
buy oramorph
Buy oxycodone online
buy-nembutal liquid
https://dolorendo.com/
https://dolorendo.com/product/
https://dolorendo.com/product/comprar-oxicodona-en-linea/
https://dolorendo.com/product/comprar-oxicodon/
https://dolorendo.com/product/comprar-oxynorm-en-linea/
https://dolorendo.com/product/comprar-oxycontin-en-linea/
https://dolorendo.com/product/comprar-percocet-en-linea/
https://dolorendo.com/product/comprar-oramorph-sr/
https://dolorendo.com/productos-comprar-dilaudid/
https://dolorendo.com/product/comprar-vyvanse-en-linea/
https://dolorendo.com/product/comprar-suboxone-en-linea/
https://dolorendo.com/product/comprar-subutex-en-linea/
https://dolorendo.com/product/comprar-pastillas-nembutal/
https://dolorendo.com/productos-comprar-dilaudid/
https://dolorendo.com/product/comprar-acetaminofen-codeina/
https://dolorendo.com/product/comprar-adderall-en-linea/
https://dolorendo.com/product/comprar-desoxyn-en-linea/
https://dolorendo.com/product/comprar-dexedrina/
https://dolorendo.com/product/comprar-dmt-en-linea/
https://dolorendo.com/product/comprar-ketamina/
https://dolorendo.com/product/comprar-klonopin/
https://dolorendo.com/product/comprar-5-meo-dmt/
https://dolorendo.com/product/comprar-adipex-en-linea/
https://dolorendo.com/product/comprar-alphabol-cr/
https://buypsychedelicsnow.com/shop/buy-morphine-canada/
https://buypsychedelicsnow.com/shop/buy-5-meo-dmt-usa/
https://buypsychedelicsnow.com/shop/buy-codeine-online/
https://buypsychedelicsnow.com/shop/buy-4-aco-dmt-online/
https://buypsychedelicsnow.com/shop/buy-ayahuasca-online-usa/
https://buypsychedelicsnow.com/shop/black-tar-heroin/
https://buypsychedelicsnow.com/shop/buy-bolivian-cocaine/
https://buypsychedelicsnow.com/shop/buy-brown-heroin-usa/
https://buypsychedelicsnow.com/shop/buy-changa-online/
https://buypsychedelicsnow.com/shop/buy-white-heroin-online/
https://buypsychedelicsnow.com/shop/buy-dmt-online-canada/
https://buypsychedelicsnow.com/shop/buy-flakka-online/
https://buypsychedelicsnow.com/shop/buy-psilocybe-cubensis-online/
https://buypsychedelicsnow.com/shop/buy-ibogaine-online-canada/
https://buypsychedelicsnow.com/shop/ketamine-powder-for-sale/
https://buypsychedelicsnow.com/shop/buy-kratom-online-canada/
https://buypsychedelicsnow.com/shop/buy-lsd-online-canada/
https://buypsychedelicsnow.com/shop/mdma-for-sale-canada/
https://buypsychedelicsnow.com/shop/buy-mescaline-online-canada/
https://buypsychedelicsnow.com/shop/buy-mushroom-online-canada/
https://buypsychedelicsnow.com/shop/buy-psilocybin-online-canada/

https://achetersaxendaenligne.com/

https://achetersaxendaenligne.com/Produit/acheter-saxenda-en-ligne/

https://achetersaxendaenligne.com/

https://achetersaxendaenligne.com/Produit/acheter-saxenda-en-ligne/

https://achetersaxendaenligne.com/Produit/acheter-adipex-en-ligne/

https://achetersaxendaenligne.com/Produit/acheter-belviq-en-ligne/

https://achetersaxendaenligne.com/Produit/acheter-dexedrine/

https://achetersaxendaenligne.com/Produit/acheter-du-ritalin/https://achetersaxendaenligne.com/Produit/ozempic-sans-ordonnance/

https://achetersaxendaenligne.com/Produit/acheter-victoza-en-ligne/https://achetersaxendaenligne.com/Produit/acheter-vyvanse/

https://achetersaxendaenligne.com/Produit/achetez-qsymia-en-ligne/

Scooped by Gust MEES
February 7, 2019 11:52 AM
Scoop.it!

Teenage Hacker's Evil App Steals Apple Mac Passwords | #CyberSecurity #Apps #NobodyIsPerfect 

Teenage Hacker's Evil App Steals Apple Mac Passwords | #CyberSecurity #Apps #NobodyIsPerfect  | Apple, Mac, MacOS, iOS4, iPad, iPhone and (in)security... | Scoop.it

Yet another teenager has uncovered a serious weakness in Apple technology.

Just last week it emerged that a 14-year-old uncovered a bug that allowed snooping on iPhone and Mac users thanks to a problem in FaceTime. Now German 18-year-old Linus Henze has uncovered a vulnerability affecting the latest Apple macOS that leaves stored passwords open to malicious apps. That could include logins for your bank website, Amazon, Netflix, Slack and many more apps. And even though this is a Mac-only bug, if you’re using the iCloud keychain, passwords synced across iPhones and Macs may also be in danger.

To make matters worse, it’s likely that no fix is in the works. Henze isn’t disclosing his findings to Apple, telling Forbes the lack of payment for such research was behind his decision to keep the hack’s details secret from the Cupertino giant.

The researcher, who has uncovered other iOS and macOS bugs in the recent past, discovered a way into the Apple “keychain.” That’s the area of the macOS that stores private keys and passwords, making it a goldmine for hackers.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/


Gust MEES's insight:

Yet another teenager has uncovered a serious weakness in Apple technology.

Just last week it emerged that a 14-year-old uncovered a bug that allowed snooping on iPhone and Mac users thanks to a problem in FaceTime. Now German 18-year-old Linus Henze has uncovered a vulnerability affecting the latest Apple macOS that leaves stored passwords open to malicious apps. That could include logins for your bank website, Amazon, Netflix, Slack and many more apps. And even though this is a Mac-only bug, if you’re using the iCloud keychain, passwords synced across iPhones and Macs may also be in danger.

To make matters worse, it’s likely that no fix is in the works. Henze isn’t disclosing his findings to Apple, telling Forbes the lack of payment for such research was behind his decision to keep the hack’s details secret from the Cupertino giant.

The researcher, who has uncovered other iOS and macOS bugs in the recent past, discovered a way into the Apple “keychain.” That’s the area of the macOS that stores private keys and passwords, making it a goldmine for hackers.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/


No comment yet.
Scooped by Gust MEES
February 7, 2019 11:43 AM
Scoop.it!

New macOS zero-day allows theft of user passwords | #CyberSecurity #Apple #NobodyIsPerfect 

New macOS zero-day allows theft of user passwords | #CyberSecurity #Apple #NobodyIsPerfect  | Apple, Mac, MacOS, iOS4, iPad, iPhone and (in)security... | Scoop.it

A German security researcher has published a video over the weekend showing a new zero-day affecting Apple's macOS desktop operating system.

In an interview to German tech site Heise, Linus Henze, the security researcher, says the vulnerability allows a malicious app running on a macOS system to get access to passwords stored inside the Keychain --the password management system built into all macOS distributions.

The exploit is highly efficient because the malicious app doesn't need admin access to retrieve passwords from the user's Keychain file, and can even retrieve the contents of other Keychain files, which store passwords for other macOS users.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/


Gust MEES's insight:

A German security researcher has published a video over the weekend showing a new zero-day affecting Apple's macOS desktop operating system.

In an interview to German tech site Heise, Linus Henze, the security researcher, says the vulnerability allows a malicious app running on a macOS system to get access to passwords stored inside the Keychain --the password management system built into all macOS distributions.

The exploit is highly efficient because the malicious app doesn't need admin access to retrieve passwords from the user's Keychain file, and can even retrieve the contents of other Keychain files, which store passwords for other macOS users.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/


No comment yet.
Scooped by Gust MEES
January 24, 2019 4:57 PM
Scoop.it!

Malvertising campaign targets Apple users with malicious code hidden in images | #CyberSecurity #Steganography #NobodyIsPerfect 

Malvertising campaign targets Apple users with malicious code hidden in images | #CyberSecurity #Steganography #NobodyIsPerfect  | Apple, Mac, MacOS, iOS4, iPad, iPhone and (in)security... | Scoop.it

Apple users continue to be some of the favorite targets of malvertising campaigns, according to a report published this week by cyber-security firm Confiant.

The report describes a new malvertising group called VeryMal that's been going after Apple users, with the latest campaigns employing steganography techniques to hide malicious code inside ad images to avoid detection.

The Confiant report comes after the company discovered a different malvertising group last year, named ScamClub, which also exclusively targeted Apple users.

But while ScamClub was a much bigger operation, hijacking as many as 300 million web sessions for US-based iOS users, the VeryMal group is a much smaller in size, being blamed for only five million hijacks.

However, the difference, according to researchers, is that this newer group is way sneakier, employing steganography to hide the code responsible for redirecting users from legitimate sites to malicious ones.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/?&tag=Steganography


https://www.scoop.it/t/securite-pc-et-internet/?&tag=Steganography


Gust MEES's insight:

Apple users continue to be some of the favorite targets of malvertising campaigns, according to a report published this week by cyber-security firm Confiant.

The report describes a new malvertising group called VeryMal that's been going after Apple users, with the latest campaigns employing steganography techniques to hide malicious code inside ad images to avoid detection.

The Confiant report comes after the company discovered a different malvertising group last year, named ScamClub, which also exclusively targeted Apple users.

But while ScamClub was a much bigger operation, hijacking as many as 300 million web sessions for US-based iOS users, the VeryMal group is a much smaller in size, being blamed for only five million hijacks.

However, the difference, according to researchers, is that this newer group is way sneakier, employing steganography to hide the code responsible for redirecting users from legitimate sites to malicious ones.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/?&tag=Steganography


https://www.scoop.it/t/securite-pc-et-internet/?&tag=Steganography


No comment yet.
Scooped by Gust MEES
December 13, 2018 10:30 AM
Scoop.it!

Un malware qui vise les MAC OS s’invite pour la première fois dans le Top 10 des malwares détectés au 3ème trimestre de l’année 2018 | #Apple #CyberSecurity 

Un malware qui vise les MAC OS s’invite pour la première fois dans le Top 10 des malwares détectés au 3ème trimestre de l’année 2018 | #Apple #CyberSecurity  | Apple, Mac, MacOS, iOS4, iPad, iPhone and (in)security... | Scoop.it


Un malware qui vise les MAC OS s’invite pour la première fois dans le Top 10 des malwares détectés au 3ème trimestre de l’année 2018

décembre 2018 par WatchGuard® Technologies

WatchGuard® Technologies publie son Rapport sur la Sécurité Internet pour le troisième trimestre 2018. Pour la première fois au cours de ce trimestre, un malware visant spécifiquement les MAC OS a fait partie de la liste des dix malwares les plus couramment détectés par WatchGuard. Le rapport a également révélé que 6,8% des 100 000 sites web générant le plus de trafic dans le monde acceptent toujours des versions obsolètes et non sécurisées du protocole de chiffrement SSL. En outre, WatchGuard a enregistré plus d’attaques de malwares dans la zone Asie-Pacifique que dans toute autre région du monde, indiquant un accroissement significatif du nombre de malwares ciblant cette zone en 2018. Le rapport WatchGuard est basé sur des données récoltées par des dizaines de milliers de boîtiers UTM WatchGuard Firebox actifs à travers le monde, et analyse les campagnes de malware majeures, les attaques réseau et les menaces de sécurité ciblant les PME et les entreprises dites distribuées.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


Gust MEES's insight:

Un malware qui vise les MAC OS s’invite pour la première fois dans le Top 10 des malwares détectés au 3ème trimestre de l’année 2018

décembre 2018 par WatchGuard® Technologies

WatchGuard® Technologies publie son Rapport sur la Sécurité Internet pour le troisième trimestre 2018. Pour la première fois au cours de ce trimestre, un malware visant spécifiquement les MAC OS a fait partie de la liste des dix malwares les plus couramment détectés par WatchGuard. Le rapport a également révélé que 6,8% des 100 000 sites web générant le plus de trafic dans le monde acceptent toujours des versions obsolètes et non sécurisées du protocole de chiffrement SSL. En outre, WatchGuard a enregistré plus d’attaques de malwares dans la zone Asie-Pacifique que dans toute autre région du monde, indiquant un accroissement significatif du nombre de malwares ciblant cette zone en 2018. Le rapport WatchGuard est basé sur des données récoltées par des dizaines de milliers de boîtiers UTM WatchGuard Firebox actifs à travers le monde, et analyse les campagnes de malware majeures, les attaques réseau et les menaces de sécurité ciblant les PME et les entreprises dites distribuées.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


benbihi elmustapha's curator insight, April 4, 2022 6:17 PM
Formation Certifiante gratuite en #Cryptage assurée par une organisation internationale + suivi personalisé par un formateur experimenté dans le domaine et une équipe de support pour vous aider à réussir. Groupe 1 = https://bit.ly/3r3wDA6 Groupe 2 = https://bit.ly/38hxMNX