


Sécurité IT : Apple corrige 83 failles dans Safari
83 failles de sécurité, dont 72 jugées critiques, grouillaient dans les arcanes de Safari. Passé en version 5.1.4, le navigateur Internet d’Apple a ciblé son ver solitaire : la librairie WebKit.

 Your new post is loading...
 Scoop.it! Sécurité IT : Apple corrige 83 failles dans Safari

No comment yet.
Sign up to comment
Scoop.it!
Apple hat seinen Web-Browser Safari für Windows und Mac aktualisiert. In der neuen Version 5.1.4 hat der Hersteller etliche Sicherheitslücken beseitigt, die er zum Teil auch bereits in Mobile Safari und iTunes geschlossen hatte.
Scoop.it!

Trend Micro helped us pull together the ten most dangerous Mac viruses in OS X's history based on impact and prominence...
===> Most of the threats come from plug-ins and add-ons, like for browsers, which are usually distributed outside official app stores, says Jamz Yaneza, a threat research manager at Trend Micro. "If its not in the Mac App or App stores, just don't download it." <===
Scoop.it!

The Flashback malware, which Intego pointed out was infecting an increasing number of Macs, turns out to be using a novel technique to operate. Many types of malware use command and control servers that they connect to, in order to get instructions from the creators of the malware.
The problem with using these servers is that their IP addresses are specified in the malware code, and the servers can generally be taken down.
Scoop.it!
Über eine Sicherheitslücke in Apples iOS können App-Entwickler nicht nur auf das komplette Adressbuch, sondern auch auf die Foto-Bibliothek von Smartphone- und Tablet-Nutzern zugreifen.
Scoop.it!
Mac OS X sous la menace d’un dangereux cheval de Troie
Cette information est l’occasion de rappeler que le Mac d’Apple est aussi la cible des hackers mafieux et que la réputation sécuritaire de l’Unix embarqué comme OS du Mac ne le met pas à l’abri des menaces, alors que nombre d’utilisateurs des produits de la pomme continuent d’affirmer que le système suffit à les protéger.
Scoop.it!
A new malware variant sets out to punish those who haven’t been keeping up to date with updates.
Patching OS X is so simple, but yet there are people who still put it off. A new malware variant sets out to punish those who haven’t been keeping up to date with updates.
The new variant is a Trojan horse called ‘Flashback.G’ and is makes use of two exploits found on older versions of the Java runtime. Users with macs running OS X 10.6 ‘Snow Leopard’ are particularly at risk since this version came with Java preinstalled while 10.7 ‘Lion’ did not.
According to security firm Intego, this malware uses three tricks to try to get itself installed onto a system: read more...
Scoop.it!
Voici le programme* de la 4ème édition des GS Days, qui se tiendra le 3 avril à l’Espace Saint-Martin - 199 bis, rue Saint Martin, 75003 Paris.
Hack Mac OS X
Par exemple, est-il simple de pirater un Mac à distance ou depuis un accès physique ?
Une démonstration permettra notamment de mettre en exergue ===> la simplicité avec laquelle il est possible de compromettre un Mac depuis un accès physique… <===
Scoop.it!

La fonctionnalité Gatekeeper de contrôle des applications de Mac OS X Mountain Lion est accueillie favorablement par plusieurs experts en sécurité, même si des attaques restent possibles...
Scoop.it!
The company is jumping on a Wall Street Journal story accusing Google of sneaking past Safari's privacy settings to lash out at its rival. Read this blog post by Lance Whitney on Microsoft.
Scoop.it!

Das Ende vergangener Woche veröffentlichte Update auf Mac OS X 10.7.3 hat etlichen Benutzern das System zerschossen. Apple zieht deshalb die Delta-Updates zurück.
Scoop.it!

Les choses n'ont pas traîné, Apple propose d'ores et déjà au téléchargement une nouvelle version de la mise à jour de sécurité 2012-001 pour Snow Leopard (Client et Server).
Scoop.it!

Update fixes 38 vulnerabilities in Mac platform...
The update, Apple's first major OS X security fix of the year, will include some ===> 38 patches for security vulnerabilities <=== in the operating system!
===> Update! <===
|
Scoop.it!
Apple a livré hier une mise à jour importante de la version 5.1.4 de Safari, comprenant 83 correctifs. Le constructeur en profite aussi pour améliorer les performances de JavaScript sur Mac OS X Lion.
Scoop.it!
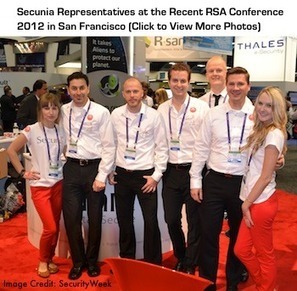
Secunia’s Chief Security Specialist hopes Apple will work better with researchers in the future and provide more informative status updates and estimated fix dates.
”It's regretful to experience that there are still some major software vendors that do not understand how to properly work with researchers,” Eiram added.
“Hopefully, Apple will in the future strive to work better with researchers to ultimately protect their customers by providing more informative status updates and estimated fix dates instead of prioritizing antiquated internal policies higher.”
Scoop.it!
Apple on Wednesday updated its iOS mobile operating system to rectify more than 80 vulnerabilities.
Scoop.it!

Influencés par le marketing rassurant d’Apple, les utilisateurs de Mac ne se protègeraient pas assez des virus et chevaux de Troie, selon certains spécialistes.
Le dernier en date, Flashback G, a été découvert il y a une semaine. Il exploite une faille encore présente sur certains ordinateurs qui ne sont pas à jour.
Scoop.it!
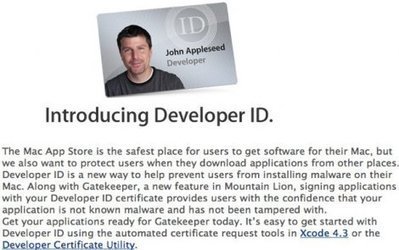
Apple compte sur les développeurs pour assurer la sécurité de Mountain Lion.
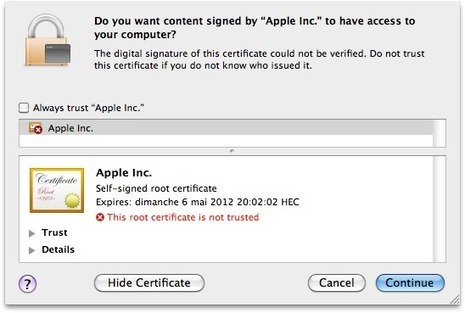
En effet, Gatekeeper pourra vérifier la provenance des applications et refuser le fonctionnement des logiciels non signé par Apple ou les développeurs certifiés.
Ainsi, la firme de Cupertino invite désormais les développeurs à rejoindre le programme Developer ID afin de disposer d'un certificat d'identification personnalisé qui servira à signer les applications.
Scoop.it!
Consumerization is happening now, but many IT departments simply aren’t prepared to deal with the new challenges and complexities it entails.
With IT managers increasingly urged by CEOs to stop saying ‘no’ and start supporting consumer tools, they need to reappraise their traditional approach. Put simply, IT needs flexible standards – they can’t say no but neither can they say yes to everyone.
Cyber crime is a multi billion dollar industry, funded and resourced like legitimate business operations. The criminal gangs need to know that any investment in their own resources is going to provide a decent return, and the best way of guaranteeing that is by targeting the one large homogenous platform, just as they did with Windows in the 90s. In the mobile world, this means iOS.
What is clear is that Apple is not the panacea for secure, manageable consumer devices in the enterprise that many believe.
Scoop.it!
If a Mac OS X user visits a web page, and their Java is not up to date, the malware infection will occur without their intervention.
===> UPDATE asap! <===
Scoop.it!

Intego a découvert de nouvelles variantes du cheval de Troie Flashback, qui avait touché les Mac à l'automne.
Scoop.it!

Apple says that applications that access contact data are in “violation” of the terms and conditions of the App Store, and a fix will soon...
Scoop.it!

Google has overrode security features in the iPhone's Safari browser to track users' behavior, according to a report.
Scoop.it!
Mac users need protecting from themselves as much as they do from malware.
Scoop.it!
Apple hat nach der letzten Aktualisierung im Oktober 2011 nun Sicherheitsupdates für die beiden Mac-Betriebssysteme 10.7 und 10.6 veröffentlicht.
|




