



A new variant of the Flashback Trojan that appeared last year can install itself on a Mac without need for an administrator's password.

 Your new post is loading...
 Scoop.it! A new variant of the Flashback Trojan that appeared last year can install itself on a Mac without need for an administrator's password. 
No comment yet.
Sign up to comment
Scoop.it!

Alors que pendant longtemps, la majeure partie des spécialistes n’imaginait pas que les virus en tous genres puissent arriver sur Mac, cela est désormais une réalité.
Les PC ne sont plus l’unique cible des pirates informatiques et des hackers.
Face au nombre croissant d’attaques qui subsiste sur internet, il est très important de se munir d’un antivirus pour Mac comme d’un antivirus pour PC. Concernant le système d’exploitation créé par Steve Jobs, il est visé par les cybercriminels car il y a de plus en plus de possesseurs de Mac, ce qui affute leur volonté de perturber de nouveaux utilisateurs.
Scoop.it!

Derzeit befinden sich mehrere Trojaner im Umlauf, die gezielt Macs infiltrieren und dafür auf Mechanismen setzen, die seit Jahren auch in Windows-Systemen genutzt werden.
Scoop.it!
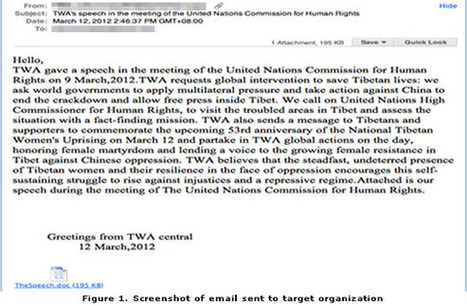
According to a newly published data, Mac OS X users are just as susceptible to targeted attacks, as Windows users are!!!
===> Nobody is perfect!!! <===
Scoop.it!

An espionage campaign targeting pro-Tibetan groups is employing malware that can seize control of employees' Macs and secretly siphon away confidential data.
Scoop.it!
Mac users are now prime targets as an APT attempts to execute on a Mac OS.
This development in targeted attacks just shows that the groups behind campaigns such as this one are taking into consideration changes in the computing landscape, such as the increase in the number of Mac users.
===> This adjustment to affect Macs also shows that they are refining their scope, and are really customizing their tools to suit their targets. <===
More on this as we are continuously investigating this. Stay tuned.
Scoop.it!

This analysis is focused on the OS X payload of a reported attack against Tibetan NGOs and the network protocol used to communicate with the C&C server.
Scoop.it!
The Flashback Trojan's latest iterations have evolved to infect Macs in different ways, but there are methods to detect and remove them. Read this blog post by Topher Kessler on MacFixIt.
Scoop.it!
Apple’s iOS mobile platform, like its desktop-and-notebook sibling Mac OS X, has garnered a reputation for strong security.
===> But as new holes in iOS's security crop up, this reputation may be exposed to less-than-friendly fire. <===
GM: NOBODY is perfect!
Scoop.it!

I’m guessing that the myth of OS X invulnerability to malware is pretty much busted by now: at any rate, there has been wave after wave of OS X-related malware reports in the past week or two.
Sophos were the latest big name to weigh in on the OSX/Imuler malware that DrWeb, Intego, ESET and your humble scribe have already commented on, though Sophos calls it Imuler-B and both Intego and ESET call it Imuler.C.
The Java attack has also been linked to bot-generated Twitter spam targeting Tibetan activist conversations by including hashtags like “#Tibet” and “#freetibet”, presumably in order to drown out political dissent.
Scoop.it!

A hole in Apple's mobile Safari can be exploited to display a different URL in the address field than the Web site being viewed in the browser.
Users of iOS 5 users, beware a security flaw in Safari that can be used to trick you into visiting potentially malicious Web sites.
Scoop.it!
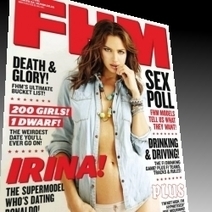
The Mac Imuler Trojan uses images of FHM supermodel Irina Shayk to do its dirty work.
Somehow I doubt that Mac users are any smarter than their Windows cousins when it comes to resisting temptation.
We're all human, after all. And there is a (probably significant) proportion of the population which isn't adverse to searching the web for nude pictures of supermodels.
Of course, the bad guys who spread malware know about human weakness all too well - and exploit it regularly to trick computer users into clicking on files and installing malicious code that exposes them to risks.
===> By default, Mac OS X doesn't display file extensions. Which means, that Mac users might be duped into believing that the file they are about to click on is a JPG image, rather than an application. <===
Scoop.it!

Keep in mind that this list is skewed toward professionals and technophiles who are using the iPad on a daily basis, but I also realize that these folks tend to use tablets like the iPad for non-work stuff as well, like reading the news in the morning during breakfast or a little entertainment on the plane during a business flight.
If you'd prefer to view this as a list instead of a photo gallery, then see the companion blog post http://www.techrepublic.com/blog/hiner/the-ipads-most-useful-apps-updated-for-2012/10373
Credit: Jason Hiner | TechRepublic
|
Scoop.it!
A new Flashback variant (Mac malware) has been spotted exploiting CVE-2012-0507 (a Java vulnerability). We've been anticipating something like this for a while now.
Oracle released an update that patched this vulnerability back in February… for Windows.
===> But — Apple hasn't released the update for OS X (yet). <===
Scoop.it!

Dissimulé dans un document Word, un malware tente d'exploiter une vieille faille pour infecter OS X.
Scoop.it!

The Opera Web browser for Mac OS X has been recently updated to version 11.62, with the latest update patching six security holes.
Scoop.it!
A backdoor Trojan horse, which would allow a remote hacker to access your Mac computer without your knowledge and potentially snoop on your files and activity, has been discovered hidden inside a b...
Scoop.it!

MacControl Trojan malware is being used in targeted APT attacks against Mac users. Researchers at Alienvault have found that the malicious program is targeting Tibetan officials and is being run from China.
===> Welcome to the age of targeted attacks, Mac users!!! <===
Perhaps having grown tired of owning Windows machines around the world for the last few years, attackers in China now have taken up the challenge of ===> going after Macs with the same kind of targeted attack tactics that have served them so well in the Windows world. <===
Scoop.it!

Bien qu’une faille dans Office Mac ait été identifiée et corrigée par Microsoft depuis 2009, des logiciels malveillants cherchent à s’attaquer par son intermédiaire aux systèmes Mac OS X qui n’ont pas été mis à jour.
Scoop.it!

F-Secure Security Labs brings you the latest online security news from around the world. Ensure that you are up-to-date with the latest online threats to guarantee your online wellbeing.
Scoop.it!
Une faille de sécurité grouille dans les arcanes de Safari. Elle permet à un site Internet d’afficher dans la barre d’adresse une fausse URL. Major Security en appelle à la vigilance face au phishing.
Or, un tel mutisme n’a d’égal que le risque grandissant que courent les utilisateurs de Safari, plus exposés encore au phishing.
Scoop.it!
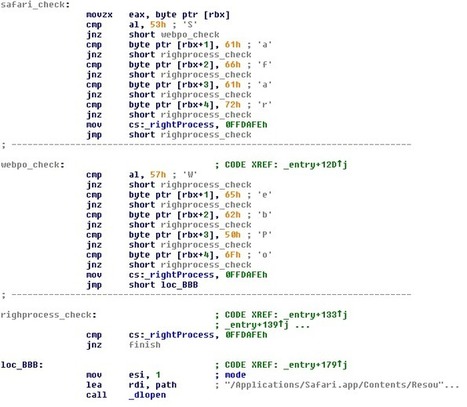
On Monday, I provided steps on how to avoid your Mac being compromised by the Flashback trojan. Today I will provide information on how to locate a Flashback infection.
To better understand the steps below, it is better to also know a bit about Flashback. It's an OS X malware family that modifies the content displayed by web browsers. To achieve this, it interposes functions used by the Mac's browsers.
The hijacked functions vary between variants but generally include CFReadStreamRead and CFWriteStreamWrite: read more...
Scoop.it!
La version de Safari proposée dans iOS 5.1 souffre d'un mal étrange et plutôt embêtant : il est possible de lui faire prendre des vessies pour des lanternes !
En attendant un éventuel correctif, la méfiance est donc de mise.
Scoop.it!
Security researchers from Sophos, have intercepted a currently circulating Mac OS X malware variant of the OSX/Imuler trojan horse.
Upon execution the malware will delete the original infection file and only leave an image file of Irina Shayk. It will also open a backdoor on the infected host, transferring private information from the infected host to a remote Web server.
===> End and corporate users are advised to turn on “Show all filename extensions” option in Finder in order to differentiate between different file types and avoid interacting with malicious applications. <===
Scoop.it!

Security researchers from Intego, have intercepted a new variant of the Imuler trojan horse targeting Mac OS X users.
|




