Your new post is loading...

|
Scooped by
Gust MEES
April 7, 2012 9:52 AM
|
Read 'Flashback botnet: The end of the Mac's malware immunity?' on Digital Trends. A new variant on Flashback malware exploits a Java vulnerability to... But the day may come — soon — when the Mac malware universe warrants widespread use of high-quality antivirus software.
|
|
Scooped by
Gust MEES
April 6, 2012 8:52 PM
|
Researchers from Kaspersky Lab supplied more evidence that there are more than 500,000 Macs infected by the Flashback malware. If correct, that would represent more than 1 percent of Macs out there.
|
|
Scooped by
Gust MEES
April 6, 2012 5:38 PM
|
Recent Flashback attacks show Apple's surging popularity has gained the attention of hackers. "All the stuff the bad guys have learned for doing attacks in the PC world is now starting to transition to the Mac world," McAfee Labs director of threat intelligence Dave Marcus told AFP. "Mac has said for a long time that they are not vulnerable to PC malware, which is true; ===> they are vulnerable to Mac malware." <===
|
|
Scooped by
Gust MEES
April 6, 2012 1:03 PM
|
Igor Soumenkov
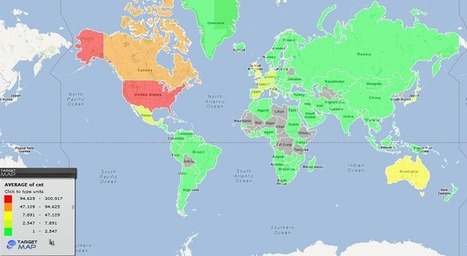
Kaspersky Lab Expert Earlier this week, Dr. Web reported the discovery of a Mac OS X botnet Flashback (Flashfake). According to their information, the estimated size of this botnet is more than 500, 000 infected Mac machines. Our logs indicate that a total of 600 000+ unique bots connected to our server in less than 24 hours. They used a total of 620 000+ external IP addresses. More than 50% of the bots connected from the United States. Read more...
The Flashback Mac OSX Trojan is building a large botnet and researchers are wondering whether there are Windows PCs involved too.
|
|
Scooped by
Gust MEES
April 6, 2012 9:02 AM
|
The company launches another Java update designed to patch a hole in the Mac OS exploited by the widespread Flashback trojan. Read this blog post by Lance Whitney on Apple.
|
|
Scooped by
Gust MEES
April 6, 2012 7:07 AM
|
Un éditeur de sécurité russe estime à 600 000 le nombre de machines d’Apple infectées par le Trojan. MacOS reste la plate-forme la plus hermétique aux malwares mais son succès dans le monde suscite de plus en plus d'intérêt de la part des pirates. La preuve : l'essor de Flashback, un Cheval de Troie qui aurait tendance à vite se propager sur la planète. Le malware qui profite de deux failles de sécurité du plugin Java s’est propagé principalement en Amérique du Nord (76,4%), au Royaume-Uni (12,8%) et en Australie (6,1%). La France quant à elle représenterait 0,6% des ordinateurs infectés par le cheval de Troie. C’est la compagnie d’anti-virus Russe DrWeb qui a mené l’enquête.
|
|
Scooped by
Gust MEES
April 5, 2012 6:21 PM
|
Bien que la menace d’une infection soit nettement réduite pour un utilisateur Mac, ===> le risque zéro n’existe pas. <=== Un troyen est en train de prouver d’ailleurs qu’il peut infecter des centaines de milliers de machines : Flashback.
|
|
Scooped by
Gust MEES
April 5, 2012 3:50 PM
|
The recent reemergence of the Flashback OSX trojan has shown a lot of things, but none more clearly than this: I have no clue how to counter virus and... I remember telling friends and supervisors multiple times that if a major Mac virus or trojan were to emerge, I would be at a complete loss as to how to fight it. This is probably still true, as the emergence of the Flashback trojan has shown most clearly. The most recent version of Flashback targets a unpatched Java vulnerability in OSX, one that Oracle fixed months ago but Apple never got around to relaying. Now, I’m still not entirely sure what Flashback does, but I was pretty completely clueless on how I could fight it. This is the bitter reality of being a Mac owner in 2012. I have very little idea of how to keep my machine safe. And I imagine many other Mac owners feel the same way. If the half million Flashback-infected Macs are any indication, ===> Mac owners are all going to need a crash course in computer safety. And fast. <===
|
|
Scooped by
Gust MEES
April 5, 2012 3:10 PM
|
If you thought your Mac was safe from harmful computer viruses, think again. Ars Technica reported on April 4 that the "Mac Flashback trojan" has returned with a vengeance in recent weeks, now affecting hundreds of thousands of Apple laptops. ===> If you thought your Mac was safe from harmful computer viruses, think again. <=== ===> Nobody is perfect!!! <=== Ars Technica reported on April 4 that the "Mac Flashback trojan" has returned with a vengeance in recent weeks, now affecting hundreds of thousands of Apple laptops. Ars first reported about the issue on April 2, explaining that anti-virus and computer security firm F-Secure had spotted the virus in action.
|
|
Scooped by
Gust MEES
April 5, 2012 2:24 PM
|
Le malware Flashback exploite une faille de Java sous Mac OS X pour voler les données d'accès à des sites web populaires. Depuis deux mois, BackDoor.Flashback.39 espionne les faits et gestes de milliers d'utilisateurs de produits Apple sur le web. La compagnie à la pomme a réagi en sortant un patch pour Java... il y a deux jours. Le 4 avril, Dr. Web, une firme russe de solutions anti-virus, évaluait le nombre d'ordinateurs infectés à 550 000, puis ajustait son estimation à 600 000 quelques heures plus tard dans un message sur Twitter.
|
|
Scooped by
Gust MEES
April 5, 2012 12:02 PM
|
Once on a system, the malware opens a backdoor and steals data. Using sinkhole technology, Dr. Web analysts redirected the botnet traffic to their own servers to count infected hosts.
|
|
Scooped by
Gust MEES
April 5, 2012 11:38 AM
|
Malicious software designed to steal personal information has infected more than 600,000 Mac computers worldwide, warns a Russian cyber security firm, with the vast majority of victims in the United States and Canada...
|
|
|
Scooped by
Gust MEES
April 7, 2012 9:44 AM
|
My work Mac (Photo credit: randomduck) Following my piece the other day on how an estimated 600,000 Macs are infected with the Flashback Trojan, I've been getting a lot of questions and queries about how to tell if a system is infected witht his malware,... Read more...
|
|
Scooped by
Gust MEES
April 6, 2012 7:25 PM
|
The Mac Flashback trojan is certainly making headlines, and it could even be making the rounds on your own computer. There are ways to check if you have it, though, and we have a few other tips for protecting yourself.
|
|
Scooped by
Gust MEES
April 6, 2012 4:17 PM
|
[Rich Mogull has worked in the security world for 18 years. He writes for TidBits and works as a security analyst through Securosis.com.] ===> We’ve entered a new era in Mac security, <=== but there’s no need to panic... The bad guys clearly care more about Macs now. But we need to keep our perspective: We still see far less malware for Macs than we do for, say, Android phones. Yet there's no doubt that Flashback is a significant development. ===> I believe it shows we will see more malware on Macs. <=== I’m also convinced these will be infrequent events and not the ongoing onslaught of epidemics that some observers are predicting— ===> as long as we all take precautions and stay vigilant. <=== ===> A MUST READ! <===
|
|
Scooped by
Gust MEES
April 6, 2012 12:37 PM
|
Security industry insiders have long known the Mac platform has its holes. The Flashback Trojan is the first in-the-wild issue that's confirmed this, and big-time. More will follow unless Apple steps up its game. Apple has cultivated a myth about security on the Mac platform. The myth goes like this: Apple users don't need antivirus software. We're more secure than anything out there. Security worries are overblown.
In reality, Apple practiced security by obscurity with the Mac.
Those days may be ending in a hurry. Apple's relative silence about malware is going to have to end as the company finds itself managing a large ecosystem, noted ZDNet's Ed Bott.
Delivering massive security updates during product launches and software rollouts just isn't going to cut it. ===> Read more, YOU should!!! <===
|
|
Scooped by
Gust MEES
April 6, 2012 9:15 AM
|
The nightmare scenario for Mac owners is here. At least 600,000 Macs worldwide have been infected, silently, by the Flashback virus. What makes this outbreak especially chilling is that the owners of infected Macs didn’t have to fall for social engineering, give away their administrative password, or do something stupid. All they had to do was visit a web page using a Mac that had a current version of Java installed. Macs are not immune. For years Apple owners have been told that Macs don’t get viruses, but we know that’s not true. And Apple’s casual approach to security updates makes them arguably more vulnerable to this sort of attack than other platforms.
|
|
Scooped by
Gust MEES
April 6, 2012 7:12 AM
|
C'est du jamais vu : une entreprise de sécurité russe a découvert un réseau de 600 000 Mac zombies, infectés à cause d'une vulnérabilité de Java. On peut même ici parler d’erreur, car la faille qu’il exploite est loin d’être inconnue. Depuis le mois de février, Oracle propose une mise à jour critique pour la corriger. Les utilisateurs de Windows qui utilisent Java l’ont par exemple obtenue grâce à l’outil de mise à jour de Java. Mais sur Mac, c’est Apple qui centralise ces mises à jour de sécurité et qui les distribue par l'intermédiaire d'un outil intégré à Mac OS X. Or la marque à la pomme n’avait pas publié ce correctif ! Il a été poussé avant-hier, mardi 3 avril 2012, comme le montre cet avis de sécurité. ===> Un peu tard, quand on sait que 600 000 machines sont infectées par ce virus. <===
|
|
Scooped by
Gust MEES
April 6, 2012 7:03 AM
|
Mac OS X succombe au cheval de Troie Flashback
Le dénommé Flashback poursuit ses ravages sur Mac OS X et atteint les 550 000 machines infectées. Il s’agit d’un cheval de Troie qui exploite deux failles de sécurité Java.
Le 16 mars et le 3 avril, Apple a déployé deux correctifs destinés à résorber les failles en question, sans toutefois orchestrer de mise à jour silencieuse. ===> Aussi, nombre d’utilisateurs n’ont pas appliqué ces patchs. <=== Autant de postes de travail en sont restés vulnérables.
|
|
Scooped by
Gust MEES
April 5, 2012 6:08 PM
|
Tips for how to find out if you're infected with the Mac Flash trojan and what to do about it.
|
|
Scooped by
Gust MEES
April 5, 2012 3:13 PM
|
Half a million Macs infected (a dream, dashed) Half a million Macs are infected by a botnet, and all I can think of is this sentence from a 2006 ad: “PCs are not Macs.”... ===> Nobody is perfect!!! <===
|
|
Scooped by
Gust MEES
April 5, 2012 2:54 PM
|
There are 600,000 Macs being remotely controlled by the growing Mac botnet, according to Russian antivirus company...
|
|
Scooped by
Gust MEES
April 5, 2012 12:13 PM
|
F-Secure Security Labs brings you the latest online security news from around the world. Ensure that you are up-to-date with the latest online threats to guarantee your online wellbeing. Our Anti-Virus for Mac detects the latest Flashback variant as Trojan-Downloader:OSX/Flashback.K. Here's some of our recent Flashback descriptions: • Flashback.I
• Flashback.K Our previous Mac related posts include instructions on how to disable Java, how to check for a Flashback infection, and manual removal: • Mac Malware at the Moment
• Are you having a (Mac) Flashback?
• Mac Flashback Exploiting Unpatched Java Vulnerability ===> For those of you celebrating the Easter Holiday this weekend — if you're visiting your parents and they have a Mac — now is the time to update, disable, or remove their Java client plugin/installation! <=== (And that goes for Windows too.)
|
|
Scooped by
Gust MEES
April 5, 2012 11:45 AM
|
Le programme malveillant Flashback est capable de modifier des pages Internet sur les ordinateurs infectés. Apple a mis en ligne un correctif pour bloquer son installation. Le programme malveillant Flashback est capable de modifier des pages Internet sur les ordinateurs infectés. Apple a mis en ligne un correctif pour bloquer son installation. ===> Apple l'affirme toujours sur son site Internet: les Mac sont «immunisés contre les virus PC». <=== Mais cela ne les empêche pas d'être touchés par des programmes malveillants spécialement conçus pour eux. Selon l'éditeur russe de logiciels de sécurité Dr.Web, plus de 600.000 Mac auraient été infectés dans le monde par le cheval de Troie Flashback. La plupart des ordinateurs ont été touchés aux États-Unis (56,6%), ===> dont 274 à Cupertino, la ville américaine qui héberge le siège d'Apple. <===
|