 Your new post is loading...

|
Scooped by
Gust MEES
March 17, 2016 1:34 PM
|
Décidément les chercheurs du Palo Alto Networks ont fort à faire ces dernières semaines. Après le ransomware KeRanger détecté sur MacOSX, c'est au tour d'iOS d'être touché par un nouveau malware. Toutefois, AceDeceiver fait dans la nouveauté. Au lieu d'essayer de leurrer les systèmes d'Apple, ce dernier a trouvé un moyen de pénétrer iOS sans même avoir besoin d'un quelconque certificat.
Habituellement lorsqu'un utilisateur achète et télécharge des applications depuis iTunes/App Store, la boutique demande obligatoirement un code d'autorisation afin d'approuver et de sécuriser l'installation.
Dans le cas de cette attaque, les hackers ont exploité une faille pour récupérer le code généré par iTunes. De cette manière, ils peuvent installer n'importe quelle application souhaitée sur appareil. Ils ont par la suite développé un logiciel qui simule le comportement d'un client iTunes cela permet de leurrer le système qui pense que l'application a bien été achetée et qu'elle est sécurisée. L'installation de l'application corrompue ce fait alors sans aucun problème sur votre appareil.
Ce type d'attaque "man in the middle" est très problématique car quand bien même les applications corrompues sont supprimées de l'App Store, la faille reste accessible. Learn more / En savoir plus / Mehr erfahren: http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/?tag=AceDeceiver
|
|
Scooped by
Gust MEES
March 16, 2016 4:06 PM
|
|
|
Scooped by
Gust MEES
March 8, 2016 11:05 AM
|
|
|
Scooped by
Gust MEES
March 7, 2016 7:54 AM
|
Des chercheurs en sécurité ont découvert ce qu’ils pensent être la toute première attaque par ransomware ou rançongiciel ciblant les utilisateurs de Mac d’Apple. Cette menace est actuellement active sur Internet et se diffuse via un logiciel de téléchargement de fichiers Torrent.
Cette attaque a été détectée en toute fin de semaine dernière par des chercheurs de Palo Alto Networks. Ces derniers ont donc identifié un ransomware, "KeRanger", dissimulé au sein d’un client BitTorrent populaire sous OS X, Transmission.
400 dollars pour récupérer ses fichiers Learn more / En savoir plus / Mehr erfahren: http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/?tag=RANSOMWARE http://www.scoop.it/t/ict-security-tools/?tag=Ransomware
|
|
Scooped by
Gust MEES
March 7, 2016 6:53 AM
|
|
|
Scooped by
Gust MEES
March 6, 2016 6:19 PM
|
|
|
Scooped by
Gust MEES
March 1, 2016 8:27 PM
|
|
|
Scooped by
Gust MEES
February 27, 2016 6:51 PM
|
|
|
Scooped by
Gust MEES
February 18, 2016 3:23 PM
|
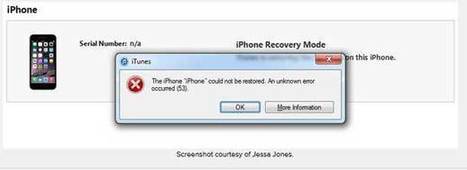
Apple has released an update for iOS 9.2.1, which will solve the annoying ‘Error 53’ message that was bricking iPhones.
If you’re not familiar, Error 53 happened when devices with new Touch ID sensors from unauthorized Apple repair shops — using components not sourced properly — failed fingerprint scans.
When the new Touch ID hardware was used, it caused iOS to freak out; it could tell the components weren’t original, and thus shut the phone down entirely as a safety precaution.
Learn more / En savoir plus / Mehr erfahren:
http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/?tag=Error53
|
|
Rescooped by
Gust MEES
from 21st Century Learning and Teaching
February 14, 2016 6:50 PM
|
Many of OS X’s most popular apps were recently revealed to be vulnerable to man-in-the-middle (MiTM) attacks.
The vulnerability specifically targets those that use Sparkle — a third-party software update framework — and unencrypted HTTP connections.
A security engineer from Vulnsec, known as Radek, said the vulnerability works on both El Capitan and its predecessor, Yosemite.
The total number of apps affected isn’t known, but Radek did estimate the number to be “huge.” Some of those confirmed as vulnerable are:
Camtasia 2 (v2.10.4)
DuetDisplay (v1.5.2.4)
uTorrent (v1.8.7)
Sketch (v3.5.1)
Additionally, security researcher Jonathan Zdziarski told Ars Technica that the ‘Hopper’ reverse engineering tool and ‘DXO Optics Pro’ are also susceptible.
Learn more:
http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
|
|
Scooped by
Gust MEES
February 10, 2016 10:28 AM
|
A security engineer has recently discovered a serious vulnerability in Sparkle, the widely used open source software update framework for Mac applications, that could be exploited by attackers to mount a man-in-the-middle attack and ultimately take control of the computer if they are located on the same network.
Since it inception in 2006, Sparkle slowly became the de-facto standard for OS X application updates. It is used by many, many popular applicationsincluding Evernote, Coda, VLC Media Player, Slack, and TeamViewer (to name a few), but not all these apps are vulnerable to this attack.
That's because the flaw can be exploited only if the app using the vulnerable version of Sparkle also uses HTTP to receive updates.
"The vulnerability is not in code signing itself. It exists due to the functionality provided by the WebKit view that allows JavaScript execution and the ability to modify unencrypted HTTP traffic (XML response)," explained the researcher, who goes by the name of Radek.
Learn more / En savoir plus / Mehr erfahren:
http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
|
|
Scooped by
Gust MEES
February 5, 2016 7:21 AM
|
The company releases iOS 9.2.1 and OS X 10.11.3 with mostly security fixes.
Nine fixes were posted for the Mac platform, including a fix for a flaw that could've allowed an attacker to execute code with kernel privileges. The patch also comes with fix for an issue that prevents some Macs from waking from sleep when connected to some 4K-resolution displays. Another batch of nine fixes were also posted for the iOS platform, including a WebSheet flaw that could've allowed a malicious captive portal from accessing user cookies.
Learn more / En savoir plus / Mehr erfahren:
http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
|
|
|
Scooped by
Gust MEES
March 17, 2016 10:46 AM
|
|
|
Scooped by
Gust MEES
March 9, 2016 3:35 AM
|
Erstmals zielt funktionstüchtige Ransomware auf OS-X-Nutzer ab. Nach der Infektion bleiben drei Tage, bis "KeRanger" Dokumente verschlüsselt. Nutzer sollten prüfen, ob sie betroffen sind – und Gegenmaßnahmen ergreifen.
Die Mac-Schad-Software "KeRanger" setzte als Infektionsweg – soweit bislang bekannt – auf den BitTorrent-Client Transmission. Die Angreifer hatten offenbar Zugriff auf den Server, über den das OS-X-Programm verteilt wird. Das normale Disk-Image mit Transmission 2.90 sei durch eine manipulierte Version ersetzt worden, die nach Angabe der Entwickler nur rund 6500 Mal heruntergeladen wurde.
Nach der Infektion wartet KeRanger drei Tage ab, bis die Malware anfängt, Nutzerdokumente zu verschlüsseln, als Lösegeld wird vom Nutzer dann ein Bitcoin gefordert, umgerechnet rund 380 Euro. Es ist möglich, dass KeRanger künftig auch auf andere Wege zur Infektion setzt. Learn more / En savoir plus / Mehr erfahren: http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/?tag=RANSOMWARE http://www.scoop.it/t/ict-security-tools/?tag=Ransomware
|
|
Scooped by
Gust MEES
March 7, 2016 9:30 AM
|
|
|
Scooped by
Gust MEES
March 7, 2016 7:09 AM
|
|
|
Scooped by
Gust MEES
March 7, 2016 6:43 AM
|
|
|
Scooped by
Gust MEES
March 4, 2016 2:13 PM
|
When Apple’s Worldwide Developer Certificate expired in February it caused problems for some developers, but another major problem that’s going to affect more people has just surfaced: it breaks OS X installers.
If you’ve created an OS X installation CD or downloaded an installer it won’t work anymore because it can’t be verified with Apple. To get it going again, you need to re-download the entire installer and create a new CD, which is an utter hassle. Learn more: http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
|
|
Scooped by
Gust MEES
February 19, 2016 7:20 PM
|
|
|
Scooped by
Gust MEES
February 15, 2016 1:38 PM
|
|
|
Scooped by
Gust MEES
February 11, 2016 4:36 AM
|
|
|
Scooped by
Gust MEES
February 5, 2016 6:28 PM
|
Anyone who has been using computers for any length of time should (hopefully) be aware of the endless ritual of updating Adobe Flash against security vulnerabilities. Even if you don't run Flash on your computer, you've surely seen the many headlines in the tech media over the years of the importance of keeping Adobe Flash (and its Acrobat PDF Reader stablemate) updated to protect against malicious attack.
So, what better way to trick someone into having their computer infected than by disguising it as an actual Adobe Flash update?
That's precisely what criminals are doing now, in their attempts to infect Apple Mac users with scareware.
Learn more:
http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
|
|
Scooped by
Gust MEES
January 20, 2016 10:17 AM
|
New iOS 9.2.1 is now available.
Users of iPhones, iPads and iPods probably didn't give much thought to Tuesday's iOS update, which brings the mobile OS to version 9.2.1. According to Apple, the update contains "security updates and bug fixes," with the company highlighting an issue that can prevent app installation completion when using an MDM server (more data can be found here).
But it's notable that one of those security updates fixes quite a nasty security bug that's been discovered nearly three years ago.
Learn more / En savoir plus / Mehr erfahren:
http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
|


















Learn more / En savoir plus / Mehr erfahren:
http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/?tag=AceDeceiver