opexxx
111.9K views |
+2 today


 Your new post is loading...
 Scoop.it! 
Hcon Security Testing Framework (HconSTF) downloads... 
Scoop.it!
RT @freebsd: BLOG: FreeBSD on Pi: more stuff: Long overdue update on how the things are going with FreeBSD on Raspberry Pi. W... Via F. Thunus
Scoop.it!
Backdooring Windows Machine With Metasploit on Back-Track 5 my facebook id got spammed by me (mistake), so from now my new id is https://www.facebook.com/jag... Via backtracktutorial
Scoop.it!

Extreme GPU Bruteforcer is a professional solution for recovering passwords from hashes using GPU... Via sachin
Scoop.it!

Javascript code to determine whether a website visitor is currently logged into a social media site (Twitter, Facebook or Google+). Via sachin
Scoop.it!
DNSChef is a highly configurable DNS proxy for Penetration Testers and Malware Analysts. A DNS proxy (aka "Fake DNS") is a tool used for application network traffic analysis among other uses. For example, a DNS proxy can be used to fake requests for "badguy.com" to point to a local machine for termination or interception instead of a real host somewhere on the Internet Via sachin
Scoop.it!
Obfuscation and detection of embedded executables We're going to talk a little bit more about how our new Cryptam system detects malware documents based on identification of the encrypted executables. A document exploit needs to install an executable, those executables are usually either obfuscated and embedded in the document, or downloaded from a remote site. Via sachin
Scoop.it!

Stephan Chenette Says -- This year I gave a series of presentations on "The Future of Automated Malware Generation". This past week the presentation finished its final debut in Tokyo on the 10th anniversary of PacSec. Via sachin
Scoop.it!
UPR - Ubuntu Privacy Remix: The goal of Ubuntu Privacy Remix is to provide an isolated working environment where sensitive data can be dealt with safely
|
Scoop.it!
How To Get A Fully Undetectable Backdoor/Payload With Set And Metasploit | Deceptive room (RT @Carbonn992012How To Get A Fully Undetectable Backdoor/Payload With Set And Metasploit http://t.co/nKaln3La ; Via Daniel A. Libby, CFC
Scoop.it!
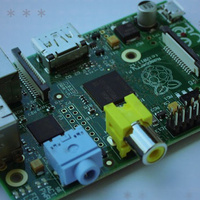
Set Up a Raspberry Pi as a Personal Web ServerLifehackerSet Up a Raspberry Pi as a Personal Web Server Want to set up your own web server for a landing page or portfolio, but don't feel like paying a monthly fee? Via F. Thunus
Scoop.it!
Convert metasploit cachedump files to Hashcat format for cracking By Commandlinefu.com. cd ~/.msf4/loot && cat *mscache* | cut -d '"' -f 2,4 | sed s/\"/\:/g | tr -cd '\11\12\40-\176' | grep -v Username | cut -d : -f 1,2 | awk -F':' ... Via Daniel A. Libby, CFC
Scoop.it!

Introduction Many have heard about the infamous DLL Hijacking attacks, but one subcategory of such attacks is far from being well-known: COM Hijacking, or COM-Server Based Binary Planting. What do these attacks have in common with the DLL Hijacking? In order to answer that question, let's examine the OLE\COM mechanism used in Windows. Via sachin
Scoop.it!

For all the folks who bought DVD-less Kindle versions of the cookbook, all the folks who received a DVD with their paper copy but want updates to the tools, and even for folks who just want to experiment with the tools without buying the book, please feel free to download with an SVN client here: Via sachin
Scoop.it!

It seems that more and more these days I find myself battling head to head against my client’s Antivirus Software. Payloads I encoded to successfully bypass one solution get picked up by another. An executable that walked effortlessly past one AV this week gets stopped dead in its tracks by the very same software build at a different client the week later. Via sachin
Scoop.it!
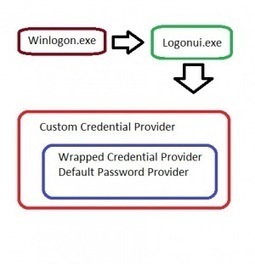
For the Eternally Impatient Via sachin
Scoop.it!
Requirement: Jailbroken iDevice and AdBlocker by @_Yllier_ for $1.99 Via 0xerror
Scoop.it!
Presently, my phone is a Samsung Galaxy S3 GT-I9300. But in general the following steps should be applicable to any Android device. First, download Android SDK and NDK. From SDK you can get the ...
|