Via ganassa

 Your new post is loading...
 Scoop.it! 
No comment yet.
Sign up to comment
Scoop.it!
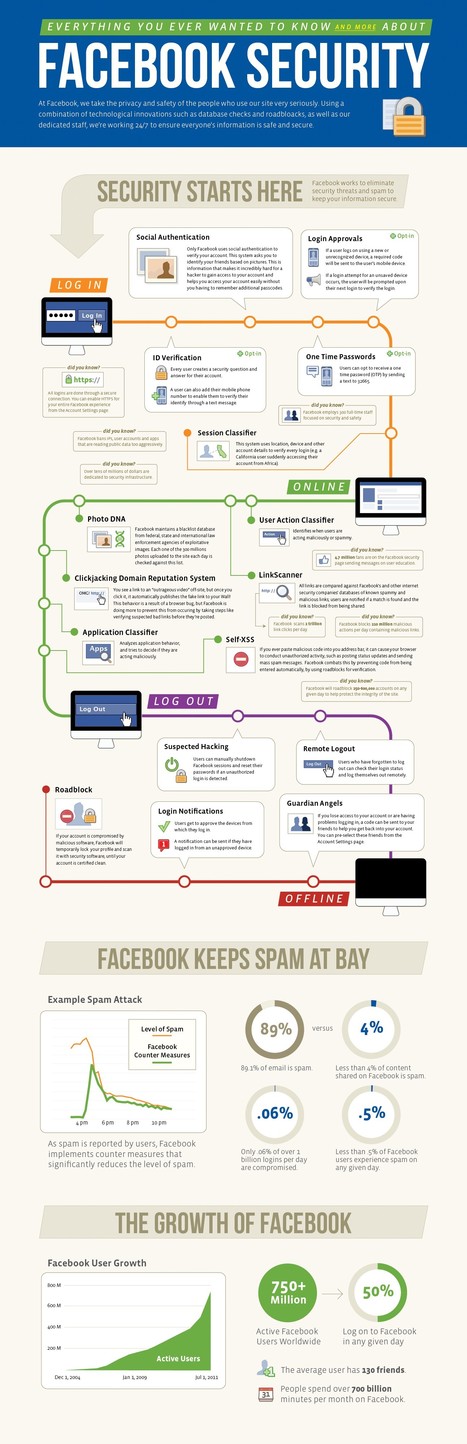
Infographics on Facebook Security Guide to stay away from Spam and Hacking in Social Networking world with Facebook Spamming Apps with Implementing Security... Via Richard H Harris
Scoop.it!
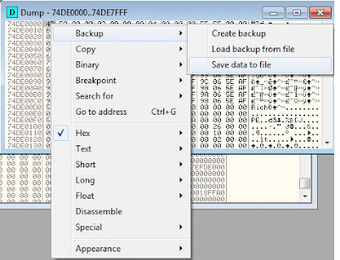
The idea started as an attempt to implement "System Calls Hooking" from user-mode under Wow64 processes (32-bit processes running on 64-bit versions of Windows). Via sachin
Scoop.it!
Author Comments: An email arrives in your inbox: "You have to check out this picture!" It came from your friends address, which you know and trust. It beckons you to open it. Maybe you weren't fooled this time, but it's likely at least one of the 50 other recipients couldn't resist. Via sachin
Scoop.it!
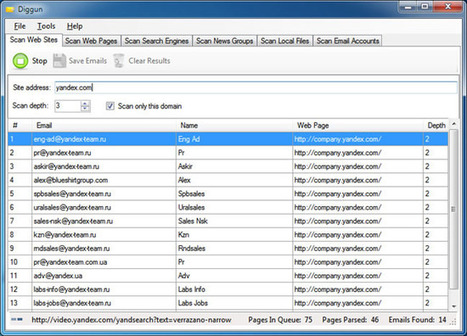
Diggun automatically extracts email addresses and user names from various sources like Web Sites, Search Engines, News Groups, Files, Email Accounts. The extracted emails and names can be exported to various formats, including CSV, TXT and XML. Create your mailing lists with a simple click. Via cheron guillaume
Scoop.it!
Scripts and templates to assist with using pywws on the Raspberry Pi as an automated weather station. (RT @EdwardORegan: Added example.php to github for @Raspberry_Pi weather station; is there anything else anyone needs? Via F. Thunus
|
Scoop.it!
Diggun automatically extracts email addresses and user names from various sources like Web Sites, Search Engines, News Groups, Files, Email Accounts. The extracted emails and names can be exported to various formats, including CSV, TXT and XML. Create your mailing lists with a simple click. Via cheron guillaume
Scoop.it!
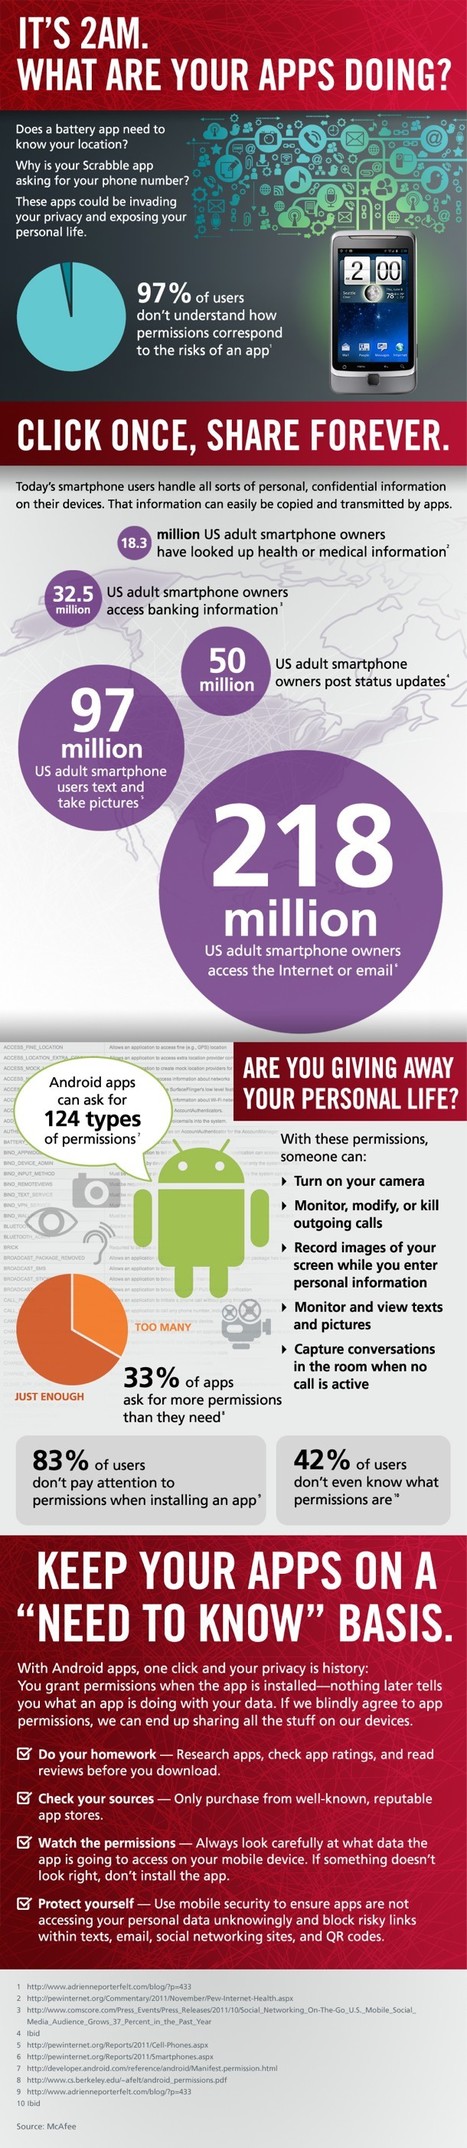
Infographics on Case study at Mobile Android Apps Permission vulnerability, starting Apps integration at 2AM on Google Play Store with malware attack on tablet... Via Richard H Harris
Scoop.it!
OWASP OWTF 0.15 - The Offensive Testing Framework. Download Penetration Testing and Security Tools at Tools Yard archive by The Hacker News. Via cheron guillaume
Scoop.it!
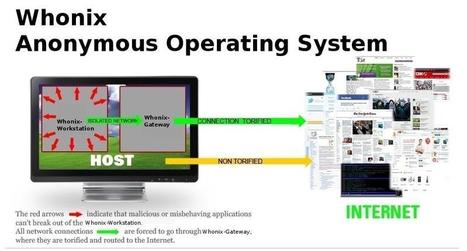
Whonix (called TorBOX or aos in past) is an anonymous general purpose operating system based on Virtual Box, Debian GNU/Linux and Tor. By Whonix design, IP and DNS leaks are impossible. Not even malware with root rights can find out the user's real IP/location. Via 0xerror
Scoop.it!
For example one could fingerprint all the extensions current user has installed. Also, they suffer from common web vulnerabilities. XSS is so "popular" that I've built XSS Chef -to assist the exploitation. Together with @theKos we ran workshops on exploiting Chrome extensions. Via sachin
Scoop.it!
Joe Document Dissector is an automated malware analysis platform for detecting malicious documents... Via sachin
Scoop.it!
DNS is a naming system for computers that converts human readable domain names e.g. (infosecinstitute.com) into computer readable IP-addresses. However some security vulnerabilities exist due to misconfigured DNS nameservers that can lead to information disclosure about the domain. Via sachin
Scoop.it!
When it comes to cloud-based data protection, there are many concerns and misconceptions about security, data privacy, and compliance. Via Richard H Harris
Scoop.it!

Current version: 0.1.1 Summary [+] Read 32- and 64-bit PE files (PE, PE+) for Windows, work similar with both formats [+] Rebuild 32- and 64-bit PE files [+] Work with directories and headers [+] Convert addresses [+] Read and write PE sections [+] Read and write imports [+] Read and write exports [+] Read and write relocations [+] Read and write resources [+] Read and write TLS [+] Read and write image config [+] Read and write basic .NET information [+] Read bound imports [+] Read exception directory (PE+ only) [+] Read debug directory and extended debug information [+] Calculate entropy [+] Change file alignment [+] Change base address [+] Work with DOS Stub and Rich overlay [+] High-level resource reading: bitmaps, icons, cursors, version info, string and message tables [+] High-level resource editing: bitmaps, icons, cursors, version info Library doesn't use WinAPI and doesn't execute PE files, so it's safe to use it with suspicious binaries. Via sachin
Scoop.it!

To save changes for file you are editing use :wq command in vim command mode (esc) Via linux tutorial
Scoop.it!
peda - PEDA - Python Exploit Development Assistance for GDB...
|