
|
Rescooped by
alexander knorr
from ITSecurity
September 19, 2012 6:08 PM
|


No comment yet.
Sign up to comment

 Your new post is loading...
 Scoop.it! No comment yet.
Sign up to comment
Scoop.it!
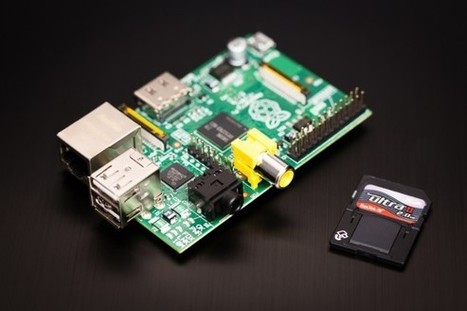
SlashGearRaspberry Pi squeezes 50% performance boost with turbo modeSlashGearRaspberry Pi has added a “turbo mode”, squeezing 50-percent more performance out of its fruity mini computer without dinging your warranty in the process. Via F. Thunus
Scoop.it!
This is the easiest way to add a Malware Domains Block List to Firefox or Chrome. (Requires AdBlock Plus Plugin/Extension) Via 0xerror
Scoop.it!
DNSChef is a highly configurable DNS proxy for Penetration Testers and Malware Analysts. A DNS proxy (aka "Fake DNS") is a tool used for application network traffic analysis among other uses. For example, a DNS proxy can be used to fake requests for "badguy.com" to point to a local machine for termination or interception instead of a real host somewhere on the Internet. Via 0xerror
Scoop.it!
The idea started as an attempt to implement "System Calls Hooking" from user-mode under Wow64 processes (32-bit processes running on 64-bit versions of Windows). Via sachin
Scoop.it!
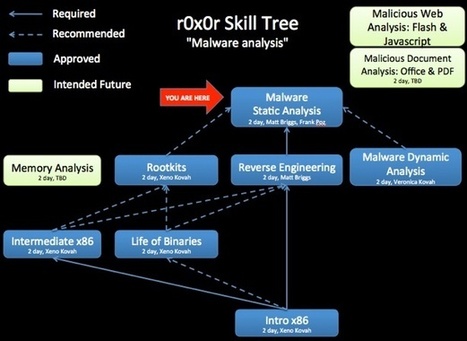
Author Comments: An email arrives in your inbox: "You have to check out this picture!" It came from your friends address, which you know and trust. It beckons you to open it. Maybe you weren't fooled this time, but it's likely at least one of the 50 other recipients couldn't resist. Via sachin
Scoop.it!
In today's Internet driven world, all of us use one or other applications starting from browsers, mail clients to instant messengers. Most of these applications store the sensitive information such as user name, password in their private location using proprietary methods. This prevents hassle of entering the credentials every time during the authentication.
Via sachin
Scoop.it!
Introduction Sometimes its necessary to locate changes within a running binary or module. This can be for the reasons of a malware modifying your code, or you want to understand how a certain bot/hack/crack is working with your process. In both cases this information can be very valuable to you. Via sachin
Scoop.it!
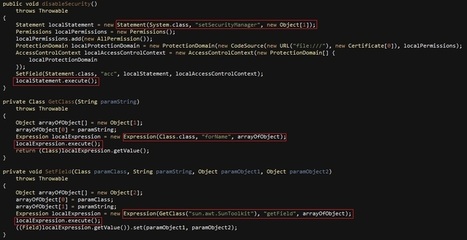
A new Java 0-day is running rampant around the internet this week. With a code paste Sunday night and a Metasploit module coming in early yesterday morning, along with myriad research and blog posts, this Java vuln is sure to be the topic of the week. Based on information in the pastie link and the usage of the Gondzz and Gondvv class files in the alienvault blog post, plus analysis we've done on the samples we've seen in the wild, we've deduced that the exploit runs as follows: Via sachin
Scoop.it!
Author Says, During the last couple of weeks I’ve come across three malware samples packed using compiled AutoIt scripts, so I decided to explore the connection between AutoIt and the malware world. I took the latest 50 samples marked as AutoIt that were submitted to the free scanning site VirusTotal. Via sachin
Scoop.it!
Over the last few months there has been a large increase of buffer overflow vulnerabilities being both discovered and exploited. Examples of these are syslog, splitvt, sendmail 8.7.5, Linux/FreeBSD mount, Xt library, at, etc. This paper attempts to explain what buffer overflows are, and how their exploits work. Via sachin
Scoop.it!

this page gathers the initial values of x86 registers, under Windows: general registers, at specific execution pointsspecial registers Note: some values may change slightly, depending on your exact configuration and settings. Via sachin
|
Scoop.it!
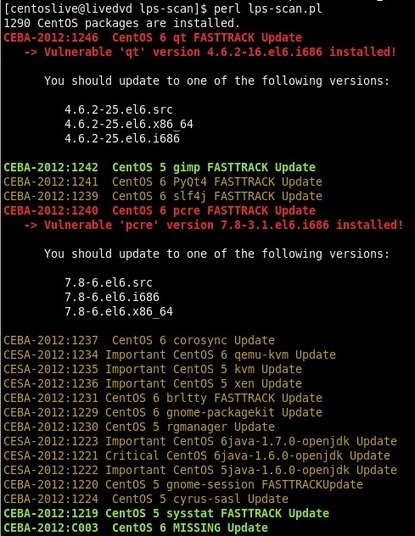
How do you know wether your Linux server (which has no desktop update notifier or unattended security updates running) does need to be updated? ... Via cheron guillaume
Scoop.it!

When a new Dell Chassis hardware infrastructure is installed, a web interface is also present to help with management of the Chassis. Each blade has its own web interface that gets installed by default on 443 (HTTPS). Via sachin
Scoop.it!
Applications of Google spreadsheet functions for external data are virtually endless, and my previous article on how =IMPORTXML() can help to automate the process of collecting web data is just an example. Since fantasy has no limits, I want to show that another possibility is to build… a proxy. Yes, a proxy inside Google preadsheet. Via sachin
Scoop.it!
Nexpose is able to use the hashes to perform credentialed scans to produce very detailed scan results of all sorts of local and remote vulnerabilities that may otherwise not be detectable. ... Via sachin
Scoop.it!
Quttera investigation engine statistics of the windows/upexec/find_tag shellcode encoded by x86/shikata_ga_nai encoder Via sachin
Scoop.it!
Joe Document Dissector is an automated malware analysis platform for detecting malicious documents... Via sachin
Scoop.it!

A French #hacker has released a tool capable of sending SMSes with #spoofed sender details on the #iPhone 4. Via sachin
Scoop.it!
Watching Egypt ’s talk at DEFCON 20 he mentioned the ability to jump on on a system when pag... Via sachin
Scoop.it!
A security identifier (SID) is a unique value of variable length that is used to identify a security principal or security group in Windows operating systems. Well-known SIDs are a group of SIDs that identify generic users or generic groups. Via sachin
Scoop.it!

Current version: 0.1.1 Summary [+] Read 32- and 64-bit PE files (PE, PE+) for Windows, work similar with both formats [+] Rebuild 32- and 64-bit PE files [+] Work with directories and headers [+] Convert addresses [+] Read and write PE sections [+] Read and write imports [+] Read and write exports [+] Read and write relocations [+] Read and write resources [+] Read and write TLS [+] Read and write image config [+] Read and write basic .NET information [+] Read bound imports [+] Read exception directory (PE+ only) [+] Read debug directory and extended debug information [+] Calculate entropy [+] Change file alignment [+] Change base address [+] Work with DOS Stub and Rich overlay [+] High-level resource reading: bitmaps, icons, cursors, version info, string and message tables [+] High-level resource editing: bitmaps, icons, cursors, version info Library doesn't use WinAPI and doesn't execute PE files, so it's safe to use it with suspicious binaries. Via sachin
|