Recent supply chain attacks have made one point clear: the attacker is no longer trying only to exploit a vulnerable application at runtime. They are increasingly targeting the systems that create, sign, test, distribute, and update software.


|
Scooped by
JC Gaillard
onto Cybersecurity Leadership October 1, 12:54 AM
|
 Scoop.it!
Recent supply chain attacks have made one point clear: the attacker is no longer trying only to exploit a vulnerable application at runtime. They are increasingly targeting the systems that create, sign, test, distribute, and update software.

 Your new post is loading...
Scoop.it!

AI hype distracts from foundational identity security risks and controls
Scoop.it!

Cyber insurers are tightening requirements, monitoring risk, and offering security services as threats evolve.
Scoop.it!
Many organizations think they’re completely ready for a cyberattack. They’ve got binders full of protocols, complex software stacks, and a general sense of security. But when a real crisis hits, these carefully crafted plans often fall apart. Why does this happen so consistently?
Scoop.it!

As with technical debt, quantum debt accumulates gradually without raising many alarms initially.
Scoop.it!

From
medium

Focusing exclusively on the evolving threat landscape risks missing the more fundamental problems that continue to undermine cybersecurity effectiveness across large organisations.
Scoop.it!
We keep buying better security tech, but the real gaps are ownership and follow-through, so cybersecurity can’t stay the CISO’s problem alone.
Scoop.it!
From
www
Directors don't need to understand how quantum computers work. They just need to know which business services and data could be exposed, how long the organization will need to reduce that risk, what the migration will cost and what should be funded first.
Scoop.it!
As the CISO’s remit grows, blending business risk management alongside its traditional technical roots, some are questioning whether it’s time to rethink the role as one business risk executive and a second focused on technical controls.
Scoop.it!
Cyber budgets are rising as AI accelerates attacks, but weak data controls and continuity plans leave organizations exposed. Security leaders say CIOs should resist
Scoop.it!
Rapidly emerging risks and the need for business agility have many CISOs forgoing fixed, multi-year plans in favor of a tiered approach that includes continual revisiting of key strategic priorities.
Scoop.it!
Cisco surveyed 8,000 security professionals in 30 markets about how well their organizations defend against AI-era threats, and only 8% landed in the top group.
Scoop.it!
The prospect of legal accountability is unclear. Lawsuits are a possibility, but some legal experts believe any criminal investigations would face an extremely high burden.
Scoop.it!
AI is becoming the biggest destination for new security dollars, but spending remains uneven and strongest among organizations with mature AI governance.
|
Scoop.it!

After years of asking whether organizations are spending enough on cybersecurity, perhaps executives and boards should start asking a more difficult question: Are we actually managing cybersecurity as the genuine business protection capability it has become?
Scoop.it!
Attackers move at machine speed, while defenders move at organizational speed. The next cybersecurity failure may come down to who patches first.
Scoop.it!

A new IANS report has found that despite the growth of the head of AI security role, accountability for AI governance in firms remains unsettled
Scoop.it!
Cybersecurity job postings hit a four-year low in 2026 as compliance roles gain share and CISO hiring swings, new CyberSN data shows.
Scoop.it!
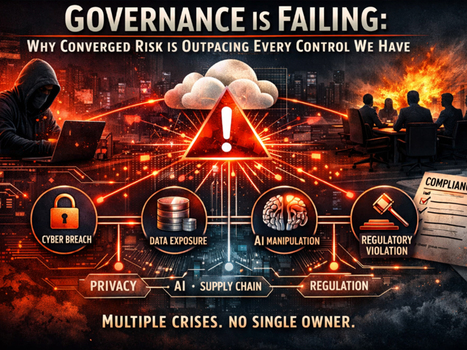
Modern risk doesn’t stay contained—it converges, and failures cascade. Identity, cloud, data, and AI failures don’t occur in isolation, yet governance models still treat them that way.
Scoop.it!

From escalating AI-enabled threats to persistent skills gaps, security leaders are reshaping their agendas to address several key long-standing and emerging concerns.
Scoop.it!
The growth of cyber insurance is a positive development, but law firms still need the fundamentals.
Scoop.it!
The work CISOs are doing to prep for the arrival of quantum computing echoes the race to update computers for Y2K — with one significant difference. They may need to prove, in the here and now, that they will be ready for the expected sea change in cybersecurity.
Scoop.it!

PwC’s survey found that only 22% of leaders would use fully autonomous AI for cyber defense, while just 21% are implementing quantum-resistant security measures.
Scoop.it!
Recent supply chain attacks have made one point clear: the attacker is no longer trying only to exploit a vulnerable application at runtime. They are increasingly targeting the systems that create, sign, test, distribute, and update software.
Scoop.it!
McKinsey report says cybersecurity isn't just one technology trend among 14; it is the connective tissue and constraint running through all of them.
Scoop.it!

Cyber insurers are facing a turbulent time as agentic AI poses new challenges and threats, as City AM understands that underwriters and insurers are considering pulling back.
|