The growth of cyber insurance is a positive development, but law firms still need the fundamentals.

 Your new post is loading...
 Scoop.it! The growth of cyber insurance is a positive development, but law firms still need the fundamentals. 
No comment yet.
Sign up to comment
Scoop.it!
The work CISOs are doing to prep for the arrival of quantum computing echoes the race to update computers for Y2K — with one significant difference. They may need to prove, in the here and now, that they will be ready for the expected sea change in cybersecurity.
Scoop.it!

PwC’s survey found that only 22% of leaders would use fully autonomous AI for cyber defense, while just 21% are implementing quantum-resistant security measures.
Scoop.it!
Recent supply chain attacks have made one point clear: the attacker is no longer trying only to exploit a vulnerable application at runtime. They are increasingly targeting the systems that create, sign, test, distribute, and update software.
Scoop.it!
McKinsey report says cybersecurity isn't just one technology trend among 14; it is the connective tissue and constraint running through all of them.
Scoop.it!

Cyber insurers are facing a turbulent time as agentic AI poses new challenges and threats, as City AM understands that underwriters and insurers are considering pulling back.
Scoop.it!
Investment alone is an increasingly poor proxy for resilience, and the more important question is becoming, "How quickly can we understand what is happening and act?"

Natalia Barbosa's curator insight,
September 28, 4:44 PM
TRANSFORMACIÓN DE LA IA CAMBIO EN LA EDUCACIÓN
Scoop.it!
Attackers now move at machine speed, but organizations make decisions at committee speed. To close the gap, businesses need a different operating model and committed executive leadership.
Scoop.it!
CISO AI security risks intensify as organizations balance growing GenAI use with data protection, governance and limited resources.
Scoop.it!
As incidents of unintended harm caused by AI agents mount, CISOs and insurance firms are charting a path on how to handle the fallout.
Scoop.it!
From
www

Baseline measures like formal AI governance, stronger oversight on AI agents, and monitoring for shadow AI can help, yet many companies haven’t yet taken these steps.
Scoop.it!

Why organizations need a business leader — not another technical executive — to connect security with strategy.
Scoop.it!

From
www
What a board needs is broad operating and governance judgment combined with enough technology-transformation experience to test management's assumptions independently.
|
Scoop.it!
As the CISO’s remit grows, blending business risk management alongside its traditional technical roots, some are questioning whether it’s time to rethink the role as one business risk executive and a second focused on technical controls.
Scoop.it!
Cyber budgets are rising as AI accelerates attacks, but weak data controls and continuity plans leave organizations exposed. Security leaders say CIOs should resist
Scoop.it!
Rapidly emerging risks and the need for business agility have many CISOs forgoing fixed, multi-year plans in favor of a tiered approach that includes continual revisiting of key strategic priorities.
Scoop.it!
Cisco surveyed 8,000 security professionals in 30 markets about how well their organizations defend against AI-era threats, and only 8% landed in the top group.
Scoop.it!
The prospect of legal accountability is unclear. Lawsuits are a possibility, but some legal experts believe any criminal investigations would face an extremely high burden.
Scoop.it!
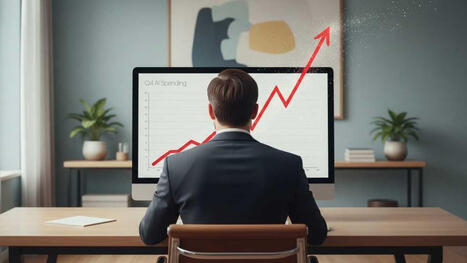
AI is becoming the biggest destination for new security dollars, but spending remains uneven and strongest among organizations with mature AI governance.
Scoop.it!
IT leaders remain confident in their cybersecurity posture after a breach, even as fear of blame affects how incidents are handled.
Scoop.it!

CISOs are rethinking cyber hygiene and implementing guardrails to prevent over-privileged AI agents from causing unintended harm.
Scoop.it!
No strangers to stress, security execs recognize cutting-edge AI capabilities as a harbinger of challenges that will make the top cyber role untenable unless liability, authority, and alignment issues are quickly addressed.
Scoop.it!
Security execs who feel prepared to face what’s coming hold several organizational factors in common, according to a recent report. But confidence and preparedness aren’t necessarily the true measures of security.
Scoop.it!
Technical debt, cybersecurity skills shortages and identity risks are among the challenges that can make it difficult for an organization to achieve cyber resilience.
Scoop.it!

Arctic Wolf's 2026 survey exposes the cybersecurity confidence gap: 96% of leaders feel ready, yet nearly 70% were breached and their response stays untested.
|