 Your new post is loading...
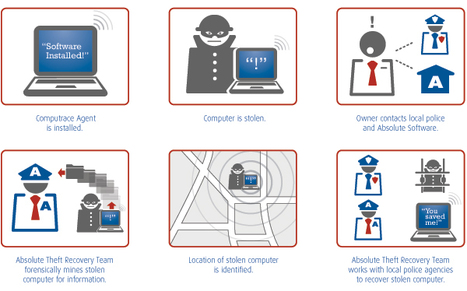
Et si je vous disais qu'il y a dans votre ordinateur un mouchard que vous ne pouvez pas enlever, qui a été mis en place par le constructeur, qui est sur les listes blanches de la plupart des antivirus et dont vous n'avez jamais entendu parler ? La société Kaspersky, spécialisée dans la détection et …
Via Frederic GOUTH

|
Scooped by
Gust MEES
May 12, 2014 7:56 AM
|
A hacker has found a way to bypass the iPhone 5 lock screen to get at your contacts. Ironically, he got in by asking Siri, Apple's voice-activated "helper."
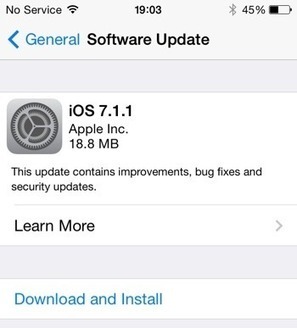
The iPhone's lock screen is the easiest way to protect your phone from prying eyes in the event that it is lost or stolen - but activating Siri from the lock screen is like having no protection at all. Siri caused other lock screen problems that needed fixing - it seems like déjà vu all over again - where holding down the home button allowed you to just ask nicely for your phone to bypass its own security. The bug affects devices running iOS 7.1.1 - the latest Apple release.
Here's how to close the hole while...
Learn more:
- http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
|
|
Scooped by
Gust MEES
April 26, 2014 9:54 AM
|
Les utilisateurs d'iOS sont restés exposés pendant trois semaines à des problèmes de sécurité connus, précédemment patchés dans Safari pour Mac OS X, selon une ancienne collaboratrice d'Apple.
En savoir plus :
Apple patches a number of bugs in the iOS platform, and takes a second stab at fixing the Touch ID fingerprint recognition "fade" reported by some iPhone 5S users.
Learn more:
|
|
Scooped by
Gust MEES
April 3, 2014 11:48 AM
|
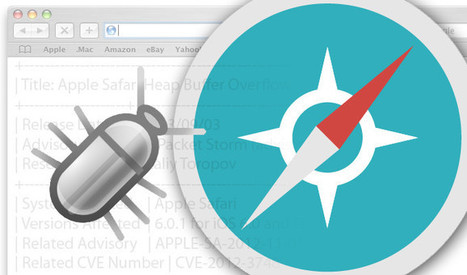
Apple has fixed more than 25 security flaws in its Safari browser.
That flaw was fixed in iOS and other products earlier this year but Apple just released the fix for Safari on Monday. Along with the 25 memory corruption vulnerabilities the company fixed, it also pushed out a patch for a separate issue in Safari that could enable an attacker to read arbitrary files on a user’s machine.
=========> UPDATE ASAP!!! <========
|
|
Scooped by
Gust MEES
March 11, 2014 11:37 AM
|
Apple iOS 7.1 fixes more than 20 code execution flaws on the iPhone.
Apple has fixed a slew of vulnerabilities that could lead to code execution on the iPhone, along with a number of other security vulnerabilities in the latest version of its mobile operating system, iOS 7.1. The new release comes just a little more than two weeks after Apple released iOS 7.06 to fix the SSL certificate validation error.
|
|
Scooped by
Gust MEES
February 28, 2014 10:57 AM
|
If Apple carries on with its many programming misdeeds, it will soon see a breakdown in its shiny, new security
|
|
Scooped by
Gust MEES
February 27, 2014 9:33 AM
|
Researchers at FireEye have developed a POC that exploits an Apple vulnerability to implement a Background Monitoring on Non-Jailbroken iOS 7 Devices
|
|
Scooped by
Gust MEES
February 26, 2014 8:01 AM
|
Apple est finalement parvenu à corriger la faille de sécurité majeure qui a touché ses systèmes d'exploitation
Mac. Un correctif qui intervient tardivement par rapport à iOS.
|
|
Scooped by
Gust MEES
February 24, 2014 12:07 PM
|
Apple's Mail, FaceTime, Calendar, Safari browser and Software Update could be vulnerable, a researcher said.
|
|
Scooped by
Gust MEES
February 24, 2014 11:00 AM
|
Besitzer eines iPhones, iPads oder eines iPod Touch sollten sofort ein wichtiges Sicherheits-Update installieren. Ihre verschlüsselten Verbindungen können gehackt werden. Für MacOS-Nutzer gibt es noch keinen Patch.
|
|
Scooped by
Gust MEES
February 22, 2014 2:50 PM
|
Apple has quietly pushed out a security update to iOS, the operating system used by its flagship iPhone and iPad products.
And it's really important for your privacy that you update your iPhones and iPads as quickly as possible.
===> A shame then that Mac OS X doesn't yet have a patch... <===
|
|
Scooped by
Gust MEES
February 21, 2014 8:27 PM
|
The tech giant fixes a security problem in iOS that affected encrypted connections. Apple on Friday released the latest update of its mobile operating system. It's of note because it fixes an SSL connection issue, an important encryption vulnerability.
SSL, or Secure Sockets Layer, is one of the most basic forms of encrypting Internet traffic. Without it, almost anybody can see what you're doing online. According to Apple's fulldescription of the update, the software previously had problems validating the authenticity of the connection, and the software fix restores steps that were missing in the validation process.
|
|
|
Scooped by
Gust MEES
May 22, 2014 7:46 AM
|
Apple distribue ce soir, via le Mac App Store, Safari 7.0.4, une mise à jour de sécurité pour son navigateur maison. Celle-ci intervient six semaines après la précédente mise à jour, Safari 7.0.3, une mise à jour là aussi à vocation sécuritaire. Les correctifs portent sur (...)
En savoir plus :
- http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
|
|
Scooped by
Gust MEES
April 29, 2014 3:07 PM
|
|
|
Scooped by
Gust MEES
April 24, 2014 6:03 PM
|
In the last couple of days, Apple has issued critical security patches for iOS, Mac OS X, the Apple Airport Base Station, and even the innocuous hockey puck-shaped Apple TV. And I trust, as a regul...
A malicious hacker could have taken one of these patched OS X vulnerabilities, and weaponised it for exploitation in a zero-day attack against iPhone and iPad users. . Every time Apple treats its smartphone and tablet customers as poor relations when it comes to security, they are putting millions of users at risk.
Learn more:
|
|
Scooped by
Gust MEES
April 10, 2014 8:36 AM
|
In the last couple of days you cannot fail to have seen the huge number of media articles about the so-called Heartbleed bug. In this article, we'll try and answer some of the common questions that...
Am I at risk if I use a Mac? What about an iPhone or iPad? Unfortunately this bug doesn’t care what kind of device you are using to communicate via the Internet. This means that iPhones, iPads and Macs are just as much at risk as, say, a computer running Windows 8.1. Learn more:
|
|
Scooped by
Gust MEES
March 20, 2014 6:40 AM
|
Title available since November raises questions about App Store vetting process.
Apple has never described exactly what its process is for ensuring the titles in its App Store are safe.
Although the comparatively fewer reports of rogue apps for iOS suggest that the review process is more stringent than Google's, the report ticket from Tor's high-ranking members suggests that Apple may not be doing everything it can or should do to protect iPhone and iPad users.
|
|
Scooped by
Gust MEES
March 4, 2014 4:45 PM
|
Mac malware in 2013 [PDF]
|
|
Rescooped by
Gust MEES
from 21st Century Learning and Teaching
February 28, 2014 7:50 AM
|
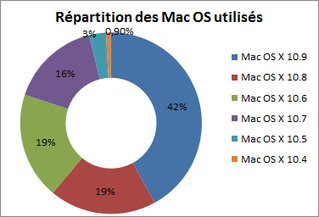
Apple a définitivement abandonné la sécurité de son Mac OS X 10.6, pourtant encore largement utilisé.
|
|
Scooped by
Gust MEES
February 27, 2014 7:55 AM
|
Apple has released an update for OS X that, among other things, patches the infamous "gotofail" bug whose existence was publicly revealed last Friday.
The flaw was initially patched on iOS and Apple TV with updates pushed out on that same day, but OS X users were left to wonder why a fix hasn't been provided for them as well.
|
|
Scooped by
Gust MEES
February 25, 2014 2:53 PM
|
Apple has just issued OS X Mavericks version 10.9.2, fixing the same serious SSL security hole that they patched for iPhone and iPad users at the end of last week.
|
|
Scooped by
Gust MEES
February 24, 2014 11:27 AM
|
[UPDATE] It says something about Apple's priorities that they fixed the iOS version of a very serious bug but left Mac users conspicuously vulnerable.
The SSL bug Apple patched on iOS on Friday is a shocking and embarrassing one. That it appears to have been in both iOS and OS X for some time and the way Apple is addressing it show both that Apple knows how serious it is and that Mac users play second fiddle in Apple's orchestra. Apple has only released a patch for iOS, not OS X.
Make no mistake about it, this is a very serious bug. The bug makes it fairly straightforward to intercept and decrypt SSL/TLS communications, probably the most important security protocol there is today.
Any time you see Apple (or really any major vendor) release an update that fixes a single bug, you can be sure it's a high-priority bug. And there's no reason to believe that it's higher-priority for iOS users than for Mac users.
So why did they not fix OS X at the same time? Because OS X isn't top priority anymore.
|
|
Scooped by
Gust MEES
February 24, 2014 9:16 AM
|
If it wasn't yet clear to Apple that its 'gotofail' security flaw has the undivided attention of the information security industry, one of its own recently departed star engineers just spelled out the severity of that bug in highly profane terms. "WHAT THE EVER LOVING F**K, APPLE??!?!!" wrote former Apple security [...]
Paget, a well-regarded researcher who left her position on Apple’s security team for a job at Tesla just earlier this month, wrote perhaps the most scathing critique yet of the company’s security response to its “gotofail” bug, which would allow a wide array of Apple programs’ SSL-encrypted communications to be hijacked, eavesdropped or corrupted. The vulnerability, which earned its nickname due to being caused by a single misplaced “goto” command in Apple’s code, was patched Friday for iOS.
But researchers quickly found that it affected Apple’s desktop OSX software as well, ===> and the company has yet to fix the desktop version of the bug. <===
|
|
Scooped by
Gust MEES
February 22, 2014 12:00 PM
|
Wer mit iPhone oder iPad vermeintlich verschlüsselte Nachrichten verschickt, könnte laut Apple zum Opfer von Hackern werden. Beheben soll das Problem ein Sicherheits-Update.
===> Doch Experten zufolge schützt es nicht alle Betroffenen. <===
|

















C'est très fort cela!!! :(((