


iStegSiri attack enables stealthy exfiltration of sensitive data from iOS devices
Learn more:
- http://www.scoop.it/t/securite-pc-et-internet/?tag=Steganography
- http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security

 Your new post is loading...
 Scoop.it! iStegSiri attack enables stealthy exfiltration of sensitive data from iOS devices Learn more: - http://www.scoop.it/t/securite-pc-et-internet/?tag=Steganography - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security 
No comment yet.
Sign up to comment
Scoop.it!
L'initiative Project Zero de Google se poursuit et ses chercheurs en sécurité ont ainsi dévoilé trois failles d'OS X jugées sévères. Apple a été informé de ces vulnérabilités trois mois plus tôt, mais n'a pas publié de correctifs. Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
Gust MEES's insight:
L'initiative Project Zero de Google se poursuit et ses chercheurs en sécurité ont ainsi dévoilé trois failles d'OS X jugées sévères. Apple a été informé de ces vulnérabilités trois mois plus tôt, mais n'a pas publié de correctifs. Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
Scoop.it!
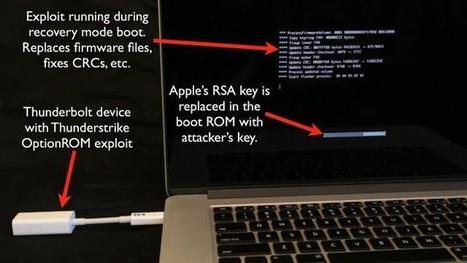
A security researcher has discovered a way to infect Macs with malware virtually undetectable, that 'can't be removed,' and which can be installed using a modified Apple gigabit Ethernet Thunderbolt adapter. Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
Gust MEES's insight:
A security researcher has discovered a way to infect Macs with malware virtually undetectable, that 'can't be removed,' and which can be installed using a modified Apple gigabit Ethernet Thunderbolt adapter. Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
Scoop.it!
The update fixes "critical security vulnerabilities" in OS X's network time protocol (NTP). Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
Gust MEES's insight:
The update fixes "critical security vulnerabilities" in OS X's network time protocol (NTP). Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
Scoop.it!
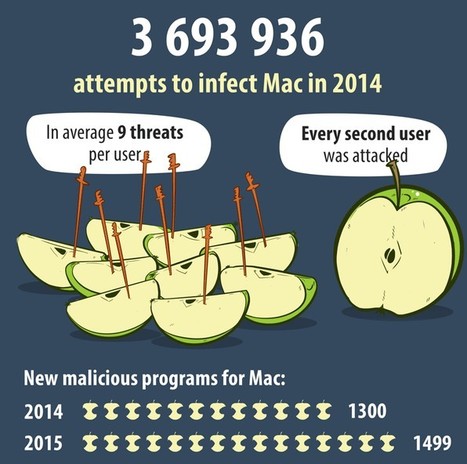
Im Jahr 2014 blockierten die Lösungen von Kaspersky Lab insgesamt 3.693.936 Infektionsversuche unter Mac OS X. Die Experten von Kaspersky Lab entdeckten 1.499 neue Schadprogramme für Mac OS X, das sind 200 Schädlinge weniger als im entsprechenden Vorjahreszeitraum. ===> Jeder zweite Anwender von Apple-Produkten war einem Angriff ausgesetzt. <=== Im Laufe des Jahres war jeder Mac-OS-X-User durchschnittlich neunmal mit einer Cyberbedrohung für sein Betriebssystem konfrontiert. Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
Gust MEES's insight:
Im Jahr 2014 blockierten die Lösungen von Kaspersky Lab insgesamt 3.693.936 Infektionsversuche unter Mac OS X. Die Experten von Kaspersky Lab entdeckten 1.499 neue Schadprogramme für Mac OS X, das sind 200 Schädlinge weniger als im entsprechenden Vorjahreszeitraum. ===> Jeder zweite Anwender von Apple-Produkten war einem Angriff ausgesetzt. <=== Im Laufe des Jahres war jeder Mac-OS-X-User durchschnittlich neunmal mit einer Cyberbedrohung für sein Betriebssystem konfrontiert. Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security

Gust MEES's curator insight,
December 10, 2014 1:26 PM
Im Jahr 2014 blockierten die Lösungen von Kaspersky Lab insgesamt 3.693.936 Infektionsversuche unter Mac OS X. Die Experten von Kaspersky Lab entdeckten 1.499 neue Schadprogramme für Mac OS X, das sind 200 Schädlinge weniger als im entsprechenden Vorjahreszeitraum. ===> Jeder zweite Anwender von Apple-Produkten war einem Angriff ausgesetzt. <=== Im Laufe des Jahres war jeder Mac-OS-X-User durchschnittlich neunmal mit einer Cyberbedrohung für sein Betriebssystem konfrontiert. Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
Scoop.it!
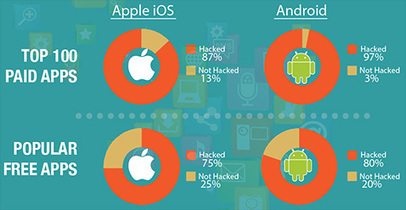
97% of the top 100 paid Android apps and 87% of the top 100 paid Apple iOS apps have been hacked, according to Arxan Technologies. Learn more: Via Gust MEES
Gust MEES's insight:
97% of the top 100 paid Android apps and 87% of the top 100 paid Apple iOS apps have been hacked, according to Arxan Technologies. Learn more:
Gust MEES's curator insight,
November 17, 2014 8:21 AM
97% of the top 100 paid Android apps and 87% of the top 100 paid Apple iOS apps have been hacked, according to Arxan Technologies. Learn more:
Gust MEES's curator insight,
November 17, 2014 8:26 AM
97% of the top 100 paid Android apps and 87% of the top 100 paid Apple iOS apps have been hacked, according to Arxan Technologies. Learn more:
Scoop.it!

Nach der vergleichsweise harmlosen WireLurker-Angriffsmethode sorgt inzwischen eine weitaus bedrohlichere iOS-Schwachstelle für Schlagzeilen. Die Angriffsart «Masque Attack» hat es dabei auf alle iPhone-Nutzer abgesehen, auch auf iPhones ohne Jailbreak. Die Cyberkriminellen seien sogar in der Lage, installierte iOS-Apps zu überschreiben. Fällt jemand auf die Masche rein, wird beispielsweise unbemerkt eine tägliche Anwendung wie Gmail überschreiben. So könnte z.B. eine E-Banking-App als Keylogger-Anwendung missbraucht werden, um Bankdaten von Nutzern auszuspionieren. Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
Gust MEES's insight:
Nach der vergleichsweise harmlosen WireLurker-Angriffsmethode sorgt inzwischen eine weitaus bedrohlichere iOS-Schwachstelle für Schlagzeilen. Die Angriffsart «Masque Attack» hat es dabei auf alle iPhone-Nutzer abgesehen, auch auf iPhones ohne Jailbreak. Die Cyberkriminellen seien sogar in der Lage, installierte iOS-Apps zu überschreiben. Fällt jemand auf die Masche rein, wird beispielsweise unbemerkt eine tägliche Anwendung wie Gmail überschreiben. So könnte z.B. eine E-Banking-App als Keylogger-Anwendung missbraucht werden, um Bankdaten von Nutzern auszuspionieren. Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
Scoop.it!
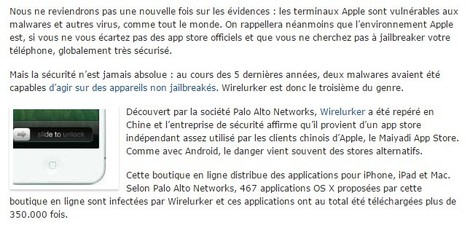
Pour l’instant, plus de peur que de mal Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security?q=wirelurker
Gust MEES's insight:
Pour l’instant, plus de peur que de mal Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security?q=wirelurker
Scoop.it!
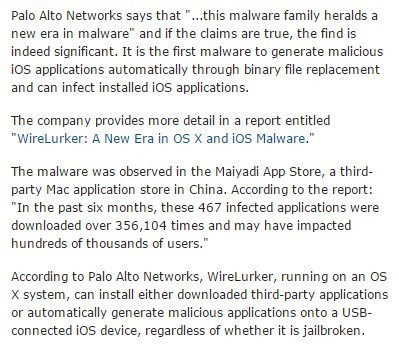
According to Palo Alto Networks, WireLurker, running on an OS X system, can install either downloaded third-party applications or automatically generate malicious applications onto a USB-connected iOS device, regardless of whether it is jailbroken. Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security?q=wirelurker
Gust MEES's insight:
According to Palo Alto Networks, WireLurker, running on an OS X system, can install either downloaded third-party applications or automatically generate malicious applications onto a USB-connected iOS device, regardless of whether it is jailbroken. Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security?q=wirelurker
Scoop.it!
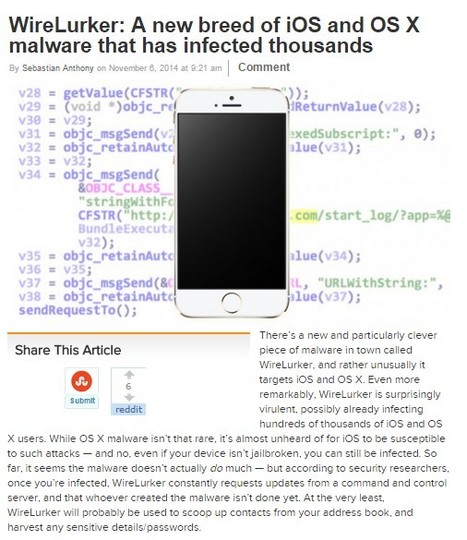
In short, the initial WireLurker infection comes from a third-party Mac OS X app store (in this case, the Chinese Maiyadi app store). Once you download and install an infected app onto your OS X machine, that’s where the fun begins. If you then plug an iOS device into an infected OS X machine, WireLurker installs itself on the iOS device. By using iOS’s enterprise provisioning system — a method usually reserved for companies to side-load apps directly onto corporate iOS devices — WireLurker can even infect non-jailbroken devices. Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security?q=wirelurker
Gust MEES's insight:
In short, the initial WireLurker infection comes from a third-party Mac OS X app store (in this case, the Chinese Maiyadi app store). Once you download and install an infected app onto your OS X machine, that’s where the fun begins. If you then plug an iOS device into an infected OS X machine, WireLurker installs itself on the iOS device. By using iOS’s enterprise provisioning system — a method usually reserved for companies to side-load apps directly onto corporate iOS devices — WireLurker can even infect non-jailbroken devices. Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security?q=wirelurker
Scoop.it!

WireLurker monitors any iOS device connected via USB with an infected OS X computer and installs downloaded third-party applications or automatically generated malicious applications onto the device, regardless of whether it is jailbroken. This is the reason we call it “wire lurker”. Researchers have demonstrated similar methods to attack non-jailbroken devices before; however, this malware combines a number of techniques to successfully realize a new brand of threat to all iOS devices. Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security?q=wirelurker
Gust MEES's insight:
WireLurker monitors any iOS device connected via USB with an infected OS X computer and installs downloaded third-party applications or automatically generated malicious applications onto the device, regardless of whether it is jailbroken. This is the reason we call it “wire lurker”. Researchers have demonstrated similar methods to attack non-jailbroken devices before; however, this malware combines a number of techniques to successfully realize a new brand of threat to all iOS devices. Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security?q=wirelurker
Scoop.it!
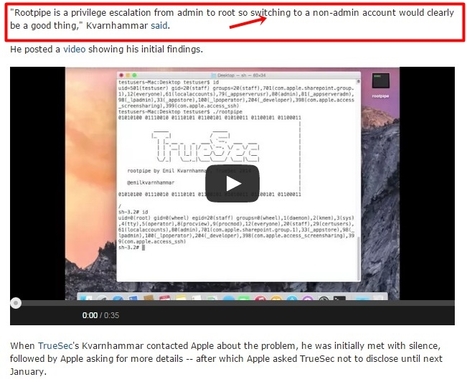
Details are finally emerging about a serious vulnerability in Apple's OS X Yosemite, called "Rootpipe" which allows root access by attackers. The privilege escalation vulnerability was discovered by Swedish hacker Emil Kvarnhammar, who has been asked by Apple to withhold details until January 2015 -- since Apple likely wouldn't allow details until they have a fix, this is probably when users can expect a patch. Rootpipe is a privilege escalation from admin to root so switching to a non-admin account would clearly be a good thing," Kvarnhammar said. Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
Gust MEES's insight:
Details are finally emerging about a serious vulnerability in Apple's OS X Yosemite, called "Rootpipe" which allows root access by attackers. The privilege escalation vulnerability was discovered by Swedish hacker Emil Kvarnhammar, who has been asked by Apple to withhold details until January 2015 -- since Apple likely wouldn't allow details until they have a fix, this is probably when users can expect a patch. Rootpipe is a privilege escalation from admin to root so switching to a non-admin account would clearly be a good thing," Kvarnhammar said. Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
Scoop.it!
SymantecTV : Are Mac Users safe from Malware? Not as much as you might think. Symantec's Security Expert Kevin Haley breaks down the Mac's invincibility myth. Learn why Malware authors are targeting unsuspecting Mac users and why you should be protected. Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
Gust MEES's insight:
SymantecTV : Are Mac Users safe from Malware? Not as much as you might think. Symantec's Security Expert Kevin Haley breaks down the Mac's invincibility myth. Learn why Malware authors are targeting unsuspecting Mac users and why you should be protected. Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
|
Scoop.it!
Google's security team has disclosed three separate zero-day vulnerabilities on Apple's OS X platform. It seems annoying Microsoft wasn't enough. Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
Gust MEES's insight:
Google's security team has disclosed three separate zero-day vulnerabilities on Apple's OS X platform. It seems annoying Microsoft wasn't enough. Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
Scoop.it!
A bug has been discovered in Apples OS X Spotlight, allowing valuable user information to be accessed by email phishers, spammers and hackers Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
Gust MEES's insight:
A bug has been discovered in Apples OS X Spotlight, allowing valuable user information to be accessed by email phishers, spammers and hackers Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
Scoop.it!
Apple apparently has patched a vulnerability that could be easily exploited by the iDict hacking tool released on New Years Day. Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
Gust MEES's insight:
Apple apparently has patched a vulnerability that could be easily exploited by the iDict hacking tool released on New Years Day. Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
Scoop.it!
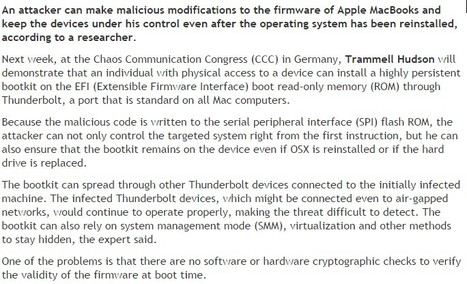
A bootkit can be written to the EFI boot ROM of Apple MacBook devices. The threat remains on the system even after the OS is reinstalled and the hard drive is replaced Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
Gust MEES's insight:
A bootkit can be written to the EFI boot ROM of Apple MacBook devices. The threat remains on the system even after the OS is reinstalled and the hard drive is replaced Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
Scoop.it!
Security update for Safari browser on Mac OS X removed from distribution after causing problems. No word from Apple yet on disposition. Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
Gust MEES's insight:
Security update for Safari browser on Mac OS X removed from distribution after causing problems. No word from Apple yet on disposition. Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
Scoop.it!
L’iPhone 5S a été mis à mal par une équipe de Corée du Sud, qui a réussi à profiter d'une combinaison de deux bugs dans Safari pour en prendre le contrôle. Le Samsung Galaxy S5 non plus n'a pas réisté aux assauts des hackers. Deux équipes ont profité de failles dans la gestion du protocole NFC pour en prendre le contrôle. le Nexus 5 a lui aussi été piraté via NFC, grâce à une technique étonnante, qui a consisté à forcer un appairage Bluetooth entre deux appareils.
Gust MEES's insight:
L’iPhone 5S a été mis à mal par une équipe de Corée du Sud, qui a réussi à profiter d'une combinaison de deux bugs dans Safari pour en prendre le contrôle. Le Samsung Galaxy S5 non plus n'a pas réisté aux assauts des hackers. Deux équipes ont profité de failles dans la gestion du protocole NFC pour en prendre le contrôle. le Nexus 5 a lui aussi été piraté via NFC, grâce à une technique étonnante, qui a consisté à forcer un appairage Bluetooth entre deux appareils.
Gust MEES's curator insight,
November 15, 2014 3:58 AM
L’iPhone 5S a été mis à mal par une équipe de Corée du Sud, qui a réussi à profiter d'une combinaison de deux bugs dans Safari pour en prendre le contrôle. Le Samsung Galaxy S5 non plus n'a pas réisté aux assauts des hackers. Deux équipes ont profité de failles dans la gestion du protocole NFC pour en prendre le contrôle. le Nexus 5 a lui aussi été piraté via NFC, grâce à une technique étonnante, qui a consisté à forcer un appairage Bluetooth entre deux appareils.
Scoop.it!
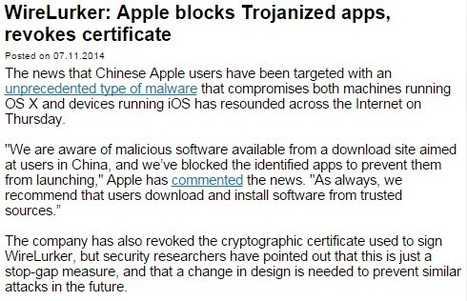
They also discovered malware samples uploaded to a public cloud storage service of Baidu by a user a month before the apps were made available on the Mayaidi app store, and they have reason to "suspect that Maiyadi has a close relationship with the creator of WireLurker." Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security?q=wirelurker
Gust MEES's insight:
They also discovered malware samples uploaded to a public cloud storage service of Baidu by a user a month before the apps were made available on the Mayaidi app store, and they have reason to "suspect that Maiyadi has a close relationship with the creator of WireLurker." Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security?q=wirelurker
Scoop.it!
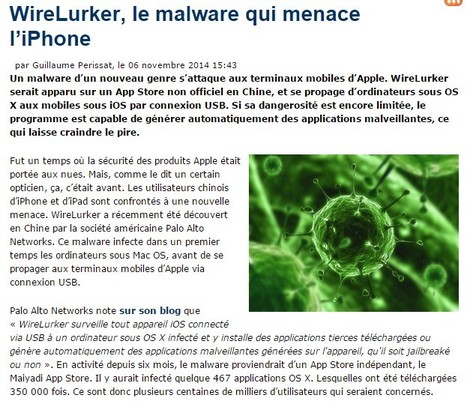
Une nouvelle génération de malwares Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security?q=wirelurker
Gust MEES's insight:
Une nouvelle génération de malwares Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security?q=wirelurker
Scoop.it!
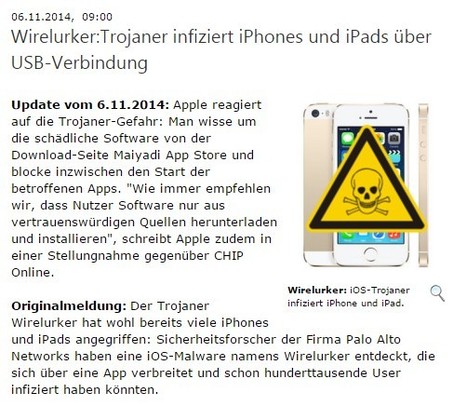
Originalmeldung: Der Trojaner Wirelurker hat wohl bereits viele iPhones und iPads angegriffen: Sicherheitsforscher der Firma Palo Alto Networks haben eine iOS-Malware namens Wirelurker entdeckt, die sich über eine App verbreitet und schon hunderttausende User infiziert haben könnten. Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security?q=wirelurker
Gust MEES's insight:
Originalmeldung: Der Trojaner Wirelurker hat wohl bereits viele iPhones und iPads angegriffen: Sicherheitsforscher der Firma Palo Alto Networks haben eine iOS-Malware namens Wirelurker entdeckt, die sich über eine App verbreitet und schon hunderttausende User infiziert haben könnten. Seinen Ursprung hat der Trojaner wohl in China, die Entdecker berichten, dass anfangs über 400 Apps im Maiyadi App Store, einem alternativen Appstore für OS X, infiziert wurden. Diese Anwendungen greifen dann die iPhones und iPads der Opfer an. Da die betroffenen Apps bislang über 350.000 Mal heruntergeladen wurden, ist die Zahl der theoretisch infizierten Apple-Geräte entsprechend groß. Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security?q=wirelurker
Scoop.it!
Des chercheurs en sécurité affirment avoir découvert une nouvelle famille de malwares, lesquels peuvent mettre à mal les appareils d'Apple. Afin d'éviter toute propagation de virus ou chevaux de Troie, Apple contrôle très strictement ses systèmes d'exploitation et plus précisément les applications publiées au sein de leurs plateformes de téléchargement respectives. Toutefois le cabinet Palo Alto Networks affirme avoir repéré une nouvelle attaque. Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security?q=wirelurker
Gust MEES's insight:
Des chercheurs en sécurité affirment avoir découvert une nouvelle famille de malwares, lesquels peuvent mettre à mal les appareils d'Apple. Afin d'éviter toute propagation de virus ou chevaux de Troie, Apple contrôle très strictement ses systèmes d'exploitation et plus précisément les applications publiées au sein de leurs plateformes de téléchargement respectives. Toutefois le cabinet Palo Alto Networks affirme avoir repéré une nouvelle attaque. Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security?q=wirelurker
Scoop.it!
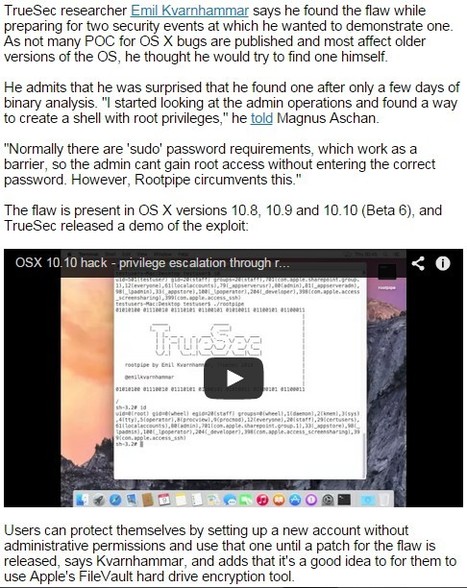
A Swedish researcher has unearthed a serious bug that affects the newest version of OS X - version 10.10, or Yosemite - and which could allow attackers to gain complete control of the target's Mac machine. Rootpipe is a privilege escalation from admin to root so switching to a non-admin account would clearly be a good thing," Kvarnhammar said. Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security?q=Rootpipe
Gust MEES's insight:
Rootpipe is a privilege escalation from admin to root so switching to a non-admin account would clearly be a good thing," Kvarnhammar said. Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security?q=Rootpipe
Scoop.it!

iWorm is a recently discovered OS X backdoor that affords an attacker complete control of an infected host. In this paper, Patrick Wardle builds upon the latest analyses, and provides a comprehensive technical analysis of iWorm's infection vector and persistence mechanism. Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
Gust MEES's insight:
iWorm is a recently discovered OS X backdoor that affords an attacker complete control of an infected host. In this paper, Patrick Wardle builds upon the latest analyses, and provides a comprehensive technical analysis of iWorm's infection vector and persistence mechanism. Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
|





Learn more:
- http://www.scoop.it/t/securite-pc-et-internet/?tag=Steganography
- http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security