


Durch eine Rechteausweitungslücke kann sich jeder Yosemite-Nutzer zum root erklären. Der Exploit ist so kurz, dass er in einen Tweet passt.
Mehr erfahren / Learn more:

 Your new post is loading...
 Scoop.it! Durch eine Rechteausweitungslücke kann sich jeder Yosemite-Nutzer zum root erklären. Der Exploit ist so kurz, dass er in einen Tweet passt. Mehr erfahren / Learn more: 
No comment yet.
Sign up to comment
Scoop.it!
Le Mac a-t-il un problème de sécurité ? On est en droit de se poser la question alors que les découvertes de failles se multiplient et qu'Apple n'y répond pas toujours promptement. Nous avons interrogé deux spécialistes. Vincent Bénony est le développeur de Hopper, un logiciel de rétro-ingénierie largement utilisé par les chercheurs de sécurité sur Mac (lire notre interview sur Hopper). Pedro Vilaça, alias fG!, est un chercheur qui analyse et met à mal la sécurité d'OS X (voir son blog). MacGeneration : Plusieurs failles de sécurité majeures ont été révélées au cours de ces derniers mois (rootpipe, Thunderstrike, XARA...). Avec toutes ces découvertes, on a l'impression que le Mac est plus vulnérable qu'avant. Est-ce seulement une impression ou est-ce bien le cas ? Vincent Bénony : Je pense surtout que l’information est beaucoup plus relayée qu’avant, et comme il y a de plus en plus de monde sur Mac, forcément, ça fait plus de bruit… Les systèmes sont développés en fonction des connaissances du moment, et il est difficile d’anticiper les problèmes. Plus un système sera utilisé, plus il aura de chances d’être étudié par des chercheurs, et plus ils remonteront des problèmes. En plus, il est difficile de mutualiser avec ce qui se fait pour Windows, car la philosophie des deux OS est très différente. L’architecture de Linux est plus proche de celle d’OS X, mais les pratiques des utilisateurs sont très différentes, et les problématiques de sécurité qui en découlent aussi.
Gust MEES's insight:
Le Mac a-t-il un problème de sécurité ? On est en droit de se poser la question alors que les découvertes de failles se multiplient et qu'Apple n'y répond pas toujours promptement. Nous avons interrogé deux spécialistes. Vincent Bénony est le développeur de Hopper, un logiciel de rétro-ingénierie largement utilisé par les chercheurs de sécurité sur Mac (lire notre interview sur Hopper). Pedro Vilaça, alias fG!, est un chercheur qui analyse et met à mal la sécurité d'OS X (voir son blog). MacGeneration : Plusieurs failles de sécurité majeures ont été révélées au cours de ces derniers mois (rootpipe, Thunderstrike, XARA...). Avec toutes ces découvertes, on a l'impression que le Mac est plus vulnérable qu'avant. Est-ce seulement une impression ou est-ce bien le cas ? Vincent Bénony : Je pense surtout que l’information est beaucoup plus relayée qu’avant, et comme il y a de plus en plus de monde sur Mac, forcément, ça fait plus de bruit… Les systèmes sont développés en fonction des connaissances du moment, et il est difficile d’anticiper les problèmes. Plus un système sera utilisé, plus il aura de chances d’être étudié par des chercheurs, et plus ils remonteront des problèmes. En plus, il est difficile de mutualiser avec ce qui se fait pour Windows, car la philosophie des deux OS est très différente. L’architecture de Linux est plus proche de celle d’OS X, mais les pratiques des utilisateurs sont très différentes, et les problématiques de sécurité qui en découlent aussi.
Scoop.it!
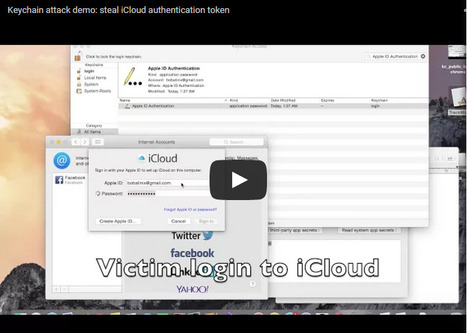
It’s become almost axiomatic that Apple devices and the apps on them are more secure than the competition. But researchers continue to blow up that notion and today a group of academics have ripped apart the securityprotections in Mac OS X and iOS to show it’s not only possible to create malware and get it onto the App Store, but it’s also feasible to launch “devastating” attacks using rogue software to steal the most sensitive personal data around, from iCloud passwords and Evernote notes to dodgy selfies and more. The attacks, known as unauthorized cross-app resource access or XARA, expose design flaws that allow a bad app to access critical pieces of data in other apps. As a result, Apple has struggled to fix the issues, according to apaper released today from Indiana University Bloomington, Peking University and the Georgia Institute of Technology. En savoir plus / Merhr erfahren / Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/?tag=XARA
Gust MEES's insight:
It’s become almost axiomatic that Apple devices and the apps on them are more secure than the competition. But researchers continue to blow up that notion and today a group of academics have ripped apart the securityprotections in Mac OS X and iOS to show it’s not only possible to create malware and get it onto the App Store, but it’s also feasible to launch “devastating” attacks using rogue software to steal the most sensitive personal data around, from iCloud passwords and Evernote notes to dodgy selfies and more. The attacks, known as unauthorized cross-app resource access or XARA, expose design flaws that allow a bad app to access critical pieces of data in other apps. As a result, Apple has struggled to fix the issues, according to apaper released today from Indiana University Bloomington, Peking University and the Georgia Institute of Technology. En savoir plus / Merhr erfahren / Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/?tag=XARA
Scoop.it!
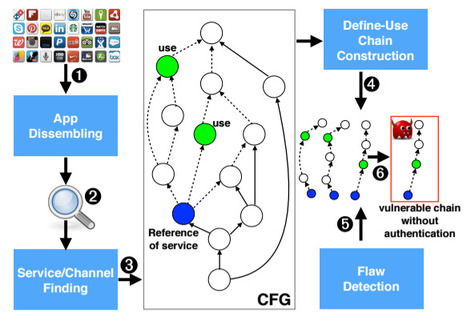
Des universitaires ont trouvé plusieurs vulnérabilités critiques touchant Mac OS X et iOS permettant le vol de données sensibles. Apple reste muet sur les correctifs. Une majorité des applications vulnérables à Xara Pour les universitaires, ces problèmes sont le résultat d’un manque d’authentification des discussions d’apps à apps ou d’apps avec l’OS. Pour découvrir ces faiblesses, ils ont mis au point un scanner capable d’analyser les binaires des applications pour Mac OS X et iOS pour trouver les protections manquantes. L’étude a porté sur 1612 applications pour Mac et 200 pour iOS avec comme résultat 88,6% des applications vulnérables à la menace Xara.
En savoir plus / Merhr erfahren / Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/?tag=XARA
Gust MEES's insight:
Des universitaires ont trouvé plusieurs vulnérabilités critiques touchant Mac OS X et iOS permettant le vol de données sensibles. Apple reste muet sur les correctifs. Une majorité des applications vulnérables à Xara Pour les universitaires, ces problèmes sont le résultat d’un manque d’authentification des discussions d’apps à apps ou d’apps avec l’OS. Pour découvrir ces faiblesses, ils ont mis au point un scanner capable d’analyser les binaires des applications pour Mac OS X et iOS pour trouver les protections manquantes. L’étude a porté sur 1612 applications pour Mac et 200 pour iOS avec comme résultat 88,6% des applications vulnérables à la menace Xara.
En savoir plus / Merhr erfahren / Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/?tag=XARA

Gust MEES's curator insight,
June 18, 2015 6:12 AM
Des universitaires ont trouvé plusieurs vulnérabilités critiques touchant Mac OS X et iOS permettant le vol de données sensibles. Apple reste muet sur les correctifs. Pour les universitaires, ces problèmes sont le résultat d’un manque d’authentification des discussions d’apps à apps ou d’apps avec l’OS. Pour découvrir ces faiblesses, ils ont mis au point un scanner capable d’analyser les binaires des applications pour Mac OS X et iOS pour trouver les protections manquantes. L’étude a porté sur 1612 applications pour Mac et 200 pour iOS avec comme résultat 88,6% des applications vulnérables à la menace Xara.
En savoir plus / Merhr erfahren / Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/?tag=XARA
Scoop.it!

"Après tout, la sécurité passe avant tout." Apple a revu son argumentaire marketing. Son slogan "Il est immunisé contre les virus", vantant les mérites de son ordinateur Mac, n'est plus. Et pour cause : les produits de la marque à la pomme sont désormais aussi sensibles aux attaques informatiques que leurs concurrents.
Gust MEES's insight:
Après tout, la sécurité passe avant tout." Apple a revu son argumentaire marketing. Son slogan "Il est immunisé contre les virus", vantant les mérites de son ordinateur Mac, n'est plus. Et pour cause : les produits de la marque à la pomme sont désormais aussi sensibles aux attaques informatiques que leurs concurrents.
Scoop.it!
Learn more: .
Gust MEES's insight:
Note that all the attack apps were successfully released by the Apple Stores. So, the security threats are indeed realistic." Learn more:
Scoop.it!
|Nach Angaben mehrerer Universitätsforscher sind das Sandboxing-System und die Schlüsselbundverwaltung von Apple nicht sicher. So soll es möglich sein, private Daten, Fotos und Passwörter zu klauen. Forschern mehrerer Universitäten ist es gelungen, Sicherheitsmechanismen in Apple-Produkten zu umgehen. Sie entdeckten mehrere Lücken, über die sie von einer manipulierten App auf andere Anwendungen zugreifen konnten. Eigentlich sollte dies nicht möglich sein. Nach ihren eigenen Aussagen informierten sie Apple über die Lücken. Der Hersteller, der im vergangenen Quartal 13,6 Milliarden Dollar Gewinn machte, forderte sie auf, mindestens sechs Monate zu warten, reagierte dann aber nicht mehr. Deswegen entschieden sie sich, ihre Erkenntnisse in einem Whitepaper (PDF) zu veröffentlichen. . Learn more: . .
Gust MEES's insight:
Nach Angaben mehrerer Universitätsforscher sind das Sandboxing-System und die Schlüsselbundverwaltung von Apple nicht sicher. So soll es möglich sein, private Daten, Fotos und Passwörter zu klauen. Forschern mehrerer Universitäten ist es gelungen, Sicherheitsmechanismen in Apple-Produkten zu umgehen. Sie entdeckten mehrere Lücken, über die sie von einer manipulierten App auf andere Anwendungen zugreifen konnten. Eigentlich sollte dies nicht möglich sein. Nach ihren eigenen Aussagen informierten sie Apple über die Lücken. Der Hersteller, der im vergangenen Quartal 13,6 Milliarden Dollar Gewinn machte, forderte sie auf, mindestens sechs Monate zu warten, reagierte dann aber nicht mehr. Deswegen entschieden sie sich, ihre Erkenntnisse in einem Whitepaper (PDF) zu veröffentlichen. . Learn more: . .
Scoop.it!
There is a vulnerability buried deep in the firmware of many Apple laptops that could allow an attacker to overwrite the machine’s BIOS and install a rootkit, gaining complete control of the Mac. Mehr erfahren/Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/?tag=EFI
Gust MEES's insight:
There is a vulnerability buried deep in the firmware of many Apple laptops that could allow an attacker to overwrite the machine’s BIOS and install a rootkit, gaining complete control of the Mac. Mehr erfahren/Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/?tag=EFI
Scoop.it!
Ein Sicherheitsexperte hat eine schwere Sicherheitslücke im Ruhemodus der Macs entdeckt. Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/?tag=EFI
Gust MEES's insight:
Ein Sicherheitsexperte hat eine schwere Sicherheitslücke im Ruhemodus der Macs entdeckt. Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/?tag=EFI
Scoop.it!
From
www

Das neue Sicherheitssystem "Rootless" soll einem Bericht zufolge den Zugriff auf bestimmte Dateien in iOS 9 sowie Mac OS X 10.11 verhindern – selbst für Nutzer mit Admin-Rechten.
Gust MEES's insight:
Das neue Sicherheitssystem "Rootless" soll einem Bericht zufolge den Zugriff auf bestimmte Dateien in iOS 9 sowie Mac OS X 10.11 verhindern – selbst für Nutzer mit Admin-Rechten. Mit iOS 9 und Mac OS X 10.11 führt Apple größere neue Sicherheitsfunktionen ein, wie 9to5Mac unter Berufung auf informierte Kreise berichtet: Das auf Kernel-Ebene angelegte Schutzsystem "Rootless" solle künftig den Zugriff auf bestimmte geschützte Dateien generell verhindern – auch für Nutzer mit den Rechten eines Administrators. Die Funktion sei unter anderem als zusätzlicher Schutz vor Malware gedacht, sie bedeute aber auch einen "schweren Schlag" gegen die Jailbreak-Community, heißt es dort. In Mac OS X lässt sich diese Rootless-Funktion möglicherweise deaktivieren, merkt 9to5Mac an – auch der gewohnte Zugriff auf das Dateisystem über den Finder soll weiterhin möglich sein.
Scoop.it!
A security firm has discovered a vulnerability in Apple’s Safari Browser that allows attackers to spoof legitimate websites and phish for user credentials. Users are encouraged to watch out for spoofing attacks that redirect them to phishing schemes. To learn more about how to spot a phish, please click here.
Gust MEES's insight:
A security firm has discovered a vulnerability in Apple’s Safari Browser that allows attackers to spoof legitimate websites and phish for user credentials. Users are encouraged to watch out for spoofing attacks that redirect them to phishing schemes. To learn more about how to spot a phish, please click here.
Scoop.it!
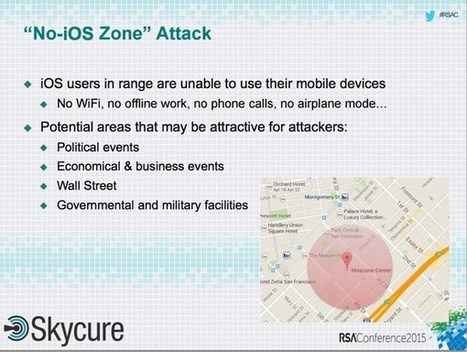
"No iOS Zone" denial-of-service vulnerability could lead to your iPhone or iPad constantly crashing. The researchers say that they first informed Apple of the problem in early October 2014, and that iOS 8.3 appears to resolve some of the issues they uncovered. Chances are that this won’t be the last time that a serious denial of service flaw is found in iOS. Just last month, Apple released iOS 8.2 which fixed a flaw that allowed hackers to restart iPhones by sending them a maliciously-crafted Flash SMS. More details of the “No iOS Zone” flaw can be found in the slide deck of the presentation given at the RSA conference.
Gust MEES's insight:
No iOS Zone" denial-of-service vulnerability could lead to your iPhone or iPad constantly crashing. The researchers say that they first informed Apple of the problem in early October 2014, and that iOS 8.3 appears to resolve some of the issues they uncovered. Chances are that this won’t be the last time that a serious denial of service flaw is found in iOS. Just last month, Apple released iOS 8.2 which fixed a flaw that allowed hackers to restart iPhones by sending them a maliciously-crafted Flash SMS. More details of the “No iOS Zone” flaw can be found in the slide deck of the presentation given at the RSA conference.
Gust MEES's curator insight,
April 27, 2015 12:51 PM
No iOS Zone" denial-of-service vulnerability could lead to your iPhone or iPad constantly crashing. The researchers say that they first informed Apple of the problem in early October 2014, and that iOS 8.3 appears to resolve some of the issues they uncovered. Chances are that this won’t be the last time that a serious denial of service flaw is found in iOS. Just last month, Apple released iOS 8.2 which fixed a flaw that allowed hackers to restart iPhones by sending them a maliciously-crafted Flash SMS. More details of the “No iOS Zone” flaw can be found in the slide deck of the presentation given at the RSA conference.
Scoop.it!
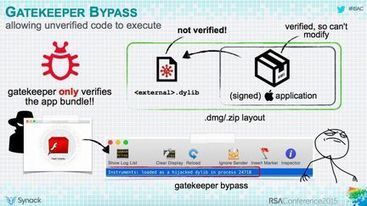
Le mythe vient de s'effondrer : un chercheur en sécurité vient de démontrer combien il était facile de contourner les mécanismes de sécurité mis en place par Apple dans OS X pour polluer le système avec des malwares. Finalement, Apple ne fait pas mieux que les autres fabricants ni même éditeurs de solutions de protection, puisque la conférence a démontré que la plupart des outils de protection pouvaient être contournés. Apple reste toutefois moins sujet aux attaques pour l'instant, mais les choses pourraient changer à l'avenir. En savoir plus / Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
Gust MEES's insight:
Le mythe vient de s'effondrer : un chercheur en sécurité vient de démontrer combien il était facile de contourner les mécanismes de sécurité mis en place par Apple dans OS X pour polluer le système avec des malwares. Finalement, Apple ne fait pas mieux que les autres fabricants ni même éditeurs de solutions de protection, puisque la conférence a démontré que la plupart des outils de protection pouvaient être contournés. Apple reste toutefois moins sujet aux attaques pour l'instant, mais les choses pourraient changer à l'avenir. En savoir plus / Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
Gust MEES's curator insight,
April 27, 2015 8:30 AM
Le mythe vient de s'effondrer : un chercheur en sécurité vient de démontrer combien il était facile de contourner les mécanismes de sécurité mis en place par Apple dans OS X pour polluer le système avec des malwares. Finalement, Apple ne fait pas mieux que les autres fabricants ni même éditeurs de solutions de protection, puisque la conférence a démontré que la plupart des outils de protection pouvaient être contournés. Apple reste toutefois moins sujet aux attaques pour l'instant, mais les choses pourraient changer à l'avenir. En savoir plus / Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security |
Scoop.it!

Well, knowing your name and how long you’ve been a card member seems only mildly invasive compared to what Apple may be up to. As you know, Apple’s Tim Cook has been vigorous in defending users’ right to privacy. As the world’s biggest luxury brand, Apple has an advantage over companies like Google that rely on turning their customers into products. However, with the companies’ forays into new advertising-based ventures like streaming music, that ethic may be harder to enforce. And a new patent application aligned with the Apple Pay product suggests a dramatic new leap into users personal space. Learn more:
Gust MEES's insight:
Well, knowing your name and how long you’ve been a card member seems only mildly invasive compared to what Apple may be up to. As you know, Apple’s Tim Cook has been vigorous in defending users’ right to privacy. As the world’s biggest luxury brand, Apple has an advantage over companies like Google that rely on turning their customers into products. However, with the companies’ forays into new advertising-based ventures like streaming music, that ethic may be harder to enforce. And a new patent application aligned with the Apple Pay product suggests a dramatic new leap into users personal space. Learn more:
Scoop.it!
Researchers at BAE just reported on a Mac bot known as OSX/Agent-ANTU that was allegedly distributed in a novel way. Here are some examples we've seen over the years where the Windows malware "playbook" has been followed, in some cases extremely effectively, on OS X: 2012: Java-based exploit. The Flashback malware was injected onto your Mac via an unpatched Java bug. Flashback was a bot, or zombie, meaning that crooks could remotely send it instructions to help them commit further cybercrime. Estimates suggest that more than 600,000 Macs ended up infected, supposedly including "274 from Cupertino." 2013: Word-based exploit. SophosLabs reported on attackers using an exploitable bug in Microsoft Word for Mac to target Chinese minority groups. If you opened a booby-trapped document, disguised as some sort of political commentary, the crooks got control of your Mac via zombie malware called OSX/Agent-AADL.
Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
Gust MEES's insight:
Researchers at BAE just reported on a Mac bot known as OSX/Agent-ANTU that was allegedly distributed in a novel way. Here are some examples we've seen over the years where the Windows malware "playbook" has been followed, in some cases extremely effectively, on OS X: 2012: Java-based exploit. The Flashback malware was injected onto your Mac via an unpatched Java bug. Flashback was a bot, or zombie, meaning that crooks could remotely send it instructions to help them commit further cybercrime. Estimates suggest that more than 600,000 Macs ended up infected, supposedly including "274 from Cupertino." 2013: Word-based exploit. SophosLabs reported on attackers using an exploitable bug in Microsoft Word for Mac to target Chinese minority groups. If you opened a booby-trapped document, disguised as some sort of political commentary, the crooks got control of your Mac via zombie malware called OSX/Agent-AADL.
So, if you haven't yet crossed the bridge and become a Mac anti-virus user, now would be a good time to give it a go. Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
Scoop.it!
Plusieurs failles de sécurité ont été repérées par des chercheurs universitaires, celles-ci permettant de contourner la sécurité de l’application keychain, des sandbox des programmes ou encore les mesures de sécurité sur l’App Store.La famille Xara Et ce type de failles se retrouve un peu partout : selon les auteurs de l’étude, qui ont testé 200 applications choisies au hasard sur l'App Store, la grande majorité d'entre elles se révèlent vulnérables face à ces failles de sécurité. Si l’exemple de Keychain est le plus parlant, les chercheurs notent que ce type de vulnérabilités peut être utilisé pour accéder à de nombreux services et applications sur iOS et OSX. Au total, les chercheurs estiment que 88,6% des applications proposées sur l’Apple Store seraient vulnérables à ce type d’attaques. En savoir plus / Merhr erfahren / Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/?tag=XARA
Gust MEES's insight:
Plusieurs failles de sécurité ont été repérées par des chercheurs universitaires, celles-ci permettant de contourner la sécurité de l’application keychain, des sandbox des programmes ou encore les mesures de sécurité sur l’App Store.La famille Xara Et ce type de failles se retrouve un peu partout : selon les auteurs de l’étude, qui ont testé 200 applications choisies au hasard sur l'App Store, la grande majorité d'entre elles se révèlent vulnérables face à ces failles de sécurité. Si l’exemple de Keychain est le plus parlant, les chercheurs notent que ce type de vulnérabilités peut être utilisé pour accéder à de nombreux services et applications sur iOS et OSX. Au total, les chercheurs estiment que 88,6% des applications proposées sur l’Apple Store seraient vulnérables à ce type d’attaques. En savoir plus / Merhr erfahren / Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/?tag=XARA
Scoop.it!

Schwachstellen in iOS und OS X versetzen Apps einer Studie zufolge in die Lage, Daten aus anderen Programmen auszulesen – darunter Passwörter aus dem Mac-Schlüsselbund. Apple habe manipulierte Apps in den Store gelassen. Mehr erfahren / Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/?tag=XARA
Gust MEES's insight:
Schwachstellen in iOS und OS X versetzen Apps einer Studie zufolge in die Lage, Daten aus anderen Programmen auszulesen – darunter Passwörter aus dem Mac-Schlüsselbund. Apple habe manipulierte Apps in den Store gelassen. Mehr erfahren / Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/?tag=XARA
Scoop.it!

From
www
Oh Oh, Apple: Alle gespeicherten Passwörter in iOS und OS X unsicher! Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/?tag=XARA
Gust MEES's insight:
Oh Oh, Apple: Alle gespeicherten Passwörter in iOS und OS X unsicher! Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/?tag=XARA
Scoop.it!

Die bisher beschriebenen Angriffe funktionieren indes nur unter Mac OS X. Unter iOS fanden die Forscher jedoch ebenfalls eine Schwachstelle in Form eines Angriffs über URL-Schemata, die auch unter Mac OS X funktioniert. Ihre Malware beanspruchte beispielsweise das Schemata für die Facebook-Anmeldung für sich. Danach starteten sie Pinterest. Die App authentifizierte sich über Facebook, welches das Token aber zunächst an die Malware weiterleitete. Die wiederum leitete das Token an Pinterest weiter und blieb so unentdeckt. Hier helfe der bereits verfügbarer API-Aufruf openURL:sourceApplication in der Pinterest-App, den es allerdings nur für iOS gebe. Außerdem weise Apple Entwickler nirgends darauf hin, dass sie sich so schützen könnten. . Learn more: . . - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/?tag=XARA
Gust MEES's insight:
Die bisher beschriebenen Angriffe funktionieren indes nur unter Mac OS X. Unter iOS fanden die Forscher jedoch ebenfalls eine Schwachstelle in Form eines Angriffs über URL-Schemata, die auch unter Mac OS X funktioniert. Ihre Malware beanspruchte beispielsweise das Schemata für die Facebook-Anmeldung für sich. Danach starteten sie Pinterest. Die App authentifizierte sich über Facebook, welches das Token aber zunächst an die Malware weiterleitete. Die wiederum leitete das Token an Pinterest weiter und blieb so unentdeckt. Hier helfe der bereits verfügbarer API-Aufruf openURL:sourceApplication in der Pinterest-App, den es allerdings nur für iOS gebe. Außerdem weise Apple Entwickler nirgends darauf hin, dass sie sich so schützen könnten. . Learn more:
Scoop.it!
From
www
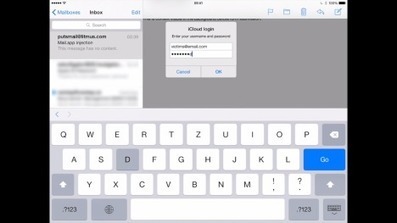
Der Sicherheitsexperte Jan Soucek hat einen äußerst gefährlichen Bug in der E-Mail-App von Apples iOS entdeckt. Ein Angreifer kann darüber eine Fake-Abfrage der Apple-ID einblenden - und so das Passwort abgreifen. CHIP Online meint: Mehr erfahren/ Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
Gust MEES's insight:
Der Sicherheitsexperte Jan Soucek hat einen äußerst gefährlichen Bug in der E-Mail-App von Apples iOS entdeckt. Ein Angreifer kann darüber eine Fake-Abfrage der Apple-ID einblenden - und so das Passwort abgreifen. CHIP Online meint: Mehr erfahren/ Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
Scoop.it!
From
t3n
Ältere Macs sind über eine neuentdeckte Sicherheitslücke angreifbar. Sie ermöglicht es, die Firmware zu überschreiben, die euren Mac bootet. Mehr erfahren/Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/?tag=EFI
Gust MEES's insight:
Ältere Macs sind über eine neuentdeckte Sicherheitslücke angreifbar. Sie ermöglicht es, die Firmware zu überschreiben, die euren Mac bootet. Mehr erfahren/Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/?tag=EFI
Scoop.it!
“It means that you can overwrite the contents of your BIOS from userland a rootkit EFI without any other tricks other than a suspend-resume cycle, a kernel extension, flashrom, and root access. Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
Gust MEES's insight:
“It means that you can overwrite the contents of your BIOS from userland a rootkit EFI without any other tricks other than a suspend-resume cycle, a kernel extension, flashrom, and root access. “The bug can be used with a Safari or other remote vector to install an EFI rootkit without physical access [provided] a suspended happens in the current session … you could probably force the suspend and trigger this, all remotely. That’s pretty epic ownage.” Apple has been contacted for comment. Flash locks are removed when machines enter a sleep state for about 30 seconds or more, allowing attackers to update the flashrom contents from userland including EFI binaries. Affected models include the MacBook Pro Retina, and Pro, and MacBook Airs, each running the latest EFI firmware updates. Some of the latest machines are not affected leading Vilaça to think Apple is aware of the vulnerability. “If they (Apple) indeed knew about the bug – because I don’t believe it’s a coincidence not working in latest machines – then they keep their pattern of not patching older versions,” he says. Learn more: - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security - http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/?tag=EFI
Scoop.it!

From
www
Mit Watch OS 1.0.1 will Apple eine Reihe an Problemen ausräumen, das Update schließt auch etliche Sicherheitslücken. Zur Installation ist ein Kabel erforderlich.
Gust MEES's insight:
Mit Watch OS 1.0.1 will Apple eine Reihe an Problemen ausräumen, das Update schließt auch etliche Sicherheitslücken. Zur Installation ist ein Kabel erforderlich.
Scoop.it!
No sooner had we reported that Microsoft will adopt a "rolling update" model for Windows 10... . . Simple: head to Apple Menu | App Store... | Updates and make sure you have the latest version of Safari. To check your Safari version, run the browser and use Safari | About Safari, or open a Finder window and go to Applications| Safari.app. For more information from the horse's mouth, visit Apple's Security Updateslanding page (which has been re-numbered from HT1222 to HT20122), or theSafari x.x.6 update page itself (HT204826).
Gust MEES's insight:
No sooner had we reported that Microsoft will adopt a "rolling update" model for Windows 10... Simple: head to Apple Menu | App Store... | Updates and make sure you have the latest version of Safari. To check your Safari version, run the browser and use Safari | About Safari, or open a Finder window and go to Applications| Safari.app. For more information from the horse's mouth, visit Apple's Security Updateslanding page (which has been re-numbered from HT1222 to HT20122), or theSafari x.x.6 update page itself (HT204826).
Scoop.it!
CyberSecurity Researchers have uncovered around 25,000 iOS apps that use old versions of a popular networking library, leaving them open to attackers on the same network viewing encrypted traffic.
Gust MEES's insight:
CyberSecurity Researchers have uncovered around 25,000 iOS apps that use old versions of a popular networking library, leaving them open to attackers on the same network viewing encrypted traffic.
|






Durch eine Rechteausweitungslücke kann sich jeder Yosemite-Nutzer zum root erklären. Der Exploit ist so kurz, dass er in einen Tweet passt.
Mehr erfahren / Learn more: