 Your new post is loading...

|
Scooped by
Gust MEES
August 8, 2015 7:15 AM
|
Des chercheurs de Check Point ont identifié de nouvelles vulnérabilités dans les dispositifs Android. Certifi-gate permet à des hackers de prendre le contrôle d'un appareil.
«Certifi-gate», tel est le nom donné à un vulnérabilité découverte par des chercheurs de Check Point au sein du système d'exploitation Android. Elle permet à des applications pour offrir aux pirates un accès sans restriction à l'appareil et ainsi, selon Check Point, «dérober des données personnelles, localiser les appareils, activer le microphone pour enregistrer des conversations, et plus encore».
Learn more / En savoir plus / Mehr erfahren:
http://www.scoop.it/t/securite-pc-et-internet/?tag=Certifi-gate
http://www.scoop.it/t/securite-pc-et-internet/?tag=Android
|
|
Scooped by
Gust MEES
August 4, 2015 7:55 AM
|
Noch bevor die Sicherheitslücken offiziell auf der Hackerkonferenz vorgestellt wurden kursiert eine Anleitung zum Bau eines Proof-of-Concept im Netz. Ferner soll ein russisches Unternehmen bereits einen Exploit verkaufen.
Die Einschläge kommen näher: Ein chinesisches Blog hat weitere Details zu einer der kritischen Stagefright-Lücken in Android veröffentlicht – darunter auch erste Schritte zum Bau eines Exploits. Wenige Änderungen an einer beliebigen MP4-Videodatei reichen aus, um mit ihr Androids Multimedia-Framework Stagefright zum Absturz zu bringen. Dies konnte heise Security nachvollziehen. Es kommt zu einem Heap Overflow, den ein Angreifer zum Ausführen von Schadcode missbrauchen kann. Bleibende Schäden kann eine nach der Anleitung präparierte Datei jedoch nicht anrichten.
Learn more / En savoir plus / Mehr erfahren:
http://www.scoop.it/t/securite-pc-et-internet/?tag=Stagefright
|
|
Scooped by
Gust MEES
July 28, 2015 7:30 AM
|
Es gibt es eine massive Android-Sicherheitslücke, von der wohl 95% aller Smartphones und Tablets mit Android betroffen sein sollen. Dies berichtet Business Insider. Die Lücke wurde von den Sicherheitsforschern von Zimperium zLabs in der Android-Komponente "Stagefright" - "Lampenfieber" - entdeckt. Sie klafft in einer Media-Bibliothek, die von Android verwendet wird, um verbreitete Formate wie etwa PDF-Dateien anzuzeigen. Wie der Vize-Chef von zLabs erläutert, ermögliche schlampig geschriebener Code, dass Angreifer ihren schadhaften Code direkt an Android-Smartphones schicken können.
Sie müssen nur die Telefonnummer des Geräts wissen, das sei alles. Besonders fies: Das Opfer kriegt nichts davon mit. Es gibt nicht einen Dialog oder auch nur eine Nachfrage, die der Nutzer bestätigen müsste.
Learn more / En savoir plus / Mehr erfahren:
|
|
Scooped by
Gust MEES
November 24, 2014 2:39 PM
|
Security researchers have discovered a new type of "Man-in-the-Middle" (MitM) attack in the wild targeting smartphone and tablets users on devices running either iOS or Android around the world.
The MitM attack, dubbed DoubleDirect, enables an attacker to redirect a victim’s traffic of major websites such as Google, Facebook and Twitter to a device controlled by the attacker. Once done, cyber crooks can steal victims’ valuable personal data, such as email IDs, login credentials and banking information as well as can deliver malware to the targeted mobile device.
San Francisco-based mobile security firm Zimperium detailed the threat in a Thursday blog post, revealing that the DoubleDirect technique is being used by attackers in the wild in attacks against the users of web giants including Google, Facebook, Hotmail, Live.com and Twitter, across 31 countries, including the U.S., the U.K. and Canada.
|
|
Scooped by
Gust MEES
May 27, 2014 12:05 PM
|
Spotify users, take note. The music streaming service just posted a message on its company blog indicating that one user's account was hacked, but assuring that steps are being taken to ensure others will not fall victim to the same exploit
Over the coming days, the Spotify Android app will prompt users to re-enter their username and password to log back in. Users running outdated versions of the app will be guided through the update process to ensure they’re running the latest version.
Et si je vous disais qu'il y a dans votre ordinateur un mouchard que vous ne pouvez pas enlever, qui a été mis en place par le constructeur, qui est sur les listes blanches de la plupart des antivirus et dont vous n'avez jamais entendu parler ? La société Kaspersky, spécialisée dans la détection et …
Via Frederic GOUTH, Gust MEES
|
|
Scooped by
Gust MEES
May 7, 2014 4:27 PM
|
The Reveton ransomware gang is selling a version of CryptoLocker that can infect Android devices.
The version of the kit that’s being advertised by the Reveton gang has variants for victims in more than 30 countries, including the United States, UK, France, Germany, Australia and Spain.
|
|
Scooped by
Gust MEES
April 15, 2014 10:55 AM
|
Millions of Android smartphones and tablets are at risk of being attacked via the Heartbleed bug, more than a week after the security vulnerability was first made public.
So, the obvious question you should be considering is, are you running Jellybean 4.1.1 on your Android devices?
Here’s how you can check: - Enter System settings
- Scroll the screen down to About
- Look for your Android version number
read more in the article...
Learn more:
|
|
Scooped by
Gust MEES
February 27, 2014 8:09 AM
|
Researchers have uncovered a potentially massive attack on Android users. This highly elaborate ploy originates on Facebook, where cyber-criminals advertise a series of apps...
|
|
Scooped by
Gust MEES
February 6, 2014 10:12 AM
|
The Electronic Frontier Foundation (EFF) has announced the release of a beta version for its HTTPS Everywhere extension for Firefox on Android.
HTTPS Everywhere is produced as a collaboration between The Tor Project and the EFF.
The extension rewrites all requests to sites from HTTP to HTTPS whenever possible - i.e. it the website supports HTTPS in the first place - and by doing so increasing users' security and privacy. Until now, it was only available for desktop versions of Firefox, Chrome and Opera.
|
|
Scooped by
Gust MEES
January 30, 2014 8:50 AM
|
The vulnerability could allow attackers to intercept traffic from Android devices despite an active VPN connection
A vulnerability in Android allows malicious applications to bypass an active VPN (virtual private network) connection and force traffic from the device through an attacker-controlled system where it can be intercepted, according to security researchers from Ben-Gurion University of the Negev in Israel.
|
|
Scooped by
Gust MEES
November 29, 2013 11:46 AM
|
These days, the 2013 edition of the DefCamp security conference is taking place in Bucharest. There have been a lot of interesting presentations so fa... Alecu has found a vulnerability in Google devices that can be exploited to cause them to reboot.
The security hole impacts devices such as Galaxy Nexus, Nexus 4 and Nexus 5, regardless of the version of Android they’re running (even the latest KitKat)!
|
|
Scooped by
Gust MEES
November 19, 2013 11:30 AM
|
Google Cloud Messaging serving as conduit for sending data from C&C servers Criminals rent such networks to others for malware distribution. Among the malware distributed is the most sophisticated Android Trojan, known as Obad, Kaspersky said. The malware opens a backdoor in an infected device in order to download additional malicious code for stealing money from victims' bank accounts. While not common in the U.S., people in other countries often use their smartphone for money transfers.
|
|
|
Scooped by
Gust MEES
August 5, 2015 7:32 PM
|
An official Google blog post has gone on to say that from this week on, Nexus devices will receive over-the-air security updates on a monthly basis.
Meanwhile, Samsung has announced that it too will be releasing security updates “regularly about once per month.”
“With the recent security issues, we have been rethinking the approach to getting security updates to our devices in a more timely manner. Since software is constantly exploited in new ways, developing a fast response process to deliver security patches to our devices is critical to keep them protected,” said Dong Jin Koh, an executive vice president at Samsung. “We believe that this new process will vastly improve the security of our devices and will aim to provide the best mobile experience possible for our users.”
So, good news. A patch for Stagefright is on its way, as well as the integer overflow bug in Android’s media server service that can “render a phone apparently dead – silent, unable to make calls, with a lifeless screen.”
The announcements haven’t come a minute too soon, as researchers prepared to demonstrate the Stagefright vulnerability to the world at the Black Hat conference in Las Vegas.
For too long many Android users have been treated appallingly, left to fend for themselves with no access to security patches to protect their smartphones and personal data.
Let’s hope that this new momentum to keep users updated shows some real results, and helps defend Android users against increasingly hostile attacks.
Google, Samsung and other Android phone manufactures and service providers… we are watching you. Don’t let us down.
Learn more / En savoir plus / Mehr erfahren:
http://www.scoop.it/t/securite-pc-et-internet/?tag=Stagefright
|
|
Scooped by
Gust MEES
July 28, 2015 8:06 AM
|
Si votre fournisseur de smartphone ou de tablette ne patche pas Stagefright de lui même, ce malware basé sur l’envoi de MMS peut être vraiment effrayant. Mais vous pouvez vous en protéger en respectant quelques étapes.
Stagefright peut attaquer tout smartphone Android, tablette, ou un autre dispositif fonctionnant sous Android 2.2 ou supérieur. Des approximativement quelque 1 milliard de gadgets Android présents sur le marché, Stagefright pourrait, en théorie, toucher 95% d'entre eux. Joshua J. Drake, le vice-président de Zimperium zLabs qui a découvert Stagefright prétend qu'il est parmi les « pires vulnérabilités Android découverts à ce jour ».
Car la partie vraiment sournoise est qu’il n’est pas nécessaire de consulter le MMS pour être infecté. Si vous utilisez l’application Hangouts de Google , vous êtes infectés sans même consulter cette application de messagerie si l’on vous fait parvenir ce message.
Learn more / En savoir plus / Mehr erfahren:
|
|
Scooped by
Gust MEES
July 27, 2015 8:16 PM
|
Successfully exploiting the vulnerabilities could allow an attacker to spy on users, or even completely take over the device.
Researchers with Zimperium have identified multiple critical remote code execution vulnerabilities in Android's Stagefright code that can be exploited on 95 percent of devices – an estimated 950 million – by simply sending an MMS message.
Learn more / En savoir plus / Mehr erfahren:
|
|
Scooped by
Gust MEES
October 7, 2014 3:29 AM
|
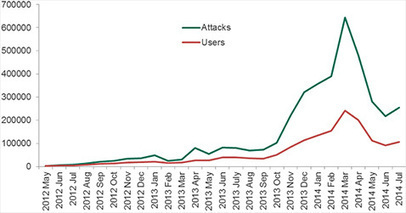
A total of 1,000,000 Android device users around the world encountered dangerous software between August 2013 and July 2014, according to the results of a survey carried out by Kaspersky Lab and INTERPOL. In fact, this period was the peak of cyber attacks registered in recent years.
The most popular malicious programs are SMS Trojans that send messages to premium rate numbers without the owner’s awareness.
|
|
Scooped by
Gust MEES
May 22, 2014 8:16 AM
|
|
|
Scooped by
Gust MEES
May 13, 2014 3:20 AM
|
We've recently found a vulnerability in certain Android apps that may leave user data at risk of being captured or being used to launch attacks.
|
|
Scooped by
Gust MEES
April 16, 2014 12:19 PM
|
A critical security vulnerability has been found in Adobe Reader Mobile, the version of the popular PDF Reader developed for the Android operating system, which [...]
A critical security vulnerability has been found in Adobe Reader Mobile, the version of the popular PDF Reader developed for the Android operating system, which could lead to remote hackers compromising documents stored on your Android device and its SD memory card. If you were feeling smug that you had managed to avoid the Heartbleed flaw affecting up to 50 million Android users because you’re not running Android 4.1.1 of Jellybean, then perhaps you should wipe that smile off your face.
|
|
Scooped by
Gust MEES
March 13, 2014 4:28 PM
|
Android-Entwickler wollen eine geheime Hintertür in Samsung-Galaxy-Smartphones entdeckt haben. Auch zwei von Samsung produzierte Nexus-Phones sollen betroffen sein.
|
|
Scooped by
Gust MEES
February 27, 2014 7:59 AM
|
Cyber criminals can infiltrate your mobile devices with the just discovered first "TOR Trojan for Android".
|
|
Scooped by
Gust MEES
January 30, 2014 5:54 PM
|
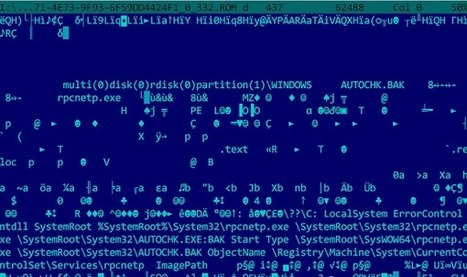
A new trojan for Android has been discovered that resides in the memory of infected devices and launches itself early on in the OS loading stage. Even if some elements of the threat ...
|
|
Scooped by
Gust MEES
January 14, 2014 12:23 PM
|
A fake version of the popular Android game Minecraft - Pocket Edition is half the price of the real thing, but comes with a nasty surprise.
|
|
Scooped by
Gust MEES
November 29, 2013 11:41 AM
|
Un chercheur a trouvé une méthode pour forcer les smartphones de la gamme Nexus de Google à redémarrer et ne pas se connecter au réseau. Il utilise une sorte d'attaques DDOS avec des SMS spéciaux.
|














«Certifi-gate», tel est le nom donné à un vulnérabilité découverte par des chercheurs de Check Point au sein du système d'exploitation Android. Elle permet à des applications pour offrir aux pirates un accès sans restriction à l'appareil et ainsi, selon Check Point, «dérober des données personnelles, localiser les appareils, activer le microphone pour enregistrer des conversations, et plus encore».
Learn more / En savoir plus / Mehr erfahren:
http://www.scoop.it/t/securite-pc-et-internet/?tag=Certifi-gate
http://www.scoop.it/t/securite-pc-et-internet/?tag=Android