 Your new post is loading...

|
Scooped by
Gust MEES
June 13, 2016 7:32 AM
|
Das populäre Exploit-Kit Angler kann selbst speziell gehärtete Windows-Systeme erfolgreich attackieren und mit Schad-Software infizieren.
Mit Tools wie Microsofts EMET kann man ein Windows-System gegen Angriffe härten. Doch die Angreifer schlafen nicht. FireEye hat jetzt erstmals ein Exploit-Kit gesichtet, das ganz gezielt die zusätzlichen Schutzmechanismen von EMET umgeht, um sein Ziel zu erreichen: Das System des Opfers mit Malware wie Erpressungs- oder Online-Banking-Trojanern zu infizieren.
Exploit-Kits werden im Untergrund gehandelt und zum Teil auch als Malware-As-A-Service-Angebote vermietet. Seit einigen Jahren zeichnet sich dabei Angler immer wieder als technisch weit entwickelt aus. Wie FireEye dokumentiert, legen dessen Entwickler jetzt erneut nach und attackieren auch speziell geschützte Windows-Systeme. Learn more / En savoir plus / Mehr erfahren: http://www.scoop.it/t/securite-pc-et-internet/ https://www.scoop.it/topic/securite-pc-et-internet/?&tag=Exploit-Kits
|
|
Scooped by
Gust MEES
June 1, 2016 11:54 AM
|
Information security bods at Trustwave have found a zero-day exploit affecting all versions of Microsoft's OS Windows, all the way from Windows 2000 up to a fully patched version of Windows 10 including all server editions.
It estimates that this affects 1.5 billion computers around the world.
The company provides threat intelligence services and regularly monitors several forums, and it is through this it discovered the exploit which was found on a Russian speaking forum and is currently being offered for sale for £62,000 ($US 90,000).
Trustwave cautioned that there is currently no fix for the exploit and has recommended Windows users stay vigilant for phishing emails. In addition, it has also issued a more general warning about the rise of malware-as-a-service (MaaS).
Ziv Mador, VP of security research at Trustwave, told SCMagazineUK.com, “This is a very serious exploit. From what we've seen in the past, exploits of this type tend to have somewhere in the region of a 10 percent success rate which spells bad news all around.”
According Trustwave, Microsoft has been notified of the zero day offering and is continuing to monitor the situation.
|
|
Scooped by
Gust MEES
February 9, 2016 5:59 PM
|
|
|
Scooped by
Gust MEES
August 3, 2015 2:43 PM
|
Just days after Microsoft released its latest operating system, hackers have begun targeting soon-to-be Windows 10 users with an emerging kind of malware.
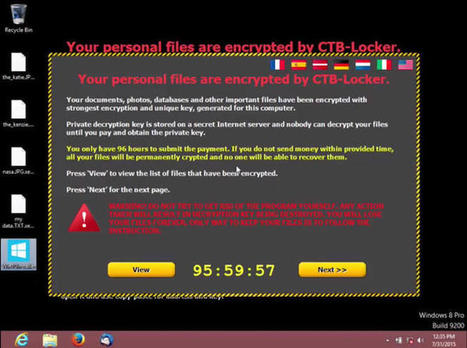
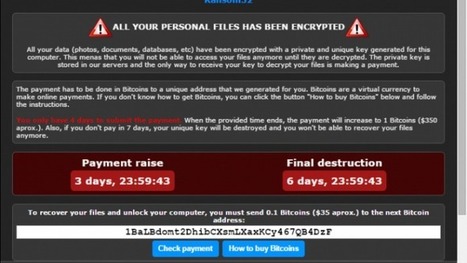
Cisco security researchers are warning users against opening email attachments purporting to be from the software giant. The "ransomware" malware, which encrypts files until a ransom is paid, is being sent as part of an email spam campaign.
|
|
Scooped by
Gust MEES
June 6, 2013 1:05 AM
|
Ohne vorherige Meldung an Microsoft hat ein Sicherheitsforscher Details einer Schwachstelle im Kernel aller gängigen Windows-Versionen mitsamt Exploit-Code veröffentlicht.
|
|
Scooped by
Gust MEES
July 12, 2012 9:36 AM
|
A new malware attack is targeting Mac computers with a Python-based backdoor Trojan.
And Windows computers aren't getting away scott free either.
|
|
Scooped by
Gust MEES
April 11, 2012 12:27 PM
|
Patchday, 10. April 2012: Mit sechs Sicherheits-Updates flickt Microsoft Lecks in Windows XP, Vista und 7. Vier kritische Schwachstellen sind dabei. April-Patchday
Die sechs Aktualisierungen beheben vier kritische Sicherheitslücken sowie zwei Lecks, deren Dringlichkeit Microsoft als „wichtig“ einstuft. Darunter eine kritische Lücke im Internet Explorer, die im Herbst 2011 für Furore unter Facebook-Anwendern sorgte: Eine Porno-Spam-Welle suchte Nutzer des sozialen Netzwerks heim.
|
|
Rescooped by
Gust MEES
from Free Tutorials in EN, FR, DE
January 12, 2012 9:19 AM
|
Des vulnérabilités critiques et exploitables ont été corrigées dans Adobe Reader et Adobe Acrobat. La mise à jour de ces deux applications devra être réalisée sans tarder. Adobe vient aujourd’hui de livrer de nouvelles versions Windows et Mac OS X de son lecteur de PDF, Adobe Reader, et de son outil de création et de gestion des PDF, Adobe Acrobat.
|
|
|
Scooped by
Gust MEES
June 3, 2016 9:11 AM
|
Ein Hacker namens BuggiCorp hat eine schwerwiegende Sicherheitslücke in allen Windows-Versionen seit Windows 2000 entdeckt. Über den Bug kann ein Hacker seiner Malware die höchsten Zugriff auf die höchste Systemsicherheits-Stufe verschaffen.
|
|
Scooped by
Gust MEES
April 16, 2016 9:32 AM
|
Quicktime Player für Windows sollte aus Sicherheitsgründen sofort gelöscht werden
Christoph Fröhlich
Windows-Nutzer sollten schleunigst Apples Videoabspielsoftware Quicktime von ihrem PC löschen, sofern das Programm installiert ist. Das raten die Epxerten der Abteilung für Computersicherheit (US-CERT) der US-amerikanischen Homeland Security. Der Grund: Quicktime erhöhe die Gefahr, sich einen Virus oder andere Schadsoftware wie Würmer oder Trojaner einzufangen. Quicktime für Apples Betriebssystem Mac OS X ist nicht betroffen.
Quicktime für Windows total veraltet
Durch zwei Sicherheitslücken sind Cyberkriminelle in der Lage, ganze Rechner zu übernehmen. Der einzige Schutz ist die "Deinstallation von Quick Time für Windows", wie es in der Warnung des US-Heimatschutzministeriums heißt. Die Behörde beruft sich dabei auf einen Bericht des japanischen Sicherheitsunternehmens Trend Micro. Ausgenutzt werde die Schwachstelle den Experten zufolge noch nicht, doch um sicherzugehen, sollte man die Software trotzdem löschen.
|
|
Scooped by
Gust MEES
January 4, 2016 10:14 AM
|
Sicherheitsforscher warnen vor der Ransomware Ransom32, die sich als JavaScript-Applikation auf Windows-Computer schleicht. Auch Linux und OS X sind potenziell gefährdet. Kriminelle können sich eine individuelle Version des Schädlings generieren lassen.
Learn more / En savoir plus / Mehr erfahren:
http://www.scoop.it/t/securite-pc-et-internet/?tag=RANSOMWARE
|
|
Scooped by
Gust MEES
July 20, 2015 2:26 PM
|
The flaw, affecting Windows Vista, 7, 8, and 8.1, may allow a hacker to take over a machine.
|
|
Scooped by
Gust MEES
July 16, 2012 5:38 PM
|
|
|
Scooped by
Gust MEES
July 11, 2012 12:21 PM
|
|
|
Scooped by
Gust MEES
June 13, 2012 8:23 AM
|
|
|
Scooped by
Gust MEES
April 23, 2012 6:32 PM
|
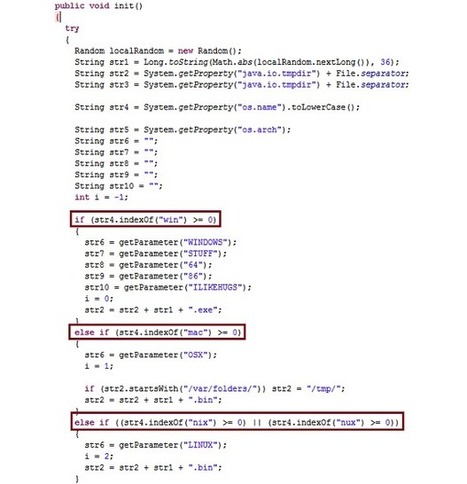
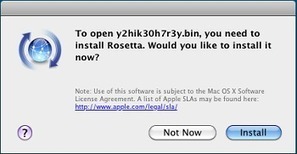
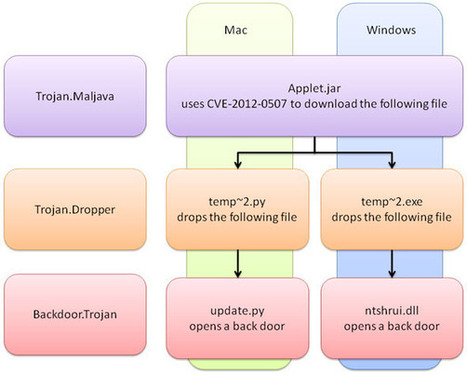
Symantec helps consumers and organizations secure and manage their information-driven world. Symantec Security Response, along with some other security vendors, reported the discovery of the OSX.Flashback malware recently patched by Apple. Many people may be surprised to learn the infection volume is reported at over 600,000 computers. On a new front, we have recently identified new Java Applet malware, which uses the Oracle Java SE Remote Java Runtime Environment Code Execution Vulnerability (CVE-2012-0507) to download its payload. This attack vector is the same as the older one, but in this case the Java Applet checks which OS it is running on and downloads a suitable malware for the OS. This is explained further in the following illustration... Read more...
|
|
Scooped by
Gust MEES
March 14, 2012 9:52 AM
|
Microsoft demande aux utilisateurs de son système d'exploitation d'installer au plus vite sa dernière mise à jour de sécurité, qui corrige deux failles pour lesquelles la firme pense que des exploits devraient apparaître sous 30 jours. La mise à jour MS12-020 corrige deux vulnérabilités liées à l'implémentation du Remote Desktop Protocol, ou RDP (qui est désactivé par défaut). L'une d'elles affecte toutes les versions de Windows et ouvre la porte à l'exécution de code à distance sur le système. ===> UPDATE !!! <===
|















Learn more / En savoir plus / Mehr erfahren:
http://www.scoop.it/t/securite-pc-et-internet/
https://www.scoop.it/topic/securite-pc-et-internet/?&tag=Exploit-Kits