 Your new post is loading...

|
Scooped by
Gust MEES
September 9, 2016 12:13 PM
|
|
|
Scooped by
Gust MEES
September 5, 2016 9:52 AM
|
Today, it is still true that Mac has less malware problem than its counterparts Windows and Android. But, it does not mean that Mac is immune to hackers, or that Mac users should take its security lightly. In 2013 Reuters reported that some Mac operating systems of Apple employees were infected with malware. So, case in point here is that your Mac operating systems are in dire need of security than you think. Learn more / En savoir plus / Mehr erfahren: http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
|
|
Scooped by
Gust MEES
September 2, 2016 4:20 PM
|
|
|
Scooped by
Gust MEES
September 2, 2016 7:27 AM
|
Mises au jour par Citizen Lab et Lookout, les vulnérabilités - anciennement 0-day - de sécurité regroupées sous le nom de Trident ont largement fait parler d'elles la semaine dernière. Présentes dans iOS pendant plusieurs années, leur exploitation a permis l'espionnage de l'iPhone par un malware dénommé Pegasus.
Ce malware a été développé par la firme israélienne NSO Group spécialisée dans l'écoute de téléphonie mobile pour les États. Sa découverte a été presque fortuite suite à l'alerte donnée par un dissident politique aux Émirats arabes unis.
Comme on pouvait s'en douter, les fameuses failles corrigées dans iOS 9.3.5 sont également présentes dans OS X. Les deux systèmes d'exploitation partagent un socle de code commun. Le système d'exploitation pour ordinateur Mac a ainsi droit aujourd'hui à des mises à jour pour combler les vulnérabilités Trident.
Apple ne s'étale pas sur le sujet et livre ses patchs sans évoquer la dangerosité liée aux vulnérabilités. En l'occurrence, OS X El Capitan et Yosemite bénéficient de correctifs pour les failles CVE-2016-4655 et CVE-2016-4656 dans les zones mémoire du noyau et pour les manipuler. Learn more / En savoir plus / Mehr erfahren: http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/?tag=Trident
|
|
Scooped by
Gust MEES
July 25, 2016 4:32 AM
|
Ciscos Sicherheitssparte Talos hat fünf verschiedene Sicherheitslücken entdeckt, die iOS-Geräte und Mac-Computer gleichermaßen betreffen. Sie erlauben Angreifern den Diebstahl von Passwörtern und Daten, Remote-Code-Ausführung und letztlich die vollständige Kontrolle eines Geräts. In den neuesten Versionen von iOS, Mac OS X, tvOS sowie watchOS hat Apple die Schwachstellen bereits behoben, was eine Aktualisierung dringend nahelegt. Learn more / En savoir plus / Mehr erfahren: http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
|
|
Scooped by
Gust MEES
July 24, 2016 6:08 AM
|
La faille, qui touche aussi bien les iPhones que les iPad et les Mac, menace notamment la confidentialité de vos codes et mots de passe. Le fiasco pourrait être de même ampleur que pour Stagefright, la faille critique qui avait fait trembler les utilisateurs d'Android. Dans un post de blog, Tyler Bohan, un chercheur en sécurité informatique de l'entreprise Cisco Talos, il existerait actuellement une faille de sécurité importante dans iOS et Mac OS X, qui permettrait notamment à un pirate de récupérer un mot de passe d'iPhone simplement à partir de l'envoi d'un iMessage ou d'un MMS.
Comment cette faille fonctionne-t-elle ? Selon le chercheur, il suffit qu'un individu mal intentionnéenvoie sur votre appareil, par message multimédia, un petit programme qu'il aura intégré dans une image de format TIFF.
Une fois le message reçu sur votre appareil, le programme en question s'exécute alors tout seul, même si vous n'ouvrez pas le message en question. Il exploite alors une faille dans l'interface de programmation applicative (API) qui gère les données image (imageIO) qui lui permet d'accéder à des données auxquelles un programme de ce type n'est pas censé accéder, telles que vos mots de passe de réseau wi-fi ou de messagerie. Learn more / En savoir plus / Mehr erfahren: http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
|
|
Scooped by
Gust MEES
July 12, 2016 5:58 AM
|
Viren, Trojaner und andere Schadsoftware galten lange als Windows-Problem. Apples Mac-Rechner schienen dagegen immun gegen Malware-Attacken zu sein. Diese Zeiten sind längst vorbei. Auch Macbook Pro und Co. befinden sich längst im Fokus der Hacker. Nun ist ein neuer Trojaner aufgetaucht, der die betroffenen Nutzer zuhause ausspionieren will.
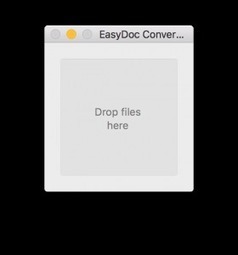
Die Entdecker vom Antiviren-Hersteller "Bitdefender" beschreiben den Trojaner mit dem Namen "Backdoor.MAC.Eleanor" in einem Blog-Eintrag. Weil Hacker auf dem Mac immer noch Schwierigkeiten haben, Schadsoftware ohne Mitwirken des Nutzers einzuschmuggeln, tarnt sich die Malware als vermeintlich harmloses Programm. Bekannt ist die Tarnung als "EasyDoc Converter", ob auch andere Programme als Deckmantel herhalten müssen, ist noch unklar. Learn more / En savoir plus / Mehr erfahren: http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
|
|
Scooped by
Gust MEES
July 9, 2016 8:24 AM
|
|
|
Scooped by
Gust MEES
July 8, 2016 8:30 AM
|
After yesterday security researchers from Bitdefender discovered the Eleanor trojan targeting Macs and opening a backdoor using Tor, today it's ESET's turn to reveal the existence of a similar backdoor trojan that also uses a Tor2Web service to steal Keychain passwords.
Named Keydnap and detected as OSX/Keydnap, this trojan is a new arrival on the Mac malware scene, first seen this past May (internal version 1.3.1), and later in June (version 1.3.5).
The malware's mode of operation is very simple, even if the infection chain is drawn out in several steps.
Keydnap dropper disguised as image or text files
Everything starts when users receive an email that contains an archive. Unzipping this file drops at first glance either an image or a text file. In reality, there's a space after the file's extension, meaning the file will run in the Mac terminal. This file is a Mach-O executable that uses a fake icon.
When executed, this file runs its malicious behavior and then shows an image if it's trying to pose as a picture, or a text pad, if it's trying to pose as a text file. Learn more / En savoir plus / Mehr erfahren: http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
|
|
Scooped by
Gust MEES
March 28, 2016 6:27 PM
|
Des chercheurs de SentinelOne ont mis au jour une importante faille de sécurité qui touche presque la totalité des versions d'iOS et de Mac OS X. Cette dernière permet de réécrire la mémoire afin de prendre le contrôle d'un Mac ou d'un appareil sous iOS et d'exécuter des commandes illicites. Là où le bât blesse, est que ce type d'attaque est difficilement décelable, il est donc possible d'être infecté sans s'en rendre compte et réagir.
Cette vulnérabilité découverte début 2015 et présentée à Apple en janvier 2016 a été corrigée sur les dernières versions d'iOS 9.3 et OS X 10.11.4, vous n'avez pas effectué ces MAJ, on ne peut donc que vous recommander de le faire. L'utilisation de cette faille est complexe et n'est pas du ressort de tout le monde, à ce jour selon les chercheurs de SentinelOne aucun virus ne semble l'exploiter. Learn more / En savoir plus / Mehr erfahren: http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
|
|
Scooped by
Gust MEES
March 7, 2016 7:54 AM
|
Des chercheurs en sécurité ont découvert ce qu’ils pensent être la toute première attaque par ransomware ou rançongiciel ciblant les utilisateurs de Mac d’Apple. Cette menace est actuellement active sur Internet et se diffuse via un logiciel de téléchargement de fichiers Torrent.
Cette attaque a été détectée en toute fin de semaine dernière par des chercheurs de Palo Alto Networks. Ces derniers ont donc identifié un ransomware, "KeRanger", dissimulé au sein d’un client BitTorrent populaire sous OS X, Transmission.
400 dollars pour récupérer ses fichiers Learn more / En savoir plus / Mehr erfahren: http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/?tag=RANSOMWARE http://www.scoop.it/t/ict-security-tools/?tag=Ransomware
|
|
Scooped by
Gust MEES
March 7, 2016 6:53 AM
|
|
|
Scooped by
Gust MEES
March 6, 2016 6:19 PM
|
|
|
|
Rescooped by
Gust MEES
from ICT Security-Sécurité PC et Internet
September 9, 2016 12:05 PM
|
Neue Malware installiert Hintertüren auf Macs
Malware gibt es auch für Mac-Nutzer. Kaspersky hat die OS-X-Variante einer Backdoor-Software entdeckt, die auch für Windows und Linux existiert. Angreifer können damit Tastaturanschläge protokollieren und gezielt nach Dateien suchen.
Eine neue Malware für OS X installiert eine Hintertür auf dem Rechner der Nutzer, wie Kaspersky schreibt. Die Software mit dem Namen OSX.Mokes wurde im Januar dieses Jahres bereits in Versionen für Linux und Windows entdeckt.
Learn more / En savoir plus / Mehr erfahren: http://www.scoop.it/t/securite-pc-et-internet/?tag=cross-platform http://www.scoop.it/t/securite-pc-et-internet
|
|
Scooped by
Gust MEES
September 3, 2016 1:47 PM
|
|
|
Scooped by
Gust MEES
September 2, 2016 9:51 AM
|
Apple has issued an urgent security update for OS X El Capitan, OS X Yosemite and Safari to protect against the same security vulnerability that hit iOS last week.
To update on OS X, go to App Store > Updates and then install the Security Update 2016-001 (for El Capitan) or 2016-005 (for Yosemite). For users on OS X Mavericks, a Safari update is available as well.
Oh and while you’re at it, you should update iOS as well. (Just go to Settings > General > Software Update on your device, and follow the instructions.) The urgent OS X patch comes a week after Lookout Security and Citizen Lab discovered a nasty strain of spyware that could hijack an iPhone with a simple text message. Lookout Security’s Mike Murray called it “one of the most sophisticated pieces of cyberespionage software we’ve ever seen.” Learn more / En savoir plus / Mehr erfahren: http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/?tag=Trident
|
|
Scooped by
Gust MEES
September 2, 2016 6:33 AM
|
Remember the critical security holes that Apple patched in iOS last week after a human rights activist had his iPhone targeted in a seemingly state-sponsored attack?
Ahmed Mansoor received two suspicious SMS messages on his iPhone, directing him to websites containing a zero-day iOS exploit. Researchers connected the attack to Israeli-based firm NSO Group, and dubbed the vulnerabilities "Trident".
Well, Apple has now quietly rolled-out a further security update revealing that the zero-day flaws are also present in Apple's OS X desktop operating system, as well as the desktop version of their OS X Safari browser.
My advice to Apple users? Make sure that your Macs, MacBooks, iPhones and iPads are up-to-date.
On OS X the easiest way to update your computer is to open the App Store app on your Mac, then click Updates in the toolbar. If updates are available, click the Update buttons to download and install them. Learn more / En savoir plus / Mehr erfahren: http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
|
|
Scooped by
Gust MEES
July 24, 2016 6:24 AM
|
Nouvelle vulnérabilité affectant MacOS et iOS, à partir d'une simple image
Sécurité : Dans un nouveau patch publié par Apple, la société corrige une faille permettant à un attaquant d’exécuter du code potentiellement malveillant sur la machine ciblée. Pour cela, celui si peut se contenter d’exploiter une faille dans la façon dont les terminaux Apple traitent les images au format .tiff. Learn more / En savoir plus / Mehr erfahren: http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
|
|
Scooped by
Gust MEES
July 21, 2016 8:57 AM
|
In short, a malicious hacker could email a malformed TIFF to you, or direct you to a webpage where one is embedded, or simply send it directly to your phone via MMS if they knew your number. Whatever route they took, if an attacker managed to trick your computer into rendering the malformed image, your Mac computer or smartphone would be in danger.
The exploitable flaws were discovered by researchers at Cisco’s Talos team, who noted that boobytrapped image files “are an excellent vector for attacks since they can be easily distributed over web or email traffic without raising the suspicion of the recipient.”
The good news is that Apple issued fixes for the problem earlier this week. If you have already updated your systems to iOS 9.3.3, tvOS 9.2.2, watchOS 2.2.2, and El Capitan v10.11.6 then you have done the right thing. Learn more / En savoir plus / Mehr erfahren: http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
|
|
Scooped by
Gust MEES
July 9, 2016 8:38 AM
|
Des logiciels malveillants spécialement pensés pour infecter les ordinateurs d'Apple se multiplient. Piqûre de rappel : les Mac ne sont pas infaillibles. Deux logiciels malveillants, autrement appelés «malwares», destinés au système d’exploitation Apple OS X, ont été repérés cette semaine. La réputation de la marque à la pomme, considérée comme étant bien plus sûre que ses concurrents, risque d’en prendre un coup. Le logiciel malveillant OSX/Keydnap a été découvert le 6 juillet par ESET, une société spécialisée dans la sécurité des systèmes informatiques. Il serait présent en pièce jointe dans certains mails indésirables ou téléchargé par mégarde à partir de sites non sécurisés. Une fois installé sur l’ordinateur, il se présente sous la forme d’un fichier ZIP. Il demande le mot de passe de la session active et le tour est joué. Le pirate aux manettes peut récupérer les identifiants et mots de passe des logiciels installés sur l’ordinateur et peut aussi accéder à ceux des services en ligne des internautes. Cependant, les appareils équipés de la protection Gatekeeper seraient en mesure de bloquer l’attaque. Learn more / En savoir plus / Mehr erfahren: http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/?tag=Keydnap+Malware+Steals+Keychain+Passwords
|
|
Scooped by
Gust MEES
July 8, 2016 6:57 PM
|
More proof-of-concept malware than serious threat, "OSX/Eleanor-A" nevertheless tells an intriguing tale. Mac malware is sufficiently rare, at least compared to Windows and Android, that new OS X malware strains often get a lot of attention. That’s both good and bad. It’s good, because it reminds us all that Macs aren’t magically immune to cybercriminality, and that basing your digital lifestyle on that assumption would be a risky strategy. And it’s bad, because it tends to bring out extreme views, with one side saying that the fuss about Mac malware is no better than unwarranted exaggeration, and the other side accusing Mac users of being credulous fanboys (and gurlz). Nevertheless, Mac malware is often technically interesting, and offers an intriguing insight into online cybercriminality. So, we thought you’d enjoy an article about the recently-discovered OSX/Eleanor-A malware. This malware shows how crooks who don’t know a lot about programming can nevertheless easily and cheaply construct devious attack tools from everyday components. Learn more / En savoir plus / Mehr erfahren: http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
|
|
Scooped by
Gust MEES
July 7, 2016 11:32 AM
|
|
|
Scooped by
Gust MEES
March 7, 2016 9:30 AM
|
|
|
Scooped by
Gust MEES
March 7, 2016 7:09 AM
|
|
|
Scooped by
Gust MEES
March 7, 2016 6:43 AM
|
|







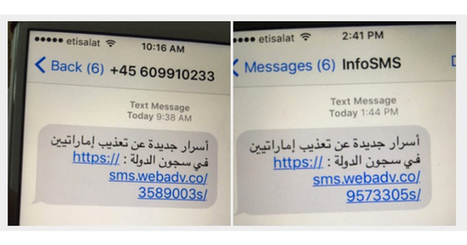







Mac users are at risk of a version of the sophisticated Moke backdoor malware, already discovered for Windows and Linux, that can spy upon you.
Learn more / En savoir plus / Mehr erfahren:
http://www.scoop.it/t/securite-pc-et-internet/?tag=cross-platform
http://www.scoop.it/t/securite-pc-et-internet