Apple, Mac, MacOS, iOS4, iPad, iPhone and (in)security...
18.2K views | +0 today
Apple, Mac, MacOS, iOS4, iPad, iPhone and (in)security...
Everything related to the (in)security of Apple products
Curated by Gust MEES
Your new post is loading...
Scooped by Gust MEES
November 28, 2017 7:56 PM
Scoop.it!

Huge MacOS bug lets anyone login as root without a password: what you need to know | #Apple #CyberSecurity #Awareness #NobodyIsPerfect #Naivety

Huge MacOS bug lets anyone login as root without a password: what you need to know | #Apple #CyberSecurity #Awareness #NobodyIsPerfect #Naivety | Apple, Mac, MacOS, iOS4, iPad, iPhone and (in)security... | Scoop.it
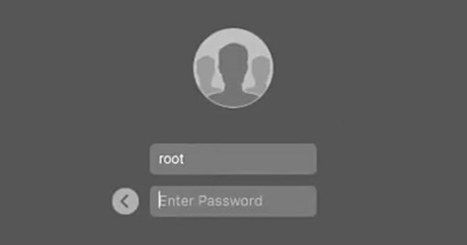
Want to have god-like powers over a Mac? Just enter your username as root... no password required.


But an attacker needs to have physical access to a Mac computer in order to exploit this flaw?

Not so fast. For instance, security researcher Patrick Wardle reports that it is possible to exploit the flaw remotely.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


Gust MEES's insight:
Want to have god-like powers over a Mac? Just enter your username as root... no password required.


But an attacker needs to have physical access to a Mac computer in order to exploit this flaw?

Not so fast. For instance, security researcher Patrick Wardle reports that it is possible to exploit the flaw remotely.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


No comment yet.
Scooped by Gust MEES
November 28, 2017 7:11 PM
Scoop.it!

Apple Macs have gaping root hole – here’s a superquick way to check and fix it | #Cybersecurity #Awareness #NobodyIsPerfect #Mac #Naivety #Passwords

Apple Macs have gaping root hole – here’s a superquick way to check and fix it | #Cybersecurity #Awareness #NobodyIsPerfect #Mac #Naivety #Passwords | Apple, Mac, MacOS, iOS4, iPad, iPhone and (in)security... | Scoop.it
What’s the maddest, baddest, craziest, can-you-believe-it, how-did-that-happen security blunder of recent memory?

Companies contending for the top three spots in the past quarter surely include:

Uber. Suffered a breach, paid the hackers off, pretended it never happened, got found out anyway.


Equifax. Personal data including social security numbers for about half of US adults carried off by crooks.


Apple. When connecting an encrypted device, [Show password hint] would reveal the password itself.


Well, Apple just did it again, and this one is even worse that before – so Cupertino may well be back in first place.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


Gust MEES's insight:
What’s the maddest, baddest, craziest, can-you-believe-it, how-did-that-happen security blunder of recent memory?

Companies contending for the top three spots in the past quarter surely include:

Uber. Suffered a breach, paid the hackers off, pretended it never happened, got found out anyway.


Equifax. Personal data including social security numbers for about half of US adults carried off by crooks.


Apple. When connecting an encrypted device, [Show password hint] would reveal the password itself.


Well, Apple just did it again, and this one is even worse that before – so Cupertino may well be back in first place.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


No comment yet.
Scooped by Gust MEES
November 28, 2017 6:50 PM
Scoop.it!

Huge security flaw lets anyone log into a MacOS High Sierra | #Mac #Apple #CyberSecurity #NobodyIsPerfect #Naivety #Awareness 

Huge security flaw lets anyone log into a MacOS High Sierra | #Mac #Apple #CyberSecurity #NobodyIsPerfect #Naivety #Awareness  | Apple, Mac, MacOS, iOS4, iPad, iPhone and (in)security... | Scoop.it
Update: Apple has acknowledged the issue and is working on it. Statement and workaround below.

Wow, this is a bad one. On Macs running the latest version of High Sierra — 10.13.1 (17B48) — it appears that anyone can log in just by putting “root” in the user name field. This is a huge, huge problem. Apple will fix it probably within hours, but holy moly. Do not leave your Mac unattended until this is resolved.

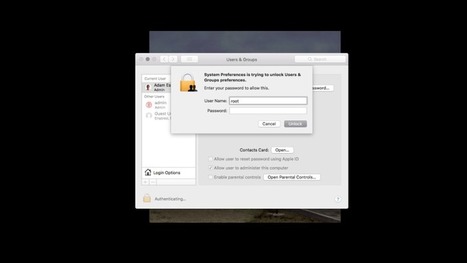
The bug is most easily accessed by going to Preferences and then entering one of the panels that has a lock in the lower left-hand corner. Normally you’d click that to enter your user name and password, which are required to change important settings like those in Security & Privacy.

No need to do that any more! Just enter “root” instead of your user name and hit enter. After a few tries, it should log right in. There’s no need to do this yourself to verify it. Doing so creates a “root” account that others may be able to take advantage of if you don’t disable it.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


Gust MEES's insight:
Update: Apple has acknowledged the issue and is working on it. Statement and workaround below.

Wow, this is a bad one. On Macs running the latest version of High Sierra — 10.13.1 (17B48) — it appears that anyone can log in just by putting “root” in the user name field. This is a huge, huge problem. Apple will fix it probably within hours, but holy moly. Do not leave your Mac unattended until this is resolved.

The bug is most easily accessed by going to Preferences and then entering one of the panels that has a lock in the lower left-hand corner. Normally you’d click that to enter your user name and password, which are required to change important settings like those in Security & Privacy.

No need to do that any more! Just enter “root” instead of your user name and hit enter. After a few tries, it should log right in. There’s no need to do this yourself to verify it. Doing so creates a “root” account that others may be able to take advantage of if you don’t disable it.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


No comment yet.
Scooped by Gust MEES
November 28, 2017 6:37 PM
Scoop.it!

MacOS High Sierra Users: Change Root Password Now — Krebs on Security | #Apple #CyberSecurity #Awareness #Mac #Passwords #NobodyIsPerfect #Naivety

MacOS High Sierra Users: Change Root Password Now — Krebs on Security | #Apple #CyberSecurity #Awareness #Mac #Passwords #NobodyIsPerfect #Naivety | Apple, Mac, MacOS, iOS4, iPad, iPhone and (in)security... | Scoop.it
A newly-discovered flaw in macOS High Sierra — Apple’s latest iteration of its operating system — allows anyone with local (and, apparently in some cases, remote) access to the machine to log in as the all-powerful “root” user without supplying a password. Fortunately, there is a simple fix for this until Apple patches this inexplicable bug: Change the root account’s password now.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


Gust MEES's insight:
A newly-discovered flaw in macOS High Sierra — Apple’s latest iteration of its operating system — allows anyone with local (and, apparently in some cases, remote) access to the machine to log in as the all-powerful “root” user without supplying a password. Fortunately, there is a simple fix for this until Apple patches this inexplicable bug: Change the root account’s password now.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


No comment yet.
Scooped by Gust MEES
November 10, 2017 4:36 PM
Scoop.it!

The volume of Mac malware | #Apple #CyberSecurity #NobodyIsPerfect

The volume of Mac malware | #Apple #CyberSecurity #NobodyIsPerfect | Apple, Mac, MacOS, iOS4, iPad, iPhone and (in)security... | Scoop.it
The volume of malware targeting Macs is growing fast as shown by the data from our Labs. Attackers are shifting their efforts towards Macs.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


Gust MEES's insight:
The volume of malware targeting Macs is growing fast as shown by the data from our Labs. Attackers are shifting their efforts towards Macs.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


No comment yet.
Scooped by Gust MEES
October 5, 2017 7:33 PM
Scoop.it!

Urgent! Update your Mac again, right now… | #CyberSecurity #Apple #NobodyIsPerfect #FSCD

Urgent! Update your Mac again, right now… | #CyberSecurity #Apple #NobodyIsPerfect #FSCD | Apple, Mac, MacOS, iOS4, iPad, iPhone and (in)security... | Scoop.it
It’s only eight days since Apple’s latest and greatest macOS 10.13 release, better known as High Sierra.

But the first security update has already come out, and we suggest you apply it urgently.

The update is called High Sierra 10.13 Supplemental Update, detailed in the security advistory APPLE-SA-2017-10-05-1.


Learn more / En savoir plus / Mehr erfahren:


http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


Gust MEES's insight:
It’s only eight days since Apple’s latest and greatest macOS 10.13 release, better known as High Sierra.

But the first security update has already come out, and we suggest you apply it urgently.

The update is called High Sierra 10.13 Supplemental Update, detailed in the security advistory APPLE-SA-2017-10-05-1.


Learn more / En savoir plus / Mehr erfahren:


http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


No comment yet.
Scooped by Gust MEES
September 30, 2017 7:01 AM
Scoop.it!

Des failles EFI pour près de 5% des Mac | #Apple #CyberSecurity

Des failles EFI pour près de 5% des Mac | #Apple #CyberSecurity | Apple, Mac, MacOS, iOS4, iPad, iPhone and (in)security... | Scoop.it

Apple a mal à son EFI. Duo Security a mené une analyse au longs cours concernant l’Extensible Firmware Interface — le programme de démarrage — de 73 000 Mac et surprise, même si des mises à jour de macOS y sont régulièrement appliquées, un certain nombre d’entre eux restent vulnérables à des attaques. La faute à des EFI qui ne sont pas à jour malgré l’application d’une version toute neuve du système d’exploitation.

Dans l’étude, c’est le cas pour 4,2% des machines : 47 des Mac analysés sont susceptibles d’être infectés via la faille Thunderstrike datant de 2014, 31 autres ordinateurs sont vulnérables à la faille Thunderstrike 2 et au “tournevis sonique” mis au point par la CIA (des attaques qui nécessitent toutefois un accès physique aux ordinateurs). Plus inquiétant, 43% des iMac 21,5 pouces lancés fin 2015 se montrent sensibles à ces failles.


Learn more / En savoir plus / Mehr erfahren:


http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


Gust MEES's insight:

Apple a mal à son EFI. Duo Security a mené une analyse au longs cours concernant l’Extensible Firmware Interface — le programme de démarrage — de 73 000 Mac et surprise, même si des mises à jour de macOS y sont régulièrement appliquées, un certain nombre d’entre eux restent vulnérables à des attaques. La faute à des EFI qui ne sont pas à jour malgré l’application d’une version toute neuve du système d’exploitation.

Dans l’étude, c’est le cas pour 4,2% des machines : 47 des Mac analysés sont susceptibles d’être infectés via la faille Thunderstrike datant de 2014, 31 autres ordinateurs sont vulnérables à la faille Thunderstrike 2 et au “tournevis sonique” mis au point par la CIA (des attaques qui nécessitent toutefois un accès physique aux ordinateurs). Plus inquiétant, 43% des iMac 21,5 pouces lancés fin 2015 se montrent sensibles à ces failles.


Learn more / En savoir plus / Mehr erfahren:


http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


No comment yet.
Scooped by Gust MEES
September 28, 2017 4:54 AM
Scoop.it!

[Infographic] More Mac malware than ever before | #Apple #CyberSecurity #Awareness

[Infographic] More Mac malware than ever before | #Apple #CyberSecurity #Awareness | Apple, Mac, MacOS, iOS4, iPad, iPhone and (in)security... | Scoop.it
Mac malware is on the rise, shows the analysis of Mac attacks by F-Secure Labs. Most are spyware, but also targeted attacks and ransomware.


Learn more / En savoir plus / Mehr erfahren:


http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


Gust MEES's insight:
Mac malware is on the rise, shows the analysis of Mac attacks by F-Secure Labs. Most are spyware, but also targeted attacks and ransomware.


Learn more / En savoir plus / Mehr erfahren:


http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


No comment yet.
Scooped by Gust MEES
September 23, 2017 9:00 AM
Scoop.it!

Some Mac users are getting hit with ransomware -- here's what to do | #CyberSecurity #Apple 

Some Mac users are getting hit with ransomware -- here's what to do | #CyberSecurity #Apple  | Apple, Mac, MacOS, iOS4, iPad, iPhone and (in)security... | Scoop.it
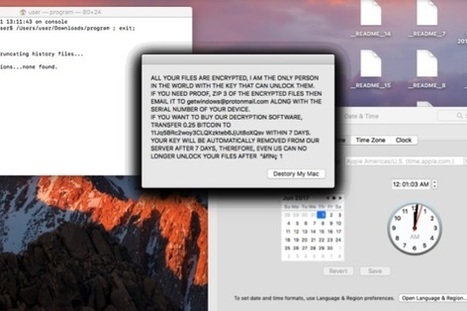
Several Mac users are complaining about getting locked out of their computers for a bitcoin ransom.


Learn more / En savoir plus / Mehr erfahren:


 http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/?&tag=RANSOMWARE


Gust MEES's insight:
Several Mac users are complaining about getting locked out of their computers for a bitcoin ransom.


Learn more / En savoir plus / Mehr erfahren:


 http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/?&tag=RANSOMWARE


No comment yet.
Scooped by Gust MEES
July 25, 2017 10:59 AM
Scoop.it!

Mac-Malware Fruitfly kann Maus und Tastatur bedienen sowie Webcam einschalten | #Apple #CyberSecurity 

Mac-Malware Fruitfly kann Maus und Tastatur bedienen sowie Webcam einschalten | #Apple #CyberSecurity  | Apple, Mac, MacOS, iOS4, iPad, iPhone and (in)security... | Scoop.it

Fruitfly blieb wahrscheinlich mehrere Jahre unentdeckt. Die neue Variante der Malware erlaubt es Angreifern, aus der Ferne die vollständige Kontrolle zu übernehmen...


Learn more / En savoir plus / Mehr erfahren:


http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/?&tag=Fruitfly


http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


Gust MEES's insight:

Fruitfly blieb wahrscheinlich mehrere Jahre unentdeckt. Die neue Variante der Malware erlaubt es Angreifern, aus der Ferne die vollständige Kontrolle zu übernehmen...


Learn more / En savoir plus / Mehr erfahren:


http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/?&tag=Fruitfly


http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


No comment yet.
Scooped by Gust MEES
June 25, 2017 5:00 PM
Scoop.it!

Mac users face increased ransomware threats | #Apple #CyberSecurity #NobodyIsPerfect #Awareness

Mac users face increased ransomware threats | #Apple #CyberSecurity #NobodyIsPerfect #Awareness | Apple, Mac, MacOS, iOS4, iPad, iPhone and (in)security... | Scoop.it
Apple Inc. has a reputation for building secure devices, but don’t become too complacent because ransomware threats to Mac users are on the rise.

While ransomware attacks against Microsoft Windows-based computers and servers remain far more prevalent, security researchers have detected new Mac threats in recent years and expect to see new threats in the future.


Protect your Mac from ransomware
Mac users are clearly not free from the threat of ransomware. While not at epidemic proportions, ransomware attacks against Macs have seen widespread success by breaking into systems that were assumed secure. Fortunately, users today have access to a variety of backup options. You can add an extra layer of protection to your Mac computer by stepping beyond the Apple ecosystem of TimeMachine nearline backups and iCloud synchronization and embracing a third-party cloud backup solution.


Learn more / En savoir plus / Mehr erfahren:


http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/?&tag=RANSOMWARE


http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


Gust MEES's insight:
Apple Inc. has a reputation for building secure devices, but don’t become too complacent because ransomware threats to Mac users are on the rise.

While ransomware attacks against Microsoft Windows-based computers and servers remain far more prevalent, security researchers have detected new Mac threats in recent years and expect to see new threats in the future.


Protect your Mac from ransomware
Mac users are clearly not free from the threat of ransomware. While not at epidemic proportions, ransomware attacks against Macs have seen widespread success by breaking into systems that were assumed secure. Fortunately, users today have access to a variety of backup options. You can add an extra layer of protection to your Mac computer by stepping beyond the Apple ecosystem of TimeMachine nearline backups and iCloud synchronization and embracing a third-party cloud backup solution.


Learn more / En savoir plus / Mehr erfahren:


http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/?&tag=RANSOMWARE


http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


No comment yet.
Scooped by Gust MEES
June 12, 2017 10:47 AM
Scoop.it!

Mac users beware! Hackers are selling 'the most sophisticated' Mac malware ever | #MacSpy #CyberSecurity

Mac users beware! Hackers are selling 'the most sophisticated' Mac malware ever | #MacSpy #CyberSecurity | Apple, Mac, MacOS, iOS4, iPad, iPhone and (in)security... | Scoop.it

Just because you’re using a Mac doesn’t mean you’ve escaped the malware threat.


Two new security threats, a malware-as-a-service (MaaS) platform and a ransomware-as-a-service (RaaS) program, are designed to specifically target machines running Apple macOS.


Two new security threats, a malware-as-a-service (MaaS) platform and a ransomware-as-a-service (RaaS) program, are designed to specifically target machines running Apple macOS.

The MaaS platform, known as "MacSpy," responds to what its authors feel is an ongoing lack of "sophisticated malware for Mac users". Of course, that perception is not entirely accurate. We've seen numerous sophisticated malware strainsdeveloped for Macs over the past year or so.


It's true, however, that MacSpy takes this budding proliferation to the next level by making macOS malware more accessible to users with low levels of technical expertise.


Learn more / En savoir plus / Mehr erfahren:


http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


Gust MEES's insight:

Just because you’re using a Mac doesn’t mean you’ve escaped the malware threat.


Two new security threats, a malware-as-a-service (MaaS) platform and a ransomware-as-a-service (RaaS) program, are designed to specifically target machines running Apple macOS.


Two new security threats, a malware-as-a-service (MaaS) platform and a ransomware-as-a-service (RaaS) program, are designed to specifically target machines running Apple macOS.

The MaaS platform, known as "MacSpy," responds to what its authors feel is an ongoing lack of "sophisticated malware for Mac users". Of course, that perception is not entirely accurate. We've seen numerous sophisticated malware strainsdeveloped for Macs over the past year or so.


It's true, however, that MacSpy takes this budding proliferation to the next level by making macOS malware more accessible to users with low levels of technical expertise.


Learn more / En savoir plus / Mehr erfahren:


http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


No comment yet.
Scooped by Gust MEES
May 11, 2017 10:51 AM
Scoop.it!

MacOS : un malware en cadeau avec le téléchargement d'Handbrake | #Apple #CyberSecurity 

MacOS : un malware en cadeau avec le téléchargement d'Handbrake | #Apple #CyberSecurity  | Apple, Mac, MacOS, iOS4, iPad, iPhone and (in)security... | Scoop.it

Quoi de mieux pour piéger l'utilisateur de se faire passer pour une source légitime ? Des pirates ont ainsi réussi à s'introduire dans les serveurs de l'éditeur d'Handbrake et ont remplacé le logiciel d'encodage vidéo par une version piégée. Du coup, entre le 2 et le 6 mai dernier, si vous avez téléchargé (ou mis à jour) l'application vous avez toutes les chances (une chance sur deux pour être précis) d'avoir obtenu une version corrompue avec un joli malware en cadeau (OSX.PROTON).


Afin de vérifier si son Mac est infecté, il suffit d’ouvrir le Moniteur d’activité (localisé dans le dossier 'Utilitaires' d’Applications) et de regarder si le processus 'activity_agent' est en cours d’exécution. Si tel est le cas, cela veut dire que le malware est actif sur la machine.


Learn more / En savoir plus / Mehr erfahren:


http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/?&tag=HandBrake


http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


Gust MEES's insight:

Quoi de mieux pour piéger l'utilisateur de se faire passer pour une source légitime ? Des pirates ont ainsi réussi à s'introduire dans les serveurs de l'éditeur d'Handbrake et ont remplacé le logiciel d'encodage vidéo par une version piégée. Du coup, entre le 2 et le 6 mai dernier, si vous avez téléchargé (ou mis à jour) l'application vous avez toutes les chances (une chance sur deux pour être précis) d'avoir obtenu une version corrompue avec un joli malware en cadeau (OSX.PROTON).


Afin de vérifier si son Mac est infecté, il suffit d’ouvrir le Moniteur d’activité (localisé dans le dossier 'Utilitaires' d’Applications) et de regarder si le processus 'activity_agent' est en cours d’exécution. Si tel est le cas, cela veut dire que le malware est actif sur la machine.


Learn more / En savoir plus / Mehr erfahren:


http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/?&tag=HandBrake


http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


No comment yet.
Scooped by Gust MEES
November 28, 2017 7:33 PM
Scoop.it!

Einfacher Trick gibt Computer frei - Riesige Sicherheitslücke ​in neuer Apple-Software | #Mac #macOS #CyberSecurity #Awareness #NobodyIsPerfect #Naivety 

Einfacher Trick gibt Computer frei - Riesige Sicherheitslücke ​in neuer Apple-Software | #Mac #macOS #CyberSecurity #Awareness #NobodyIsPerfect #Naivety  | Apple, Mac, MacOS, iOS4, iPad, iPhone and (in)security... | Scoop.it
Sicherheitsexperten haben eine gigantische Lücke im neuen Apple-Betriebsystem Mac OS High Sierra entdeckt!


Laut einem Bericht des Magazin „Wired“ lässt sich die Abfrage von Nutzername und Passwort mit einem erschreckend einfachen Trick umgehen: Statt des Nutzernamens tippt man lediglich das Wort „root“ ein, lässt das Passwort-Feld leer, drückt mehrfach die Eingabetaste – und erhält vollständigen Zugriff auf das Gerät.


Dann sei es jedem Angreifer mit Zugang zu einem solchen Computer möglich, in die tiefsten Systemeinstellungen vorzudringen.


Beim Kurznachrichtendienst Twitter zeigen gleich mehrere Nutzer, wie simpel sich die Passwortabfrage aushebeln lässt.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


Gust MEES's insight:
Sicherheitsexperten haben eine gigantische Lücke im neuen Apple-Betriebsystem Mac OS High Sierra entdeckt!


Laut einem Bericht des Magazin „Wired“ lässt sich die Abfrage von Nutzername und Passwort mit einem erschreckend einfachen Trick umgehen: Statt des Nutzernamens tippt man lediglich das Wort „root“ ein, lässt das Passwort-Feld leer, drückt mehrfach die Eingabetaste – und erhält vollständigen Zugriff auf das Gerät.


Dann sei es jedem Angreifer mit Zugang zu einem solchen Computer möglich, in die tiefsten Systemeinstellungen vorzudringen.


Beim Kurznachrichtendienst Twitter zeigen gleich mehrere Nutzer, wie simpel sich die Passwortabfrage aushebeln lässt.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


No comment yet.
Scooped by Gust MEES
November 28, 2017 7:05 PM
Scoop.it!

There's a Massive Security Vulnerability in the New macOS | #Apple #Cybersecurity #Awareness #NobodyIsPerfect #Naivety

There's a Massive Security Vulnerability in the New macOS | #Apple #Cybersecurity #Awareness #NobodyIsPerfect #Naivety | Apple, Mac, MacOS, iOS4, iPad, iPhone and (in)security... | Scoop.it
In software, there are bugs, and there are dangerous bugs. It looks like macOS High Sierra has one of those dangerous bugs; one that could give someone full access to virtually any user account. And holy buckets, it is scary.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


Gust MEES's insight:
In software, there are bugs, and there are dangerous bugs. It looks like macOS High Sierra has one of those dangerous bugs; one that could give someone full access to virtually any user account. And holy buckets, it is scary.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


No comment yet.
Scooped by Gust MEES
November 28, 2017 6:44 PM
Scoop.it!

Anyone Can Hack MacOS High Sierra Just by Typing "Root" | #Apple #CyberSecurity #Mac #NobodyIsPerfect #Naivety #Awareness 

Anyone Can Hack MacOS High Sierra Just by Typing "Root" | #Apple #CyberSecurity #Mac #NobodyIsPerfect #Naivety #Awareness  | Apple, Mac, MacOS, iOS4, iPad, iPhone and (in)security... | Scoop.it
THERE ARE HACKABLE security flaws in software. And then there are those that don't even require hacking at all—just a knock on the door, and asking to be let in. Apple's macOS High Sierra has the second kind.

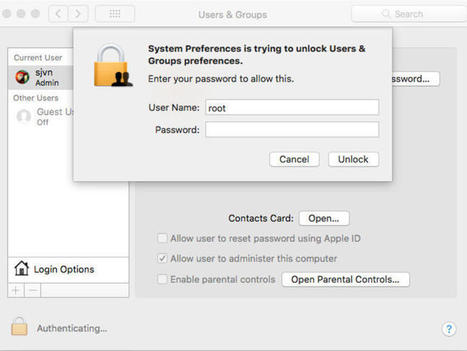
On Tuesday, security researchers disclosed a bug that allows anyone a blindingly easy method of breaking that operating system's security protections. Anyone who hits a prompt in High Sierra asking for a username and password before logging into a machine with multiple users, they can simply type "root" as a username, leave the password field blank, click "unlock" twice, and immediately gain full access.

In other words, the bug allows any rogue user that gets the slightest foothold on a target computer to gain the deepest level of access to a computer, known as "root" privileges. Malware designed to exploit the trick could also fully install itself deep within the computer, no password required.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


Gust MEES's insight:
THERE ARE HACKABLE security flaws in software. And then there are those that don't even require hacking at all—just a knock on the door, and asking to be let in. Apple's macOS High Sierra has the second kind.

On Tuesday, security researchers disclosed a bug that allows anyone a blindingly easy method of breaking that operating system's security protections. Anyone who hits a prompt in High Sierra asking for a username and password before logging into a machine with multiple users, they can simply type "root" as a username, leave the password field blank, click "unlock" twice, and immediately gain full access.

In other words, the bug allows any rogue user that gets the slightest foothold on a target computer to gain the deepest level of access to a computer, known as "root" privileges. Malware designed to exploit the trick could also fully install itself deep within the computer, no password required.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


No comment yet.
Scooped by Gust MEES
November 28, 2017 6:05 PM
Scoop.it!

Stupid, stupid MacOS security flaw grants admin access to anyone | #Apple #CyberSecurity #Naivety #Awareness #NobodyIsPerfect 

Stupid, stupid MacOS security flaw grants admin access to anyone | #Apple #CyberSecurity #Naivety #Awareness #NobodyIsPerfect  | Apple, Mac, MacOS, iOS4, iPad, iPhone and (in)security... | Scoop.it
Apple, Apple, Apple. What are we going to do with you? In your most recent High Sierra macOS release, it turns out you've given a way for any local user to take over a Mac -- lock, stock, and two smoking barrels.

This exploit doesn't require any mad NSA-type hacker skillz. All you have to do is go to System Preferences, then Users and Groups, and click the lock to make changes. Then, enter "root" as your username without a password. Shazam! You're in.

As on any Unix/Linux-based system, the root user can control all administration functions and can read and write to any file system, including those of other users. In theory, root is disabled on Apple systems unless expressly authorized. Wrong!

Once in, you can edit your own permissions. For example, want to give yourself administrator privileges? Sure! Or, you can set up new administration-level accounts. Once you've done that, you can do anything your heart desires within the system.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


Gust MEES's insight:
Apple, Apple, Apple. What are we going to do with you? In your most recent High Sierra macOS release, it turns out you've given a way for any local user to take over a Mac -- lock, stock, and two smoking barrels.

This exploit doesn't require any mad NSA-type hacker skillz. All you have to do is go to System Preferences, then Users and Groups, and click the lock to make changes. Then, enter "root" as your username without a password. Shazam! You're in.

As on any Unix/Linux-based system, the root user can control all administration functions and can read and write to any file system, including those of other users. In theory, root is disabled on Apple systems unless expressly authorized. Wrong!

Once in, you can edit your own permissions. For example, want to give yourself administrator privileges? Sure! Or, you can set up new administration-level accounts. Once you've done that, you can do anything your heart desires within the system.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


No comment yet.
Scooped by Gust MEES
October 21, 2017 10:26 AM
Scoop.it!

Mac OSX Trojan malware spread via compromised software downloads | #CyberSecurity #Apple 

Mac OSX Trojan malware spread via compromised software downloads | #CyberSecurity #Apple  | Apple, Mac, MacOS, iOS4, iPad, iPhone and (in)security... | Scoop.it
Supply-chain attack saw data-stealing Proton RAT loaded into legitimate downloads of Elmedia Player and Folx applications by Eltima Software.


Learn more / En savoir plus / Mehr erfahren:


http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


Gust MEES's insight:
Supply-chain attack saw data-stealing Proton RAT loaded into legitimate downloads of Elmedia Player and Folx applications by Eltima Software.


Learn more / En savoir plus / Mehr erfahren:


http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


No comment yet.
Scooped by Gust MEES
October 3, 2017 6:53 AM
Scoop.it!

Les mises à jour de sécurité du système d’amorçage des Mac sont défaillantes | #Apple #CyberSecurity

Les mises à jour de sécurité du système d’amorçage des Mac sont défaillantes | #Apple #CyberSecurity | Apple, Mac, MacOS, iOS4, iPad, iPhone and (in)security... | Scoop.it
Dans de nombreux cas, le système EFI des Mac reste vulnérable même si l’on télécharge toutes les mises à jour proposées par Apple. Les utilisateurs concernés peuvent donc être la cible d’attaques Thunderstrike, particulièrement néfastes.

Vous avez un Mac totalement patché et vous vous sentez en sécurité ? Voici une étude qui risque de vous faire déchanter. Les chercheurs en sécurité Rich Smith et Pepjin Bruienne de la société Duo ont analysé le niveau de sécurité du système d’amorçage EFI de 73.324 ordinateurs Mac et – surprise – celui-ci est loin d’être toujours à la hauteur des espérances.


Learn more / En savoir plus / Mehr erfahren:


http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/?&tag=EFI


Gust MEES's insight:
Dans de nombreux cas, le système EFI des Mac reste vulnérable même si l’on télécharge toutes les mises à jour proposées par Apple. Les utilisateurs concernés peuvent donc être la cible d’attaques Thunderstrike, particulièrement néfastes.

Vous avez un Mac totalement patché et vous vous sentez en sécurité ? Voici une étude qui risque de vous faire déchanter. Les chercheurs en sécurité Rich Smith et Pepjin Bruienne de la société Duo ont analysé le niveau de sécurité du système d’amorçage EFI de 73.324 ordinateurs Mac et – surprise – celui-ci est loin d’être toujours à la hauteur des espérances.


Learn more / En savoir plus / Mehr erfahren:


http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/?&tag=EFI


No comment yet.
Scooped by Gust MEES
September 29, 2017 3:34 PM
Scoop.it!

New study finds small percentage of Macs are running insecure firmware | #Apple #CyberSecurity #Updates 

New study finds small percentage of Macs are running insecure firmware | #Apple #CyberSecurity #Updates  | Apple, Mac, MacOS, iOS4, iPad, iPhone and (in)security... | Scoop.it

If you own a Mac and haven't upgraded to the new High Sierra OS, your system could be vulnerable to threats like Thunderstrike, a malware attack that enters through your computer's Thunderbolt port.

Researchers from Duo Security published a white paper today explaining the potential issues, which was first noticed by 9to5Mac. The firm analyzed 73,324 Mac computers and found that, on average, 4.2 percent of them weren't running the proper firmware, leaving the systems vulnerable to cyber attacks. Luckily for consumers, the vulnerabilities aren't thought to be as risky for home users according to a Duo blog post summarizing the paper — but you should still be sure you're running the right firmware. 

Although Apple has released security updates to protect against Thunderstrike attacks, the researchers found that, for some reason, the critical updates weren't always applied.


Learn more / En savoir plus / Mehr erfahren:


http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


Gust MEES's insight:
If you own a Mac and haven't upgraded to the new High Sierra OS, your system could be vulnerable to threats like Thunderstrike, a malware attack that enters through your computer's Thunderbolt port.

Researchers from Duo Security published a white paper today explaining the potential issues, which was first noticed by 9to5Mac. The firm analyzed 73,324 Mac computers and found that, on average, 4.2 percent of them weren't running the proper firmware, leaving the systems vulnerable to cyber attacks. Luckily for consumers, the vulnerabilities aren't thought to be as risky for home users according to a Duo blog post summarizing the paper — but you should still be sure you're running the right firmware. 

Although Apple has released security updates to protect against Thunderstrike attacks, the researchers found that, for some reason, the critical updates weren't always applied.


Learn more / En savoir plus / Mehr erfahren:


http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


No comment yet.
Scooped by Gust MEES
September 26, 2017 12:16 PM
Scoop.it!

MacOS High Sierra: MacOS-Keychain kann per App ausgelesen werden | #Apple #CyberSecurity #NobodyIsPerfect 

MacOS High Sierra: MacOS-Keychain kann per App ausgelesen werden | #Apple #CyberSecurity #NobodyIsPerfect  | Apple, Mac, MacOS, iOS4, iPad, iPhone and (in)security... | Scoop.it
MacOS-Keychain kann per App ausgelesen werden
Der Sicherheitsforscher Patrick Wardle hat demonstriert, dass Apples Keychain unter MacOS mit einer App komplett ausgelesen werden kann. Diese muss aber zunächst an Apples Gatekeeper vorbei.


Der Hacker Patrick Wardle hat nach eigenen Angaben eine Sicherheitslücke in der aktuellen Version von Apples Desktop-Betriebssystem High Sierra gefunden, die es bösartigen Applikationen ermöglicht, Passwörter aus Apples Keychain auszulesen. Normalerweise müssen Nutzer einzelne Passwörter durch Eingabe eines Master-Passworts freigeben.


Learn more / En savoir plus / Mehr erfahren:


http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/?&tag=MacOS


Gust MEES's insight:
MacOS-Keychain kann per App ausgelesen werden
Der Sicherheitsforscher Patrick Wardle hat demonstriert, dass Apples Keychain unter MacOS mit einer App komplett ausgelesen werden kann. Diese muss aber zunächst an Apples Gatekeeper vorbei.


Der Hacker Patrick Wardle hat nach eigenen Angaben eine Sicherheitslücke in der aktuellen Version von Apples Desktop-Betriebssystem High Sierra gefunden, die es bösartigen Applikationen ermöglicht, Passwörter aus Apples Keychain auszulesen. Normalerweise müssen Nutzer einzelne Passwörter durch Eingabe eines Master-Passworts freigeben.


Learn more / En savoir plus / Mehr erfahren:


http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/?&tag=MacOS


No comment yet.
Scooped by Gust MEES
August 31, 2017 4:27 PM
Scoop.it!

Mac malware is spreading at a frightening rate, claims report | #CyberSecurity #Awareness #NobodyIsPerfect

Mac malware is spreading at a frightening rate, claims report | #CyberSecurity #Awareness #NobodyIsPerfect | Apple, Mac, MacOS, iOS4, iPad, iPhone and (in)security... | Scoop.it
Macs are becoming an increasingly big target for malware authors, and a new report has pointed to a massive increase this year in the likes of viruses aimed at Apple’s machines (which were once regarded as relative safe havens in comparison to Windows PCs).

The findings from Malwarebytes show that as of July 2017, there has been a huge leap of 230% in Mac malware compared to the previous year.

Some categories of malicious software are increasing at an even faster rate than this, namely adware and potentially unwanted programs (PUPs) according to the security firm, although it didn’t clarify any percentage rates in these cases.

Malwarebytes also observed that the Mac App Store is currently awash with a ‘tidal wave’ of scam software.

As Betanews reports, the authors of the study looked to the future, predicting that: “In 2018, Mac malware will increase but PUPs will see the largest growth. These are not very well policed and are free to proliferate unchecked.

“Mac users are already experiencing some of this now, with an explosion of fake anti-virus apps in the Mac App Store. These are not well controlled by Apple and not commonly known of even within the security community.”


Learn more / En savoir plus / Mehr erfahren:


http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


Gust MEES's insight:
Macs are becoming an increasingly big target for malware authors, and a new report has pointed to a massive increase this year in the likes of viruses aimed at Apple’s machines (which were once regarded as relative safe havens in comparison to Windows PCs).

The findings from Malwarebytes show that as of July 2017, there has been a huge leap of 230% in Mac malware compared to the previous year.

Some categories of malicious software are increasing at an even faster rate than this, namely adware and potentially unwanted programs (PUPs) according to the security firm, although it didn’t clarify any percentage rates in these cases.

Malwarebytes also observed that the Mac App Store is currently awash with a ‘tidal wave’ of scam software.

As Betanews reports, the authors of the study looked to the future, predicting that: “In 2018, Mac malware will increase but PUPs will see the largest growth. These are not very well policed and are free to proliferate unchecked.

“Mac users are already experiencing some of this now, with an explosion of fake anti-virus apps in the Mac App Store. These are not well controlled by Apple and not commonly known of even within the security community.”


Learn more / En savoir plus / Mehr erfahren:


http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


No comment yet.
Scooped by Gust MEES
July 25, 2017 7:36 AM
Scoop.it!

Fruit Fly 2: Mysteriöse Mac-Malware seit Jahren aktiv | #Apple #CyberSecurity

Fruit Fly 2: Mysteriöse Mac-Malware seit Jahren aktiv | #Apple #CyberSecurity | Apple, Mac, MacOS, iOS4, iPad, iPhone and (in)security... | Scoop.it
Auch Mac-Nutzer sind nicht vor Schadsoftware sicher: Eine Malware soll seit mehr als fünf Jahren aktiv sein, aber nur einige hundert Nutzer befallen haben. Die Software ermöglicht einen weitgehenden Zugriff auf den Rechner und private Informationen.
Mehrere hundert Mac-Nutzer in den USA und Kanda sind offenbar mit einer bislang unbekannten Malware infiziert worden. Diese soll bereits seit mehr als fünf Jahren aktiv sein, wie Motherboard berichtet.


Die Malware sammelt nach Angaben des Sicherheitsforscher Patrick Wardle Informationen wie Tastatureingaben und sendet diese an verschiedene Command-und-Control-Server. Über den Infektionsweg ist bislang nichts bekannt. Details zur Malware will Wardle auf den Sicherheitskonferenzen Black Hat und Defcon bekanntgeben.


Learn more / En savoir plus / Mehr erfahren:


http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/?&tag=Fruitfly


http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


Gust MEES's insight:
Auch Mac-Nutzer sind nicht vor Schadsoftware sicher: Eine Malware soll seit mehr als fünf Jahren aktiv sein, aber nur einige hundert Nutzer befallen haben. Die Software ermöglicht einen weitgehenden Zugriff auf den Rechner und private Informationen.
Mehrere hundert Mac-Nutzer in den USA und Kanda sind offenbar mit einer bislang unbekannten Malware infiziert worden. Diese soll bereits seit mehr als fünf Jahren aktiv sein, wie Motherboard berichtet.


Die Malware sammelt nach Angaben des Sicherheitsforscher Patrick Wardle Informationen wie Tastatureingaben und sendet diese an verschiedene Command-und-Control-Server. Über den Infektionsweg ist bislang nichts bekannt. Details zur Malware will Wardle auf den Sicherheitskonferenzen Black Hat und Defcon bekanntgeben.


Learn more / En savoir plus / Mehr erfahren:


http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/?&tag=Fruitfly


http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


No comment yet.
Scooped by Gust MEES
June 13, 2017 4:35 PM
Scoop.it!

MacOS a aussi son ransomware-as-a-service | #Apple #CyberSecurity 

MacOS a aussi son ransomware-as-a-service | #Apple #CyberSecurity  | Apple, Mac, MacOS, iOS4, iPad, iPhone and (in)security... | Scoop.it
Sécurité : Fortinet publie l’analyse d’un ransomware destiné à viser les utilisateurs de macOS. Mais si celui-ci se distingue par un fonctionnement de type as-a-service, il ne présente pas la même sophistication que ses semblables.


Learn more / En savoir plus / Mehr erfahren:


http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


Gust MEES's insight:
Sécurité : Fortinet publie l’analyse d’un ransomware destiné à viser les utilisateurs de macOS. Mais si celui-ci se distingue par un fonctionnement de type as-a-service, il ne présente pas la même sophistication que ses semblables.


Learn more / En savoir plus / Mehr erfahren:


http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security


No comment yet.
Scooped by Gust MEES
May 17, 2017 9:52 AM
Scoop.it!

Apple fixes dozens of security bugs for iPhones, Macs | #CyberSecurity #Updates

Apple fixes dozens of security bugs for iPhones, Macs | #CyberSecurity #Updates | Apple, Mac, MacOS, iOS4, iPad, iPhone and (in)security... | Scoop.it

Apple has squashed dozens of security bugs in its latest releases of its iPhone, iPad, and Mac operating systems.

The Cupertino, Calif.-based company rolled out 23 security fixes in iOS 10.3.2 and another 30 fixes in macOS 10.12.5, both of which were released on Monday.

Among the bugs, two bugs in iBooks for iOS could allow an attacker to arbitrarily open websites and execute malicious code at the kernel level. Over a dozen flaws were found in WebKit, which renders websites and pages on iPhones and iPads, that could allow several kinds of cross-site scripting (XSS) attacks.

A separate flaw in iBooks for macOS desktops and notebooks could allow an application to escape its secure sandbox, a technology used to prevent data loss or theft in the case of an app compromise.

Almost half of the bugs found were attributed to Google's Project Zero, the search giant's in-house vulnerability-finding and security team.


Learn more / En savoir plus / Mehr erfahren:


http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/?&tag=Updates


http://www.scoop.it/t/securite-pc-et-internet/?&tag=Updates


Gust MEES's insight:
Apple has squashed dozens of security bugs in its latest releases of its iPhone, iPad, and Mac operating systems.

The Cupertino, Calif.-based company rolled out 23 security fixes in iOS 10.3.2 and another 30 fixes in macOS 10.12.5, both of which were released on Monday.

Among the bugs, two bugs in iBooks for iOS could allow an attacker to arbitrarily open websites and execute malicious code at the kernel level. Over a dozen flaws were found in WebKit, which renders websites and pages on iPhones and iPads, that could allow several kinds of cross-site scripting (XSS) attacks.

A separate flaw in iBooks for macOS desktops and notebooks could allow an application to escape its secure sandbox, a technology used to prevent data loss or theft in the case of an app compromise.

Almost half of the bugs found were attributed to Google's Project Zero, the search giant's in-house vulnerability-finding and security team.


Learn more / En savoir plus / Mehr erfahren:


http://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/?&tag=Updates


http://www.scoop.it/t/securite-pc-et-internet/?&tag=Updates


No comment yet.