 Your new post is loading...

|
Scooped by
Gust MEES
June 22, 2019 6:54 AM
|
Des hackers ont exploité deux failles dans Firefox pour installer un porte dérobée sur des Mac. Mozilla a comblé les vulnérabilités avec la version 67.0.4 de Firefox sortie hier. La mise à jour est donc chaudement recommandée à tous les utilisateurs (elle s’applique normalement automatiquement lors d’un redémarrage).
Les hackers ont visé des employés de Coinbase, une plateforme populaire d’achat et de vente de cryptomonnaies. D’après le responsable de la sécurité de Coinbase, l’attaque a été bloquée et aucun utilisateur de la plateforme n’aurait été visé directement. Il ajoute que d’autres plateformes cryptomonnaies ont été la cible d’une attaque identique.
Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security https://www.scoop.it/topic/apple-mac-ios4-ipad-iphone-and-in-security/?&tag=Browsers
|
|
Scooped by
Gust MEES
March 4, 2019 10:30 AM
|
|
|
Scooped by
Gust MEES
December 27, 2018 11:02 AM
|
The FBI has solved the final mystery surrounding a strain of Mac malware that was used by an Ohio man to spy on people for 14 years.
The man, 28-year-old Phillip Durachinsky, was arrested in January 2017, and charged a year later, in January 2018.
US authorities say he created the Fruitfly Mac malware (Quimitchin by some AV vendors) back in 2003 and used it until 2017 to infect victims and take control off their Mac computers to steal files, keyboard strokes, watch victims via the webcam, and listen in on conversations via the microphone.
Court documents reveal Durachinsky wasn't particularly interested in financial crime but was primarily focused on watching victims, having collected millions of images on his computer, including many of underage children. Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/?&tag=Fruitfly
|
|
Scooped by
Gust MEES
December 7, 2018 2:06 PM
|
Earlier this week, we discovered a new piece of Mac malware that is combining two different open-source tools—the EmPyre backdoor and the XMRig cryptominer—for the purpose of evil.
The malware was being distributed through an application named Adobe Zii. Adobe Zii is software that is designed to aid in the piracy of a variety of Adobe applications. In this case, however, the app was called Adobe Zii, but it was definitely not the real thing.
As can be seen from the above screenshots, the actual Adobe Zii software, on the left, uses the Adobe Creative Cloud logo. (After all, if you’re going to write software to help people steal Adobe software, why not steal the logo, too?) The malware installer, however, uses a generic Automator applet icon. Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
|
|
Scooped by
Gust MEES
September 14, 2018 7:22 AM
|
Une nouvelle faille découverte par F-Secure mettrait en danger presque tous les ordinateurs, portables comme de bureau, Mac et Windows, y compris si FileVault est activé.
Selon nos confrères de TechCrunch, la faille du firmware est liée au fait que presque toutes les machines Mac et Windows écrasent les données lorsqu’elles sont désactivées. Cette faille est basée sur une attaque dites « cold boot », où les pirates informatiques tentent de voler des données sur un ordinateur hors tension.
Olle Segerdahl et Pasi Saarinen de F-Secure ont découvert une vulnérabilité au sein du firmware qui permet de désactiver l'effacement des données. Toutefois, les individus malveillant devront avoir un accès physique à la machine convoitée. Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
|
|
Scooped by
Gust MEES
February 19, 2018 1:12 PM
|
Apple has confirmed that it is working on a bug fix that will stop apps like Messages from crashing when they attempt to display a Unicode symbol representing a letter from the south Indian language of Telugu.
The Unicode-based bug has been exploited by juvenile pranksters, who posted app-crashing messages on Twitter, WhatsApp, Instagram, and Facebook, or even changed their screenname to one which contained the symbol.
The symbol, which I won’t repeat here for fear of crashing readers’ apps (trust me.. while writing this article I managed to bork my browser once at twice), can cause iPhones, iPads, Apple Watches and even Apple TV devices to endlessly reboot themselves if received in a notification. If you’re curious there’s a good write-up about it on Mozilla engineer Manish Goregaokar’s blog.
One security researcher demonstrated that it was possible to make macOS network applications crash by creating a Wi-Fi hotspot which included the offending symbol. Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/?&tag=Telugu+Character https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/?&tag=iOS https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
|
|
Scooped by
Gust MEES
January 8, 2018 6:30 PM
|
If you own any Apple products, you're going to want to make sure you have the latest updates installed.
Apple just released two incredibly important security updates for iOS and MacOS, which address the massive Spectre vulnerability Apple previously said affects all Macs and iPhones.
SEE ALSO: Apple on Meltdown and Spectre bugs: 'All Mac systems and iOS devices are affected'
The updates, 11.2.2 for iOS and 10.13.2 for macOS High Sierra, are available now for iPhones, iPads, and Macs.
Spectre was one of two major CPU vulnerabilities revealed by security researchers last week that affects devices with processors from major chip makers, including Intel, AMD, and ARM. Apple previously released software updates to address the other flaw, Meltdown.
While it's always a good idea to keep your software up to date, these latest updates are especially important. As security researchers have warned, the Meltdown and Spectre bugs are particularly nasty. So even if you're the type to wait days, or even weeks, to update to the latest software, you really shouldn't waste any time with these updates.
Google and Microsoft also previously released software updates to address the issue. Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/t/securite-pc-et-internet/?&tag=Meltdown+and+Spectre+Attacks https://gustmeesde.wordpress.com/2014/12/26/programme-die-auf-jeden-neuen-pc-und-smartphones-gehoren/ https://gustmeesde.wordpress.com/2014/12/16/browser-sind-das-einfallstor-fur-malware-sind-eure-browser-up-to-date/
|
|
Scooped by
Gust MEES
January 4, 2018 8:09 PM
|
05.01.2018 - 01:50 Uhr
Durch eine massive Sicherheitslücke in den Computerchips von Milliarden Geräten können auf breiter Front vertrauliche Daten abgeschöpft werden.
Jetzt hat Apple bestätigt, dass auch „alle Mac-Systeme und iOS-Geräte betroffen sind“. Im Klartext: Jeder Apple-Computer, jedes iPhone und jedes iPad könnte von Hackern angegriffen werden. Bislang seien aber keine solche Attacken bekannt, erklärt Apple in einem Hilfe-Dokument.
Was müssen Besitzer von Apple-Geräten wissen?
Nach Angaben des Unternehmens wurde eines der beiden möglichen Angriffsszenarien („Meltdown“) bereits mit Aktualisierungen seiner Betriebssysteme abgestellt. Auf Geräten, die mit iOS 11.2, MacOS 10.13.2 bzw. tvOS 11.2 arbeiten, soll diese Angriffsmöglichkeit nicht mehr möglich sein.
Mit einem Update für den Internet-Browser Safari solle in den nächsten Tagen auch das Angriffsszenario „Spectre“ verhindert werden. Die Apple Watch ist laut Apple nicht von der Sicherheitslücke betroffen, benötigt daher keine Aktualisierung.
Apple empfiehlt außerdem dringend, Apps oder Programme ausschließlich aus sicheren Quellen wie dem eigenen App-Store zu laden. Andernfalls laufe man Gefahr, gefährliche Spionagesoftware aufs eigene Gerät zu holen. Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/t/securite-pc-et-internet/?&tag=Meltdown+and+Spectre+Attacks https://gustmeesde.wordpress.com/2014/12/26/programme-die-auf-jeden-neuen-pc-und-smartphones-gehoren/ https://gustmeesde.wordpress.com/2014/12/16/browser-sind-das-einfallstor-fur-malware-sind-eure-browser-up-to-date/
|
|
Scooped by
Gust MEES
December 7, 2017 5:08 PM
|
Dans la foulée de macOS 10.13.2, Apple livre aussi des mises à jour de sécurité pour macOS Sierra et OS X El Capitan. Elles contiennent les mêmes correctifs que la toute dernière mouture de High Sierra bien évidemment.
Avec macOS 10.13.2, Safari passe en version 11.0.2 pour High Sierra bien sûr, mais aussi pour Sierra (10.12.6) et El Capitan (10.11.6). Ces mises à jour sont à récupérer depuis le Mac App Store.
Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
|
|
Scooped by
Gust MEES
November 30, 2017 10:32 AM
|
The patch that Apple rushed out yesterday to fix the root access flaw in macOS brings with it problems of its own. Fortunately, this new bug is quite easy to fix. The patch that Apple released to fix the "root" security flaw discovered in the latest release of macOS High Sierra is causing problems for some users. Must read: How strong are iPhone X sales? The patch - which Apple rushed out in less than 24 hours - can cause file sharing to stop working for some users, according to a support document published by Apple. The fix itself is pretty straightforward, although does require users to be familiar with using Terminal: - Open the Terminal app (which is in the Utilities folder of the Applications folder)
- Type sudo /usr/libexec/configureLocalKDC and press Return
- Enter your administrator password when requested and press Return
- Quit the Terminal app
Note that this fix is only for the file sharing bug caused by Security Update 2017-001 for macOS High Sierra 10.13.1. If you're running a different version, this patch isn't for you. It's likely that Apple will push a patch for this bug as part of the macOS High Sierra 10.13.2 update. Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
|
|
Scooped by
Gust MEES
November 29, 2017 12:58 PM
|
At first, the Twitter user who publicised this flaw was criticised by some people, who considered his tweet to be “irresponsible disclosure”, because it told the world about a problem that it might have been better to tell Apple about privately first so the hole could be closed and then announced.
But others soon realised that this was not a brand new discovery – indeed, it had been discussed more than two weeks ago on Apple’s on support forum.
Apple’s official policy of saying nothing about security issues until a fix is out meant that there wasn’t much to go on once the news broke, except to assume that the company was frantically coding up a fix…
…and, fortunately that turns out to have been true. Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
|
|
Scooped by
Gust MEES
November 29, 2017 10:55 AM
|
Das Bundesamt für Sicherheit in der Informationstechnik (BSI) warnt vor einer schwerwiegenden Sicherheitslücke im Apple-Betriebssystem macOS 10.13 (High Sierra), die es ermöglicht, sich ohne die Eingabe eines Passwortes mit vollen administrativen Rechten auf diesem System anzumelden.
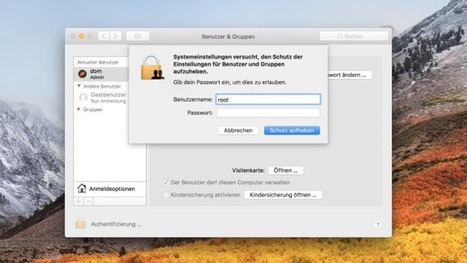
Bei betroffenen Computern können mit dem Nutzernamen "root" und einer leeren Passwortzeile Sicherheitseinstellungen überwunden werden, indem mehrfach auf "Schutz aufheben" geklickt wird. Anschließend kann sich der Angreifer ohne die Eingabe eines Passwortes als Benutzer "root" mit vollen administrativen Rechten auf diesem System anmelden. Dieser Vorgang ist unter bestimmten Voraussetzungen über das Apple-eigene Remote Access Tool auch ohne physischen Zugriff auf das Gerät möglich. Andere Wege zur Ausnutzung dieser Schwachstelle sind denkbar.
Das Bundesamt für Sicherheit in der Informationstechnik (BSI) empfiehlt die explizite Vergabe eines starken Passworts für den Root-Account betroffener Apple-Computer. Daneben sollten auch passwortgeschützte Apple-Computer nicht unbeaufsichtigt gelassen werden.
Apple hat bekanntgegeben, in Kürze ein Sicherheitsupdate zur Verfügung stellen zu wollen. Sobald das Update veröffentlicht ist, sollten Anwender es einspielen.
Dazu sagt BSI-Präsident Arne Schönbohm: "Der vorliegende Fall macht einmal mehr deutlich, dass Software-Qualität ein entscheidender Faktor für die Informationssicherheit ist. Betroffene Anwender sollten sich nun aktuell informieren und ihren Apple-Rechner mit den empfohlenen Maßnahmen absichern." Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
|
|
Scooped by
Gust MEES
November 29, 2017 5:21 AM
|
In der aktuellen macOS-Version High Sierra steckt eine Sicherheitslücke, die Beobachter sprachlos macht: Mit wenigen Klicks können Angreifer sich root-Rechte verschaffen - weil Apple dafür kein Passwort verlangt.
Schon vor einigen Wochen fiel macOS High Sierra, die aktuelle Version des Apple-Betriebssystems, durch einen abstrusen Bug auf: Das Passwort verschlüsselter Festplatten kopierte das Betriebssystem kurzerhand in den Passwort-Hinweis und machte es damit für jeden sichtbar. Wer damals dachte, viel schlimmer kann es nicht kommen, hat sich getäuscht: In einer jetzt entdeckten Sicherheitslücke verlangt Apple an kritischen Punkten einfach überhaupt kein Passwort mehr. Angreifer können sich mit wenigen Klicks vollen Zugriff auf den Computer sichern.
Öffentlich wurde der eklatante Bug durch einen Tweet. Der Entwickler Lemi Orhan Ergin beschreibt darin das Vorgehen, mit dem sich Dritte auf einem Mac root-Rechte verschaffen können, ohne dafür ein Passwort zu benötigen. Mit diesen Rechten ist es möglich, den Mac vollständig zu übernehmen.
Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
|
|
|
Scooped by
Gust MEES
June 21, 2019 6:21 PM
|
Before either of those patches rolled out, Mozilla became aware of an attack leveraging both vulnerabilities. At the time, we only knew the attacks had something to do with Coinbase as the initial bug report came from a researcher who works on both Google’s Project Zero and the Coinbase security team. Now, Coinbase’s head of security Philip Martin says the attack was aimed at Coinbase employees and not users. Martin also notes that other exchanges were targeted in the attacks, although none have stepped forward.
Meanwhile, Apple security expert Patrick Wardle published an analysis of malware that appears to have installed itself on a fully updated Mac. The hash provided by Wardle matches one from Martin, and the victim of the attack was involved with a cryptocurrency exchange until very recently. Unfortunately, the malware is novel and avoided Apple’s protection mechanisms, but Wardle believes that Apple will have a patch to change the way macOS scans files downloaded by applications rather than the user. Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security https://www.scoop.it/topic/apple-mac-ios4-ipad-iphone-and-in-security/?&tag=Browsers
|
|
Scooped by
Gust MEES
March 4, 2019 10:21 AM
|
|
|
Scooped by
Gust MEES
December 13, 2018 10:30 AM
|
Un malware qui vise les MAC OS s’invite pour la première fois dans le Top 10 des malwares détectés au 3ème trimestre de l’année 2018
décembre 2018 par WatchGuard® Technologies
WatchGuard® Technologies publie son Rapport sur la Sécurité Internet pour le troisième trimestre 2018. Pour la première fois au cours de ce trimestre, un malware visant spécifiquement les MAC OS a fait partie de la liste des dix malwares les plus couramment détectés par WatchGuard. Le rapport a également révélé que 6,8% des 100 000 sites web générant le plus de trafic dans le monde acceptent toujours des versions obsolètes et non sécurisées du protocole de chiffrement SSL. En outre, WatchGuard a enregistré plus d’attaques de malwares dans la zone Asie-Pacifique que dans toute autre région du monde, indiquant un accroissement significatif du nombre de malwares ciblant cette zone en 2018. Le rapport WatchGuard est basé sur des données récoltées par des dizaines de milliers de boîtiers UTM WatchGuard Firebox actifs à travers le monde, et analyse les campagnes de malware majeures, les attaques réseau et les menaces de sécurité ciblant les PME et les entreprises dites distribuées. Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
|
|
Rescooped by
Gust MEES
from 21st Century Learning and Teaching
September 25, 2018 9:15 AM
|
Les contrôles d’accès censés protéger les données personnelles comme le carnet d’adresses peuvent être contournés, comme vient de le démontrer un chercheur en sécurité.
Depuis hier, 24 septembre, les utilisateurs d’ordinateurs Mac peuvent installer la dernière version du système d’exploitation macOS Mojave. Malheureusement, celle-ci est déjà impacté par une importante faille de sécurité qui met à mal la protection des données personnelles. Avec macOS Mojave, Apple a en effet musclé les contrôles d’accès aux fichiers et aux applications sensibles tels que le carnet d’adresses, l’historique des messages, la base de données d’email, le microphone, la caméra, etc. Mais ces contrôles d’accès peuvent être court-circuités, comme le démontre le chercheur en sécurité Patrick Wardle.
Cet expert a développé une application baptisée « breakMojave » capable de siphonner en douce le carnet d’adresses de l’utilisateur sans rien lui demander. Il a montré le déroulement du hack dans une vidéo Vimeo. Au départ, on constate qu’aucune application tierce n’a accès au carnet d’adresses. Le chercheur ouvre ensuite une fenêtre Terminal et tente d’accéder directement aux données du carnet d’adresses, sans succès. Le lancement de breakMojave provoque enfin l’extraction des données, qui se retrouvent copiées en vrac sur le bureau. Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
|
|
Scooped by
Gust MEES
March 13, 2018 2:57 PM
|
Déjà quatre nouveaux malwares identifiés en 2018 sur Mac
Malwarebytes dévoile en outre que pas moins de quatre nouveaux malwares ont été identifiés depuis le début de l'année 2018. L'un d'entre eux a été identifié par un utilisateur dont les DNS ont été changés à son insu et qui s'est retrouvé dans l'impossibilité de les remettre à zéro : OSX.MaMi. Outre le changement de DNS, le malware avait également installé un nouveau certificat de sécurité.
Un autre malware serait issu des outils développés par le Liban dans le cadre de l'opération d'espionnage d'Etat DarkCaracal. Ce malware ne serait toutefois qu'en phase de développement, la version identifiée étant la 0.1, d'après Malwarebytes. Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
|
|
Scooped by
Gust MEES
January 13, 2018 7:08 AM
|
US authorities have charged a 28-year-old Ohio man who is alleged to have created and installed creepy spyware on thousands of computers for 13 years.
Phillip R. Durachinsky, of North Royalton, Ohio, is alleged to have used Mac malware known as “Fruitfly” to remotely control victims’ computers, access and upload files, grab screenshots, log keystrokes, and surreptitiously spy via infected computer’s webcams.
Durachinsky, who faces multiple charges including Computer Fraud and Abuse Act violations, Wiretap Act violations, and identify theft, is said to have created a visual interface that allowed him to retrieve live images from several infected computers simultaneously.
In the indictment, Durachinsky is said to have used malware he created between 2003 and January 2017 to steal personal data, tax records, passwords, and “potentially embarrassing communications.”
According to the indictment, Durachinsky used stolen usernames and passwords to hack into his victims’ online accounts and steal further information, keeping detailed notes on his victims. Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/?&tag=Fruitfly
|
|
Scooped by
Gust MEES
January 8, 2018 12:27 PM
|
Apple has issued a statement regarding the Meltdown and Spectre vulnerabilities, confirming all Mac systems and iOS devices are affected, but saying there are no known exploits impacting customers at this time.
The iPhone maker has already released mitigations in iOS 11.2, macOS 10.13.2, and tvOS 11.2 to help defend against Meltdown. A spokesperson confirmed Friday that Apple Watch is not affected by either Meltdown or Spectre, despite its own initial report Thursday.
"In the coming days we plan to release mitigations in Safari to help defend against Spectre," the company said in a statement. "We continue to develop and test further mitigations within the operating system for the Spectre techniques, and will release them in upcoming updates of iOS, macOS, and tvOS." Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/t/securite-pc-et-internet/?&tag=Meltdown+and+Spectre+Attacks https://gustmeesde.wordpress.com/2014/12/26/programme-die-auf-jeden-neuen-pc-und-smartphones-gehoren/ https://gustmeesde.wordpress.com/2014/12/16/browser-sind-das-einfallstor-fur-malware-sind-eure-browser-up-to-date/
|
|
Scooped by
Gust MEES
December 17, 2017 4:46 PM
|
New MacOS malware steals bank log-in details and intellectual property.
Security researchers have discovered a new, invasive OSX.Pirrit adware variant targeting Mac OS X that enables cyber-criminals to take full control of a user's Mac computer.
The malware has already infected thousands of Mac computers around the world. According to a blog post by Amit Serper, principal security researcher at Cybereason, while usual adware campaigns enable the attackers to flood a person's computer with ads, this malware not only bombards Macs with adware, it spies on users and runs with the highest user privileges, enabling hackers to leverage this adware to capture personal information on the users, including bank account logins and intellectual property of businesses.
“To my surprise, it's very active. Not only is it still infecting people's Macs, OSX.Pirrit's authors learned from one of their mistakes (They obviously read at least one of our earlier reports),” said Serper.
He added that unlike old versions of OSX.Pirrit that used rogue browser plug-ins or even installed a proxy server on the victim's machine to hijack the browser, this incarnation uses AppleScript, Apple's scripting/automation language.
Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security/?&tag=Malware https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
|
|
Scooped by
Gust MEES
December 2, 2017 4:03 PM
|
In den ersten drei Quartalen des Jahres 2017 stieg die Zahl der Malware-Angriffe auf Macs um über 70 % und die PUA (potenziell unerwünschte Anwendungen wie z.B. Adware) um 50 % gegenüber dem Vorjahr (Quelle: F-Secure Labs). Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
|
|
Scooped by
Gust MEES
November 30, 2017 9:18 AM
|
Die von Apple schnell ausgelieferte Aktualisierung für macOS 10.13 kann die Dateifreigabe lahmlegen. Inzwischen hat der Mac-Hersteller bei dem Sicherheits-Update nochmals nachgebessert – das File-Sharing-Problem aber offenbar nicht ausgeräumt.
Das wichtige Sicherheits-Update 2017-001 für macOS High Sierra führt unter Umständen zu Problemen bei der Dateifreigabe: Nach der Installation des Updates, das Apple inzwischen auch automatisch einspielt, funktioniert der entfernte Zugriff auf die per File Sharing geteilten Verzeichnisse des Macs nicht länger, wie Nutzer berichten.
Workaround bei Dateifreigabe-Problem in High Sierra
Apple ist der Fehler bekannt, das Unternehmen hat bereits einen manuellen Workaround veröffentlicht: Nutzer sollen im Terminal
sudo /usr/libexec/configureLocalKDC
eingeben und den Befehl ausführen, so Apple – dafür ist die Eingabe des Admin-Passwortes vonnöten. Dies repariere die Dateifreigabe.
Apple bessert bei Sicherheits-Update nach
Offenbar hat Apple bei dem Security-Update 2017-001 inzwischen nachgebessert und – ohne weiteren Hinweis – eine neue Fassung veröffentlicht, die nun auch für macOS 10.13.0 gedacht ist. Zuvor wurde noch macOS 10.13.1 vorausgesetzt. Nach der Installation zeigt die Neufassung die Build-Nummer 17B1003, bei der ersten Version war es noch 17B1002. Die neue Fassung scheint aber ein für Unterstützung der ersten öffentlichen High-Sierra-Version zu sorgen, das Dateifreigabenproblem kann offenbar weiterhin auftreten.
Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
|
|
Scooped by
Gust MEES
November 29, 2017 12:51 PM
|
Apple released a security update Wednesday to fix a major bug that allowed anyone to bypass security protocols and act as a computer's administrator.
"Security is a top priority for every Apple product, and regrettably we stumbled with this release of macOS," a spokesperson for Apple said in a statement. "When our security engineers became aware of the issue Tuesday afternoon, we immediately began working on an update that closes the security hole."
The security issue impacted macOS High Sierra 10.13.1. Apple says the update is now available for download and will be rolled out automatically to all systems running the affected software.
On Tuesday, developers noticed that someone with access to a Mac computer running Apple's most recent Mac software could type "root" and no password in the Users & Groups section of System Preferences and gain administrator-level access to the computer.
Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
|
|
Scooped by
Gust MEES
November 29, 2017 7:34 AM
|
Une incroyable faille de sécurité permet d'accéder à un appareil sous macOS High Sierra sans le moindre effort en rentrant simplement le nom d'utilisateur "root".
Une énorme faille de sécurité permet de pénétrer dans d’importe quel appareil sous macOS High Sierra et cela sans le moindre effort. La démarche est on ne peut plus simple. Lorsque le système d’exploitation demande une autorisation d’accès avec un mot de passe et un identifiant, il suffit de rentrer le nom d’utilisateur « root » puis de cliquer plusieurs fois sur le bouton d'accès et comme par magie la machine accepte l'opération.
Cette faille a été découverte Lemi Orhan Ergin, le fondateur de Software Craftsmanship Turkey. Il a tweeté l’information à Apple qui travaille déjà sur un correctif. Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
|

















Des hackers ont exploité deux failles dans Firefox pour installer un porte dérobée sur des Mac. Mozilla a comblé les vulnérabilités avec la version 67.0.4 de Firefox sortie hier. La mise à jour est donc chaudement recommandée à tous les utilisateurs (elle s’applique normalement automatiquement lors d’un redémarrage).
Les hackers ont visé des employés de Coinbase, une plateforme populaire d’achat et de vente de cryptomonnaies. D’après le responsable de la sécurité de Coinbase, l’attaque a été bloquée et aucun utilisateur de la plateforme n’aurait été visé directement. Il ajoute que d’autres plateformes cryptomonnaies ont été la cible d’une attaque identique.
Learn more / En savoir plus / Mehr erfahren:
https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
https://www.scoop.it/topic/apple-mac-ios4-ipad-iphone-and-in-security/?&tag=Browsers