 Your new post is loading...

|
Scooped by
Gust MEES
August 6, 4:09 PM
|
Researchers at Huntress have uncovered a strain of macOS malware that can gradually siphon funds out of victims’ cryptocurrency wallets, after tracing an infection back to a fake CAPTCHA scam known as ClickFix.
The incident came to light during a retrospective threat hunt in June 2026, when a Huntress analyst discovered remnants of a Mac-specific stealer on a system that had actually been compromised three months earlier. The victim had been served a pop-up disguised as a routine CAPTCHA check, instructing them to copy a command and paste it into the Mac Terminal application – a social engineering technique the security vendor says has surged in popularity in recent years. Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
|
|
Scooped by
Gust MEES
February 12, 2024 10:57 AM
|
|
|
Scooped by
Gust MEES
September 5, 2022 10:13 AM
|
|
|
Scooped by
Gust MEES
February 11, 2022 5:08 PM
|
Here on Naked Security, we’ve been lamenting the mysterious nature of Apple’s security updates for ages.
For example, even when widely-known security problems appear in components that are part of Apple’s operating system, Apple routinely refuses to say when, or even if, it plans to address the issues itself. Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
|
|
Scooped by
Gust MEES
April 26, 2021 5:51 PM
|
Apple Mac users are being urged to update their macOS software now, as they’re at “grave risk” of hackers exploiting what’s been described as one of the worst vulnerabilities to affect the tech giant’s computers in years in years. Malware that takes advantage of the bug has been hitting Macs since at least January, making patching all the more urgent. Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
|
|
Scooped by
Gust MEES
March 9, 2021 6:34 PM
|
Pour combler une faille qui permettait à un pirate de prendre le contrôle de votre appareil à distance via une page Web, Apple vient de publier un correctif pour iOS et iPadOS (14.4.1), macOS (11.2.3), watchOS (7.3.2), ainsi que pour son navigateur Web, Safari (14.0.3). Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
|
|
Scooped by
Gust MEES
April 6, 2020 7:42 PM
|
The vulnerabilities were identified in the Webkit browser engine and Safari. When combined together, the flaws would let infected websites to activate cameras on iPhone, iPad, and Mac.
Eventually, Pickern hijacked the iPhone’s camera and notified Apple product security team about it. The company patched the flaws in January and rewarded Pickern with a handsome amount.
See: Vulnerability in Zoom video conference app lets Mac’s camera hijacking
As for Apple’s Security Bounty Program; launched in December last year, the program offers white hack hackers and security research some big bucks. You can also become a part of it. More information on the Security Bounty Program is available here. Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
|
|
Scooped by
Gust MEES
February 13, 2020 9:35 AM
|
Die US-amerikanische Sicherheitsfirma Malwarebytes hat ihrem jährlichen Report zum Status von Malware-Angriffen rund um den Globus veröffentlicht. Demnach wurden erstmalig Macs öfter das Ziel von Angriffen als Windows-PCs. Allerdings unterscheiden sich die Arten von Angriffen.
Die Studie konnte eine Steigerung von 400 Prozent in der Gesamtanzahl von Angriffen auf Macs feststellen. Da sich gleichzeitig die Nutzerbasis auf Mac-System erhöht hat, ist die relevantere Angabe die entdeckten Angriffe pro Endpunkt. Das waren 4,8 in 2018, in 2019 ganze 11,0. Eine Steigerung von mehr als 100 Prozent. Zum Vergleich: Windows-Systeme entdeckten durchschnittlich 5,8 Angriffe in 2019. Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security https://www.scoop.it/topic/apple-mac-ios4-ipad-iphone-and-in-security/?&tag=Mac
|
|
Scooped by
Gust MEES
January 28, 2020 6:06 PM
|
|
|
Scooped by
Gust MEES
October 29, 2019 9:00 PM
|
|
|
Scooped by
Gust MEES
August 12, 2019 11:42 AM
|
For the majority of users, the security offered by iOS and macOS is more than enough, and they can go about their day-to-day business secure in the knowledge that their data is safe.
But determined criminals can find a way around these safeguards, and while these two hacks are impractical for widespread use, they go to show just how creative ne'er-do-wells can be when it comes to cracking security measures.
Must read: The 2019 iPhone 11 will be annoying, boring, and expensive
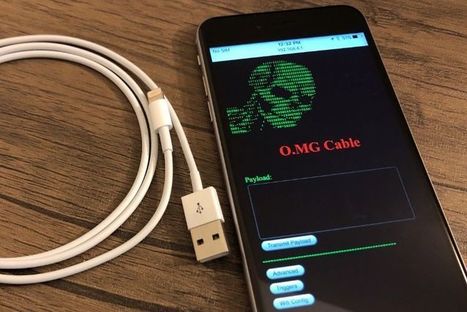
First, let's look at how a cable can be used to hack a Mac. Enter the O.MG Cable. This is an Apple Lightning charging cable with a twist. That twist is that it has been custom-modified with electronics that allow it to be used to access any Mac it has been connected to over a Wi-Fi network. Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/topic/apple-mac-ios4-ipad-iphone-and-in-security
|
|
Scooped by
Gust MEES
August 12, 2019 9:44 AM
|
"Ich wollte zeigen, dass es nicht allzu schwierig ist", sagt Wardle später im Gespräch mit dem SPIEGEL, "was bedeutet, dass es wahrscheinlich häufiger passiert, als wir denken."
Schon immer störte sich Wardle an "dieser Mentalität, dass Macs sicher sind, geradezu unhackbar". Apple selbst habe das so dargestellt, und weil es lange Zeit nur wenig Mac-spezifische Malware gab, hätten es die Nutzer geglaubt. Manche tun es seiner Ansicht nach bis heute. Er will mit diesem Mythos aufräumen, denn die Zeiten haben sich geändert.
"Traditionell war Windows leichter zu hacken", sagt er. "Aber heute ist Windows viel sicherer als macOS - auch wenn sich das Sicherheitsniveau in den vergangenen Jahren insgesamt deutlich erhöht hat. Ein Windows-10-Gerät mit Defender ist eine wirklich harte Nuss für Hacker. Im Vergleich dazu ist macOS ein ziemlich leichtes Ziel." Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/topic/apple-mac-ios4-ipad-iphone-and-in-security
|
|
Scooped by
Gust MEES
July 9, 2019 6:25 AM
|
|
|
|
Scooped by
Gust MEES
November 19, 2024 4:28 PM
|
Apple rushes out out major macOS and iOS security updates to cover a pair of vulnerabilities already being exploited in the wild.
|
|
Scooped by
Gust MEES
December 25, 2022 11:14 AM
|
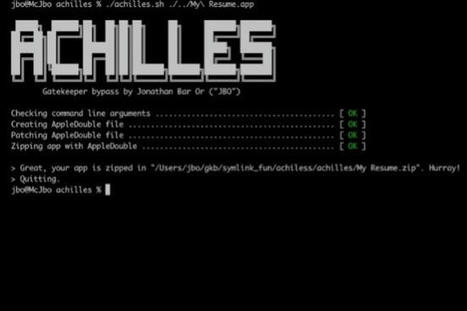
La vulnérabilité Achilles, découverte par Microsoft, a été comblée par Apple dans les récentes mises à jour de macOS Ventura, Monterey et Big Sur.
Enregistrée dans la National Vulnerability Database sous la référence CVE-2022-42821, la faille Achilles a été découverte par Microsoft en juillet dernier. (crédit : Microsoft)
Ceux qui n’ont pas mis à jour leur ordinateur Mac avec la dernière version de Ventura, Monterey ou Big Sur, devraient se dépêcher de le faire. En effet, un méchant bug découvert par Microsoft et corrigé dans les mises à jour livrées par Apple la semaine dernière pourrait être utilisé par un attaquant pour contourner les protections de sécurité strictes du constructeur et installer des logiciels malveillants sur les ordinateurs Mac.
Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
|
|
Scooped by
Gust MEES
March 15, 2022 2:28 PM
|
The latest raft of non-emergency Apple security updates are out, patching a total of 87 different CVE-rated software bugs across all Apple products and plaforms.
There are 10 security bulletins for this bunch of updates, as follows:
APPLE-SA-2022-03-14-1: iOS 15.4 and iPadOS 15.4 (HT213182)
APPLE-SA-2022-03-14-2: watchOS 8.5 (HT213193)
APPLE-SA-2022-03-14-3: tvOS 15.4 (HT213186)
APPLE-SA-2022-03-14-4: macOS Monterey 12.3 (HT213183)
APPLE-SA-2022-03-14-5: macOS Big Sur 11.6.5 (HT213184)
APPLE-SA-2022-03-14-6: Security Update 2022-003 Catalina (HT213185)
APPLE-SA-2022-03-14-7: Xcode 13.3 (HT213189)
APPLE-SA-2022-03-14-8: Logic Pro X 10.7.3 (HT213190)
APPLE-SA-2022-03-14-9: GarageBand 10.4.6 (HT213191)
APPLE-SA-2022-03-14-10: iTunes 12.12.3 for Windows (HT213188) Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
|
|
Scooped by
Gust MEES
July 27, 2021 11:56 AM
|
You might be forgiven for thinking that July 2021 was Microsoft’s month for cybersecurity vulnerabilities.
First there was PrintNightmare in several guises, followed by HiveNightmare (an entirely unrelated bug that nevertheless attracted the “Nightmare” moniker), followed by PetitPotam (which went down the cute aquatic mammal naming path).
Now, however, it’s Apple’s turn to be in the patch-right-now spotlight, with a somewhat under-announced emergency zero-day fix, just a few days after the company’s last, and much broader, security update.
This one doesn’t have a fancy name, but instead goes simply by CVE-2021-30807, and was reported, according to Apple “by an anonymous researcher”.
Indeed, all we know about it, and all Apple has said so far, is that:
An application may be able to execute arbitrary code with kernel privileges. Apple is aware of a report that this issue may have been actively exploited. Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
|
|
Scooped by
Gust MEES
April 26, 2021 5:48 PM
|
The latest version of Apple's macOS comes with more than just a slew of fancy new features.
Buried inside macOS 11.3, which was released Monday morning, is a patch that fixes a critical vulnerability that was actively being exploited. This means that, yes, hackers or criminals or governments around the world were using this previously unreported bug for their own malicious ends.
That's according to Patrick Wardle, creator of the Mac security website and tool suite Objective-See. In a blog post timed to coincide with the release of macOS 11.3, Wardle explains just how serious the now-patched vulnerability is.
"This bug trivially bypasses many core Apple security mechanisms, leaving Mac users at grave risk," he writes.
Worryingly, Wardle and Jamf, a company that makes Apple management software for enterprise customers, were able to detect real malware exploiting this bug in the wild.
We reached out to Apple to both confirm Wardle's report and that macOS 11.3 contains a patch for this specific vulnerability. An Apple spokesperson confirmed that the latest version of macOS does include a fix for the underlying issues. Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
|
|
Scooped by
Gust MEES
August 15, 2020 7:00 AM
|
Xcode projects are being exploited to spread a form of Mac malware specializing in the compromise of Safari and other browsers.
The XCSSET malware family has been found in Xcode projects, "lead[ing] to a rabbit hole of malicious payloads," Trend Micro said on Thursday.
In a paper (.PDF) exploring the wave of attacks, cybersecurity researchers said an "unusual" infection in a developer's project also included the discovery of two zero-day vulnerabilities. Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security
|
|
Scooped by
Gust MEES
February 16, 2020 7:36 AM
|
The Mac vs. PC debate isn't nearly as intense as it was earlier in the 21st century, but a new malware report could stoke the flames a little bit for the first time in years.
Antivirus company Malwarebytes released a big ol' report about the prevalence of different types of malware across different operating systems this week. There's plenty to chew on, but the most eye-catching finding is that, for the first time anyone can remember, Macs are more susceptible to malware than Windows PCs.
Malwarebytes measured the average number of threats detected per endpoint, which basically means "device" in this context. In 2018, Macs only averaged 4.8 threats per endpoint, but that number ballooned to 11 in 2019. Windows devices, by comparison, only saw 5.8 threats per endpoint last year. Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security https://www.scoop.it/topic/apple-mac-ios4-ipad-iphone-and-in-security/?&tag=Mac
|
|
Scooped by
Gust MEES
February 13, 2020 5:38 AM
|
Selon un rapport de la solution de sécurité Malwarebytes, les ordinateurs de la marque Apple auraient été victimes de deux fois plus d'infections que les PC Windows en 2019.
Malwarebytes, l'éditeur du logiciel éponyme qui permet de supprimer les logiciels malveillants, vient de publier un rapport sur le niveau de menace actuel des malwares en tous genres. Grâce aux statistiques collectées par la protection en temps réel, la firme a pu analyser les infections détectées pour l'année 2019 partout dans le monde.
La grande surprise de ce rapport concerne les Mac. Alors que les ordinateurs d'Apple sont généralement perçus comme étant plus sûrs que les PC équipés de Windows, les chiffres montrent une tout autre réalité. En 2019, Malwarebytes a détecté en moyenne 11 infections par appareil pour les Mac, largement plus que les 5,8 infections par appareil pour Windows. Ce chiffre a plus que doublé par rapport à 2018, où le logiciel comptait 4,8 infections pour chaque Mac. Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security https://www.scoop.it/topic/apple-mac-ios4-ipad-iphone-and-in-security/?&tag=Mac
|
|
Scooped by
Gust MEES
January 23, 2020 2:33 PM
|
|
|
Scooped by
Gust MEES
August 13, 2019 6:55 AM
|
Quoi de plus banal et innocent qu'un câble Lightning ? Regardez-le ce petit câble, on lui donnerait le bon dieu sans confession. Mais gare ! Derrière cet air angélique se cache peut-être un démon capable de hacker votre Mac ! Le chercheur en sécurité et bidouilleur de génie MG a mis au point un implant qui, au terme d'une petite opération chirurgicale, s'intègre dans des câbles Apple légitimes.
Une fois le bricolage terminé, ils deviennent des O.MG Cable, sans toutefois se démarquer dans leur design. Lorsque la victime le branche à son Mac, il fonctionne comme un câble Lightning tout ce qu'il y a de plus standard : on peut y recharger un iPhone, transférer des données avec iTunes, etc.
Mais en douce, l'implant créé un réseau Wi-Fi auquel le malandrin peut se connecter : après avoir entré une adresse IP, le navigateur du vaurien peut lancer à distance des commandes dans le Terminal du Mac… et faire à peu près n'importe quoi. Il y a même un « kill switch » permettant de désactiver l'implant une fois le forfait accompli. Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/topic/apple-mac-ios4-ipad-iphone-and-in-security https://www.scoop.it/topic/apple-mac-ios4-ipad-iphone-and-in-security/?&tag=O.MG
|
|
Scooped by
Gust MEES
August 12, 2019 10:27 AM
|
|
|
Scooped by
Gust MEES
July 10, 2019 2:55 PM
|
Zoom, l’éditeur de l’application de visioconférence pour macOS, a déployé en urgence un correctif après qu’un chercheur en sécurité ait dévoilé l’existence d’une faille de sécurité pouvant permettre à des sites Web de lancer un chat vidéo Zoom depuis un Mac sans la permission de son propriétaire. Dans le cadre de son correctif, Zoom supprimera complètement le serveur web local créé sur les Mac.
Jonathan Leitschuh, le chercheur à l’origine de cette découverte, a indiqué qu’il avait également pu activer des webcams Mac sans autorisation.
L’éditeur ajoutera une option à la barre de menu de son application qui permet aux utilisateurs de désinstaller manuellement le client Zoom, y compris le serveur Web installé localement. Une fois le correctif déployé, les utilisateurs verront une option « Désinstaller Zoom », qui supprimera complètement logiciel et les paramètres enregistrés. Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security https://www.scoop.it/topic/apple-mac-ios4-ipad-iphone-and-in-security/?&tag=Zoom
|



















Researchers at Huntress have uncovered a strain of macOS malware that can gradually siphon funds out of victims’ cryptocurrency wallets, after tracing an infection back to a fake CAPTCHA scam known as ClickFix.
The incident came to light during a retrospective threat hunt in June 2026, when a Huntress analyst discovered remnants of a Mac-specific stealer on a system that had actually been compromised three months earlier. The victim had been served a pop-up disguised as a routine CAPTCHA check, instructing them to copy a command and paste it into the Mac Terminal application – a social engineering technique the security vendor says has surged in popularity in recent years.
Learn more / En savoir plus / Mehr erfahren:
https://www.scoop.it/t/apple-mac-ios4-ipad-iphone-and-in-security