

Plus: Alleged Apple source code leaks online, cybercrime group Scattered Spider's alleged kingpin gets arrested, and more.


 Your new post is loading...
 Scoop.it! Plus: Alleged Apple source code leaks online, cybercrime group Scattered Spider's alleged kingpin gets arrested, and more. 
No comment yet.
Sign up to comment
Scoop.it!
The company’s annual developer event was stacked with demonstrations that showed off the new artificial intelligence capabilities coming to iPhones, iPads, and Macs.
Scoop.it!

Security experts investigating a major cyber attack on an NHS partner that has caused frontline services across South London to grind to a halt say that the Qilin ransomware gang appears to be the culprit
Scoop.it!
Plus: A whistleblower claims the Biden administration falsified a report on Gaza, “Operation Endgame” disrupts the botnet ecosystem, and more.
Scoop.it!

The US says a Chinese national operated the “911 S5” botnet, which included computers worldwide and was used to file hundreds of thousands of fraudulent Covid claims and distribute CSAM, among other crimes.
Scoop.it!

Police are using subtle psychological operations against ransomware gangs to sow distrust in their ranks—and trick them into emerging from the shadows.
Scoop.it!

From
www

Julius Kivimäki threatened thousands of patients he would publish details of their therapy sessions.
Scoop.it!
Shopping for a laptop can be infuriating. Here’s how to sift through the acronyms, storage options, and extra features to find the best one for you.
Scoop.it!
Plus: New York’s legislature suffers a cyberattack, police disrupt a global phishing operation, and Apple removes encrypted messaging apps in China.
Scoop.it!

Latest research finds fibre and FWA both play crucial roles in expanding internet connectivity and bridging digital divide – but on balance, fibre is still the fixed comms top gun.
Scoop.it!
Change Healthcare ransomware hackers already received a $22 million payment. Now a second group is demanding money, and it has sent WIRED samples of what they claim is the company's stolen data.
Scoop.it!

Data stolen from an earlier attack on NHS Dumfries and Galloway has been leaked by a ransomware gang that claims to be in possession of much more content.
Scoop.it!

Three members of an organised cyber criminal group who hacked and appropriated personal email and social media accounts face up to 15 years in prison
|
Scoop.it!

At its worldwide developer conference, Apple updated macOS and iOS, making Siri more context-aware.
Scoop.it!

The number of alleged hacks targeting the customers of cloud storage firm Snowflake appears to be snowballing into one of the biggest data breaches of all time.
Scoop.it!
TikTok has confirmed a “potential exploit” that is being used to go after accounts belonging to media organizations and celebrities, including CNN and Paris Hilton, through direct messages.
Scoop.it!
The US says a Chinese national operated the “911 S5” botnet, which included computers worldwide and was used to file hundreds of thousands of fraudulent Covid claims and distribute CSAM, among other crimes.
Scoop.it!
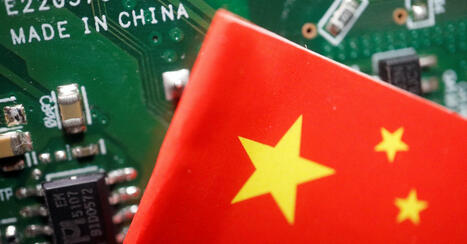
China has set up its third planned state-backed investment fund to boost its semiconductor industry, with a registered capital of 344 billion yuan ($47.5 billion), according to a filing with a government-run companies registry.
Scoop.it!
Law enforcement officials say they’ve identified, sanctioned, and indicted the person behind LockBitSupp, the administrator at the heart of LockBit’s $500 million hacking rampage.
Scoop.it!

Mandiant has formally attributed a long-running campaign of cyber attacks by a Russian state actor known as Sandworm to a newly designated advanced persistent threat group to be called APT44.
Scoop.it!
Shopping for a laptop can be infuriating. Here’s how to sift through the acronyms, storage options, and extra features to find the best one for you.
Scoop.it!

Police have shut down a web service used by more than 2,000 criminals worldwide to launch and managed phishing attacks, making 37 arrests. The Metropolitan Police took part in an operation by police forces from 19 countries to disrupt one the worlds largest phishing as a service platforms known as LabHost.
Scoop.it!

Plus: Apple warns iPhone users about spyware attacks, CISA issues an emergency directive about a Microsoft breach, and a ransomware hacker tangles with an unimpressed HR manager named Beth.
Scoop.it!
This video explores 20 emerging technologies and their future. Watch this next video about the 10 stages of AI. Via Edumorfosis
Scoop.it!

MDR specialist Adlumin says its new features will help customers stop in-progress ransomware attacks before they can cause significant damage
|




