ICT Security-Sécurité PC et Internet
114.2K views | +2 today
ICT Security-Sécurité PC et Internet
ICT Security + Privacy + Piracy + Data Protection - Censorship - Des cours et infos gratuites sur la"Sécurité PC et Internet" pour usage non-commercial... (FR, EN+DE)...
Curated by Gust MEES
Your new post is loading...
Rescooped by Gust MEES from 21st Century Learning and Teaching
April 30, 2013 6:19 AM
Scoop.it!

Backdoor entdeckt: Angreifer kaperten schon hunderte Apache-Server

Backdoor entdeckt: Angreifer kaperten schon hunderte Apache-Server | ICT Security-Sécurité PC et Internet | Scoop.it
Bösartige Angreifer kapern Apache-Webserver und leiten deren Besucher auf Schad-Websites um. Die Tarnung der Malware ist fast perfekt.


Eine Hintertür, die von Administratoren nur schwer bemerkt werden kann, sorgt dafür, dass Internet-Anfragen an Apache-Server nicht in Logs aufgenommen werden. Die gesendeten http-Anfragen, die in Wirklichkeit einen Trojaner steuern, sind nicht ersichtlich. Der Rest des Angriffs läuft im Speicher ab, Bugfixes gibt es noch nicht.


29. April 2013 von Manfred Kohlen 0


Die Malware Linux/Cdorked.A ist eine raffinierte Hintertür, die alles tut, um den Internetverkehr auf schädliche Webseiten umzuleiten, schreibt Sicherheitsanbieter Eset in einer aktuellen Warnung.   Der Schädling sei so gut, dass er laut eigener Analysen schon hunderte von Webservern unter seine Kontrolle gebracht habe.

 

Gust MEES's insight:


Learn more:


- http://www.scoop.it/t/securite-pc-et-internet/?tag=Apache-vulnerabilities


Scooped by Gust MEES
March 11, 2013 3:36 AM
Scoop.it!

Linux kernel: denial of service via DCCP getsockopt

Linux kernel: denial of service via DCCP getsockopt | ICT Security-Sécurité PC et Internet | Scoop.it
This bulletin was written by Vigil@nce : http://vigilance.fr/offer SYNTHESIS OF THE VULNERABILITY A local attacker can use the getsockopt() (...)
Gust MEES's insight:


Check also:


- http://www.scoop.it/t/securite-pc-et-internet?tag=Linux-Vulnerabilities


Selena Mini's comment, March 11, 2013 5:28 AM
It's great to see ..
Scooped by Gust MEES
February 25, 2013 10:51 AM
Scoop.it!

Linux-Rootkits missbrauchen SSH-Dienst

Linux-Rootkits missbrauchen SSH-Dienst | ICT Security-Sécurité PC et Internet | Scoop.it
Auf kompromittierten Linux-Systemen haben Sicherheitsexperten eine heimtückische Hintertür entdeckt, die sich über eine Bibliothek in den SSH-Dienst einklinkt.
Gust MEES's insight:

Check also:


- http://www.scoop.it/t/securite-pc-et-internet?tag=Linux-Vulnerabilities


- http://www.scoop.it/t/securite-pc-et-internet?tag=Nobody-is-perfect


No comment yet.
Scooped by Gust MEES
November 20, 2012 8:32 AM
Scoop.it!

Linux Rootkit Found Launching iFrame Injection Attacks

Linux Rootkit Found Launching iFrame Injection Attacks | ICT Security-Sécurité PC et Internet | Scoop.it
The Linux root kit targets 64-bit Linux platforms and uses advanced techniques to hide itself, and infects the websites hosted on attacked HTTP server working to launch drive-by download attacks.


“It's an outstanding sample, not only because it targets 64-bit Linux platforms and uses advanced techniques to hide itself, but primarily because of the unusual functionality of infecting the websites hosted on attacked HTTP server - and therefore working as a part of drive-by download scenario,” commented Marta Janus, a Kaspersky Lab Expert who examined the rootkit sample.


===> “This rootkit, though it's still in the development stage, shows a new approach to the drive-by download schema and we can certainly expect more such malware in the future.” <===


Read more:

http://www.securityweek.com/linux-rootkit-found-launching-iframe-injection-attacks


No comment yet.
Scooped by Gust MEES
July 16, 2012 5:38 PM
Scoop.it!

Cross-platform Trojan attacks Windows, Intel Macs, Linux

Cross-platform Trojan attacks Windows, Intel Macs, Linux | ICT Security-Sécurité PC et Internet | Scoop.it
Summary: A second cross-platform Trojan downloader has been discovered that detects if you're running Windows, Mac OS X, or Linux, and then downloads the corresponding malware for your platform.


Read more:

http://www.zdnet.com/cross-platform-trojan-attacks-windows-intel-macs-linux-7000000872/


No comment yet.
Rescooped by Gust MEES from 21st Century Learning and Teaching
July 11, 2012 7:06 AM
Scoop.it!

Multi-platform backdoor malware targets Windows, Mac and Linux users

Multi-platform backdoor malware targets Windows, Mac and Linux users | ICT Security-Sécurité PC et Internet | Scoop.it
A web-based malware attack has been discovered, targeting users of Windows, Mac and Linux.

Although the amount of malware written for different operating systems can vary, it's becoming increasi...


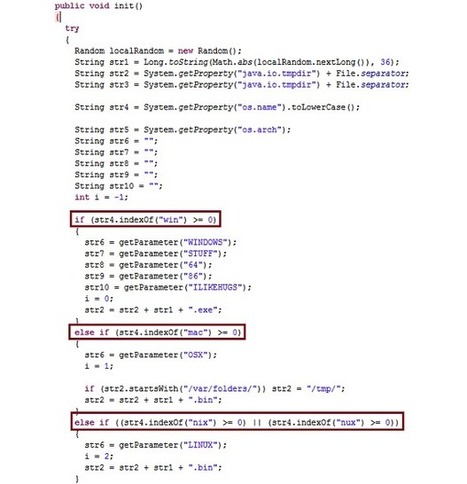
Visiting a hacked webpage, triggers a JAR (Java Archive) file which will ask permission to do its business - secretly determining if you are running Windows, Mac OS X or Linux.


Read more:


http://nakedsecurity.sophos.com/2012/07/11/backdoor-malware/?utm_source=twitter&amp;amp;utm_medium=status%2Bmessage&amp;amp;utm_campaign=naked%2Bsecurity


No comment yet.
Scooped by Gust MEES
March 29, 2013 2:47 PM
Scoop.it!

Critical Flaw Threatens Millions of BIND Servers | threatpost

Critical Flaw Threatens Millions of BIND Servers | threatpost | ICT Security-Sécurité PC et Internet | Scoop.it

There is a critical vulnerability in several current versions of the BIND nameserver software that could allow an attacker to knock vulnerable DNS servers offline or compromise other applications running on those machines. The bug is present in several versions of the ubiquitous BIND software and the maintainers of the application have released a patch for it ===> that they recommend users install as soon as possible. <===


===> The vulnerability is in BIND 9.7, 9.8, and 9.9 for Unix systems, but Windows versions are not affected. <===


The problem lies in the way that the software handles certain regular expressions, and an attacker who exploits the vulnerability could not only cause a denial-of-service condition on the server but also could potentially compromise other software on the machine.


Gust MEES's insight:


The bug is present in several versions of the ubiquitous BIND software and the maintainers of the application have released a patch for it ===> that they recommend users install as soon as possible. <===


===> The vulnerability is in BIND 9.7, 9.8, and 9.9 for Unix systems, but Windows versions are not affected. <===


The problem lies in the way that the software handles certain regular expressions, and an attacker who exploits the vulnerability could not only cause a denial-of-service condition on the server but also could potentially compromise other software on the machine.


Check also:


- http://www.scoop.it/t/securite-pc-et-internet?tag=Linux-Vulnerabilities


No comment yet.
Scooped by Gust MEES
February 25, 2013 1:44 PM
Scoop.it!

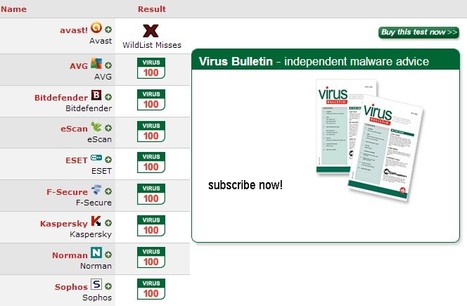
Virus Bulletin : VB100 results SUSE Linux - February 2013

Virus Bulletin : VB100 results SUSE Linux - February 2013 | ICT Security-Sécurité PC et Internet | Scoop.it
View the results of the Virus Bulletin VB100 anti-virus product comparisons
Gust MEES's insight:

A MUST check for Linux users!!!


Check also:


- http://www.scoop.it/t/securite-pc-et-internet?tag=Nobody-is-perfect


- http://www.scoop.it/t/securite-pc-et-internet?q=Linux


Scooped by Gust MEES
January 3, 2013 3:38 AM
Scoop.it!

Malware is targeting Java HTTP servers

Malware is targeting Java HTTP servers | ICT Security-Sécurité PC et Internet | Scoop.it
Security researchers from antivirus vendor Trend Micro have uncovered a piece of backdoor-type malware that infects Java-based HTTP servers and allows attackers to execute malicious commands on the underlying systems.
Gust MEES's insight:

                       ===> Be AWARE of the MALWARE! <===

No comment yet.
Scooped by Gust MEES
September 1, 2012 9:53 AM
Scoop.it!

Linux users targeted by password-stealing 'Wirenet' Trojan

Linux users targeted by password-stealing 'Wirenet' Trojan | ICT Security-Sécurité PC et Internet | Scoop.it


===> Malware writers are interested in Linux after all. <===


Russian security firm Dr Web has reported finding a shadowy Trojan that sets out to steal passwords on the open source platform as well as OS X.


Cross platform malware is rare but not unheard of, the usual technique being to hook into Java in search of victims using OS X.

Malware specifically designed to steal credentials from Linux systems is almost unheard of but might, on the basis of this new discovery, become a little less so in future.


"We do not have explicit evidence that it uses Java. To my knowledge it does not. This file was received from Virustotal," Dr Web analyst Igor Zdobnov told Techworld.


Read more:

http://news.techworld.com/security/3378804/linux-users-targeted-by-password-stealing-wirenet-trojan/?olo=rss&amp;utm_source=dlvr.it&amp;utm_medium=twitter


No comment yet.
Scooped by Gust MEES
July 11, 2012 12:21 PM
Scoop.it!

Multi-Platform Java Exploit Targets Macs, Linux, Windows

Multi-Platform Java Exploit Targets Macs, Linux, Windows | ICT Security-Sécurité PC et Internet | Scoop.it
If allowed to run, a malicious Java applet checks the user's operating system and delivers a payload customized for that platform, whether it's Windows, Mac OS X, or Linux.


Read more:

http://www.securityweek.com/multi-platform-java-exploit-targets-macs-linux-windows


No comment yet.