


More than 100,000 Android applications in Google Play are considered "suspicious" or "questionable," according to new research.
Read more:
http://mashable.com/2012/11/05/android-apps-suspicious/

 Your new post is loading...
 Scoop.it! More than 100,000 Android applications in Google Play are considered "suspicious" or "questionable," according to new research.
Read more: http://mashable.com/2012/11/05/android-apps-suspicious/

No comment yet.
Sign up to comment
Scoop.it!
French police have arrested a 20-year-old man in Northern France, in connection with an attack that infected thousands of Android smartphones with money-making malware.
Read more:
Scoop.it!
Cybercriminals are working on more complex schemes to wage attacks on PCs, laptops, and smartphones.
A new report shows that: ===> every single device that connects to the Internet is in danger. <===
Read this blog post by Dara Kerr on Security & Privacy:
Scoop.it!
Mobile variants of the commercial FinFisher trojan target BlackBerry, Windows Mobile, Symbian, Android and iOS devices.
The commercial FinFisher FinSpy spyware trojan was created by Gamma International, and its development is believed to take place in Germany. The company sells its trojan toolkit – which is thought to currently support all major operating systems including Linux, Mac OS X and Windows – to governments for use by security agencies. Until now, relatively little was known about the mobile variant of the trojan.
Scoop.it!

Three websites which distributed copyrighted smartphone 'apps', or applications, have been shut down by law enforcement authorities in the US, in which the Department of Justice (DoJ) said was the first case involving "cell phone app marketplaces".27 Aug 2012
The DoJ said that the seizures were the result of "comprehensive enforcement action taken to prevent the infringement of copyrighted mobile device apps" involving international authorities, including those in France and the Netherlands. Visitors to any of the three sites - applanet.net, appbucket.net and snappzmarket.com - will now find a banner notifying them that the relevant domain name has been seized by the authorities and informing them that "wilful copyright infringement" is a federal crime.
Read more:
Scoop.it!

Die Sicherheitsexperten von G-Data haben einen neuen Android-Schädling entdeckt, der selbstständig kostenpflichtige Apps herunterlädt.
G-Data empfiehlt zum Schutz von solchen und ähnlichen Schädlingen die Installation einer Sicherheitslösung auf dem mobilen Gerät. Außerdem sollte das Gerät und die darauf installierten Applikationen immer aktuell gehalten werden, um so auch vor bereits bekannten und geschlossenen Sicherheitslücken geschützt zu sein. Grundsätzlich sollten Apps nur aus vertrauenswürdigen Quellen heruntergeladen und installiert werden. Dazu zählen etwa Google Play und die Marktplätze der Hersteller.
In diesem Artikel finden Sie weitere Tipps, wie Sie ein Android-Gerät absichern können:
Scoop.it!

Summary: Cybercriminals have created a new variant of the OpFake malware for Android that comes bundled with a legitimate version of the Opera Mini mobile browser.
Read more: http://www.zdnet.com/warning-new-android-malware-tricks-users-with-real-opera-mini-7000001586/
Scoop.it!

Summary: Phandroid's AndroidForums.com has been hacked. The database that powers the site was compromised and more than 1 million user account details were stolen.
===> If you use the forum, make sure to change your password asap. <===
Read more: http://www.zdnet.com/android-forums-hacked-1-million-user-credentials-stolen-7000000817/
Scoop.it!
Android Botnet Used to Advertise Shady Pharmacy Sites, Experts Find...
Read more:
Scoop.it!
Criminals have created a botnet of Android phones to send spam messages using Yahoo! mail. The malware problems on Android continue to grow and mimic their Windows cousins.
Read more:
Scoop.it!

Eine neue Variante des SpyEye-Trojaners stiehlt mTANs von Android-Smartphones. Doch der Schädling belässt es nicht dabei.
Weiter lesen:
Scoop.it!
From
www

Lookout Mobile Security has identified hacked websites targeting Android devices, an attack vector previously only used to infect PCs with malware.
Read more...
Scoop.it!
Lookout warnt vor dem erstern Drive-by-Download-Schädling für Android-Nutzer. „NotCompatible“ mogelt sich fast automatisch auf Ihr Smartphone.
Read more...
|
Scoop.it!
The company says the apps demand a 'suspicious' number of high-risk permissions.
According to a new report from Bit9, more than 100,000 Android apps in the Google Play store (25 percent of more than 400,000 apps studied) pose a security risk to users.
Read more:
Scoop.it!
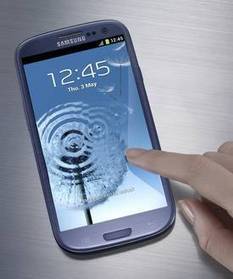
Une faille de sécurité permet à un simple code reçu par SMS de réinitialiser automatiquement et d’effacer toutes les données de certains smartphones fonctionnant sous Android.
Visualisez aussi la vidéo ici : http://www.youtube.com/watch?v=Q2-0B04HPhs&amp;feature=player_embedded
Scoop.it!
DFI News Digital Forensic Investigator is a multi-media resource for digital forensic professionals working in academic, government, law enforcement, and corporate settings.
Call it Invasion of the iPhone Snatchers: a new FinFisher-based spyware is built to infect iPhones and iPads (and Android, BlackBerry and Windows Phone gadgets too) in order to take over the device completely — all unbeknownst to the user.
The smartphones and tablets will innocently appear to be themselves, but in reality the mobile malware is working in the background to track the device’s location, monitor activity and intercept communications including emails, voice calls and text messages.
Read more:
Scoop.it!

Wenn auf Ihrem Smartphone FinSpy Mobile läuft, können Ihre Telefonate, SMS und Mails mitgeschnitten werden. Außerdem sind Sie stillen Anrufen ausgesetzt: Der Hacker hört heimlich alles mit.
Mehr lesen und schlauer werden:
Scoop.it!

With its vast number of Android users and their preference for third-party online app markets, China is the perfect breeding ground for new Android malware.
Read more: http://www.net-security.org/malware_news.php?id=2230
Scoop.it!
By Jim Finkle LAS VEGAS (Reuters) - Hacking experts have demonstrated ways to attack Android smartphones using methods they said work on virtually all such devices in use today, despite recent efforts by search engine giant Google to...
Scoop.it!

Des pirates ont accédé aux données des membres du forum américain Android Forums, qui compte plus d’un million de membres. Nvidia a de son côté fermé la zone Développeurs suite à une intrusion.
En savoir plus :
Scoop.it!

Recently Trusteer discovered the first Tatanga-based man in the mobile (MITMO) attack as well as new SPITMO configurations which are targeting Android mobile banking users in Germany, the Netherlands, Portugal and Spain.
With nearly 60 percent of the market and a reputation for weak app security, it’s no surprise that Android has become the preferred target for financial malware.
Read more: http://www.net-security.org/malware_news.php?id=2183
Scoop.it!
L’éditeur Trend Micro anticipe une importante croissance des malwares sur Android et avertit que la situation pourrait devenir pandémique d’ici à la fin de l’année.
L’éditeur japonais affirme que le nombre d’applications malicieuses sur plates-formes Android est passé de 10 000 à 20 000 en seulement un mois et que des centaines de milliers de périphériques ont été infectés par des applications que l’on peut trouver sur la plate-forme GooglePlay. L’éditeur indique que 17 applications contenant un malware ont été téléchargées à plus de 700 000 reprises avant d’être supprimées par Google. Durant les trois premiers mois de l’année, plus de 5000 applications destinées à infecter les téléphones Android ont été découvertes, soit une multiplication par quatre et les chiffres continuent à augmenter.
Pour le troisième trimestre, le nombre pourrait atteindre 38 000 malwares et … 130 000 au cours du 4ème trimestre, ce qui permet de qualifier la situation de pandémie.
$$$$$$$$$$$$$$$$$$$$$$$$$$$
En savoir plus :
Scoop.it!
Ein Microsoft-Ingenieur hat ein Spam-Botnetz ausgemacht, dass sich auf Android-Geräten einnistet und von dort aus massenhaft Werbemails versendet.
Weiter lesen:
Scoop.it!
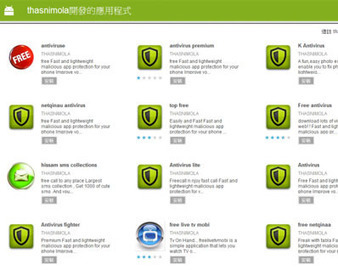
Downloading apps from Google Play, the official online Android app market, is not without its dangers.
Even though Google has been scanning the offered apps for malware by using "Bouncer" - an automated app scanning service that should, in theory, detect malicious software and developers who keep offering it - there are still instances where they aren't booted out of the market soon enough.
Security researchers from AegisLab have recently discovered over 15 fake AV and "free SMS" apps being offered by the same developer ("thasnimola") that has been flagged for selling fake NQ Mobile apps in April.
Read more and be aware...
Scoop.it!
Analysts with Lookout Mobile Security have found websites that have been hacked to deliver malicious software to devices running Android, an apparent new attack vector crafted for the mobile operating system.
Read more...
|




