 Your new post is loading...

|
Scooped by
Gust MEES
July 7, 2015 10:04 AM
|
A security researcher conducted an experiment to demonstrate that someone is sniffing passing traffic from Tor network exit nodes.
When talking about Tor network, normally everyone assumes that you have an end-to-end security, but someone believes it may be wrong as it was discovered by the security researcher Chloe.
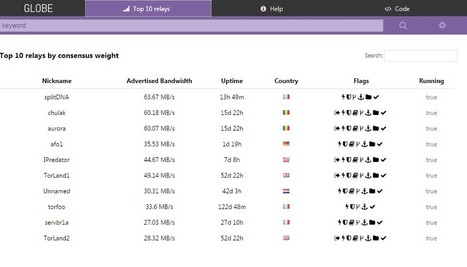
Tor network is free and it is the safest way to be anonymous since it hides your original IP from the destination server, to do that Tor uses relays to redirect traffic, but now the security researcher Chloe concludes that traffic is being sniffed in the exit nodes.
|
|
Scooped by
Gust MEES
May 27, 2015 4:40 PM
|
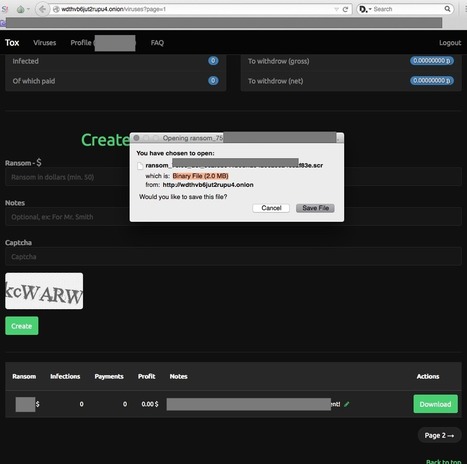
Die Einstiegshürde für angehende Online-Erpresser ist erneut gesunken: Ein Dienst im Tor-Netz erstellt nach wenigen Klicks den individuellen Erpressungs-Trojaner. Falls ein Opfer das geforderte Lösegeld zahlt, verdienen die Betreiber mit.
Die Einstiegshürde für angehende Online-Erpresser ist erneut gesunken: Ein Dienst im Tor-Netz erstellt nach wenigen Klicks den individuellen Erpressungs-Trojaner. Falls ein Opfer das geforderte Lösegeld zahlt, verdienen die Betreiber mit.
- http://www.scoop.it/t/securite-pc-et-internet/?tag=TOR
|
|
Scooped by
Gust MEES
January 16, 2015 8:49 AM
|
Das Tor-Netzwerk: Dort tummeln sich Whistleblower, Aktivisten, politisch Verfolgte, aber auch Drogenhändler oder Pädophile. Alle wollen dort aus unterschiedlichen Motiven ihre Anonymität bewahren. Es gibt aber Zweifel an der Effektivität der Anonymisierung.
Learn more:
- http://www.scoop.it/t/securite-pc-et-internet/?tag=TOR
|
|
Scooped by
Gust MEES
December 28, 2014 10:05 AM
|
|
|
Scooped by
Gust MEES
December 26, 2014 1:44 PM
|
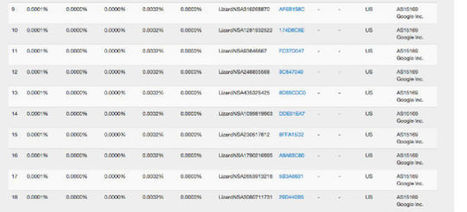
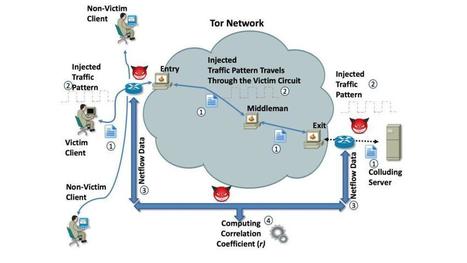
The hacker group appears to be attempting to dominate Tor's relays to the point where it can comprise anonymity. Tor keeps you anonymous by bouncing your communications around a network of volunteer nodes. But if one group is controlling the majority of the nodes, it could be able to eavesdrop on a substantial number of vulnerable users. Which means Lizard Squad could gain the power to track Tor users if it infiltrates enough of the network.
So far, they have already established over 3000 relays, nearly half of the total number. That's very not good.
Learn more:
- http://www.scoop.it/t/securite-pc-et-internet/?tag=TOR
|
|
Scooped by
Gust MEES
November 19, 2014 8:07 AM
|
|
|
Scooped by
Gust MEES
November 14, 2014 10:24 PM
|
|
|
Scooped by
Gust MEES
November 10, 2014 11:31 AM
|
|
|
Scooped by
Gust MEES
August 6, 2014 11:35 AM
|
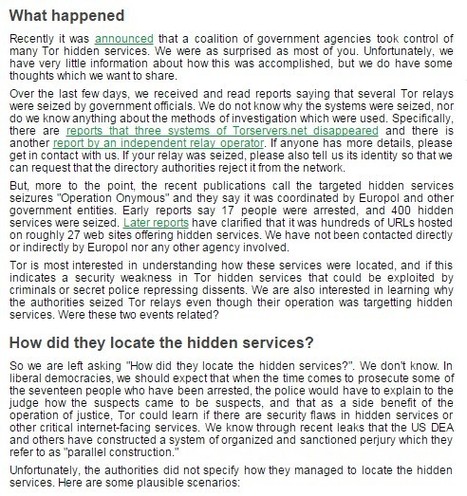
Tor's had a tough week. Just a few days ago, the organization made the difficult announcement that an attack on their system likely stripped users of anonymity. Now, Wired reports that the FBI effort has been running a campaign to identify Tor users by installing malware on their computers for years, virtually unchecked by the courts.
|
|
Scooped by
Gust MEES
July 3, 2014 12:34 PM
|
|
|
Scooped by
Gust MEES
February 27, 2014 7:59 AM
|
Cyber criminals can infiltrate your mobile devices with the just discovered first "TOR Trojan for Android".
|
|
Scooped by
Gust MEES
October 2, 2013 1:03 PM
|
The feds have caught up to the Silk Road. The underground website long known for drug trafficking was seized by the FBI who also arrested the owner on three criminal counts.
Tous les accès corrompus au réseau maillé TOR l'ont été grâce à une faille du TOR Bundle exploitée sur Windows. Une solution : switchez, affirme l'équipe derrière TOR.
Via Frederic GOUTH
|
|
|
Scooped by
Gust MEES
May 27, 2015 4:46 PM
|
|
|
Scooped by
Gust MEES
February 18, 2015 9:00 AM
|
Last week, user Virgil Griffith went onto the Tor-talk mailing list and announced Onion City, a Dark Web search engine that allows regular web users to delve into the Dark Web.
The search engine delves into the anonymous Tor network, finds .onion sites and makes them available to regular users on the ordinary World Wide Web.
Up to now the best way to search for .onion sites has been to get on the Tor network using something like the Tor browser, but Onion City effectively does that bit for you so you can search from the comfort of your favourite, insecure web browser.
|
|
Scooped by
Gust MEES
December 30, 2014 9:22 AM
|
|
|
Scooped by
Gust MEES
December 26, 2014 9:37 PM
|
|
|
Scooped by
Gust MEES
December 17, 2014 10:05 AM
|
For more than a decade, a powerful app called Metasploit has been the most important tool in the hacking world: An open-source Swiss Army knife of hacks that puts the latest exploits in the hands of anyone who’s interested, from random criminals to the thousands of security professionals who rely on the app to scour client networks for holes.
Now Metasploit has a new and surprising fan: the FBI. WIRED has learned that FBI agents relied on Flash code from an abandoned Metasploit side project called the “Decloaking Engine” to stage its first known effort to successfully identify a multitude of suspects hiding behind the Tor anonymity network.
Learn more:
- http://www.scoop.it/t/securite-pc-et-internet/?tag=TOR
|
|
Scooped by
Gust MEES
November 15, 2014 3:47 AM
|
The recent shutdown of SilkRoad 2.0 was just a small part of the events affecting the Tor network that unfolded last week.
Cybercrime, just like any other illegal activity, is hard to eradicate completely. Whenever illegal services are taken down, the gap created will always be filled by other criminals willing to profit from the opportunity. The reality we have to accept is that there will always be demand for such services.
Learn more:
- http://www.scoop.it/t/securite-pc-et-internet/?tag=TOR
|
|
Scooped by
Gust MEES
November 14, 2014 11:18 AM
|
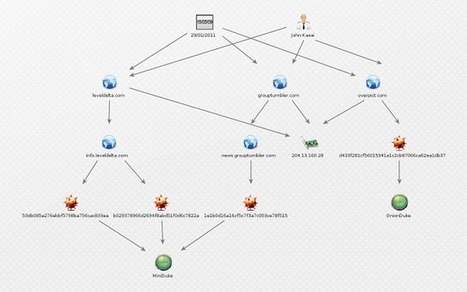
Recently, research was published identifying a Tor exit node, located in Russia, that was consistently and maliciously modifying any uncompressed Windows executables downloaded through it. Naturally this piqued our interest, so we decided to peer down the rabbit hole. Suffice to say, the hole was a lot deeper than we expected! In fact, it went all the way back to the notorious Russian APT family MiniDuke, known to have been used in targeted attacks against NATO and European government agencies.
The malware used in this case is, however, not a version of MiniDuke. It is instead a separate, distinct family of malware that we have since taken to calling OnionDuke.
Learn more:
- http://www.scoop.it/t/securite-pc-et-internet/?tag=TOR
|
|
Scooped by
Gust MEES
November 7, 2014 3:50 PM
|
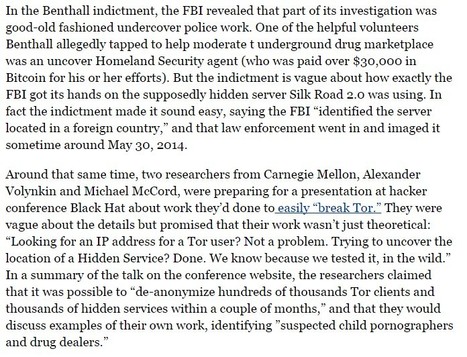
If you control enough of the Tor network, it’s possible to get a kind of bird’s eye view of the traffic being routed through it. It was clear that Tor thought the Carnegie Mellon researchers were responsible. The researchers refused to talk to the press, but a conference spokesperson told Reuters the talk was canceled because the researchers hadn’t cleared the release of their work through their department, the Software Engineering Institute, which is funded by the Defense Department.
At the time, many assumed that the university pulled the plug on the talk because of the gray legal zone it was in, with the researchers casually intercepting Web traffic. But maybe it got pulled because the researchers were revealing a law enforcement technique that the government did not want publicized. If nothing else, it’s highly likely the information the researchers collected about “drug dealers and child pornographers” made its way into law enforcement hands. McCord said he was “unable to comment on the matter.” Carnegie Mellon’s SEI declined comment about the canceled talk and about whether it had provided information from the research to law enforcement.
Learn more:
- http://www.scoop.it/t/securite-pc-et-internet/?tag=TOR
|
|
Scooped by
Gust MEES
July 30, 2014 5:59 PM
|
C’est dans un message diffusé sur le blog du système d’anonymisation TOR que l’on apprend, du moins que nous avons la confirmation, du piratage du système TOR. Comme nous vous l’indiquions sur zataz, voilà une dizaine de jours, nous nous étonnions de la disparition d’une conférence dédiée à la surveillance de TOR lors du Black Hat 2014 de Las Vegas. La conférence de d’Alexander Volynkin et Michael McCord devait revenir sur les moyens de rendre beaucoup moins anonymes les utilisateurs du système. TOR, donc, via son blog explique que ce “4 juillet, nous avons trouvé un groupe de relais dont le but supposé était de contourner l’anonymat des utilisateurs. Il semble qu’ils ciblaient les internautes qui utilisent Tor pour accéder ou exploiter des services cachés. Les attaques entraînaient la modification des en-tête de Tor pour s’effectuer.” Bref, nous revoilà avec le coup de 2007 et la lecture des données passant par les ordinateurs permettant à TOR de fournir l’anonymat tant recherché. Une technique d’espionnage démontrée par Dan Egerstad qui avait permis de révéler des centaines de données sensibles d’ambassades ou encore du Dalaïlama.
Article original appartenant à zataz.com : ZATAZ Magazine » Piratage de TOR confirmé par… TOR http://www.zataz.com/piratage-de-tor-confirme-par-tor/#ixzz38zXP7urA
Follow us: @zataz on Twitter
|
|
Scooped by
Gust MEES
March 6, 2014 5:59 PM
|
Das Anonymisierungsnetzwerk TOR wird inzwischen auch durch Online-Kriminelle gern genutzt. Kaspersky Lab kennt mittlerweile etwa 900 Dienste der Online-Kriminalität, die sich im so genannten Darknet verstecken. Dazu zählen etwa Kommando-Server für Bot-Netze.
|
|
Scooped by
Gust MEES
October 3, 2013 10:49 AM
|
Das Federal Bureau of Investigation (FBI) hat den Untergrund-Online-Marktplatz für Drogen Silk Road geschlossen. Über die Plattform konnten unter anderem Heroin, Kokain und Crystal Meth gegen die virtuelle Währung Bitcoin erworben werden.
|
|
Scooped by
Gust MEES
September 5, 2013 3:44 PM
|
In the wake of the revelations surrounding the NSA's domestic surveillance and intelligence-gathering operations, security experts said there would likely be a natural uptick in the usage of privac...
|















When talking about Tor network, normally everyone assumes that you have an end-to-end security, but someone believes it may be wrong as it was discovered by the security researcher Chloe.
Tor network is free and it is the safest way to be anonymous since it hides your original IP from the destination server, to do that Tor uses relays to redirect traffic, but now the security researcher Chloe concludes that traffic is being sniffed in the exit nodes.