 Your new post is loading...

|
Scooped by
Gust MEES
March 2, 2023 12:57 PM
|
A pervasive cyber-espionage group known as Iron Tiger, believed to be out of China, has updated one of its malware frameworks to attack Linux-based systems.
Researchers at Trend Micro recently discovered that Iron Tiger (aka Emissary Panda or APT27) had added new features to its so called SysUpdate malware family, which allows it to infect Linux platforms in addition to Windows. SysUpdate abuses system services, grabs screenshots, browses and terminates processes, retrieves drive information, executes commands, and can find, delete, rename, upload, and download files as well as peruse a victim's file directory. Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux
|
|
Scooped by
Gust MEES
December 27, 2022 3:09 PM
|
Une grave faille de sécurité affecte le noyau Linux
Sécurité : La faille de sécurité affecte ksmbd, un serveur SMB intégré au noyau de Linux 5.15, et sa note de gravité avoisine le 10, selon la ZDI.
Joyeux Noël à tous les administrateurs de systèmes Linux ! Et en guise de cadeau : une grave faille de sécurité dans le noyau Linux.
C’est la Zero Day Initiative (ZDI), une société de recherche sur les failles zero-day, qui l’a découverte et annoncée juste avant le réveillon.
Cette vulnérabilité pourrait permettre à un attaquant à distance authentifié de divulguer des informations sensibles et d’exécuter du code sur les versions vulnérables du noyau Linux.
|
|
Scooped by
Gust MEES
March 18, 2022 5:47 PM
|
Behind almost all Linux firewalls tools such as iptables; its newer version, nftables; firewalld; and ufw, is netfilter, which controls access to and from Linux's network stack. It's an essential Linux security program, so when a security hole is found in it, it's a big deal.
|
|
Scooped by
Gust MEES
January 26, 2022 5:11 PM
|
Triviale Linux-Lücke ermöglicht Root-Rechte
Zum Ausnutzen der Sicherheitslücke in Polkit muss der Dienst nur installiert sein. Das betrifft auch Serversysteme. Exploits dürften schnell genutzt werden. Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux
|
|
Scooped by
Gust MEES
January 21, 2022 4:40 PM
|
|
|
Scooped by
Gust MEES
January 20, 2022 9:20 AM
|
Rechenfehler im Linux-Kernel erlaubt Rechteausweitung
Vor allem in Cloud-Systemen problematisch: An Linux-Systemen angemeldete Nutzer könnten aufgrund eines potenziellen Pufferüberlaufs ihre Rechte ausweiten. Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux
|
|
Scooped by
Gust MEES
August 3, 2021 6:53 AM
|
Microsoft has continued its analysis of the LemonDuck malware, known for installing crypto-miners in enterprise environments. It makes a strong case for why it is worth removing it from your network.
This group, according to Microsoft, has a well-stocked arsenal of hacking tools, tricks and exploits aimed at one thing: for their malware to retain exclusive access to a compromised network for as long as possible.
While crypto-mining malware could be just a nuisance, LemonDuck attributes suggest the attacker group really do try to own compromised networks by disabling anti-malware, removing rival malware, and even automatically patching vulnerabilities -- a competitive effort to keep rival attackers from feeding off its turf. Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/topic/securite-pc-et-internet
|
|
Scooped by
Gust MEES
April 28, 2021 3:16 PM
|
An information disclosure vulnerability in the Linux kernel can be exploited to leak data and act as a springboard for further compromise.
Disclosed by Cisco Talos researchers on Tuesday, the bug is described as an information disclosure vulnerability "that could allow an attacker to view Kernel stack memory."
The kernel is a key component of the open source Linux operating system. The vulnerability, tracked as CVE-2020-28588, was found in the proc/pid/syscall functionality of 32-bit ARM devices running the OS.
According to Cisco, the issue was first found in a device running on Azure Sphere. Attackers seeking to exploit the security flaw could read the /syscall OS file via Proc, a system used for interfacing between kernel data structures. Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux
|
|
Scooped by
Gust MEES
March 15, 2021 7:38 PM
|
Google has addressed yet another actively exploited zero-day in Chrome browser, marking the second such fix released by the company within a month.
The browser maker on Friday shipped 89.0.4389.90 for Windows, Mac, and Linux, which is expected to be rolling out over the coming days/weeks to all users.
While the update contains a total of five security fixes, the most important flaw rectified by Google concerns a use after free vulnerability in its Blink rendering engine. The bug is tracked as CVE-2021-21193. Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/topic/securite-pc-et-internet/?&tag=Browsers
|
|
Scooped by
Gust MEES
March 9, 2021 7:06 PM
|
Rising Linux security developer Alexander Popov of London-based Positive Technologies discovered and fixed a set of five security holes in the Linux kernel's virtual socket implementation. An attacker could use these vulnerabilities (CVE-2021-26708) to gain root access and knock out servers in a Denial of Service (DoS) attack.
With a Common Vulnerability Scoring System (CVSS) v3 base score of 7.0, high severity, smart Linux administrators will patch their systems as soon as possible.
While Popov discovered the bugs in Red Hat's community Linux distribution Fedora 33 Server, it exists in the system using the Linux kernel from November 2019's version 5.5 to the current mainline kernel version 5.11-rc6. Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux
|
|
Scooped by
Gust MEES
February 7, 2021 11:48 AM
|
Auf der Open-Source-Entwicklerkonferenz FOSDEM haben Sanja Bonic und Janos Pasztor vorgestellt, wie man mit ihrem Projekt ContainerSSH und dem Programm asciinema anschaulich macht, was angreifende Hacker auf einem Server tun. ContainerSSH erlaubt es, Software-Container dynamisch zu erzeugen, wenn sich ein SSH-Nutzer auf einem Server anmeldet. Meldet er sich wieder ab, wird der Container eingestampft. Das eignet sich zum Beispiel für Anwendungen im Webhosting-Bereich oder für Lernumgebungen für praxisnahe Linux-Kurse. Man kann damit aber auch einen Honeypot bauen.
Ein Honeypot ist ein absichtlich verwundbarer Server, der mit dem Zweck ins Internet eingebracht wird, Angreifer anzulocken. So kann man zum Beispiel die neuesten Angriffstechniken untersuchen, die gerade im Einsatz. Aber nicht nur für Sicherheitsexperten, auch als Admin kann ein Honeypot nützlich sein. So brachte etwa Pasztor das Beispiel eines Admins, der SSH-Server betreibt und schützen möchte. So jemand kann anhand der Login-Versuche auf einem Honeypot lernen, wogegen er seine echten Server verteidigen muss. Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/topic/securite-pc-et-internet/?&tag=Honeypot
|
|
Scooped by
Gust MEES
February 2, 2021 11:42 AM
|
A small but complex malware variant is targeting supercomputers worldwide.
Reverse engineered by ESET and described in a blog post on Tuesday, the malware has been traced back to attacks against supercomputers used by a large Asian Internet Service Provider (ISP), a US endpoint security vendor, and a number of privately-held servers, among other targets.
The cybersecurity team has named the malware Kobalos in deference to the kobalos, a small creature in Greek mythology believed to cause mischief.
Kobalos is unusual for a number of reasons. The malware's codebase is tiny but is sophisticated enough to impact at least Linux, BSD, and Solaris operating systems. ESET suspects it may possibly be compatible with attacks against AIX and Microsoft Windows machines, too.
"It has to be said that this level of sophistication is only rarely seen in Linux malware," commented cybersecurity researcher Marc-Etienne Léveillé. Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux
|
|
Scooped by
Gust MEES
January 20, 2021 4:41 PM
|
According to Checkpoint, the “FreakOut” malware attack is exploiting “newest vulnerabilities.”
Cybersecurity researchers identify vulnerabilities regularly, some serious, some not. In the latest, researchers from Checkpoint have discovered a range of attacks against Linux devices.
Dubbed FreakOut; the malware attack is being carried out to create an IRC botnet. It is worth noting that an IRC Botnet is a collection of machines infected with malware that can be controlled remotely via an IRC channel.
Done by a threat actor named “freak;” the botnet in question would allow attackers to perform malicious tasks such as brute-forcing attacks, network sniffing, killing processes, crypto-mining, and DDoS attacks.
Delving into the details, the campaign is not aimed at the masses but chooses a targeted approach in which it only attacks systems running the TerraMaster operating system ZEND framework or Liferay Portal. What’s troubling is that all 3 have a significant number of users globally. Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux
|
|
|
Scooped by
Gust MEES
January 27, 2023 2:45 PM
|
The Feds have disrupted the prolific Hive ransomware gang, saving victims from a collective $130 million in ransom demands. But it remains to be seen how much of a blow the effort will be to the overall ransomware landscape.
The group's operations have been buzzing with activity for months, racking up more than 1,500 victims in 80-plus countries around the world since it appeared in June 2021, according to an announcement from the US Justice Department. The gang has been operating with a ransomware-as-a-service (RaaS) model, engaging in data theft and double extortion, and delivering its venom indiscriminately to school districts, financial firms, critical infrastructure, and others. At least one affiliate has become a bit of a hospital specialist, disrupting patient care in some attacks.
|
|
Scooped by
Gust MEES
April 27, 2022 6:44 PM
|
Flaws in networkd-dispatcher, a service used in the Linux world, can be exploited by a rogue logged-in user or application to escalate their privileges to root level, allowing the box to be commandeered, Microsoft researchers said Wednnesday.
It's nice of Redmond to point out these flaws and have them fixed in any affected distributions; the US tech giant is a big user of Linux and relies on the open-source OS throughout its empire. It's just a little perplexing the biz went to all the effort of a big write-up and giving the flaws a catchy name, Nimbuspwn, when countless privilege-elevation holes are fixed in its Windows operating system each month, and we can't recall Microsoft lately making this much of a song and dance over them. Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux
|
|
Scooped by
Gust MEES
March 7, 2022 9:13 AM
|
|
|
Scooped by
Gust MEES
January 26, 2022 5:08 PM
|
If it's not one thing, it's another. After one real Linux problem -- the heap overflow bug in the Linux kernel's fs/fs_context.c program -- is found and fixed, then a new security problem is discovered. This time security company Qualys has uncovered a truly dangerous memory corruption vulnerability in polkit's pkexec, CVE-2021-4034.
Polkit, formerly known as PolicyKit, is a systemd SUID-root program. It's installed by default in every major Linux distribution.
How dangerous is it? Very. Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux
|
|
Scooped by
Gust MEES
January 21, 2022 4:25 PM
|
|
|
Scooped by
Gust MEES
October 29, 2021 12:30 PM
|
The Hive ransomware gang now also encrypts Linux and FreeBSD using new malware variants specifically developed to target these platforms.
However, as Slovak internet security firm ESET discovered, Hive's new encryptors are still in development and still lack functionality.
The Linux variant also proved to be quite buggy during ESET's analysis, with the encryption completely failing when the malware was executed with an explicit path.
|
|
Scooped by
Gust MEES
July 27, 2021 6:15 AM
|
Microsoft is warning customers about the LemonDuck crypto mining malware which is targeting both Windows and Linux systems and is spreading via phishing emails, exploits, USB devices, and brute force attacks, as well as attacks targeting critical on-premise Exchange Server vulnerabilities uncovered in March.
The group was discovered to be using Exchange bugs to mine for cryptocurrency in May, two years after it first emerged.
Notably, the group behind LemonDuck is taking advantage of high-profile security bugs by exploiting older vulnerabilities during periods where security teams are focussed on patching critical flaws, and even removing rival malware. Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/topic/securite-pc-et-internet
|
|
Scooped by
Gust MEES
March 16, 2021 5:11 PM
|
Three recently unearthed vulnerabilities in the Linux kernel, located in the iSCSI module used for accessing shared data storage facilities, could allow root privileges to anyone with a user account.
The trio of flaws – CVE-2021-27363, CVE-2021-27364 and CVE-2021-27365 – have lurked in Linux code since 2006 without detection until GRIMM researchers discovered them.
“If you already had execution on a box, either because you have a user account on the machine, or you’ve compromised some service that doesn’t have repaired permissions, you can do whatever you want basically,” said Adam Nichols, principal of the Software Security practice at GRIMM.
While the vulnerabilities “are in code that is not remotely accessible, so this isn’t like a remote exploit,” said Nichols, they are still troublesome. They take “any existing threat that might be there. It just makes it that much worse,” he explained. “And if you have users on the system that you don’t really trust with root access it, it breaks them as well.”
Referring to the theory that ‘many eyes make all bugs shallow,’ Linux code “is not getting many eyes or the eyes are looking at it and saying that seems fine,” said Nichols. “But, [the bugs] have been in there since the code was first written, and they haven’t really changed over the last 15 years.” Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux
|
|
Scooped by
Gust MEES
March 12, 2021 12:38 PM
|
Researchers say the new RedXOR backdoor is targeting Linux systems with various data exfiltration and network traffic tunneling capabilities.
Researchers have discovered a new backdoor targeting Linux systems, which they link back to the Winnti threat group.
The backdoor is called RedXOR – in part because its network data-encoding scheme is based on the XOR encryption algorithm, and in part because its samples were found on an old release of the Red Hat Enterprise Linux platform. The latter fact provides a clue that RedXOR is utilized in targeted attacks against legacy Linux systems, noted researchers.
The malware has various malicious capabilities, said researchers – from exfiltrating data to tunneling network traffic to another destination. Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux
|
|
Scooped by
Gust MEES
February 24, 2021 3:11 PM
|
CERTFR-2021-AVI-138 : Multiples vulnérabilités dans le noyau Linux de SUSE (22 février 2021)
De multiples vulnérabilités ont été découvertes dans le noyau Linux de SUSE. Certaines d'entre elles permettent à un attaquant de provoquer un problème de sécurité non spécifié par l'éditeur, une exécution de code arbitraire et un déni de service. Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux
|
|
Scooped by
Gust MEES
February 3, 2021 7:53 AM
|
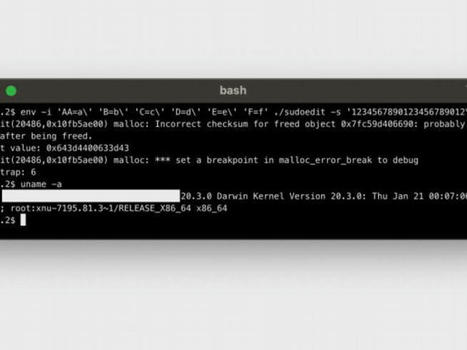
A British security researcher has discovered today that a recent security flaw in the Sudo app also impacts the macOS operating system, and not just Linux and BSD, as initially believed.
The vulnerability, disclosed last week as CVE-2021-3156 (aka Baron Samedit) by security researchers from Qualys, impacts Sudo, an app that allows admins to delegate limited root access to other users.
Qualys researchers discovered that they could trigger a "heap overflow" bug in the Sudo app to change the current user's low-privileged access to root-level commands, granting the attacker access to the whole system.
The only condition to exploit this bug was that an attacker gain access to a system, which researchers said could be done by either planting malware on a device or brute-forcing a low-privileged service account. Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux
|
|
Scooped by
Gust MEES
January 27, 2021 6:37 AM
|
A major vulnerability impacting a large chunk of the Linux ecosystem has been patched today in Sudo, an app that allows admins to delegate limited root access to other users.
The vulnerability, which received a CVE identifier of CVE-2021-3156, but is more commonly known as "Baron Samedit," was discovered by security auditing firm Qualys two weeks ago and was patched earlier today with the release of Sudo v1.9.5p2.
In a simple explanation provided by the Sudo team today, the Baron Samedit bug can be exploited by an attacker who has gained access to a low-privileged account to gain root access, even if the account isn't listed in /etc/sudoers — a config file that controls which users are allowed access to su or sudo commands in the first place. Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux
|







A pervasive cyber-espionage group known as Iron Tiger, believed to be out of China, has updated one of its malware frameworks to attack Linux-based systems.
Researchers at Trend Micro recently discovered that Iron Tiger (aka Emissary Panda or APT27) had added new features to its so called SysUpdate malware family, which allows it to infect Linux platforms in addition to Windows. SysUpdate abuses system services, grabs screenshots, browses and terminates processes, retrieves drive information, executes commands, and can find, delete, rename, upload, and download files as well as peruse a victim's file directory.
Learn more / En savoir plus / Mehr erfahren:
https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux