 Your new post is loading...

|
Scooped by
Gust MEES
October 10, 2024 8:23 AM
|
|
|
Scooped by
Gust MEES
September 7, 2023 10:08 AM
|
The fake TradingView website is hosted on trabingviews[.]com, with special font characters being used to make it look like the legitimate domain and help it avoid detection.
The malicious website is designed to look authentic, claiming to offer downloads for the TradingView app’s Windows, macOS and Linux versions.
While the Windows and Linux files deliver the NetSupport RAT, the Mac file delivers the AMOS malware. Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/topic/securite-pc-et-internet
|
|
Scooped by
Gust MEES
January 27, 2022 2:45 PM
|
North Korean-backed hacking group Lazarus has added the Windows Update client to its list of living-off-the-land binaries (LoLBins) and is now actively using it to execute malicious code on Windows systems.
The new malware deployment method was discovered by the Malwarebytes Threat Intelligence team while analyzing a January spearphishing campaign impersonating the American security and aerospace company Lockheed Martin.
After the victims open the malicious attachments and enable macro execution, an embedded macro drops a WindowsUpdateConf.lnk file in the startup folder and a DLL file (wuaueng.dll) in a hidden Windows/System32 folder. Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/topic/securite-pc-et-internet/?&tag=Windows
|
|
Scooped by
Gust MEES
July 27, 2021 6:15 AM
|
Microsoft is warning customers about the LemonDuck crypto mining malware which is targeting both Windows and Linux systems and is spreading via phishing emails, exploits, USB devices, and brute force attacks, as well as attacks targeting critical on-premise Exchange Server vulnerabilities uncovered in March.
The group was discovered to be using Exchange bugs to mine for cryptocurrency in May, two years after it first emerged.
Notably, the group behind LemonDuck is taking advantage of high-profile security bugs by exploiting older vulnerabilities during periods where security teams are focussed on patching critical flaws, and even removing rival malware. Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/topic/securite-pc-et-internet
|
|
Scooped by
Gust MEES
July 2, 2021 9:28 AM
|
Microsoft has assigned CVE-2021-34527 to the print spooler remote code execution vulnerability known as "PrintNightmare" and confirmed that the offending code is lurking in all versions of Windows.
The megacorp said it was still investigating whether the vulnerability was exploitable in every version, but domain controllers are indeed affected.
Microsoft also confirmed that this nasty was distinct from CVE-2021-1675, which was all about a different attack vector and a different vulnerability in RpcAddPrinterDriverEx(). The June 2021 Security update dealt with that, according to Microsoft, and did not introduce the new badness. That had existed prior to the update.
The Windows giant also confirmed that the PrintNightmare vulnerability was being exploited in the wild. Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/topic/securite-pc-et-internet/?&tag=Windows https://www.scoop.it/topic/securite-pc-et-internet/?&tag=PrintNightmare
|
|
Scooped by
Gust MEES
March 24, 2021 9:43 AM
|
An upgraded variant of Purple Fox malware with worm capabilities is being deployed in an attack campaign that is rapidly expanding.
Purple Fox, first discovered in 2018, is malware that used to rely on exploit kits and phishing emails to spread. However, a new campaign taking place over the past several weeks -- and which is ongoing -- has revealed a new propagation method leading to high infection numbers.
In a blog post on Tuesday, Guardicore Labs said that Purple Fox is now being spread through "indiscriminate port scanning and exploitation of exposed SMB services with weak passwords and hashes. Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/topic/securite-pc-et-internet/?&tag=Malware
|
|
Scooped by
Gust MEES
August 12, 2019 10:41 AM
|
Researchers discovered multiple flaws in more than 40 device drivers from at least 20 different vendors that could to install a persistent backdoor on Windows PCs.
Experts at firmware security firm Eclypsium have conducted a study on the device drivers from major vendors and discovered serious issues in over 40 drivers from 20 companies.
The researchers warn that the vulnerabilities that can be exploited by attackers to deploy persistent backdoor on vulnerable systems.
Flawed drivers were developed by several major vendors, including ASUS, Toshiba, Intel, NVIDIA, and Huawei, below the complete list: Learn more / En savooir plus / Mehr erfahren: https://www.scoop.it/topic/securite-pc-et-internet
|
|
Scooped by
Gust MEES
July 18, 2019 9:29 AM
|
Wie Forscher herausgefunden haben, gibt es ein massives Sicherheitsproblem bei Bluetooth. Geräte sind dadurch von Angreifern leicht zu verfolgen.
Forscher der Boston University haben einen Fehler im Kommunikationsprotokoll von Bluetooth entdeckt, durch den die meisten Geräte von Dritten getrackt werden können und Daten verloren gehen.
In dem Forschungsbericht, der unter dem Namen „Tracking Anonymized Bluetooth Devices“ erschien und von den Forschern Johannes K. Becker und David Starobinski herausgegeben wurde, wird die Sicherheitsanfälligkeit von Bluetooth-Geräten detailliert beschrieben. Betroffen sein können Geräte, die Windows 10, iOS und macOS nutzen, sowie Smartwatches von Apple und Fitbit. Learn more / En savoir plus / Mehr erfahren: http://www.scoop.it/t/securite-pc-et-internet/?&tag=Bluetooth
|
|
Scooped by
Gust MEES
February 4, 2018 10:48 AM
|
Sicherheitsexperten von Proofpoint untersuchten das Mining-Botnet Smominru, das auf mehr als 500.000 Windows-Maschinen die Kryptowährung Minero schürft.
Nach Erkenntnissen von Sicherheitsexperten der Firma Proofpoint missbrauchen Kriminelle die Rechenleistung von mehr als einer halben Million Windows-Systemen, um die Kryptowährung Minero zu "schürfen". Laut Proofpoint handelt es sich bei den befallenen Maschinen vor allem um Windows-Server, von denen viele in Russland, Indien, Taiwan und der Ukraine laufen. Im Beobachtungszeitraum von Mai 2017 bis Januar 2018 hätten die Angreifer Mineros im Wert von rund 3,6 Millionen US-Dollar ergattert.
Server unbrauchbar
Auf den Stromkosten bleiben die Geschädigten sitzen, außerdem vermuten die Sicherheitsforscher, dass viele der befallenen Server wegen der zusätzlichen Rechenlast nur noch eingeschränkt funktionieren. Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/t/securite-pc-et-internet/?&tag=crypto-currency https://www.scoop.it/t/securite-pc-et-internet/?&tag=cryptojacking
|
|
Scooped by
Gust MEES
January 4, 2018 9:48 AM
|
Microsoft has warned users that its patches for the dangerous Meltdown CPU bug won't reach them if their third-party antivirus hasn't been updated to support this week's Windows security update.
By now Windows users should have received the patches Microsoft released yesterday to plug the widespread Meltdown bug and its companion Spectre, which expose most computers and phones to speculative execution side-channel attacks that affect chips from Intel, AMD, and Arm.
Microsoft released software updates for Internet Explorer, Microsoft Edge, Windows, and SQL Server, but customers will also need to apply firmware updates from their respective hardware vendors too.
Surface and Surface Book users can expect an automatic firmware update from Microsoft but those with other hardware will need to check with their vendors. Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/t/securite-pc-et-internet/?&tag=Meltdown+and+Spectre+Attacks
|
|
Scooped by
Gust MEES
August 27, 2017 11:51 AM
|
Une note de sécurité du Kaspersky Lab, sur sa plateforme SecureList, met en garde contre un malware multiplateforme qui se répand via Facebook Messenger.
Pratiquement, le malware vous envoie un message sur Messenger, sous l'identité d'un ami... Learn more / En savoir plus / Mehr erfahren: http://www.scoop.it/t/securite-pc-et-internet/?&tag=Facebook
|
|
Scooped by
Gust MEES
February 22, 2017 12:18 PM
|
Mirai n’a pas dit son dernier mot. Les éditeurs d’antivirus Dr Web et Kaspersky communiquent ainsi sur une nouvelle version du fameux malware, visant cette fois-ci des machines sous Windows. Dr. Web a été le premier à tirer la sonnette d’alarme au début du mois de février, suivi de près par Kaspersky.
Baptisé trojan.mirai1 par Dr Web, ce malware infecte les machines sous Windows en utilisant des vecteurs classiques, type pièce jointe malveillante ou macro Office. Une fois la machine infectée par le trojan, celui-ci va scanner le réseau local à la recherche d’objets connectés fonctionnant sous Linux. Puis il va utiliser ceux-ci afin de les infecter avec une variante de Mirai, et ceux-ci seront ajoutés au botnet des cybercriminels qui peuvent alors les utiliser pour lancer des attaques DDoS. Learn more / En savoir plus / Mehr erfahren: http://www.scoop.it/t/securite-pc-et-internet/?&tag=Botnet http://www.scoop.it/t/securite-pc-et-internet/?&tag=Botnet&tag=Mirai+Botnet
|
|
Scooped by
Gust MEES
November 21, 2016 6:33 PM
|
A proof of concept from security researcher and software developer Samy Kamkar shows that macOS, Windows, and Linux computers can have any previously active Web logins hijacked merely by plugging in a tiny Unix device via USB or Thunderbolt, even if the computer is locked and password protected, and possibly even when it seems to be asleep. It can also hijack many router brands on the same network.
PoisonTap exploits several interlocked network and browser design features, rather than relying on an operating system, hardware, or browser flaw. This will make it harder to root out and resolve. Kamkar said in an interview, “The interesting attacks to me are by design: how do you exploit the protocol rather than a single buffer overflow that gets patched the next day.” Learn more / En savoir plus / Mehr erfahren: http://www.scoop.it/t/securite-pc-et-internet/?tag=Samy+KAMKAR http://www.scoop.it/t/securite-pc-et-internet/?tag=Raspberry+PI
|
|
|
Scooped by
Gust MEES
December 20, 2023 12:02 PM
|
|
|
Scooped by
Gust MEES
June 3, 2023 9:39 AM
|
Neue Gefahr für Windows-Nutzer: Wie unter anderem "Bleeping Computer" berichtet, wird in Hacker-Foren aktuell ein Tool verkauft, das sich "Terminator" nennt. Kriminelle zahlen dem Portal zufolge bis zu 3.000 US-Dollar für die offenbar sehr effektive Software. Der Entwickler nennt sich in den Foren selbst "Spyboy".
Was "Terminator" so gefährlich macht: Das Tool ist offenbar in der Lage, 24 weitverbreitete Antivirus-, Endpoint Detection and Response- und Extended Detection and Response-Sicherheitsanwendungen zu umgehen. Davon ist offenbar auch der Windows Defender betroffen. Angreifbar sind alle Systeme ab Windows 7.
Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/topic/securite-pc-et-internet
|
|
Scooped by
Gust MEES
August 3, 2021 6:53 AM
|
Microsoft has continued its analysis of the LemonDuck malware, known for installing crypto-miners in enterprise environments. It makes a strong case for why it is worth removing it from your network.
This group, according to Microsoft, has a well-stocked arsenal of hacking tools, tricks and exploits aimed at one thing: for their malware to retain exclusive access to a compromised network for as long as possible.
While crypto-mining malware could be just a nuisance, LemonDuck attributes suggest the attacker group really do try to own compromised networks by disabling anti-malware, removing rival malware, and even automatically patching vulnerabilities -- a competitive effort to keep rival attackers from feeding off its turf. Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/topic/securite-pc-et-internet
|
|
Scooped by
Gust MEES
July 7, 2021 11:14 AM
|
Microsoft hat Notfallpatches für eine Sicherheitslücke mit dem Namen Printnightmare veröffentlicht. Ein Problem mit dem Druck-Spooler ermöglichte es Angreifern, Code aus der Ferne auszuführen.
Über die Remote Code Execution könnten Angreifer weitere Programme installieren oder Nutzerkonten mit Administratorrechten erstellen. Zunächst war für das Problem kein Patch verfügbar. Offenbar veröffentlichten Sicherheitsforscher versehentlich einen Proof-of-Concept für einen Exploit, der sich weiterhin ausnutzen ließ. Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/topic/securite-pc-et-internet/?&tag=Windows https://www.scoop.it/topic/securite-pc-et-internet/?&tag=PrintNightmare
|
|
Scooped by
Gust MEES
June 25, 2021 4:14 PM
|
Researchers have discovered a strain of cryptocurrency-mining malware that abuses Windows Safe mode during attacks.
After finding reports on Reddit of Avast antivirus users querying the sudden loss of the antivirus software from their system files, the team conducted an investigation into the situation, realizing it was due to a malware infection.
Crackonosh has been in circulation since at least June 2018. Once a victim executes a file they believe to be a cracked version of legitimate software, the malware is also deployed. Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/t/securite-pc-et-internet/?&tag=crypto-currency
|
|
Scooped by
Gust MEES
May 28, 2020 5:56 PM
|
Mittels automatisierter Tests, so genanntem Fuzzing, haben Sicherheitsforscher insgesamt 26 Programmierfehler in USB-Treibern entdeckt. 18 davon betreffen verschiedene Linux-Kernelversionen; wiederum zehn dieser Linux-Bugs erhielten aufgrund von ihnen ausgehender hoher Sicherheitsrisiken CVE-Nummern. Vier weitere Bugs betreffen Windows 8 und 10, drei stecken in macOS 10.15 Catalina und einer im freien BSD-Derivat FreeBSD 12. Learn more / En savoir plus / Mehr erfahren: http://www.scoop.it/t/securite-pc-et-internet/?tag=USB
|
|
Scooped by
Gust MEES
August 8, 2019 5:24 PM
|
The popular Steam game client for Windows has a zero-day privilege escalation vulnerability that can allow an attacker with limited permissions to run a program as an administrator
Privilege escalation vulnerabilities are bugs that enable a user with limited rights to launch an executable with elevated, or administrative privileges. As Steam has over 100 million registered users and millions of them playing at a time, this is a serious risk that could be abused by malware to perform a variety of unwanted activities. Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/topic/securite-pc-et-internet/?&tag=Games
|
|
Scooped by
Gust MEES
February 4, 2018 11:47 AM
|
|
|
Scooped by
Gust MEES
January 7, 2018 12:37 PM
|
Microsoft has warned users that its patches for the dangerous Meltdown CPU bug won't reach them if their third-party antivirus hasn't been updated to support this week's Windows security update.
By now Windows users should have received the patches Microsoft released yesterday to plug the widespread Meltdown bug and its companion Spectre, which expose most computers and phones to speculative execution side-channel attacks that affect chips from Intel, AMD, and Arm.
Microsoft released software updates for Internet Explorer, Microsoft Edge, Windows, and SQL Server, but customers will also need to apply firmware updates from their respective hardware vendors too.
Surface and Surface Book users can expect an automatic firmware update from Microsoft but those with other hardware will need to check with their vendors. Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/t/securite-pc-et-internet/?&tag=Meltdown+and+Spectre+Attacks https://gustmeesde.wordpress.com/2014/12/16/browser-sind-das-einfallstor-fur-malware-sind-eure-browser-up-to-date/ https://gustmeesde.wordpress.com/2014/12/26/programme-die-auf-jeden-neuen-pc-und-smartphones-gehoren/
|
|
Scooped by
Gust MEES
November 26, 2017 10:47 AM
|
Aktuell häufen sich im Netz sich erneut Beschwerden von Usern, die von angeblichen Microsoft-Mitarbeitern angerufen wurden. Ihre Windows-Lizenz sei "abgelaufen". Dabei handelt es sich um eine bereits bekannte Betrugsmasche, vor der nun sogar die Polizei warnt. Sollte "Microsoft" demnächst bei Ihnen anrufen, legen Sie am besten sofort auf.
Hallo, hier Microsoft: Bitte bezahlen!
Offenbar macht eine bereits bekannte Telefonbetrugs-Masche derzeit wieder die Runde - wodurch die Polizeistelle in Aachen sich gezwungen sah, eine offizielle Warnung herauszugeben. Über 100 Menschen meldeten in den letzten Tagen demnach Anrufe von angeblichen Microsoft-Mitarbeitern.
Learn more / En savoir plus / Mehr erfahren: https://www.scoop.it/t/securite-pc-et-internet/?&tag=Awareness https://www.scoop.it/t/securite-pc-et-internet/?&tag=Arnaques
|
|
Scooped by
Gust MEES
March 30, 2017 3:03 PM
|
Une anomalie de sécurité précédemment non divulguée dans un ancien serveur Web Windows ne sera pas corrigée, même si des centaines de milliers de serveurs exécutent encore le logiciel obsolète.
La vulnérabilité dans Internet Information Services (IIS 6) a été exploitée à distance depuis juillet dernier, selon deux chercheurs en sécurité d'une université de technologie chinoise. Ces derniers ont d'ailleurs publié cette semaine le PoC d'un exploit sur Github.
La version touchée d'IIS 6 a été livrée pour la première fois avec Windows Server 2003, mais n'est plus supportée depuis 2015.
Microsoft a fait savoir que par conséquent, il ne corrigerait probablement pas cette faille.
"Ce problème n'affecte pas les versions actuellement supportées" a déclaré un porte-parole de Microsoft. "Nous continuons à recommander aux clients de migrer vers nos derniers systèmes d'exploitation et de bénéficier d'une protection robuste et moderne."
Plus de 600.000 anciens serveurs IIS 6 sont toujours utilisés, principalement aux Etats-Unis et en Chine, d'après une recherche sur Shodan, un moteur de recherche pour les terminaux connectés à Internet. Learn more / En savoir plus / Mehr erfahren: http://www.scoop.it/t/securite-pc-et-internet/
|
|
Scooped by
Gust MEES
February 10, 2017 3:49 PM
|
Mit einem einfachen Trick greift der MacDownloader Passwörter ab. Die Malware soll es auf Mitarbeiter von US-Rüstungsfirmen und Menschenrechtler abgesehen haben. Getarnt als Adobe-Flash-Installer und Entfernungs-Tool für Adware von Bitdefender versucht die Malware MacDownloader, Passwörter an seine Urheber weiterzuleiten. Das schreiben die beiden Sicherheitsforscher Claudio Guarnieri und Collin Anderson in einem Bericht. Tarnung: Die Malware gibt sich als Flashplayer aus. (Quelle: iranthreats.github.io) Nach der Installation versucht der MacDownloader, mithilfe eines gefälschten System-Dialogs, an die Passwörter der Opfer zu kommen, und leitet den Apple-Schlüsselbund schließlich an die Angreifer weiter. Diese sollen aus dem Iran stammen, so die Sicherheitsforscher. Learn more / En savoir plus / Mehr erfahren:
|


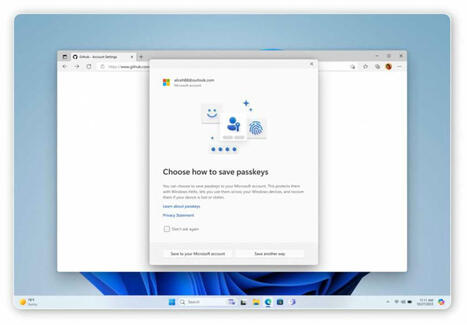










Windows 11 now supports third-party passkeys and cleaner passkey saving via Windows Hello.
Learn more / En savoir plus / Mehr erfahren:
https://www.scoop.it/topic/securite-pc-et-internet
https://www.scoop.it/topic/securite-pc-et-internet/?&tag=PassKey