ICT Security-Sécurité PC et Internet
114.1K views | +0 today
ICT Security-Sécurité PC et Internet
ICT Security + Privacy + Piracy + Data Protection - Censorship - Des cours et infos gratuites sur la"Sécurité PC et Internet" pour usage non-commercial... (FR, EN+DE)...
Curated by Gust MEES
Your new post is loading...
Scooped by Gust MEES
October 16, 4:39 PM
Scoop.it!

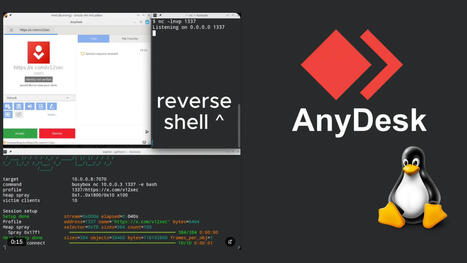
AnyDesk Linux Flaw Lets Remote Attackers Execute Code as Root Without Authentication

AnyDesk Linux Flaw Lets Remote Attackers Execute Code as Root Without Authentication | ICT Security-Sécurité PC et Internet | Scoop.it

A working proof-of-concept for a serious AnyDesk Linux vulnerability that can let remote attackers run commands as root without authentication or user approval.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux


Gust MEES's insight:

A working proof-of-concept for a serious AnyDesk Linux vulnerability that can let remote attackers run commands as root without authentication or user approval.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux


No comment yet.
Scooped by Gust MEES
August 5, 5:32 PM
Scoop.it!

New OVSwrap Linux Vulnerability Lets Attackers Gain Root Access

A newly disclosed Linux kernel vulnerability, tracked as CVE-2026-64531 and dubbed OVSwrap, allows unprivileged local users to escalate privileges to root on a wide range of popular Linux distributions.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux


Gust MEES's insight:

A newly disclosed Linux kernel vulnerability, tracked as CVE-2026-64531 and dubbed OVSwrap, allows unprivileged local users to escalate privileges to root on a wide range of popular Linux distributions.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux


No comment yet.
Scooped by Gust MEES
May 20, 6:57 PM
Scoop.it!

PinTheft Linux Vulnerability Let Attackers Gain Root Access - PoC Released

PinTheft Linux Vulnerability Let Attackers Gain Root Access - PoC Released | ICT Security-Sécurité PC et Internet | Scoop.it

A proof-of-concept (PoC) exploit was published for a new Linux Local Privilege Escalation (LPE) vulnerability dubbed “PinTheft.” Exploitvulnerability assessment

Discovered by Aaron Esau of the V12 security team, the flaw allows local attackers to gain root access by exploiting an RDS zerocopy double-free bug.

A kernel patch is currently available, prompting the researchers to release their PoC code to the public.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux


Gust MEES's insight:

A proof-of-concept (PoC) exploit was published for a new Linux Local Privilege Escalation (LPE) vulnerability dubbed “PinTheft.” Exploitvulnerability assessment

Discovered by Aaron Esau of the V12 security team, the flaw allows local attackers to gain root access by exploiting an RDS zerocopy double-free bug.

A kernel patch is currently available, prompting the researchers to release their PoC code to the public.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux


No comment yet.
Scooped by Gust MEES
May 16, 7:15 PM
Scoop.it!

The third major Linux kernel flaw in two weeks has been found - thanks to AI

The third major Linux kernel flaw in two weeks has been found - thanks to AI | ICT Security-Sécurité PC et Internet | Scoop.it

AI is exposing Linux security holes faster than developers can patch them. Fragnesia is the latest. Here's what we know about it.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux


Gust MEES's insight:

AI is exposing Linux security holes faster than developers can patch them. Fragnesia is the latest. Here's what we know about it.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux


No comment yet.
Scooped by Gust MEES
May 16, 6:32 PM
Scoop.it!

« Dirty Frag » : une nouvelle faille dangereuse sous Linux 

« Dirty Frag » : une nouvelle faille dangereuse sous Linux  | ICT Security-Sécurité PC et Internet | Scoop.it

Cette faille du noyau Linux met les responsables de la sécurité en émoi. Voici les systèmes concernés et les mesures à prendre sans tarder.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux


Gust MEES's insight:

Cette faille du noyau Linux met les responsables de la sécurité en émoi. Voici les systèmes concernés et les mesures à prendre sans tarder.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux


No comment yet.
Scooped by Gust MEES
May 15, 8:36 AM
Scoop.it!

New Fragnesia Linux Kernel LPE Grants Root Access via Page Cache Corruption

New Fragnesia Linux Kernel LPE Grants Root Access via Page Cache Corruption | ICT Security-Sécurité PC et Internet | Scoop.it

Details have emerged about a new variant of the recent Dirty Frag Linux local privilege escalation (LPE) vulnerability that allows local attackers to gain root access, making it the third such bug to be identified in the kernel within a span of two weeks.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux


Gust MEES's insight:

Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux


No comment yet.
Scooped by Gust MEES
April 30, 9:34 AM
Scoop.it!

Linux Kernel 0-Day "Copy Fail" Roots Every Major Distribution Since 2017

A critical zero-day vulnerability in the Linux kernel has been publicly disclosed, enabling any unprivileged local user to obtain root access on virtually every major Linux distribution shipped since 2017.

Dubbed “Copy Fail” and tracked as CVE-2026-31431, the flaw was discovered by Theori researcher Taeyang Lee and scaled into a full exploit chain by the Xint Code Research Team using AI-assisted analysis.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux


Gust MEES's insight:

A critical zero-day vulnerability in the Linux kernel has been publicly disclosed, enabling any unprivileged local user to obtain root access on virtually every major Linux distribution shipped since 2017.

Dubbed “Copy Fail” and tracked as CVE-2026-31431, the flaw was discovered by Theori researcher Taeyang Lee and scaled into a full exploit chain by the Xint Code Research Team using AI-assisted analysis.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux


No comment yet.
Scooped by Gust MEES
October 15, 2024 2:25 PM
Scoop.it!

New Linux Variant of FASTCash Malware Targets Payment Switches in ATM Heists

New Linux Variant of FASTCash Malware Targets Payment Switches in ATM Heists | ICT Security-Sécurité PC et Internet | Scoop.it

North Korean hackers deploy Linux-based FASTCash malware to exploit ATMs globally, enabling fraudulent withdrawals.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux


Gust MEES's insight:

North Korean hackers deploy Linux-based FASTCash malware to exploit ATMs globally, enabling fraudulent withdrawals.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux


No comment yet.
Scooped by Gust MEES
September 26, 2024 3:42 PM
Scoop.it!

Doomsday 9.9 unauthenticated RCE bug affects 'all Linux'

Doomsday 9.9 unauthenticated RCE bug affects 'all Linux' | ICT Security-Sécurité PC et Internet | Scoop.it

No fix yet plus criticalness plus uncertainty plus talk of example exploit equals nightmare
Jessica Lyons


Details about an as-yet-non-public critical 9.9-out-of-10-severity unauthenticated remote-code execution vulnerability affecting all GNU/Linux systems could be revealed today.

That's according to software developer Simone Margaritelli, who says there's still no fix for the decade-old flaw he disclosed to developers three weeks ago. If it is as described, the bug could be used to hijack Linux-based systems from across the internet or network.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux


Gust MEES's insight:

No fix yet plus criticalness plus uncertainty plus talk of example exploit equals nightmare
Jessica Lyons


Details about an as-yet-non-public critical 9.9-out-of-10-severity unauthenticated remote-code execution vulnerability affecting all GNU/Linux systems could be revealed today.

That's according to software developer Simone Margaritelli, who says there's still no fix for the decade-old flaw he disclosed to developers three weeks ago. If it is as described, the bug could be used to hijack Linux-based systems from across the internet or network.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux


No comment yet.
Scooped by Gust MEES
September 12, 2023 11:33 AM
Scoop.it!

Free Download Manager site redirected Linux users to malware for years

Free Download Manager site redirected Linux users to malware for years | ICT Security-Sécurité PC et Internet | Scoop.it

A reported Free Download Manager supply chain attack redirected Linux users to a malicious Debian package repository that installed information-stealing malware.

The malware used in this campaign establishes a reverse shell to a C2 server and installs a Bash stealer that collects user data and account credentials.

Kaspersky discovered the potential supply chain compromise case while investigating suspicious domains, finding that the campaign has been underway for over three years.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux


Gust MEES's insight:

A reported Free Download Manager supply chain attack redirected Linux users to a malicious Debian package repository that installed information-stealing malware.

The malware used in this campaign establishes a reverse shell to a C2 server and installs a Bash stealer that collects user data and account credentials.

Kaspersky discovered the potential supply chain compromise case while investigating suspicious domains, finding that the campaign has been underway for over three years.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux


No comment yet.
Scooped by Gust MEES
August 15, 2023 3:59 PM
Scoop.it!

Monti Ransomware Returns with New Linux Variant and Enhanced Evasion Tactics

Monti Ransomware Returns with New Linux Variant and Enhanced Evasion Tactics | ICT Security-Sécurité PC et Internet | Scoop.it

The threat actors behind the Monti ransomware have resurfaced after a two-month break with a new Linux version of the encryptor in its attacks targeting government and legal sectors.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux


Gust MEES's insight:

The threat actors behind the Monti ransomware have resurfaced after a two-month break with a new Linux version of the encryptor in its attacks targeting government and legal sectors.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux


No comment yet.
Scooped by Gust MEES
July 13, 2023 8:33 AM
Scoop.it!

Angriff ohne Spuren: Kryptomining-Malware versteckt sich ausschließlich im Ram 

Angriff ohne Spuren: Kryptomining-Malware versteckt sich ausschließlich im Ram  | ICT Security-Sécurité PC et Internet | Scoop.it

Kryptomining-Malware versteckt sich ausschließlich im Ram
Ein Python-Skript namens Pyloose hat es auf Linux-Systeme abgesehen, um direkt aus dem Arbeitsspeicher heraus Kryptowährungen zu schürfen.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux


Gust MEES's insight:

Kryptomining-Malware versteckt sich ausschließlich im Ram
Ein Python-Skript namens Pyloose hat es auf Linux-Systeme abgesehen, um direkt aus dem Arbeitsspeicher heraus Kryptowährungen zu schürfen.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux


No comment yet.
Scooped by Gust MEES
May 9, 2023 12:54 PM
Scoop.it!

New Linux kernel NetFilter flaw gives attackers root privileges

New Linux kernel NetFilter flaw gives attackers root privileges | ICT Security-Sécurité PC et Internet | Scoop.it

A new Linux NetFilter kernel flaw has been discovered, allowing unprivileged local users to escalate their privileges to root level, allowing complete control over a system.

The CVE-2023-32233 identifier has been reserved for the vulnerability, but a severity level is yet to be determined.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux


Gust MEES's insight:

A new Linux NetFilter kernel flaw has been discovered, allowing unprivileged local users to escalate their privileges to root level, allowing complete control over a system.

The CVE-2023-32233 identifier has been reserved for the vulnerability, but a severity level is yet to be determined.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux


No comment yet.
Scooped by Gust MEES
August 7, 2:46 PM
Scoop.it!

18-Year-Old Linux SCTP Flaw Could Let Local Users Gain Root and Escape Containers

18-Year-Old Linux SCTP Flaw Could Let Local Users Gain Root and Escape Containers | ICT Security-Sécurité PC et Internet | Scoop.it

A use-after-free bug in Linux's SCTP networking code can be turned into full root on a host, and Tencent researchers say they used it to escape a container and reach the machine underneath.

The flaw has existed since 2008. The fix already shipped: stable kernels 7.1.6, 6.18.42, 6.12.101 and 6.6.148, released August 3, close it. Anyone running an older kernel with SCTP reachable should update.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux


Gust MEES's insight:

A use-after-free bug in Linux's SCTP networking code can be turned into full root on a host, and Tencent researchers say they used it to escape a container and reach the machine underneath.

The flaw has existed since 2008. The fix already shipped: stable kernels 7.1.6, 6.18.42, 6.12.101 and 6.6.148, released August 3, close it. Anyone running an older kernel with SCTP reachable should update.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux


No comment yet.
Scooped by Gust MEES
July 8, 8:39 AM
Scoop.it!

15-Year-Old GhostLock Flaw Enables Root and Container Escape on Most Linux Distros

15-Year-Old GhostLock Flaw Enables Root and Container Escape on Most Linux Distros | ICT Security-Sécurité PC et Internet | Scoop.it

Researchers at Nebula Security have disclosed GhostLock (CVE-2026-43499), a 15-year-old Linux kernel flaw that lets any logged-in user take full root control of a machine that has not been patched.

The vulnerable code has shipped by default in essentially every mainstream distribution since 2011. The flaw needs no special permission, no unusual settings, and no network access; ordinary threading calls from any local program are enough.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux


Gust MEES's insight:

Researchers at Nebula Security have disclosed GhostLock (CVE-2026-43499), a 15-year-old Linux kernel flaw that lets any logged-in user take full root control of a machine that has not been patched.

The vulnerable code has shipped by default in essentially every mainstream distribution since 2011. The flaw needs no special permission, no unusual settings, and no network access; ordinary threading calls from any local program are enough.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux


No comment yet.
Scooped by Gust MEES
May 18, 4:15 AM
Scoop.it!

Exploit available for new DirtyDecrypt Linux root escalation flaw

Exploit available for new DirtyDecrypt Linux root escalation flaw | ICT Security-Sécurité PC et Internet | Scoop.it

A recently patched local privilege escalation vulnerability in the Linux kernel's rxgk module now has a proof-of-concept exploit that allows attackers to gain root access on some Linux systems.

Named DirtyDecrypt and also known as DirtyCBC, this security flaw was also autonomously found and reported by the V12 security team earlier this month, when the maintainers informed them that it was a duplicate that had already been patched in the mainline.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux


Gust MEES's insight:

A recently patched local privilege escalation vulnerability in the Linux kernel's rxgk module now has a proof-of-concept exploit that allows attackers to gain root access on some Linux systems.

Named DirtyDecrypt and also known as DirtyCBC, this security flaw was also autonomously found and reported by the V12 security team earlier this month, when the maintainers informed them that it was a duplicate that had already been patched in the mainline.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux


No comment yet.
Scooped by Gust MEES
May 16, 6:58 PM
Scoop.it!

The 4th Linux kernel flaw this month can lead to stolen SSH host keys

The 4th Linux kernel flaw this month can lead to stolen SSH host keys | ICT Security-Sécurité PC et Internet | Scoop.it

The good news is there's already a patch. The bad news is that the fix isn't available for all Linux distributions yet. Here's what you can do in the meantime.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux


Gust MEES's insight:

The good news is there's already a patch. The bad news is that the fix isn't available for all Linux distributions yet. Here's what you can do in the meantime.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux


No comment yet.
Scooped by Gust MEES
May 16, 7:38 AM
Scoop.it!

Critical Linux Kernel Flaw 'ssh-keysign-pwn' Exposes SSH Keys and Shadow Passwords

A newly disclosed Linux kernel vulnerability is raising serious concerns across the security community, as it allows attackers to access highly sensitive data, including SSH private keys and password hashes, on affected systems.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux


Gust MEES's insight:

A newly disclosed Linux kernel vulnerability is raising serious concerns across the security community, as it allows attackers to access highly sensitive data, including SSH private keys and password hashes, on affected systems.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux


No comment yet.
Scooped by Gust MEES
May 15, 8:04 AM
Scoop.it!

Fragnesia - New Linux Kernel Vulnerability Enables Root Access

A newly disclosed Linux kernel vulnerability dubbed Fragnesia allows any local unprivileged user to escalate privileges to root without requiring a race condition, making it one of the more reliable local privilege escalation exploits seen in recent years.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux


Gust MEES's insight:

A newly disclosed Linux kernel vulnerability dubbed Fragnesia allows any local unprivileged user to escalate privileges to root without requiring a race condition, making it one of the more reliable local privilege escalation exploits seen in recent years.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux


No comment yet.
Scooped by Gust MEES
April 27, 5:01 AM
Scoop.it!

„Pack2TheRoot“: Sicherheitslücke betrifft mehrere Linux-Distributionen

„Pack2TheRoot“: Sicherheitslücke betrifft mehrere Linux-Distributionen | ICT Security-Sécurité PC et Internet | Scoop.it

Das Telekom-Sicherheitsteam hat die Sicherheitslücke „Pack2TheRoot“ entdeckt, die Rechteausweitung in mehreren Distributionen ermöglicht.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux


Gust MEES's insight:

Das Telekom-Sicherheitsteam hat die Sicherheitslücke „Pack2TheRoot“ entdeckt, die Rechteausweitung in mehreren Distributionen ermöglicht.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux


No comment yet.
Scooped by Gust MEES
October 8, 2024 2:25 PM
Scoop.it!

Linux-Malware "Perfctl" befällt offenbar schon seit Jahren Linux-Server

Linux-Malware "Perfctl" befällt offenbar schon seit Jahren Linux-Server | ICT Security-Sécurité PC et Internet | Scoop.it

Linux-Malware "Perfctl" befällt offenbar schon seit Jahren Linux-Server.
Eine ausgeklügelte Malware befällt massenweise Linux-Server mit falschen Konfigurationen. Das blieb lange unentdeckt, auch wegen der guten Tarnung.


Eine jetzt entdeckte Malware hat es auf Linux-Server abgesehen: Wie die Experten der Cybersecurity-Beratung Aqua Security berichten, ist das Programm namens "Perfctl" vermutlich schon seit 2021 im Umlauf und befällt Linux-Systeme, um diese heimlich als Proxyserver und für Cryptomining zu nutzen. Das Schadprogramm kann auch als Loader für weitere unerwünschte Programme fungieren.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux


Gust MEES's insight:

Linux-Malware "Perfctl" befällt offenbar schon seit Jahren Linux-Server.
Eine ausgeklügelte Malware befällt massenweise Linux-Server mit falschen Konfigurationen. Das blieb lange unentdeckt, auch wegen der guten Tarnung.


Eine jetzt entdeckte Malware hat es auf Linux-Server abgesehen: Wie die Experten der Cybersecurity-Beratung Aqua Security berichten, ist das Programm namens "Perfctl" vermutlich schon seit 2021 im Umlauf und befällt Linux-Systeme, um diese heimlich als Proxyserver und für Cryptomining zu nutzen. Das Schadprogramm kann auch als Loader für weitere unerwünschte Programme fungieren.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux


No comment yet.
Scooped by Gust MEES
February 9, 2024 9:54 AM
Scoop.it!

Bootloader-Lücke gefährdet viele Linux-Distributionen | heise online

Bootloader-Lücke gefährdet viele Linux-Distributionen | heise online | ICT Security-Sécurité PC et Internet | Scoop.it

Bootloader-Lücke gefährdet viele Linux-Distributionen
Im Bootloader shim, der Secure-Boot auch für nicht-Windows-Betriebssysteme erlaubt, klafft eine Sicherheitslücke.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux


Gust MEES's insight:

Bootloader-Lücke gefährdet viele Linux-Distributionen
Im Bootloader shim, der Secure-Boot auch für nicht-Windows-Betriebssysteme erlaubt, klafft eine Sicherheitslücke.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux


No comment yet.
Scooped by Gust MEES
September 7, 2023 10:08 AM
Scoop.it!

'Atomic macOS Stealer' Malware Delivered via Malvertising Campaign

'Atomic macOS Stealer' Malware Delivered via Malvertising Campaign | ICT Security-Sécurité PC et Internet | Scoop.it

The fake TradingView website is hosted on trabingviews[.]com, with special font characters being used to make it look like the legitimate domain and help it avoid detection.

The malicious website is designed to look authentic, claiming to offer downloads for the TradingView app’s Windows, macOS and Linux versions.

While the Windows and Linux files deliver the NetSupport RAT, the Mac file delivers the AMOS malware. 


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/topic/securite-pc-et-internet


Gust MEES's insight:

The fake TradingView website is hosted on trabingviews[.]com, with special font characters being used to make it look like the legitimate domain and help it avoid detection.

The malicious website is designed to look authentic, claiming to offer downloads for the TradingView app’s Windows, macOS and Linux versions.

While the Windows and Linux files deliver the NetSupport RAT, the Mac file delivers the AMOS malware. 


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/topic/securite-pc-et-internet


No comment yet.
Scooped by Gust MEES
July 14, 2023 5:24 AM
Scoop.it!

AVrecon malware infects 70,000 Linux routers to build botnet

AVrecon malware infects 70,000 Linux routers to build botnet | ICT Security-Sécurité PC et Internet | Scoop.it

Since at least May 2021, stealthy Linux malware called AVrecon was used to infect over 70,000 Linux-based small office/home office (SOHO) routers to a botnet designed to steal bandwidth and provide a hidden residential proxy service.

This allows its operators to hide a wide spectrum of malicious activities, from digital advertising fraud to password spraying.

According to Lumen's Black Lotus Labs threat research team, while the AVrecon remote access trojan (RAT) compromised over 70,000 devices, only 40,000 were added to the botnet after gaining persistence.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux


Gust MEES's insight:

Since at least May 2021, stealthy Linux malware called AVrecon was used to infect over 70,000 Linux-based small office/home office (SOHO) routers to a botnet designed to steal bandwidth and provide a hidden residential proxy service.

This allows its operators to hide a wide spectrum of malicious activities, from digital advertising fraud to password spraying.

According to Lumen's Black Lotus Labs threat research team, while the AVrecon remote access trojan (RAT) compromised over 70,000 devices, only 40,000 were added to the botnet after gaining persistence.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux


No comment yet.
Scooped by Gust MEES
July 6, 2023 9:39 AM
Scoop.it!

New StackRot Linux kernel flaw allows privilege escalation

New StackRot Linux kernel flaw allows privilege escalation | ICT Security-Sécurité PC et Internet | Scoop.it

Technical information has emerged for a serious vulnerability affecting multiple Linux kernel versions that could be triggered with "minimal capabilities." The security issue is being referred to as StackRot (CVE-2023-3269) and can be used to compromise the kernel and elevate privileges.

A patch is available for the affected stable kernels since July 1st and full details about the issue along with a complete exploit code are expected by the end of the month.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux


Gust MEES's insight:

Technical information has emerged for a serious vulnerability affecting multiple Linux kernel versions that could be triggered with "minimal capabilities." The security issue is being referred to as StackRot (CVE-2023-3269) and can be used to compromise the kernel and elevate privileges.

A patch is available for the affected stable kernels since July 1st and full details about the issue along with a complete exploit code are expected by the end of the month.


Learn more / En savoir plus / Mehr erfahren:


https://www.scoop.it/t/securite-pc-et-internet/?&tag=Linux


No comment yet.